SCP Is Still The Fastest Way To Move Files Between Servers When You Don't Trust Anything Else
It looks simple because it is simple. SCP copies files over an SSH connection using the same authentication you already have set up. No extra daemons running, no config files to negotiate, just a command and a path. Most people discover this when they need to push a 40-gigabyte dataset to a staging server at 2 AM and rsync isn't installed on the destination yet. The basic syntax is straightforward enough that I don't even open a terminal man page for it anymore. scp source destination. That's the core of it. You point it at a file or directory on your machine and tell it where to put it on the remote host. The protocol handles encryption automatically because it rides on top of SSH. You don't get to opt out of encryption. That's either a feature or a limitation depending on whether you care about latency over an untrusted network.
What Is Scp The Ultimate Guide To Secure Copy Protocol Explained
I need to be honest about something most tutorials skip. SCP as a protocol is actually older than SFTP, and the original implementation has known performance problems that nobody fixes because everyone just moved to rsync anyway. The OpenSSH team acknowledged this years ago. In newer versions of OpenSSH, scp is basically a compatibility wrapper around the sftp subsystem with a different CLI. The old scp1 protocol had severe issues with concurrency. It doesn't utilize multiple parallel transfers. It streams files sequentially, which means copying twenty small files takes longer than copying one large file of the same total size. This is not theoretical. I burned about forty-five minutes once copying a documentation site with thousands of tiny assets while wondering why scp was moving at exactly the speed of a single TCP stream. Switched to rsync and it finished in three. The real SCP experience is about understanding when it's actually the right tool. It's the right tool when you have SSH access, you need everything encrypted by default, and you're doing a one-off transfer. It's not the right tool when you're moving terabytes across a stable internal network every day. For that you want rsync with SSH as the transport, or SFTP if you need an interactive session. Here's the command you'll use most: scp -r /local/folder user@remote:/remote/path. The -r flag handles directories recursively. Without it, scp refuses to copy anything that isn't a single file and you'll spend five minutes staring at the error before remembering. Add -P for a non-standard port because default port 22 is rarely available in production environments where security matters. The capital P matters. Lowercase -p preserves modification times and permissions, which you almost always want unless you're deliberately overwriting them.
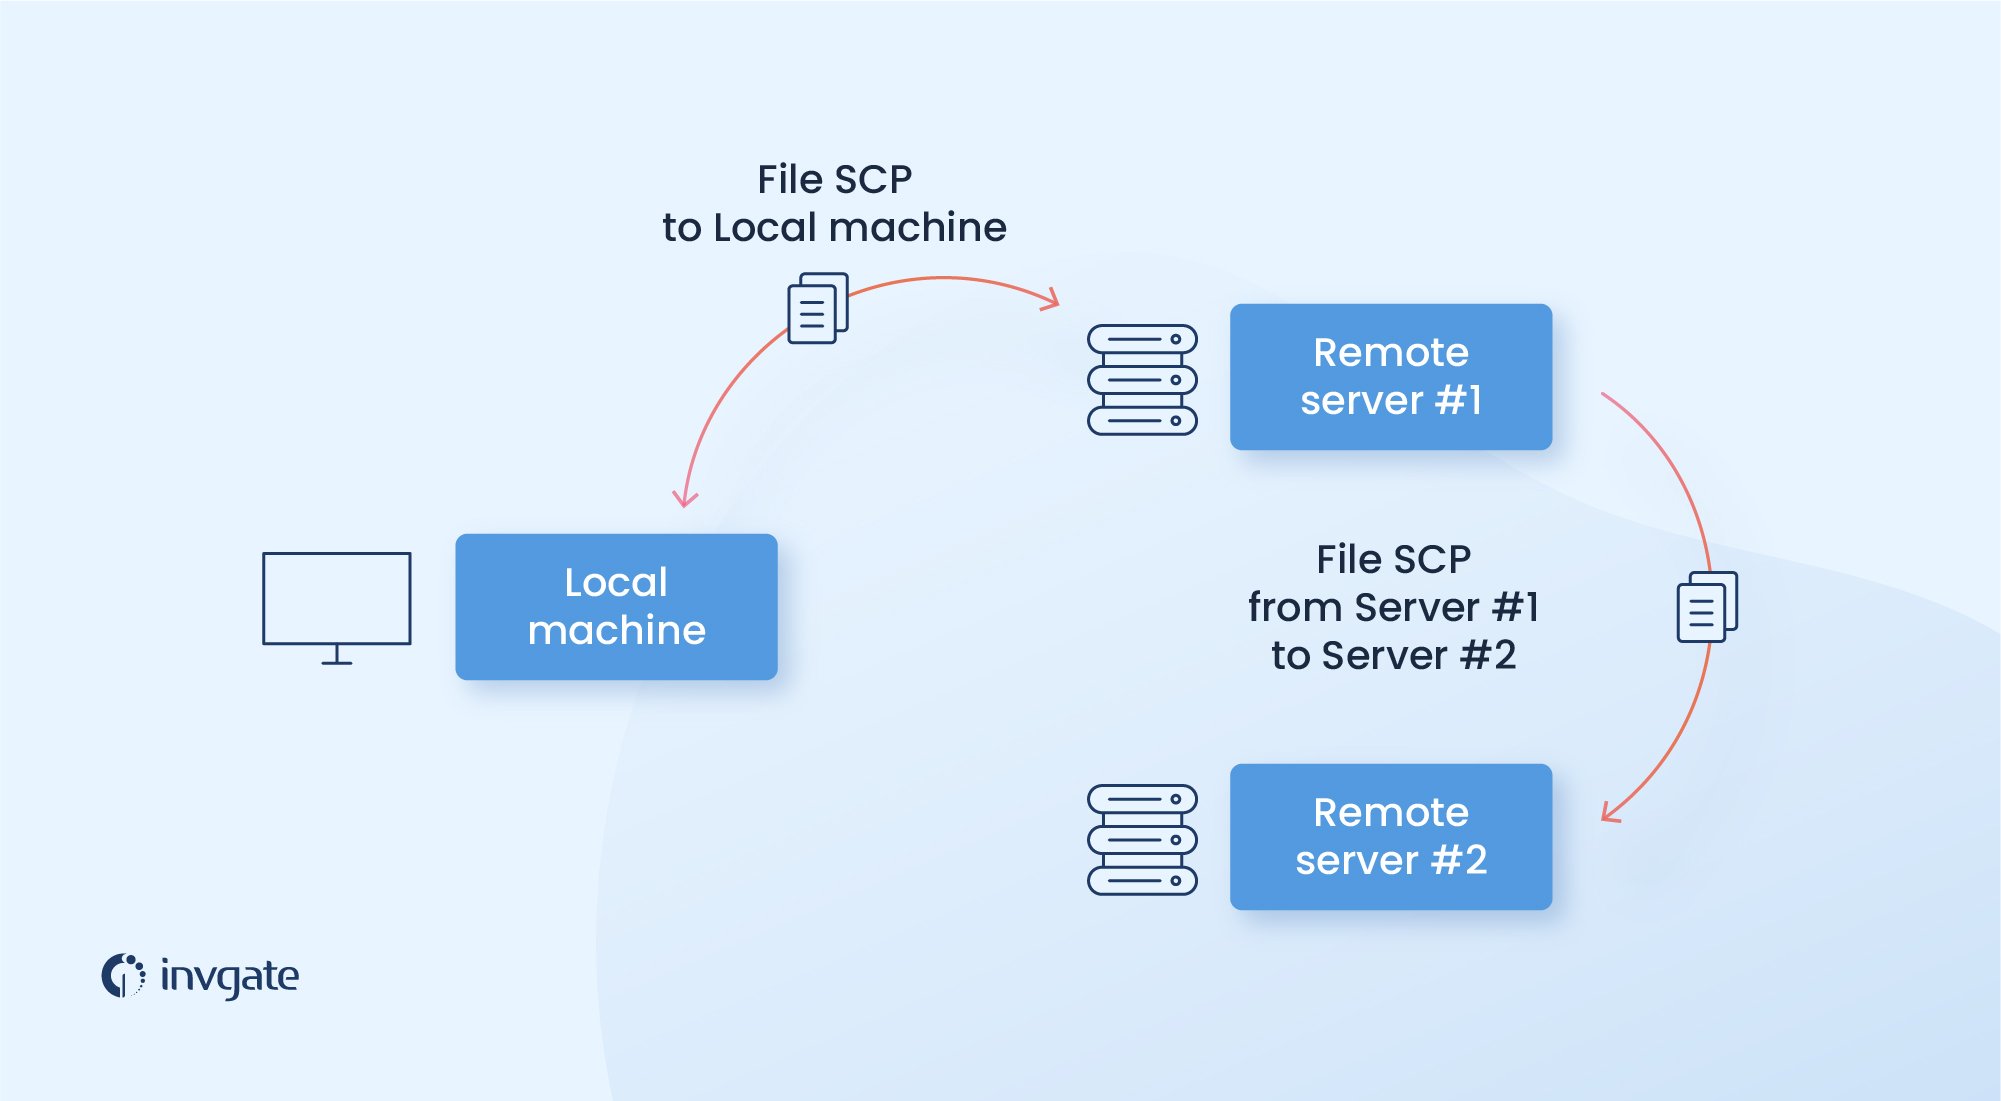
I ran into a specific issue last year that took me two days to troubleshoot. I was transferring a large archive to a server that had a user disk quota of 50 gigabytes. The archive was 48 gigabytes. SCP started the transfer, proceeded normally for about ten minutes, then failed with a vague "broken pipe" error. No useful output. Nothing in the logs that pointed to the quota. I spent an hour thinking it was a network MTU issue or some kind of SSH cipher negotiation failure. Turns out the destination filesystem just filled up partway through and the kernel started rejecting writes. The workaround was running df -h on the destination before starting any large transfer. Now I check disk space first every single time. It saves me the debugging step. Another practical detail that people miss is the colon syntax. When copying to a remote path, the destination needs the colon separator. scp file.txt user@example.com:/home/user/. If you forget the colon, scp interprets the whole thing as a local path and complains that the destination doesn't exist. This is actually useful to know because it means you can also copy from remote to local using the same syntax in reverse. scp user@example.com:/remote/file.txt ./local/. The direction is determined entirely by which side of the colon the path sits on. There's no separate command for inbound transfers. Performance tuning SCP is mostly about SSH options since SCP inherits the connection layer from OpenSSH. You can pass through flags like -o Compression=yes which trades CPU for bandwidth. Over a slow link this can cut transfer times significantly. Over a fast LAN with modern CPUs, compression might actually slow things down because you're adding CPU overhead for data that compresses poorly. Encrypted databases, already-zipped archives, and video files won't shrink much under SSH compression. Test both modes if you're unsure. There's also -C as a shorthand for compression on the command line itself.
Get the Full Details

Bandwidth limiting is another thing worth knowing about. If you're copying during business hours and don't want to saturate the link, -l 500 caps the transfer at 500 kilobits per second. This is a Linux/Unix option. Windows SCP clients handle this differently or not at all depending on which implementation you're using. I've seen people run into this on WSL where the -l flag doesn't behave the same way and they accidentally flood the network. There's a less common but genuinely useful flag: -B for batch mode. It tells SCP to not prompt for passwords and instead rely on SSH keys or other configured authentication. This is critical for automation scripts. Without it, SCP will hang indefinitely waiting for a password prompt in a cron job, and the job just sits there until you notice it and kill it. I once had a backup script that appeared to work for months because it ran during business hours when someone was logged in and could type the password. Then we switched to off-hours execution and it silently failed every night for two weeks before anyone checked the logs. Adding -B and ensuring key-based auth was properly configured fixed it immediately. The security side is worth a brief mention because people treat SCP as automatically secure without understanding what that actually means. Every byte is encrypted with the negotiated SSH cipher suite. The authentication method depends entirely on your SSH configuration. If you're using password auth, you're vulnerable to credential stuffing if the key isn't protected. If you're using key auth without a passphrase, anyone who gets onto that machine has your credentials for every other machine you connect to. This isn't SCP-specific. It's an SSH problem that SCP inherits. Consider that when you're setting up automated transfers between servers.
If you're on a modern OpenSSH installation and someone tells you to avoid SCP entirely, they're probably right for most production use cases. SFTP gives you interactive file management, resume support, and better performance. Rsync gives you delta transfers, which means you only send the parts of files that changed instead of retransmitting everything. SCP is the tool you reach for when you need something that works out of the box without negotiating protocols or installing additional software on the remote end. It's reliable in that narrow context. It's inadequate in the broader one. The protocol itself doesn't change often. You won't see major feature additions in the near future because the ecosystem has effectively moved on. OpenSSH continues to maintain it for compatibility, and that's likely all it will ever be. The good news is that knowing how it works still matters. When your rsync breaks because of a permission mismatch or a symlinks issue or a network timeout mid-transfer, SCP is the thing you fall back on because it does one thing and does it predictably. It connects, it authenticates, it moves bytes, it disconnects. No resume state to manage. No synchronization algorithm to debug. Just a file from here to there, encrypted the whole way.