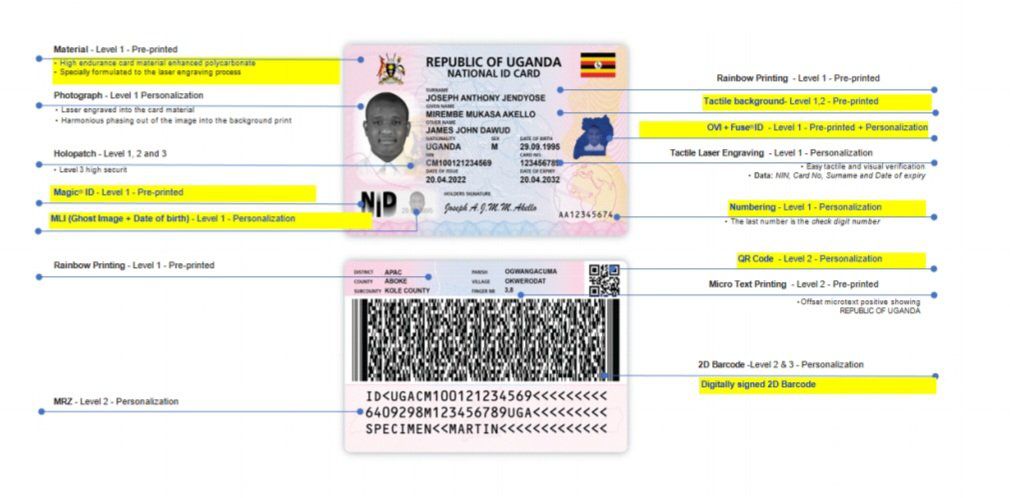
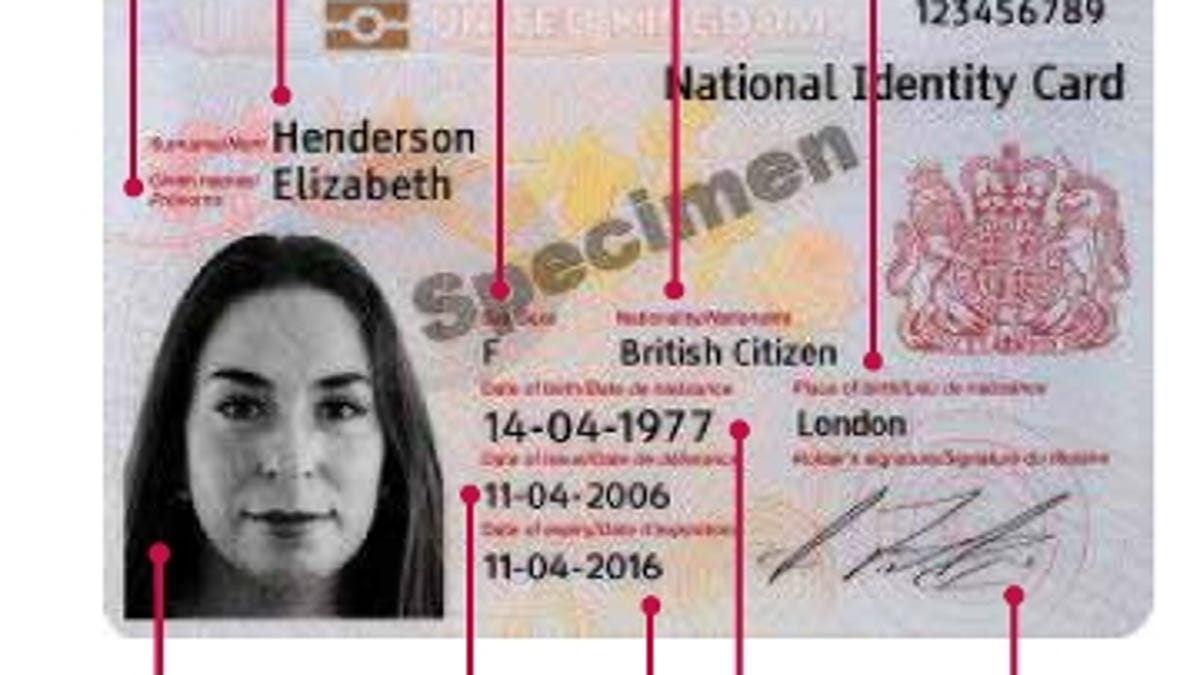
National Id Card Numbers Explained
A national identification number is a unique string of digits assigned by a government to each citizen or legal resident. It serves as the primary key for linking a person to tax records, healthcare systems, voting registers, and other state-maintained databases. The exact length and structure vary by country—China uses an 18-digit format, South Africa has a 13-digit barcoded number, and the United States doesn't issue a single national ID at all but instead relies on Social Security Numbers for most purposes. The primary purpose is identification at scale. Before digital systems existed, names alone were enough for local transactions. Once governments started maintaining electronic records across provinces or states, duplicate names became a genuine problem. Two people named Mohammed Ali could both apply for the same government benefit if the system couldn't distinguish between them. A number eliminates that ambiguity.
What Is National Id Card Number Definition Purpose And Security Explained
The definition portion is straightforward: it is an algorithmically generated identifier tied to a specific individual. Purpose covers everything from tax collection and conscription to healthcare eligibility and bank account verification. Security is where things get complicated, and where most people encounter problems without realizing it. I spent about six months dealing with ID number reconciliation for a healthcare integration project in Southeast Asia. The issue wasn't the technology—it was that roughly 12 percent of the population had been assigned numbers through multiple overlapping systems, each using different generation algorithms. One provincial health department issued numbers starting with the date of birth, another used sequential registration order, and a third combined both with a check digit. Patients would show up at urban clinics with cards from rural districts, and the automated matching engine kept flagging them as duplicates when they were actually the same person. The workaround I ended up using was fairly brute-force: we pulled all available biographic fields—full name, date of birth, parents' names, registered address—and ran fuzzy matching across the three databases. We then created a unified mapping table keyed by confidence score, with manual review for anything below 85 percent. It took about three weeks to process 40,000 records, but once we had the mapping table, reconciliation took under two seconds per query. The real lesson was that the number itself is less important than the data linkage around it. A clean algorithm means nothing if the assignment process is inconsistent.
Structure matters more than most people realize. China's 18-digit ID follows ISO/IEC 7812, which is the same standard used for payment card numbering. The first six digits encode the administrative region, the next eight are the birth date in YYYYMMDD format, the following three are a sequence number for same-day births, and the final digit is a modulo-11 check value. This means you can validate a Chinese ID without consulting any database—you just do the math. I've seen fraud investigators use this property to quickly screen large datasets for obviously fake numbers before spending time on deeper verification. Other countries don't make it this easy. The UK National Insurance number has a format like QQ 12 34 56 C, where the letters encode region and status, but there's no built-in validation algorithm. You can't tell if a number is structurally valid without checking against government records. This makes it harder to detect fabrication at point of entry but also means more false positives when legitimate numbers look unusual.
Get the Full Details
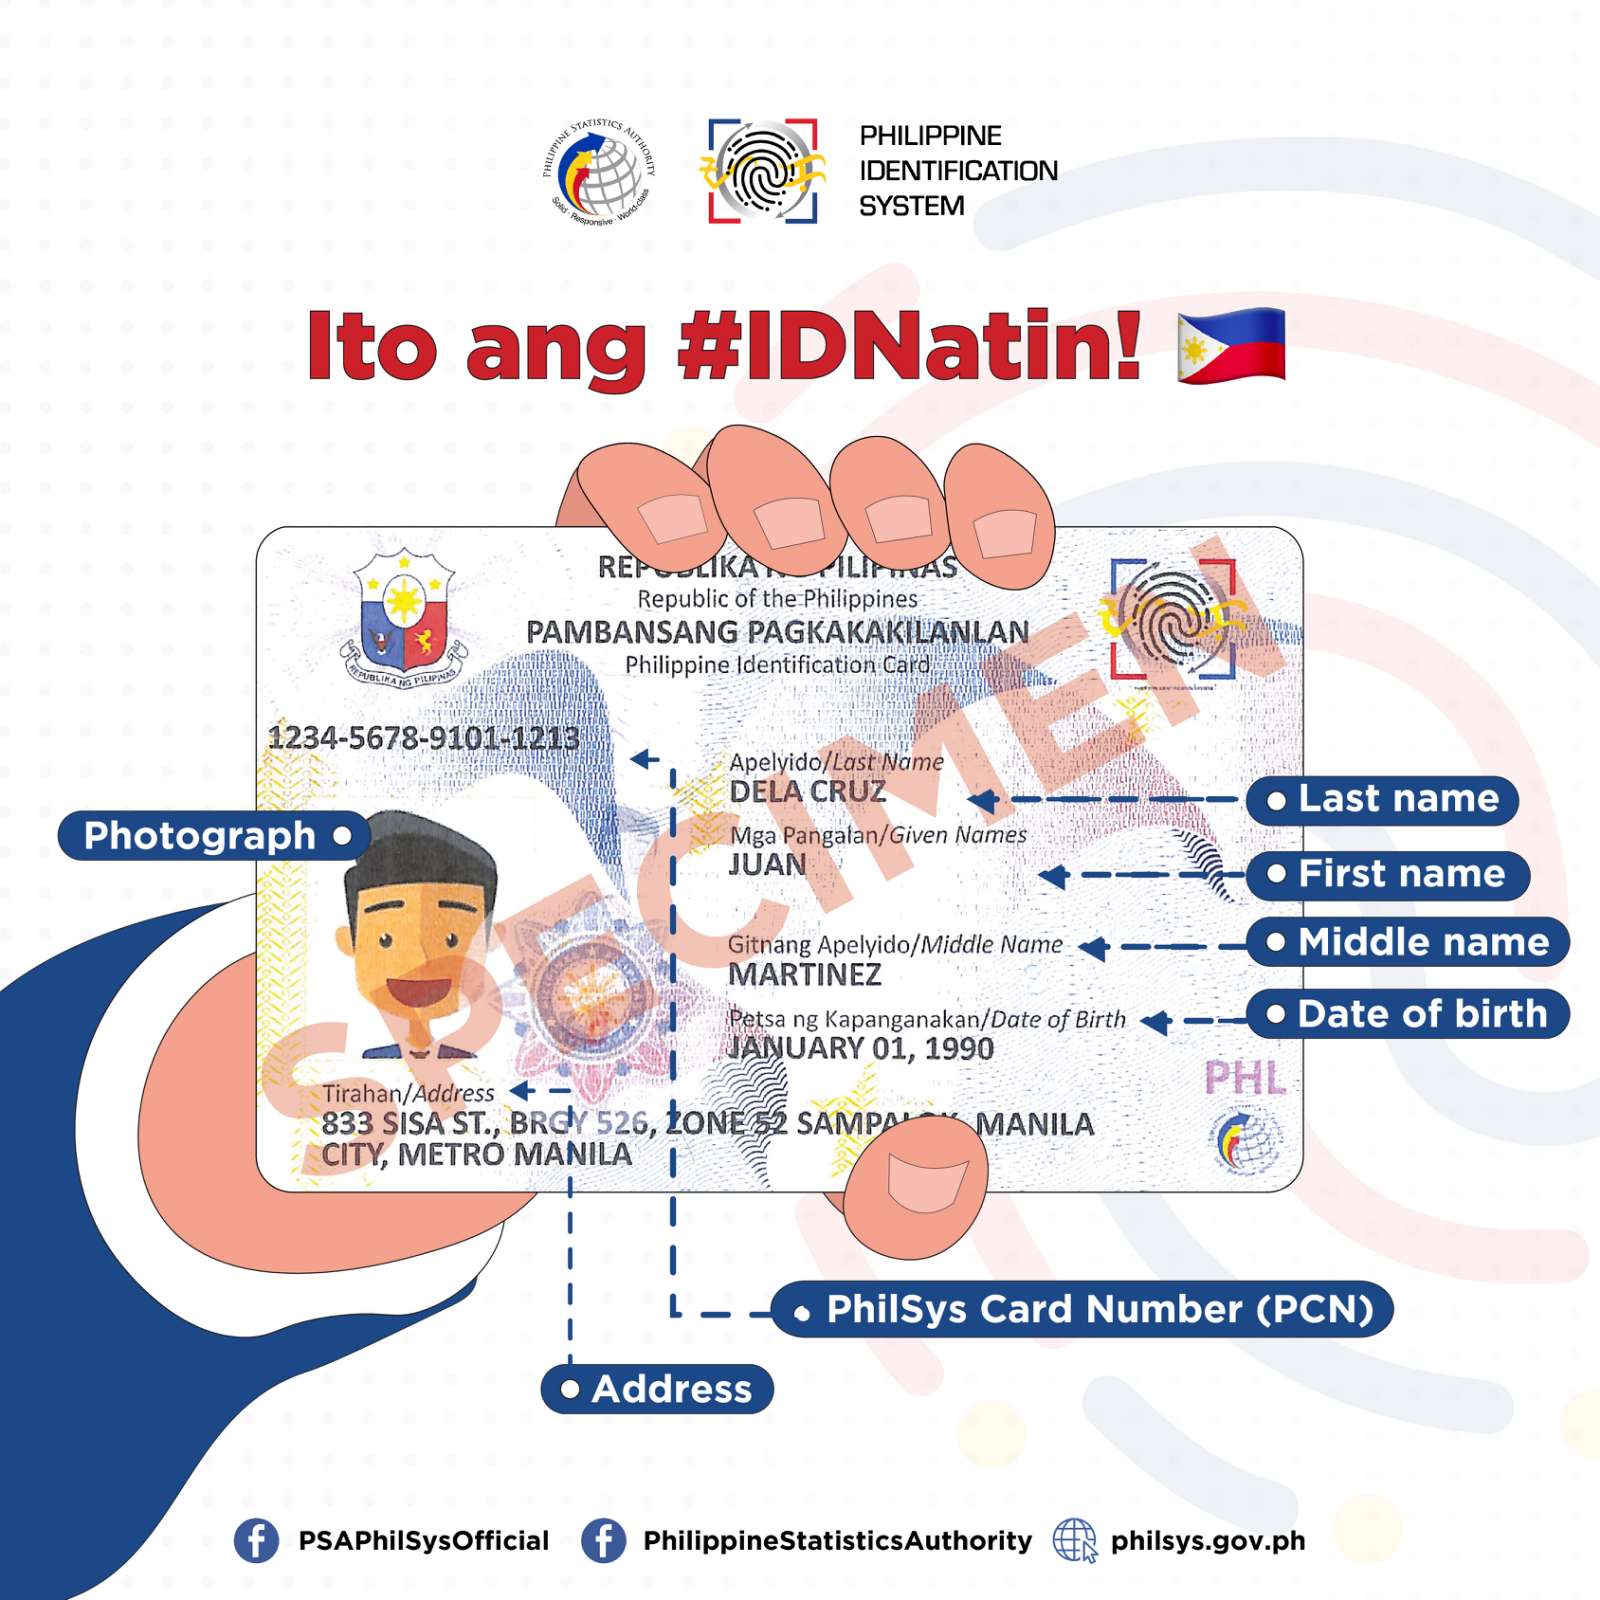
How National ID Numbers Are Used in Practice
Banks require them for account opening. Government agencies use them for benefits distribution. Employers need them for payroll tax reporting. Private sector companies increasingly ask for them during identity verification, especially in financial services where know-your-customer regulations demand documented proof of identity. The practical reality is that these numbers circulate far beyond government systems. Every time someone fills out a form, opens an account, or verifies their identity online, the number gets transmitted to at least one private database. Most organizations treat it like any other sensitive field, but the exposure surface is enormous. A single data breach at a utility company can expose millions of national ID numbers alongside names, addresses, and payment information. I worked on an audit for a mid-size logistics company that collected employee ID numbers for tax reporting. They stored them in a spreadsheet accessible to every regional manager, with no encryption at rest and passwords written on sticky notes under keyboards. We found 340 employees whose full ID numbers were visible to anyone with physical access to the office. The fix was simple—encrypt the column and restrict access—but the point is that most breaches happen through organizational negligence, not sophisticated attacks.
Some countries have built additional protections into the number itself. Brazil's CPF number includes a second check digit, making it nearly impossible to guess a valid sequence. India's Aadhaar number uses biometric linkage rather than pure numeric validation. These design choices reduce the attack surface for number-guessing attacks, but they don't prevent leakage through system breaches or insider access.
Security Considerations You Should Understand
National ID numbers are permanent. You can change your name, move, even reconstruct part of your face through surgery, but you cannot change your ID number. This permanence is what makes it valuable to governments and what makes it dangerous when compromised. A stolen credit card number can be cancelled and replaced. A stolen national ID number stays stolen for life. The most common misuse pattern is identity synthesis, where criminals combine real ID numbers with fabricated personal details to create new identities. Unlike pure identity theft, which uses an existing person's full profile, synthesis creates something novel that can open accounts, apply for loans, and build credit history without immediately triggering alerts. The victim often doesn't discover the problem until credit agencies start reporting delinquencies on accounts they never opened. I encountered this during a case involving a call center in Manila that sold aggregated ID number datasets to brokers in three countries. The data came from employees who had been asked to submit copies of their national ID cards for background checks, then forwarded through a chain of subcontractors before reaching the brokers. The IDs hadn't been altered—they were real, valid numbers linked to real people. The damage wasn't immediate, but the exposure meant those numbers would circulate indefinitely.

Password reuse across government and private systems compounds the risk. Many people use the same authentication methods for their national ID verification portals as they do for email or social media. When one system is breached, the ID numbers become vulnerable through credential stuffing. I've seen phishing sites that perfectly replicate government ID lookup portals, asking users to enter their number and a one-time code sent to their phone. The code comes from a legitimate notification system, but the request itself is fraudulent. This social engineering approach bypasses technical controls entirely. The security model for most national ID systems assumes that possession of the number equals authority over the identity. This assumption breaks down in digital environments where numbers can be copied without physical theft. Some countries have addressed this by requiring multi-factor authentication for online ID verification, combining the number with a biometric check or a government-issued digital certificate. Others rely on institutional controls, trusting that banks and employers will verify identity through proper channels.
What You Can Do to Protect Yourself
The first step is treating your national ID number with the same caution you'd give a password. Don't share it in email, don't upload unencrypted copies to cloud storage, and don't provide it unless there's a clear legal requirement. Many private companies ask for it unnecessarily—retailers processing returns, gyms signing up members, social clubs collecting membership fees. They often claim it's for identity verification, but they rarely store it securely and rarely need it for their actual operations. If you must provide it, ask how it will be stored and for how long. Legitimate organizations can usually answer this question. Those that can't or won't should be treated as suspicious. I once refused to give my ID number to a utility company connecting service to a new apartment. Their response was that it was required by law, but they couldn't cite which provision. When I asked for the specific regulation, they couldn't produce it. I ended up providing it to the landlord instead, who handled the connection directly. Sometimes the workaround is simpler than the confrontation. Monitor your credit reports regularly. In countries with centralized credit reporting, this is straightforward. In places with fragmented systems, it requires more effort but remains important. A single delinquent account tied to your ID number could indicate that someone has used your number to open credit without your knowledge. Early detection limits damage significantly.
Some jurisdictions allow you to request an audit trail showing who has accessed your ID record. This isn't universally available, but where it exists, it can reveal unauthorized accesses that might otherwise go undetected. I helped someone in Europe request their access logs after noticing an unusual address on their registration. The logs showed seven views from IP addresses in different countries over a six-month period, none of which matched their known location history. The investigation that followed identified a compromised government employee who had been selling access data. The technical landscape is shifting. Several countries are moving toward digital ID systems that use cryptographic proofs instead of plain number presentation. With these systems, you can prove you are over 18 without revealing your birth date, or prove you have a valid license without disclosing your address. This zero-knowledge approach reduces the exposure surface significantly. Until these systems are widespread, though, the number itself remains the primary identifier, and that creates ongoing risk.
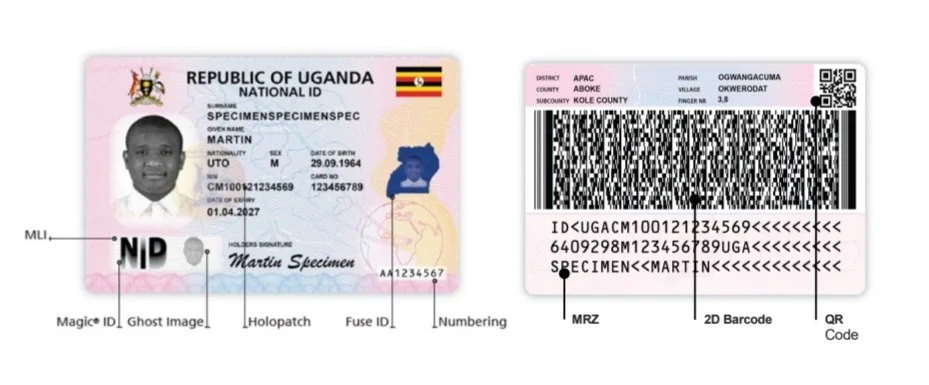
Understanding the Limitations
National ID systems have real weaknesses that no amount of policy reform fully addresses. First, they were designed for paper-based bureaucracies, not digital networks. The original assumption was that the number would be written on forms and filed in cabinets. Digital transmission was never part of the design, so the security properties weren't built in from the start. Retrofitting security onto legacy systems is expensive and often incomplete. Second, interoperability between systems creates additional vulnerability. When a bank verifies an ID number through a government API, it trusts that the API is secure and that the response is authentic. When that same number appears in a private sector database that lacks equivalent protections, the guarantee disappears. The number doesn't care about the context in which it's being used. Third, there's no universal standard for handling compromised numbers. Some countries allow reissuance under exceptional circumstances. Most don't. If your number is compromised and you can't get a replacement, you're stuck managing the risk rather than eliminating it. I've spoken with several people in this position who describe living with a constant low-level anxiety about whether some new account was opened in their name.
The legal framework varies enormously. In some jurisdictions, unauthorized disclosure of someone else's ID number is a criminal offense with significant penalties. In others, the remedies are civil and limited. Enforcement is inconsistent even where strong laws exist. A breach at a large corporation might trigger regulatory action, while the same breach at a small business often goes unnoticed. The practical takeaway is that national ID numbers are necessary infrastructure but inherently risky assets. They enable modern governance and commerce, but they also create concentration points for identity-related harm. Understanding how they work, how they're used, and where the gaps are helps you manage the risk rather than ignoring it. The systems won't disappear, and neither will the requirement to provide your number in many situations. What changes is how carefully you handle it once you do.