Why Your Business Emails Keep Landing in Spam
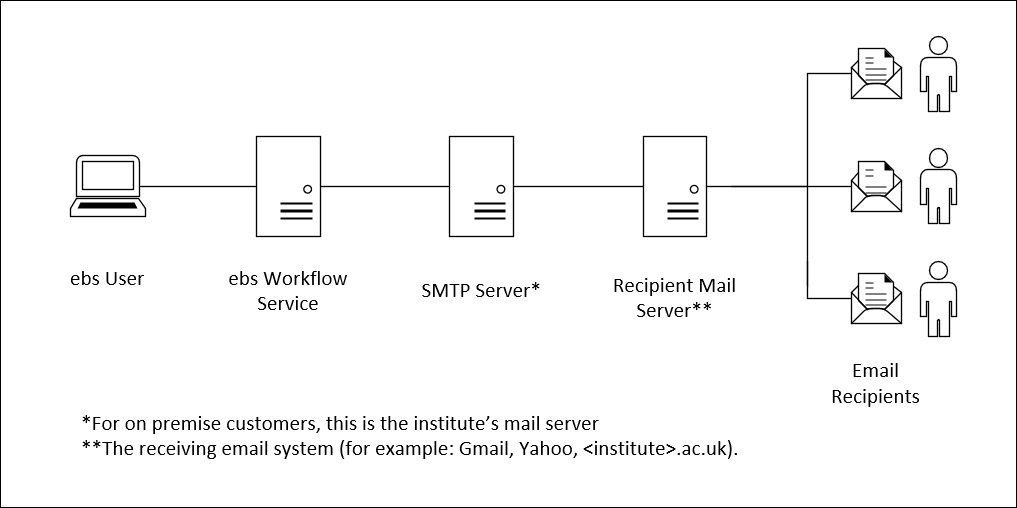
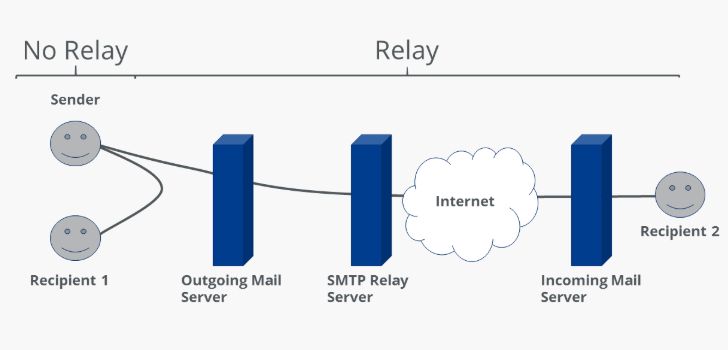
You send an invoice to a client at nine in the morning. It never arrives. Or it does, but it hits their promotions tab or, worse, gets bounced entirely. This is not a hypothetical problem. It happens to companies every single day, and in most cases the culprit sits on the company's own network, doing exactly what it was supposed to do — nothing suspicious at all. A mail relay is simply an intermediary server that accepts email from your applications and forwards it to the destination mail server on the internet. In enterprise environments, this is usually implemented as a centralized SMTP relay — sometimes branded as a "centralized relay" or abbreviated as "CL mail relay" in internal documentation. The idea is straightforward: instead of letting every workstation or application send mail directly to the outside world, you route everything through a single controlled gateway. That gateway handles authentication, policy enforcement, logging, and reputation management. Here's what nobody tells you about this setup, though. The relay itself is not the hard part. Setting one up takes maybe twenty minutes if you know what you're doing. The hard part is maintaining the delivery pipeline once traffic starts flowing. I learned this the hard way in 2022 when our relay started getting rate-limited by Google and Microsoft simultaneously. No warnings. No explanation. Just sustained 550 errors across thousands of transactional messages. The root cause turned out to be a misconfigured PTR record pointing to an old hosting provider, combined with our SPF entry including a blocklist of IPs that no longer existed. Fixing it required removing eight stale DNS entries and updating the reverse DNS on two interfaces. Took me about forty-five minutes of staring at dig output and mailing list archives.
How Mail Relay Actually Works in Practice
Your application calls SMTP on port 587 and hands off the message to the relay server. The relay authenticates the connection — usually via SASL plain text over TLS, sometimes IP-based allowlisting for internal services. Then the relay looks up the destination domain's MX record using DNS, establishes a separate SMTP session to the target server, and attempts delivery. If the target server says no, the relay queues the message and retries according to its configured schedule — typically at 5 minutes, 30 minutes, 2 hours, and 24 hours before final bounce. The entire process should take under three seconds for a successfully delivered message. In my experience, anything over five seconds suggests either a DNS resolution issue or the relay is sitting in a queue waiting for some timeout to expire. The most common timeout I see is during the TLS handshake on port 25. Some mail servers on the internet simply don't support STARTTLS properly, and if your relay isn't configured to fall back gracefully, messages pile up in an awkward limbo state. Let me be clear about what relay doesn't do. It does not guarantee delivery. It does not prevent spam flags. It does not protect your domain's sender reputation by itself. What it does is give you a single point where you can monitor, control, and troubleshoot outbound email. That distinction matters because companies often conflate "having a relay" with "having good deliverability." Those are related but completely different problems.
The DNS Configuration That Actually Matters
If you have only one thing to configure correctly before sending business email at scale, it's the DNS records associated with your relay's sending IP. Every major mailbox provider — Gmail, Outlook, Yahoo — checks these records before accepting mail. Get them wrong and your messages will be accepted then silently filtered or rejected at various points in the pipeline. SPF records specify which IPs are authorized to send on behalf of your domain. A typical record looks something like v=spf1 ip4:203.0.113.0/24 include:_spf.google.com ~all. The tilde-all at the end is a soft fail, which means unauthorized sends get flagged but not outright rejected. Hard fail with minus-all is more aggressive but can break legitimate forwarding scenarios. I recommend soft fail for most business use cases unless you control every possible sending path, which almost no one does. DKIM adds a cryptographic signature to each message using your private key. The public key lives in your DNS as a TXT record. Receiving servers verify the signature and can reject messages where it fails. The trick is key rotation. Most people set up a single DKIM key and never change it. That's acceptable for low-volume senders but problematic if you're pushing thousands of messages daily. Industry standard practice is two keys in active rotation — one for signing, one for verification during the handoff. The overhead is minimal if your mail software supports it natively.
Get the Full Details
DMARC ties SPF and DKIM together with a policy instruction. It tells receiving servers what to do when a message fails alignment checks. The three policy values are none, quarantine, and reject. Start with none while you validate your setup. Move to quarantine once you're confident legitimate traffic passes. Reject is the correct final state but requires that your relay and all sending applications are fully compliant first. Setting reject too early is one of the most common mistakes I see — it silently kills delivery for any message that doesn't perfectly align, including forwarded mail from external lists. Reverse DNS, or PTR, is the record that maps your sending IP back to a hostname. This is the one most people neglect because it requires coordination with your ISP or hosting provider. A PTR that points to a generic hostname like smtp1.hostingcompany.net rather than mail.yourdomain.com will trigger reputation penalties at several major providers. I've seen deliverability improve just by getting a clean PTR configured, with no other changes at all.
Common Pitfalls That Break Delivery Without Warning
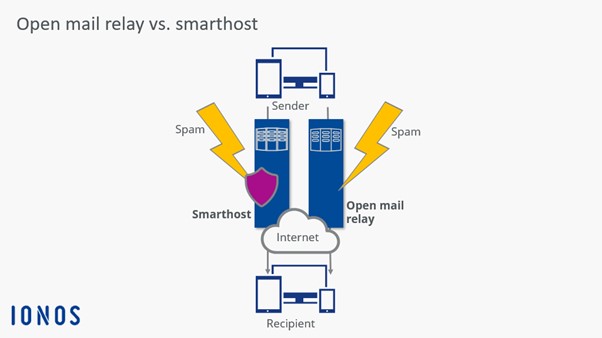
Here's a list of things that will make your relay seem broken even when it's working correctly. First, the 25-port block. Most residential and many commercial ISPs block outbound SMTP on port 25 to prevent spam. If your relay tries to deliver on port 25 and the connection times out, the message enters the retry queue. After four retries spanning roughly twenty-six hours, the message bounces with a timeout error. The fix is either to negotiate unblocking with your provider or to route all outbound mail through port 587 with authentication to a smart host. Many cloud providers now block port 25 by default, so this isn't hypothetical — it's likely your current situation. Second, IP warming. If you just provisioned a new sending IP and start pushing full volume immediately, every major mailbox provider will treat you as suspicious. The standard warming schedule is roughly twenty percent of target volume for the first week, forty percent for the second, sixty percent for the third, and one hundred percent by the fourth week. Rush this and you'll spend months recovering from a blacklist placement. Slow it down and you protect your domain's long-term reputation. There's no shortcut here. Third, bounce handling. When a message bounces, your relay should log the reason and update any subscriber lists accordingly. Hard bounces — permanent failures like invalid addresses — should be removed immediately. Soft bounces — temporary issues like full mailboxes — should be retried but tracked. If you keep mailing addresses that have hard bounced, your bounce rate climbs, and mailbox providers use bounce rate as a primary reputation signal. A bounce rate above five percent starts triggering filters. Above ten percent is a reliable path to the blacklist.
Fourth, TLS version mismatches. Some older relay configurations default to TLS 1.0 or 1.1. Several major providers have dropped support for these versions. If your relay is still attempting TLS 1.0, connections may succeed or fail unpredictably depending on the receiving server's configuration. Update to TLS 1.2 minimum, ideally 1.3. The performance difference is negligible and the compatibility gain is substantial.
Monitoring What Actually Matters
Most people monitor whether their relay is running. That's necessary but insufficient. Running and delivering are two different states. Here's what I track on every relay I manage: queue depth and age distribution, per-domain success and failure rates, average TLS handshake time, DNS resolution latency, and bounce categorization breakdown. The queue age metric is particularly useful — a queue depth of five hundred messages is fine if they're all less than ten minutes old. It's a crisis if half of them are older than six hours. Open-source tools like Postfix's maillog, Exim's mainlog, or OpenSMTPD's daemon.log give you most of this data if you parse them correctly. Commercial relay services provide dashboards, but they're often limited to aggregated metrics and may not surface domain-specific failure patterns until it's too late. I've found that a simple cron job parsing log entries for 5xx responses and aggregating by recipient domain catches problems faster than most vendor dashboards.
When Relay Isn't the Right Answer
There are scenarios where running your own mail relay is actively worse than using a managed service. If you send fewer than fifty thousand messages per month, the operational overhead of maintaining authentication, DNS records, IP reputation, and bounce handling probably exceeds the cost of a transactional email API. Services like SendGrid, Amazon SES, or Mailgun handle the infrastructure problems for you at predictable pricing. The tradeoff is less control and shared IP reputation — your messages travel alongside other customers' mail on the same sending infrastructure. If you do run your own relay, budget for ongoing maintenance. This is not a set-it-and-forget-it system. DNS records expire. Certificates need renewal. Blacklists get updated. Provider policies change without notice. I've seen relays go from healthy delivery to complete blockage because a provider changed their DKIM verification requirements and the relay wasn't reconfigured to match. The maintenance window I allocate is roughly two hours per week for log review and configuration validation, plus whatever time troubleshooting throws at me. For companies sending appointment reminders, password resets, invoice notifications, and marketing batches all through the same relay, the complexity multiplies. Different content types have different failure modes. Transactional mail needs higher priority queuing. Marketing batches benefit from volume throttling. A single relay can handle both, but you need explicit queue separation and delivery policy rules configured per message category. Without that separation, a marketing batch that hits a few hard bounces can degrade delivery of your critical transactional messages.
Getting Your First Relay Operational
If you're setting up a relay from scratch, the sequence that works reliably is: configure the SMTP listener with TLS enabled, set up authenticated submission on port 587, add your sending IP to SPF, generate a DKIM key pair and publish the public half, set DMARC to none initially, verify your PTR record resolves correctly, send test messages to Gmail and Outlook accounts and check the headers they return, then gradually increase volume following the warming schedule. Each step should be verified independently before moving to the next. Skipping the header check is the most common mistake — those received headers tell you exactly how the receiving server evaluated your authentication, which is far more useful than waiting for a real customer to complain about missing mail. The relay itself is simple technology. SMTP has been around since the eighties. The complexity comes from the ecosystem of reputation systems, filtering heuristics, and policy changes that any single sender has no control over. Understanding that gap between what the relay does and what deliverability requires is what separates a functioning setup from one that actually reaches inboxes consistently.