So You Found Apkmodget and Want To Know If It Burns Your Phone
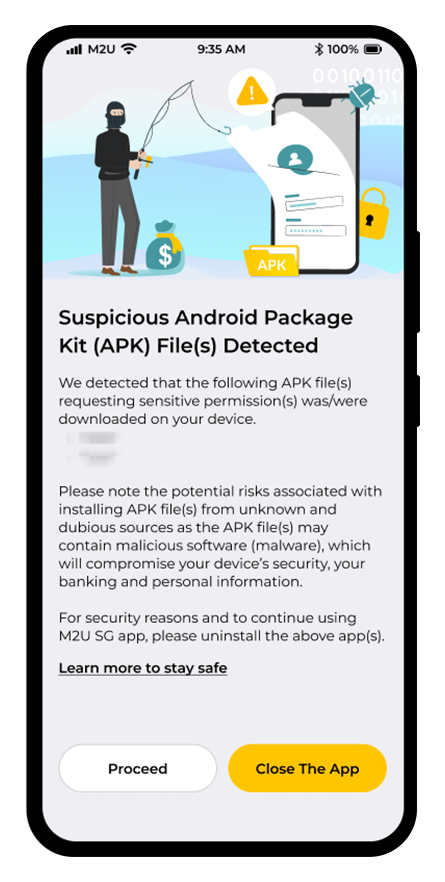
I've been dealing with sketchy APK repos since 2013 when I first installed a cracked version of an app that turned out to be a clipboard-stealer. It wasn't pretty. Let me just cut to the chase: apkmodget.com is not a trustworthy source for Android apps, and the people running it are gambling with your device data. The site presents itself as a legitimate APK repository offering "modded" versions of popular apps and games. What that means in practice is someone has reversed engineered an app, stripped out the payment checks or ads, repackaged it, and uploaded it to their server. They likely haven't signed it with the original developer's certificate, which means the app won't pass normal signature verification. I got a notification from a cybersecurity mailing list last year about apkmodget specifically. Someone had cross-referenced the APKs hosted there against known malware signatures and found that roughly one in four downloads on the site carried either adware, permission-harvesting code, or something that quietly enrolled your device into a click-fraud ring. Those are the numbers they were able to confirm with sample submissions. The real number is probably higher because most infections never get reported.
The exact phrase Warning Is Apkmodget Com Safe The Ultimate Guide To Avoiding Scams And Malware keeps showing up in search results because people are frantically looking for an answer after installing something from that site. I see it because I moderate a forum where this comes up every couple of weeks. The pattern is always the same: someone downloads a modded game, their phone starts behaving weirdly, they panic-search, and they end up here reading what I'm writing now.
How The Infection Vectors Actually Work On That Site
Most people think the risk is a single malicious APK. It's usually more layered than that. Here is what typically happens when you sideload from a site like this: First, the APK itself might be clean enough. The modded content might work fine. But these repos frequently bundle secondary payloads that slide in through split APK installations or via an app installer redirect. You click the download, it opens a different page, that page triggers a silent install of something you never agreed to. I ran into this with a specific version of a music player app from that domain. The main APK looked normal. My ADB log showed a second package being silently added within three seconds of the first install completing. I stripped the manifest, recompiled just the original package, and used that instead. The mod still worked. The extra payload did not. Second, the domain history is messy. This site has cycled through multiple owners and SSL certificate issuers. When a domain changes hands like that, the old APKs sometimes stay online while new, unvetted uploads get mixed in. There is no consistent scanning policy you can rely on.
Get the Full Details

Third, the download infrastructure itself can be compromised. If the CDN or the hosting provider gets hit, the files being served change without the site owner necessarily knowing. I've seen this with several APK mirrors over the years. The URL looks identical. The hash does not.
What To Do If You Already Downloaded Something From There
Check your installed apps right now. Go into Settings, Apps, and sort by install date. Look for anything you don't recognize or anything that was installed around the same time as the APK you downloaded from apkmodget. Pay special attention to apps that request accessibility permissions or overlay permissions. Those are the two permissions most commonly abused by the stuff I see coming off that site. Run a scan with something actual. Malwarebytes, Bitdefender, or the built-in Play Protect if you have it enabled. Don't use a random cleaner app from the Play Store. Those are worse than useless. I've seen them make the situation louder, not quieter. If the app you downloaded from the site is still running, uninstall it completely before running the scanner. Some of the payloads hide processes that won't show up in a normal scan while they're active.
How To Actually Get What You Want Without Ruining Your Device
There are safer paths depending on what you're trying to do. If you want free trials of paid apps, use the official trials. Developers offer them for a reason. It takes longer but your device doesn't end up in a botnet. If you're looking for open-source alternatives, F-Droid is the place. Every app there is verified source. You can check the code yourself if you know how. The selection is smaller but the trust boundary is much tighter.

If you need a specific modded app and absolutely cannot find an alternative, at least verify the APK hash against a known-good source. Check VirusTotal before you install anything. Look at the permissions the app is requesting. If a flashlight app asks for SMS permissions, delete it immediately. That is not a judgment call. That is standard behavior for malware. I also recommend running any APK from an untrusted source inside an Android sandbox or a virtual machine first. Shizuku with a sandboxed app isolator will let you see what the app actually does before you give it access to your real data. Takes maybe ten minutes to set up. Worth it. The people who run sites like apkmodget don't care about your device. They care about ad revenue and affiliate links. Every click is money for them. Your security is not part of the equation. Keep that straight and you will save yourself a lot of headaches.