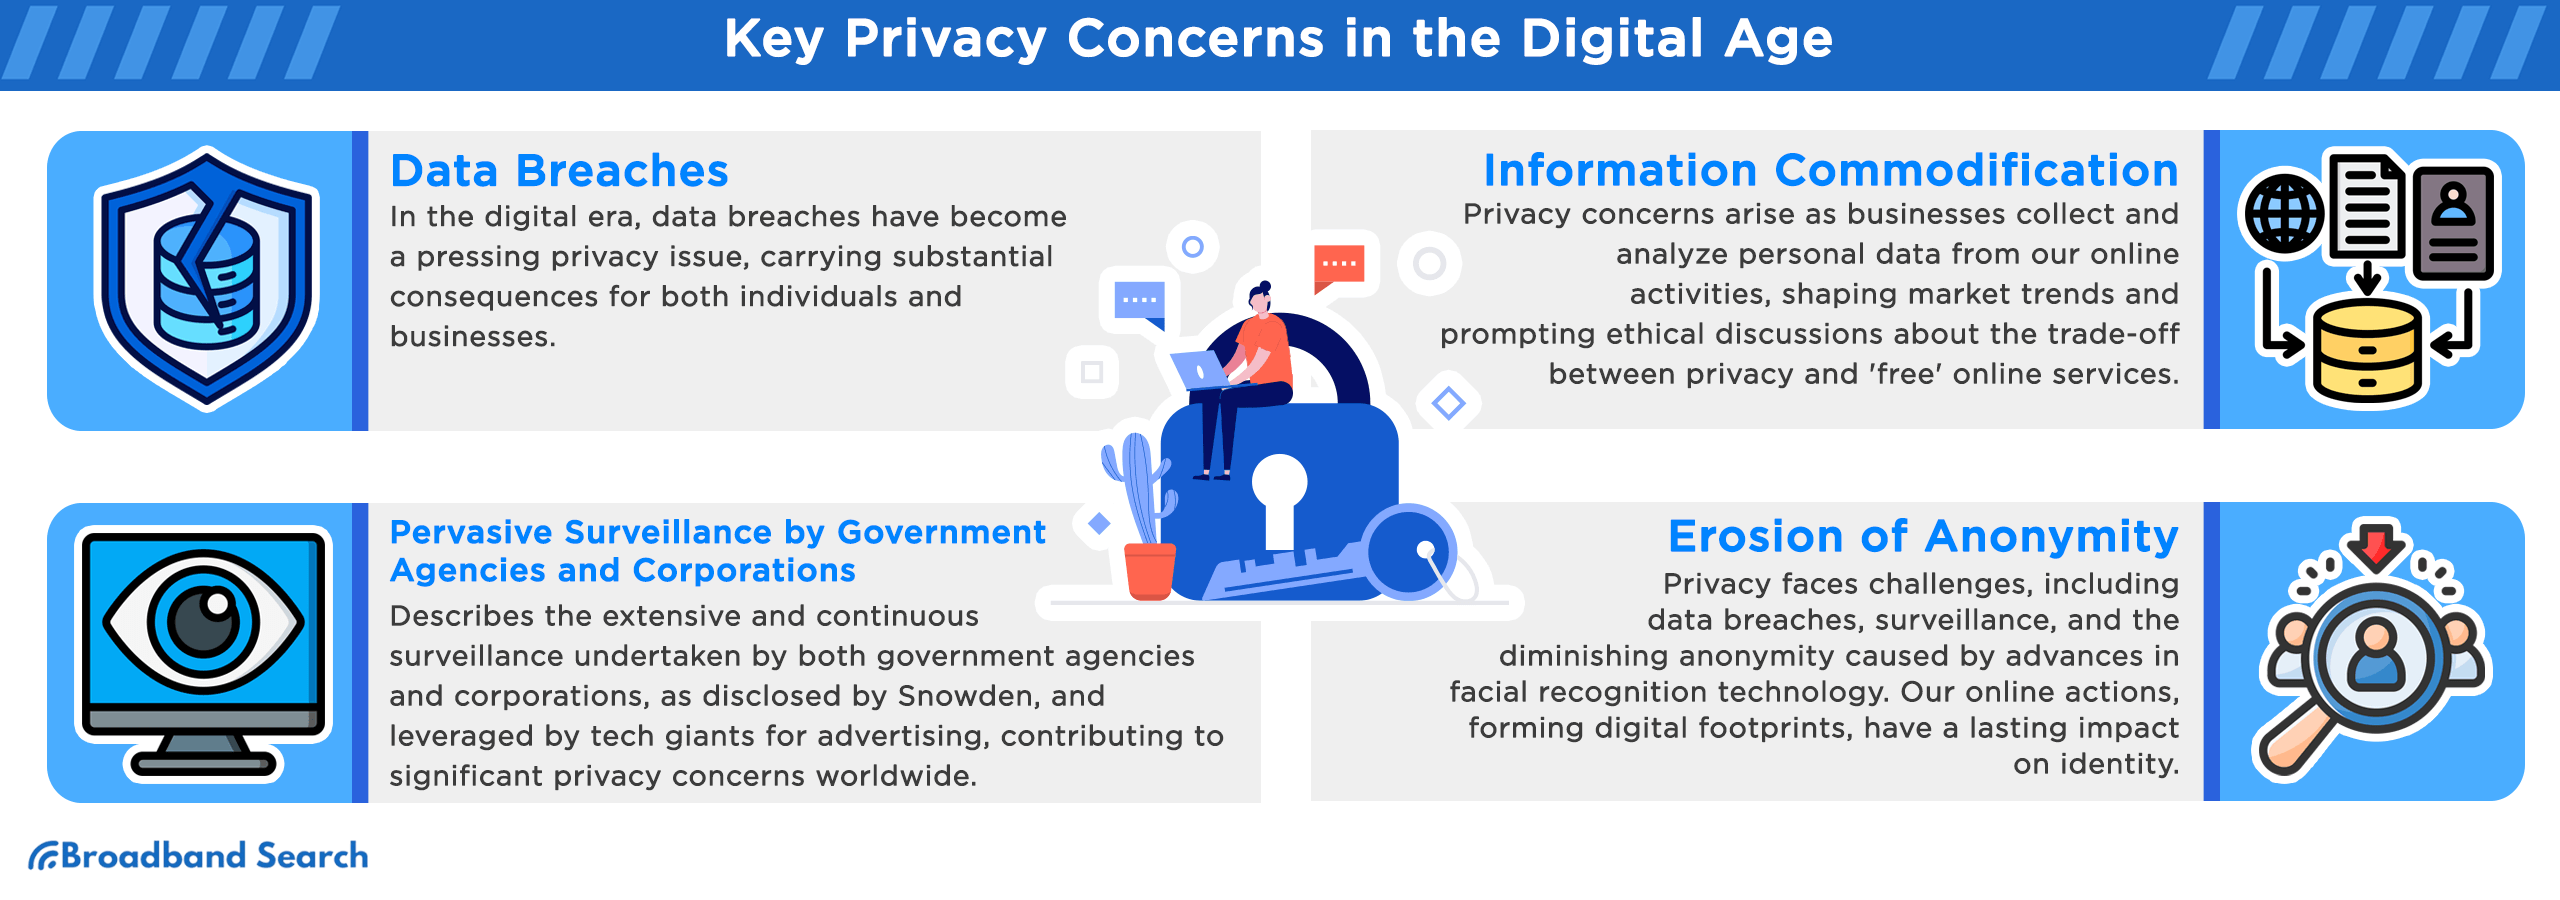
Why Your Digital Footprint Is Already Compromised
Most people think privacy means turning off tracking cookies or using a different browser. That is the surface level. The real problem runs much deeper and involves how data flows between services, what metadata gets collected alongside your actual content, and how companies build profiles that no single privacy tool can undo. I spent years managing privacy configurations for enterprise clients before the conversation shifted toward consumer-facing tools, and even then the landscape was already fractured.The Fight For Privacy In The Digital Age Understanding The Challenges And Opportunities
Data minimization should be the first step in any serious privacy strategy, yet most people ignore it entirely. The principle is simple: if you do not collect or share data, you cannot lose it. The challenge is that almost every app and website demands more than it needs. Your weather app asking for contacts. A flashlight app requesting location history. These are not edge cases, they are standard practice across the industry. I ran a full privacy audit for a small company recently. We went through their employee devices and found that at least twelve separate apps were shipping telemetry data to third-party analytics platforms without any explicit consent mechanism. The workaround was not technical, it was procedural. We created a standardized app whitelist, required IT approval for anything new, and deployed a network-level DNS filter that blocked known tracking domains. This cut the average data leakage from about four hundred kilobytes per session down to roughly twelve kilobytes, which is still not zero but it is a dramatic improvement. End-to-end encryption gets a lot of attention, and for good reason, but it solves only part of the problem. If you are using Signal or WhatsApp, your messages are protected in transit. What is not protected is the metadata: who you talked to, when, how long, and how often. Metadata is where the real profiling happens. Companies and surveillance systems care far more about patterns of communication than the content itself because patterns reveal relationships, routines, and behaviors that content alone does not.
Here is a counter-intuitive point that most people miss: switching to a privacy-respecting search engine will not make you significantly harder to track if you continue logging into the same accounts everywhere. Your identity is already constructed from cross-service correlation. Email, social media, shopping habits, payment records, and device fingerprints all converge to create a persistent profile. Privacy tools work best when they address the entire data ecosystem, not just individual points of contact. The opportunity side of this is more interesting than the challenges. Zero-knowledge proofs are becoming practical for authentication without revealing personal information. You can prove you are over twenty-one without disclosing your birthdate. You can verify you are a unique human without providing a phone number. These technologies exist today, though adoption remains limited mostly to specific platforms and communities rather than mainstream infrastructure. Self-hosting is another area that has matured significantly. Running your own nextcloud instance for file storage, using pleroma or misskey for social networking, and relying on local email with a forwarder for the catch-all addresses you inevitably accumulate, this approach gives you actual control over your data. The cost is time and operational overhead, which most people do not have, but the privacy gain is real and measurable. A well-maintained self-hosted setup can eliminate ninety percent of the data collection chains that exist in standard cloud-based services.
Browser fingerprinting is the most overlooked tracking method right now. Even with all ad blockers and tracker prevention enabled, your browser configuration creates a unique signature based on screen resolution, installed fonts, WebGL renderer, time zone, and hardware details. Anti-detect browsers and privacy-focused configurations try to flatten this fingerprint, but no solution is perfect because true anonymity requires uniformity that most people will never accept in their daily browsing experience. I encountered a specific issue with a client who was using a VPN service that kept connection logs despite advertising a no-logs policy. The logs were not stored on the VPN server itself but were being routed through a third-party infrastructure partner that had its own logging requirements. This happened because the fine print referenced multiple subsidiaries and partners, and the no-logs claim only applied to the primary provider. The workaround was switching to a provider with independent audit reports and requiring them to confirm in writing that no third-party log sharing existed, which most standard VPN companies either cannot or will not do. Password managers are non-negotiable for anyone with more than five online accounts, which is probably everyone reading this. A quality password manager combined with hardware key support for two-factor authentication represents the single highest-impact privacy upgrade most people can make. The downside is that centralized password manager services become attractive targets for attackers, which is why offline or self-hosted options deserve consideration for high-risk users.
Get the Full Details

Two-factor authentication should always use an authenticator app or hardware key rather than SMS. SMS-based verification can be intercepted through SIM swapping, a technique that social engineers execute in minutes with access to your phone carrier account and basic personal information. I have seen this happen repeatedly in workplace security assessments, and it is not because carriers are negligent, it is because the verification process between you and your carrier relies on information that is easily harvested from public records and previous breaches. Incident response planning is the gap most people fail to address. When your data gets compromised, the typical reaction is panic and reactive password changes. A proper incident response plan for personal data includes pre-established steps for freezing credit, reporting breaches to relevant authorities, rotating credentials systematically rather than chaotically, and documenting what was exposed so you can respond proportionally to each category of compromised information. This process takes about two hours to set up properly but saves approximately six hours of damage control later. The reality is that complete digital privacy is impossible if you participate in modern society. Every transaction, every communication, every device connection generates some form of data trail. The goal is risk reduction, not elimination. Focus on the areas where data collection is most invasive and least justified, implement controls where they have the highest return on effort, and accept that some level of data exposure is a trade-off for participating in connected systems that most people find useful enough to tolerate.