How SDN and NFV Actually Work When You Stop Reading Vendor Marketing
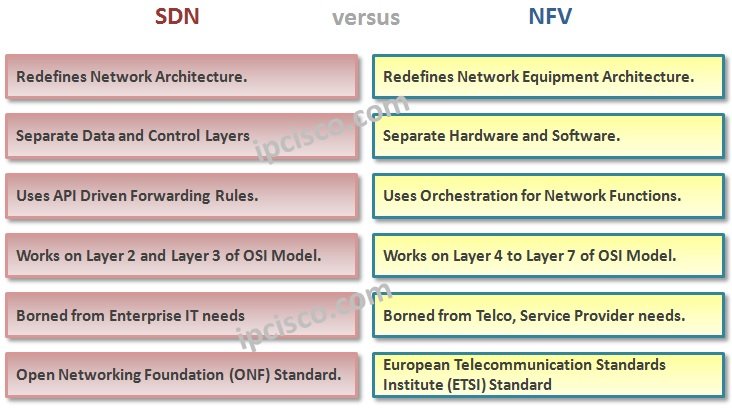
Software-defined networking and network function virtualization get thrown around a lot in this industry. People use them interchangeably sometimes, which is annoying because they solve different problems. SDN separates the control plane from the data plane. NFV replaces dedicated hardware appliances with software running on commodity servers. Put them together and you get something useful, but only if you understand what each piece actually does before you try to design around it. The control plane is the part of your network that decides where traffic goes. In traditional networking, every switch and router makes its own routing decisions using protocols like OSPF or BGP. That works fine for small setups. When you scale up, you end up with dozens of devices all running their own instance of the same protocol, converging independently, sometimes at slightly different times. SDN pulls those decisions out of the individual boxes and puts them into a centralized controller. The physical devices become dumb forwarding engines. They just do what the controller tells them. I spent two years working with a multi-site retail chain trying to roll out SDN across thirty locations. Their existing infrastructure was a mess of vendor-specific CLI configurations that nobody had documented properly. The migration wasn't a big bang moment. It was more like slowly replacing the engine on a moving car while also changing the fuel type. We started with a single PoC site, ran it for six weeks, then pushed out in waves. Each site took about three weeks to fully decommission the old control logic and hand everything over to the centralized controller. Not fast, not slow. Just what it was.
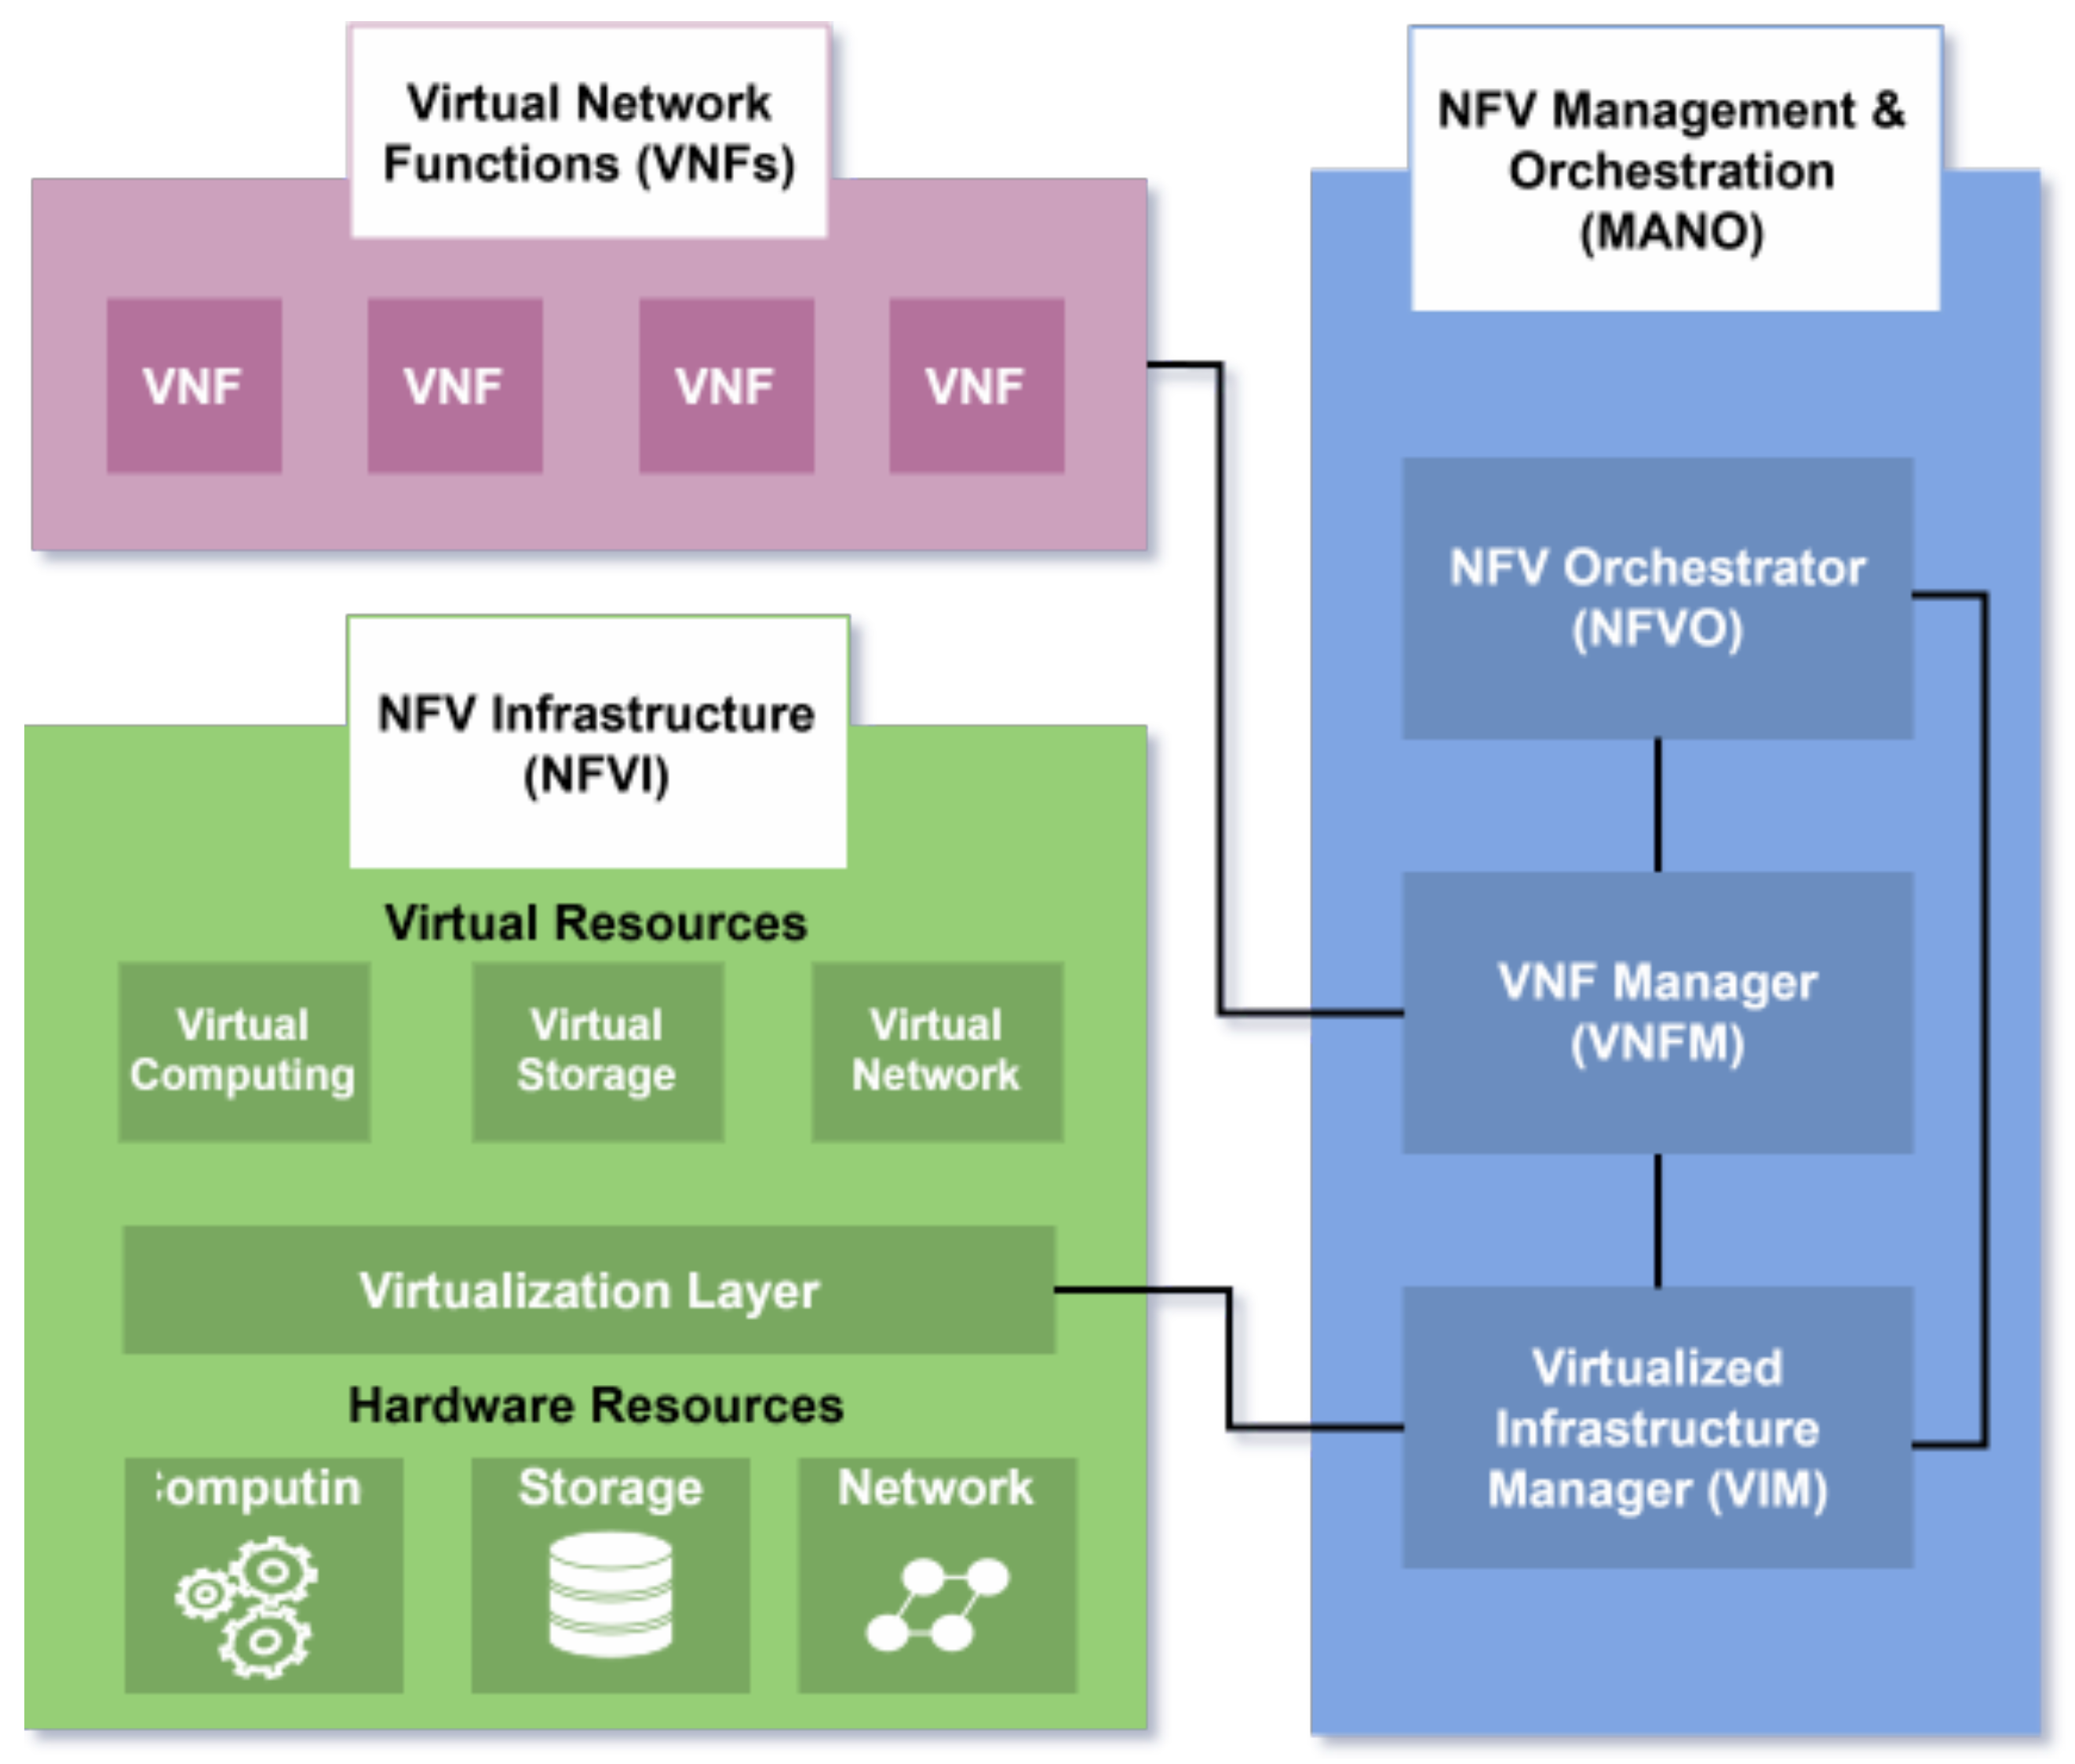
NFV is different but related. Instead of buying a dedicated firewall box, a dedicated load balancer, and a dedicated WAN optimizer, you run each of those functions as virtual machines or containers on standard x86 hardware. The idea is cost savings and flexibility. The reality is a bit more nuanced. You save on hardware procurement, yes. But you also need to handle virtual network function management, which introduces a whole new layer of complexity. You need orchestration. You need enough CPU headroom. You need to think about whether your hypervisor networking stack can handle the throughput you're pushing through it. Here is something most beginner guides don't mention clearly. NFV and SDN don't automatically make your network faster or cheaper. They change where your complexity lives. Traditional networking hides complexity inside each device's firmware. SDN moves that complexity into the controller software. NFV moves it into the virtualization layer and the orchestration platform. You are not eliminating operational difficulty. You are relocating it to a different part of your stack. If your team is good at CLI scripting and device-level troubleshooting but has never touched Kubernetes or OpenStack, you have a skills gap that no amount of licensing will fix. I ran into a specific edge case last year that took us about four days to resolve. We were running a containerized firewall function on a KVM hypervisor behind an Open vSwitch setup. The firewall policy required stateful inspection for a custom application protocol that used dynamic port allocation on the 50000-60000 range. The vFWS was dropping these connections because the state tracking table was expiring entries too aggressively. Not because of a misconfiguration we could see in the UI. The default connection tracking timeout was set to thirty seconds, but the application's keepalive interval was forty-five seconds. Every time the keepalive hit, the entry was gone and the state was reset. We ended up patching the kernel-level nf_conntrack_tcp_timeout parameter on each hypervisor host directly, bypassing the vendor's management interface entirely. The vendor support team hadn't seen this combination before. We documented the workaround and opened a feature request.
Another thing people miss about SDN is that the controller itself becomes a single point of failure, even if you configure it in a high-availability cluster. During a power outage at one of our data centers, the primary SDN controller went down and the secondary picked it up in about forty-five seconds. The network kept forwarding. Good. But the moment that failover happened, every flow table entry had to be rebuilt from scratch across all switches. That meant roughly twelve thousand flows reinstalled. It took about ninety seconds. During those ninety seconds, some connections stalled. Nothing catastrophic, but noticeable. The lesson was that HA for the controller isn't just about availability. It's about how fast the new primary can reconstruct the full state without dropping active sessions. If you are planning to implement this, here is a practical approach. Start by inventorying what you actually have. Map every device, every firmware version, every vendor. You cannot centralize control if you don't know what you are controlling. Then pick a single use case that justifies the effort. Common starting points are automating VLAN provisioning across multiple switches or centralizing firewall policy management. Don't try to boil the ocean. A well-run automation job for VLAN creation can cut a task that used to take two hours of manual CLI work down to about eight minutes, sometimes less depending on how many switches are in scope. For NFV deployments, your first decision is whether to go with a full NFV orchestrator like OpenStack or something lighter. OpenStack is overkill for small deployments. It brings a massive operational footprint. If you just need to run virtual firewalls and load balancers, look at solutions like VMware NSX, even if you aren't running a full VMware environment. It has its own issues, obviously, but the integration between virtual networking and the compute layer is mature. For more modern stacks, consider integrating your SDN controller with a container runtime like Kubernetes and using CNIs like Calico or Cilium to handle the virtual networking. This gives you a lot of the same benefits with less heavy infrastructure.
Get the Full Details

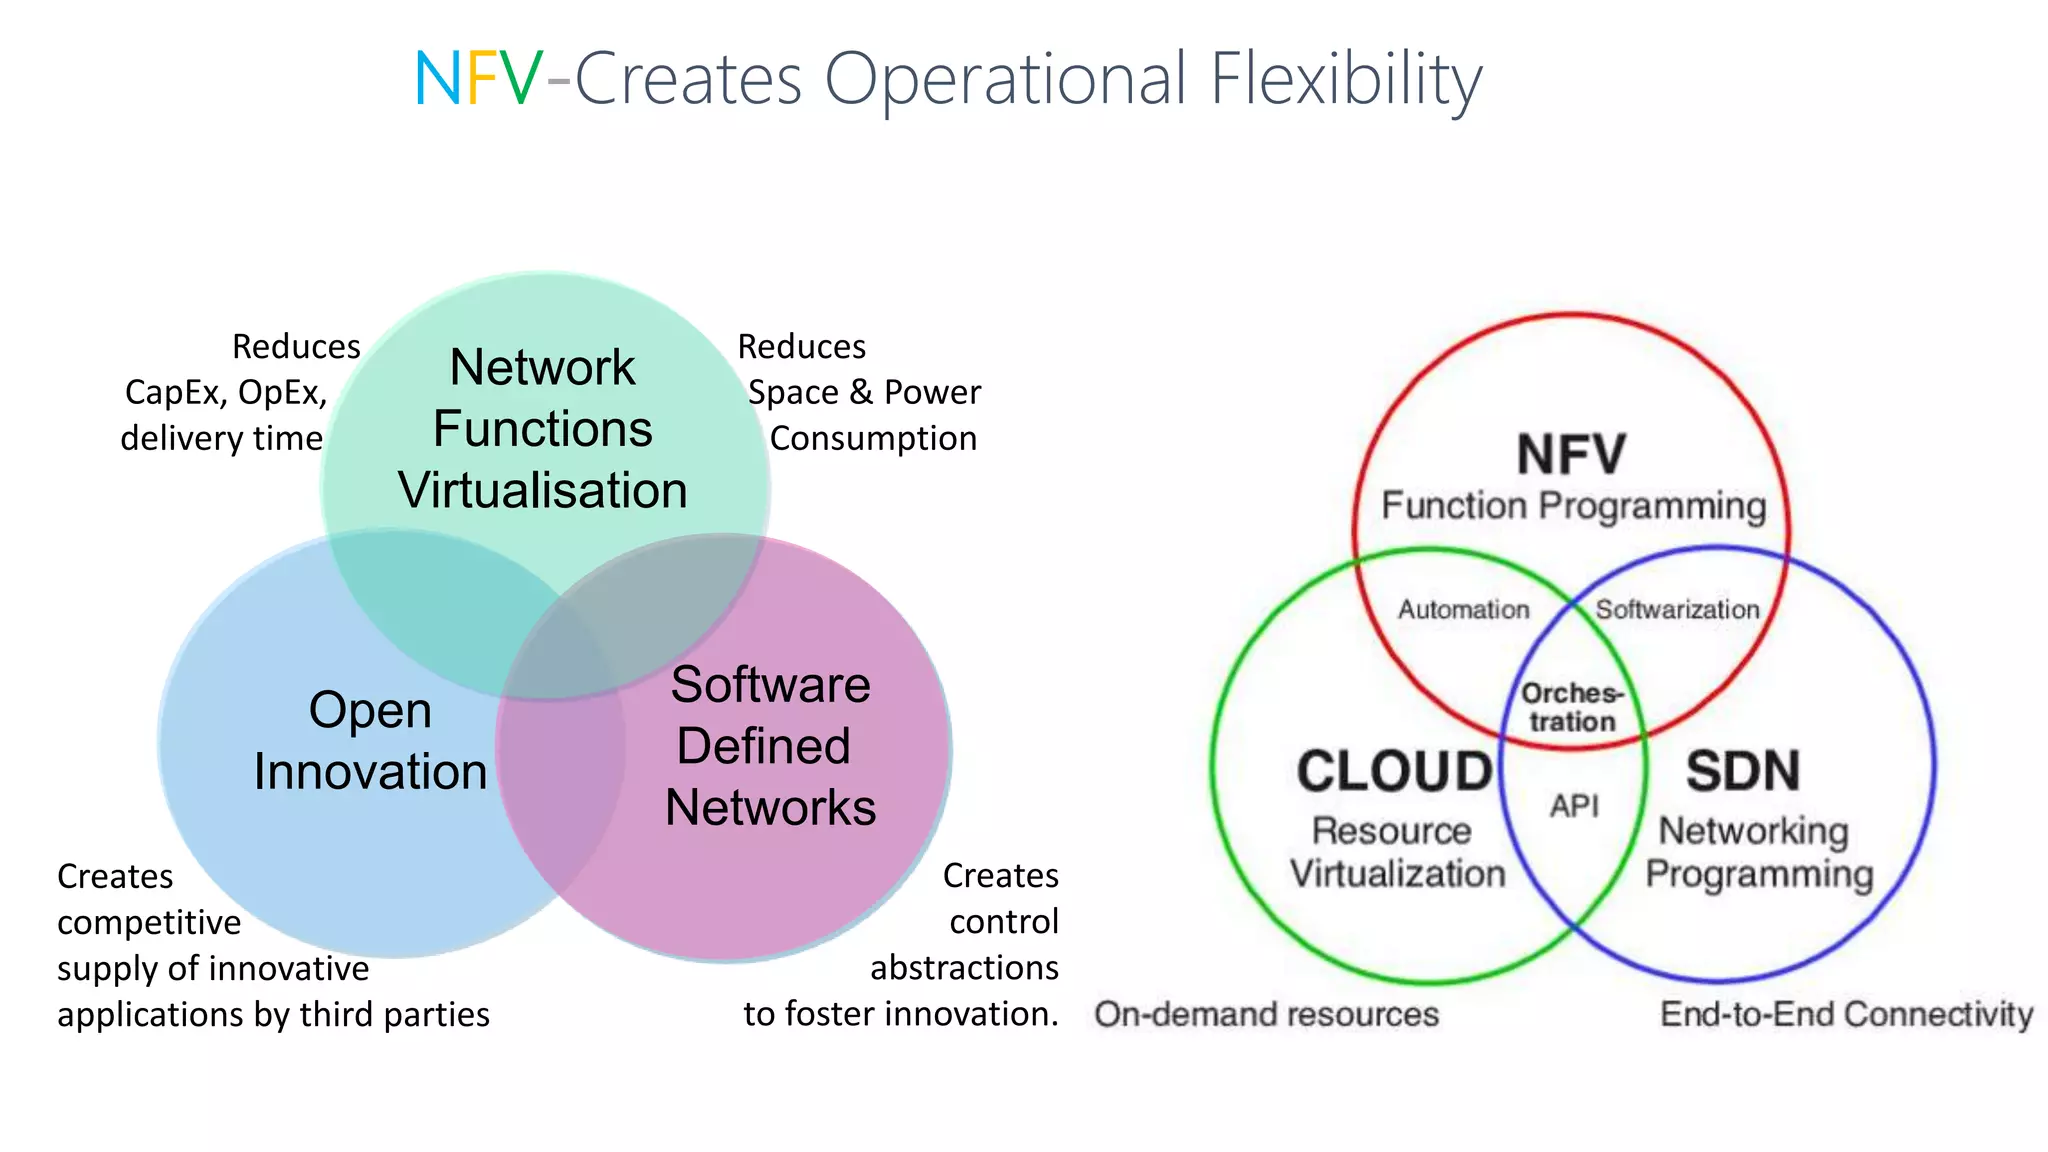
There are downsides to both approaches that vendors rarely highlight upfront. With SDN, vendor lock-in is real. The moment you commit to a specific controller, moving to a different vendor means rewriting your automation scripts, reconfiguring your northbound API integrations, and retraining your team. The open standards like OpenFlow exist, but not every vendor implements them the same way. In practice, you are often tied to the ecosystem. NFV has a different problem. Performance. Virtual functions on commodity hardware will never match the throughput of purpose-built appliances. A dedicated firewall chassis might handle forty gigabits per second. The same function as a VM on a dual-socket server with SR-IOV enabled might push twenty-five gigabits before you start seeing CPU-bound limitations. It depends heavily on your packet sizes and whether you are using DPDK acceleration. Without DPDK, expect performance to drop significantly. I would also recommend against trying to run SDN and NFV together in your first deployment if you can avoid it. Each one introduces its own learning curve. Layering them simultaneously means debugging issues where you can't tell whether a problem is in the SDN controller, the NFV orchestrator, the hypervisor, or the underlying physical network. A better path is to deploy one, get comfortable with it, then add the other on top. Maybe six to eight months apart. That gives your team time to build institutional knowledge before the problem space doubles. The networking industry isn't going back to manually configured CLI boxes. The economic and operational pressure is too strong. But the people who succeed with SDN and NFV are the ones who treat it like any other infrastructure migration. Plan carefully, test extensively, acknowledge the trade-offs, and accept that you are trading one set of problems for another. The reward is automation capability and flexibility that legacy architectures simply cannot match. The cost is that you now need to maintain software platforms instead of maintaining command line references.