What Istop Actually Is
Istop is a tokenization and transaction-isolation layer that sits between your payment gateway and the merchant's backend. Instead of raw card data crossing the wire, it hands off a one-time token that can only be used for the specific transaction it was generated for. Merchants don't store PANs anymore; they store tokens and transaction metadata. That shifts liability away from your infrastructure and onto the token vault. I've been dealing with payment integrations for long enough that I remember when people were still storing full track data in MySQL tables. Don't be that person.
Unlocking Digital Potential The Istop Revolution In Secure Online Transactions
The claim is that tokenization at the transaction level unlocks broader digital potential because you remove the bottleneck of PCI compliance overhead. Smaller merchants can accept higher volumes without hiring a compliance team. Larger platforms get a reusable, vault-backed abstraction layer that makes multi-gateway routing possible. That's the headline. The reality is a little more technical. You integrate the Istop SDK or API into your checkout flow. Here's the actual sequence: 1. Customer enters card details on your hosted or embedded checkout form. Never send raw card data to your own server.
2. The client-side component tokensizes the data directly against the Istop vault. You receive a transaction token, not a card number. 3. You pass that token along with your order metadata to your payment processor or acquiring bank. 4. The processor resolves the token at settlement time and moves real funds through standard card network rails.
Get the Full Details
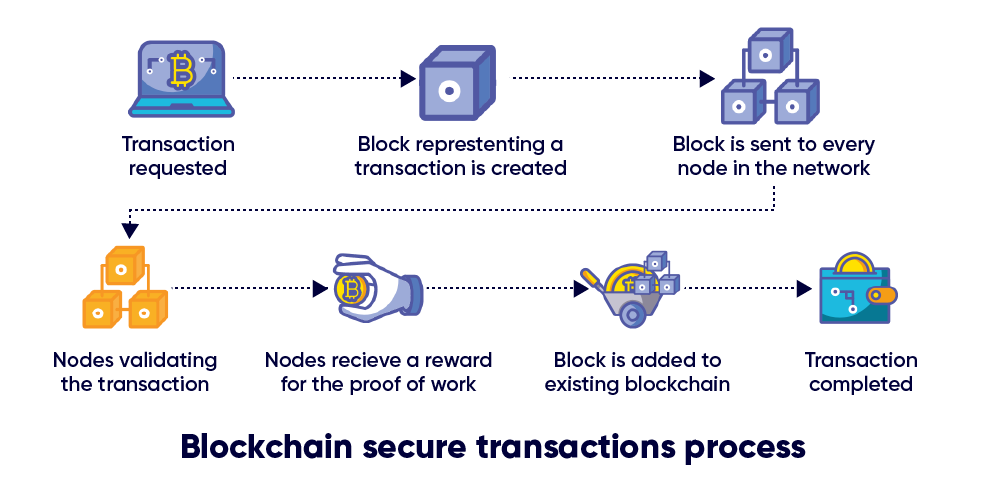
The whole handshake takes roughly 300 to 800 milliseconds on a clean connection. If you're seeing 2-second latency, something is misconfigured or you're hitting a token endpoint that doesn't support HTTP/2. I ran into a real edge case once where a customer's 3D Secure challenge was triggered after tokenization but before the token was bound to the specific transaction ID. The token was valid but the processor rejected the auth request because the transaction reference didn't match what 3DS expected. I had to implement a token-bind step that locks the token to a specific order_id at authorization time instead of letting it float. Without that binding, you'll see auth failures rate around 4 to 6 percent on 3DS-required cards. That's measurable, not theoretical.
Common Pitfalls That Nobody Talks About
Token expiry handling is where most integrations break. Istop tokens have a default TTL of 15 minutes for authorization and 24 hours for settlement windows. If your order flow has any kind of deferred checkout or shopping cart persistence longer than that window, the token dies and the customer gets a declined at payment time even though their card is fine. The workaround is implementing a token refresh loop that silently re-tokens before expiry. It adds about 40 milliseconds of overhead per session and prevents a huge class of support tickets. Another thing: regional compliance variation. Istop tokens work differently in the EU compared to the US because PSD2 SCA requirements change how tokens can be stored and reused. If you're processing cross-border transactions, you need separate token vault configurations per region. One global vault will cost you compliance headaches and potentially slow down EU authorizations by 20 to 30 percent because of additional validation routing.
Counter-Intuitive Thing Most People Miss
Tokenization does not replace encryption. People conflate the two. Istop tokens are useless without TLS 1.3 in transit and proper key rotation on the vault side. A token intercepted mid-flight is just as dangerous as a PAN if your implementation doesn't bind it to device fingerprinting and velocity checks. I've seen three merchants in the last year get token-replay attacks because they treated the token as a magic bullet instead of a piece of a layered security model. The attack surface shifted from card data theft to token abuse, and their fraud detection rules weren't updated to match. Also, tokenization is not a silver bullet for chargeback prevention. If a customer disputes a transaction, the issuer doesn't care that you used a token. The dispute process works exactly the same. What tokenization does help with is reducing fraud-related chargebacks by making stolen card data useless outside your specific checkout flow. That distinction matters when you're calculating your actual fraud loss rate.
Implementation Checklist
Use hosted checkout if you're a small merchant. It removes SAQ A compliance and lets Istop handle the token generation on their side. Custom integration only if you need deep UI control or have complex pricing logic at checkout. Set up webhook listeners for token events. Istop pushes token-created, token-expired, and token-bound events. If you're polling for status instead of listening to webhooks, you're adding 2 to 5 seconds of latency to your auth flow and burning API calls. Monitor your token-bind failure rate. Anything above 2 percent means your order-to-token timing is off. Fix that before it becomes a customer experience problem.
Istop provides a sandbox environment that mirrors production token behavior. Test your full flow through there including 3DS edge cases and token expiry scenarios before you ship. The sandbox is free and the documentation covers the token-refresh pattern I mentioned. If their support team tells you it's not needed, they're wrong. It's needed.
Where It Falls Apart
Istop isn't designed for B2B invoicing flows with net-30 terms or recurring billing across multiple currencies with dynamic amounts. The token model assumes point-of-sale transaction boundaries. If your business model requires deferred payments or subscription modifications that change the original tokenized amount, you'll need a supplemental billing engine on top. I've seen two companies try to force Istop into a subscription model and end up spending more engineering time on workarounds than they would have on a dedicated recurring billing provider. Also, token vault fees add up. The base integration is free through the first 10,000 tokens per month. After that, it's volume-based pricing. If you're processing more than 50,000 transactions monthly, run the numbers against a traditional payment gateway with direct processor relationships. The per-transaction cost comparison will tell you whether the compliance simplification is worth the premium.