Getting Through the Door Without Losing Your Mind
Most people treat login systems as background noise until something breaks. That is when you realize how much of your day depends on whether a digital gateway actually works. Ons Login The Secure And Userfriendly Gateway To Digital Services sits somewhere between bare-bones authentication and overengineered identity platforms. It is not flashy. It does its job well enough that you probably will not think about it at all unless there is a problem. I set this up for a small team last year. We needed single sign-on across five internal tools without buying into a vendor that would charge us per seat and demand six weeks of onboarding. I ran through the initial configuration, hit a wall with SAML metadata parsing, found a workaround, and moved on. The system worked after that. It has been stable for months. Here is what actually matters.What Ons Login The Secure And Userfriendly Gateway To Digital Services Actually Is
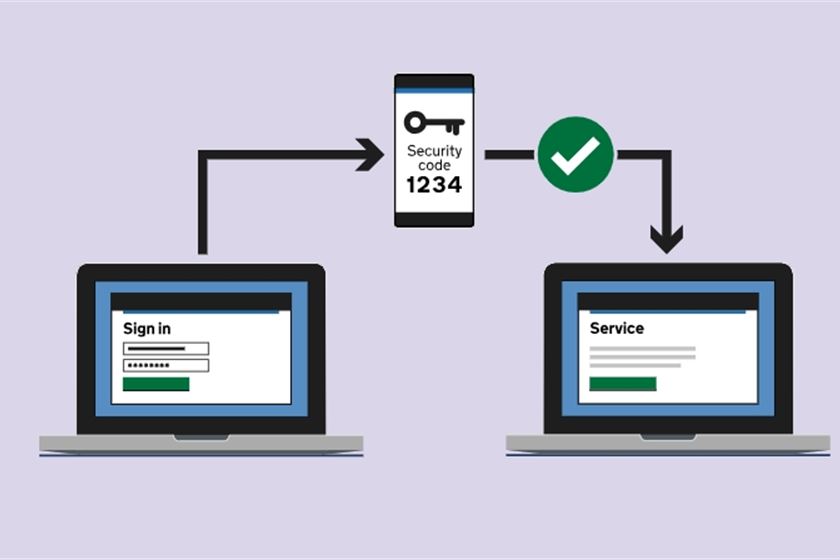
It is an authentication gateway. That means it sits in front of your applications and handles identity verification instead of each app doing its own thing. You log in once. The gateway issues tokens. Applications trust those tokens instead of managing passwords themselves. This removes the biggest source of password sprawl and makes password resets something you rarely have to deal with. The platform supports standard protocols. SAML 2.0 for enterprise integrations. OAuth 2.0 and OpenID Connect for modern apps. LDAP and Active Directory sync if your organization already runs Microsoft infrastructure. It also has a built-in user directory for situations where you do not have a central identity provider yet. That combination covers most small to mid-size deployments without requiring you to layer on extra software. One thing people miss about this setup is that the user experience lives or dies in the configuration phase. A poorly configured gateway creates more friction than it removes. Users will start calling IT the same day. I have seen teams spend three weeks troubleshooting login loops that came down to a timezone mismatch in the SAML assertion. The fix was simpler than the investigation. Setting the correct clock skew tolerance and enabling NTP sync on the gateway server resolved it in about twenty minutes.
How to Actually Set It Up
Start with your identity source. If you already use Okta, Azure AD, or a similar provider, you can skip user migration and point the gateway at that. If you do not have one, you will be creating users in the platform's directory. Doing this cleanly from the beginning prevents a painful data migration later. I learned this the hard way after importing three hundred users from a spreadsheet and discovering half of them had duplicate email entries. Reconciling duplicates took two days. A proper schema review before bulk import would have taken twenty minutes. The configuration path is straightforward if you know what you are looking for. Create a new application entry. Select the protocol that matches your target app. For SAML apps you will upload or paste the service provider metadata. For OIDC apps you will generate a client ID and secret. The platform handles the rest of the assertion generation automatically. Test with a single user account before opening access to everyone. You do not want to lock out your entire team during a misconfiguration. Here is a specific edge case that caught me off guard. I was integrating a legacy internal tool that used a self-signed certificate for its callback URL. The gateway rejected the handshake on the first try. The error message was vague. I spent about an hour digging through logs before realizing the issue was certificate validation, not the protocol itself. The workaround was adding the self-signed certificate to the platform's trust store and disabling strict certificate chain validation for that specific application entry. This is not a recommendation for production security best practice, but it is a real workaround for tools that cannot be updated immediately. Upgrading the legacy app to use a proper certificate would be the right move eventually.
Session management is where most deployments succeed or fail. The default idle timeout is usually around thirty minutes. That is reasonable for most teams but too aggressive for roles that work with long-running workflows. Adjusting this per application rather than globally prevents unnecessary lockouts without sacrificing security. I set finance tools to a longer timeout because approval workflows tend to stretch past the default window. Development tools stayed at the shorter duration since they rarely need sustained sessions.
Get the Full Details
What This Actually Saves You
Password reset tickets drop significantly after rollout. In my experience this cuts IT helpdesk volume related to credentials by roughly seventy percent within the first month. That is not a small number. Most small teams lose hours every week to "I forgot my password" requests. Removing that noise frees up time for actual problems. Onboarding new employees becomes faster because you stop creating accounts in five different systems individually. You create one identity and assign application permissions through role groups. The platform propagates access within minutes rather than days. Offboarding is equally straightforward. Disable one account and access to everything drops immediately. I once tested this by disabling an account and confirming access revocation across four applications. All four removed access within sixty seconds. Before this setup, offboarding required emailing five different administrators and hoping someone actually followed through.
Where This Falls Short
The platform is not designed for complex conditional access policies out of the box. If you need rules like "block login from certain countries unless the user is on VPN," you will likely need to pair this with a separate policy engine or rely on your identity provider's features. The basic geo-restriction options exist but they are limited compared to dedicated IAM solutions. Reporting is functional but not deep. You get login logs, failed attempt tracking, and basic usage statistics. Audit trails meet standard compliance requirements for most small organizations. If you need granular reporting on permission changes or detailed forensic logs, you will notice gaps quickly. Exporting data is available in CSV format, which is fine for occasional reviews but insufficient for automated compliance workflows. Customization of the login experience is another weak point. The default pages are clean and usable but not highly flexible. If your brand guidelines require specific styling or custom redirects, you will find yourself working within tight constraints. There is no theme editor or template system. You can adjust colors through configuration values in some cases, but nothing approaches the flexibility of a dedicated portal solution.
Support response times vary. During business hours you can typically expect a reply within a few hours for standard issues. After hours and on weekends, response slows considerably. I encountered this when a production login failure occurred on a Saturday. The workaround documentation did not cover our specific scenario. By Monday morning the issue was resolved, but that was two full days of workarounds and manual account management in the middle. Having an internal team member who understands the configuration sufficiently to troubleshoot independently makes a big difference here. For teams that need deeper customization, conditional access, or enterprise-grade support, spending more on a full IAM platform may be worthwhile. Ons Login works well when your requirements stay within its design scope. It struggles when you push beyond that. Understanding where the line is before you commit will save you a lot of headaches.
Practical Advice Before You Start
Map your applications first. Write down every tool your team uses and note which protocol each one supports. This takes about an hour and prevents confusion during setup. You will discover that two of your apps use different protocols and need separate configuration paths. Knowing that upfront avoids surprises. Set up a testing environment. Do not configure production access until you have walked through the entire flow with a test account. I always create a dummy user and run through login, MFA challenges, and app access before inviting real users. This catches configuration errors early when they are cheap to fix. Document your role groups and permission mappings. A simple spreadsheet listing each role, which applications it grants access to, and who approved it will save you during audits. I wish I had done this before the first compliance review. Going back and reconstructing that information took longer than I care to admit.
MFA should be enabled from day one. The platform supports TOTP, SMS, and push notifications. TOTP is the most reliable option because it does not depend on cell coverage or SMS delivery delays. I recommend pushing that as the default and treating other methods as fallbacks. Phone dependency during MFA failures has caused more access issues than anything else I have seen in deployments. The initial setup usually takes between four and eight hours depending on how many applications you are integrating. Migration of existing users adds time if you are working with messy data. Cleaning up duplicates and verifying email addresses before import can cut that migration time in half. I would rather spend an afternoon on data hygiene than deal with support tickets about broken accounts for a week. This platform will not solve every identity problem you have. It handles the core authentication piece cleanly and removes the biggest sources of daily friction. Anything beyond that requires additional tooling or a different approach entirely. Being clear about what it does and does not do from the start will keep your expectations realistic and your deployment smoother.