Windows 10 Proxy Configuration: What Actually Happens When You Turn It On
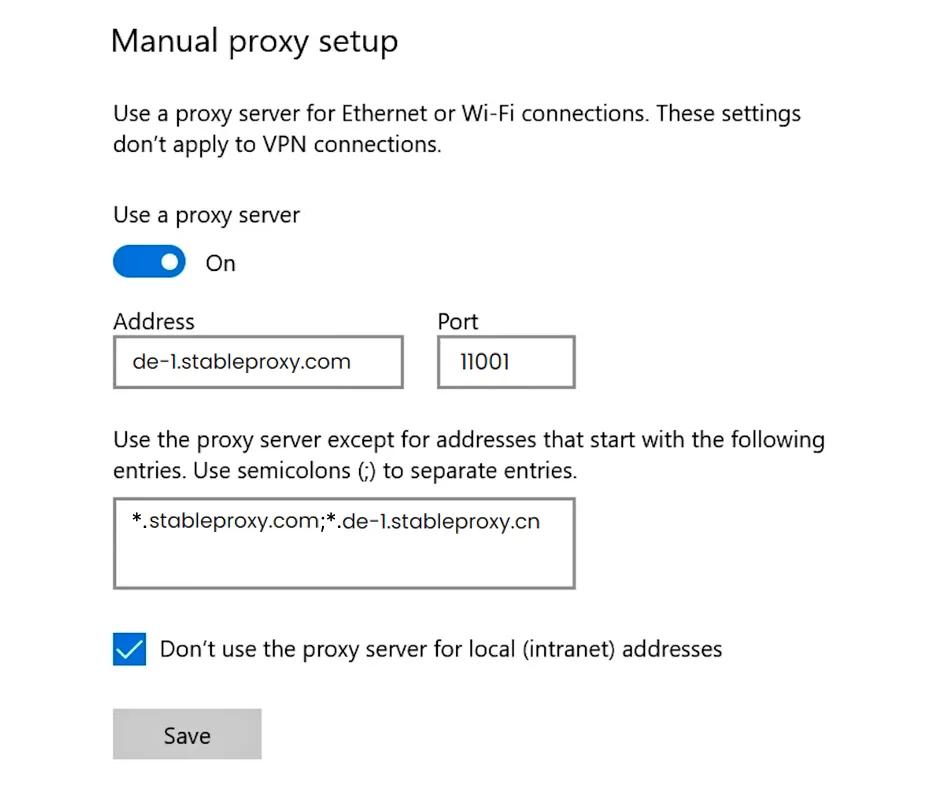
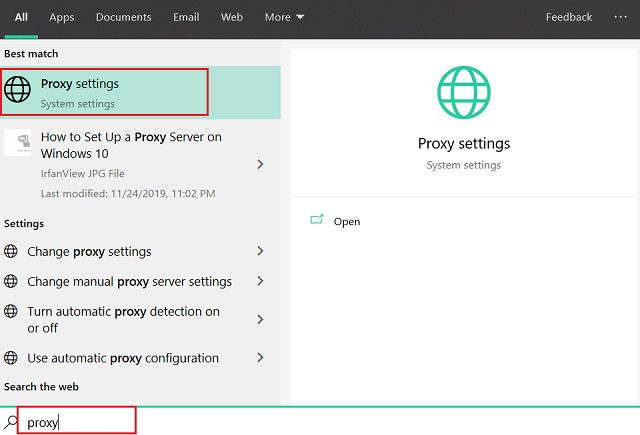
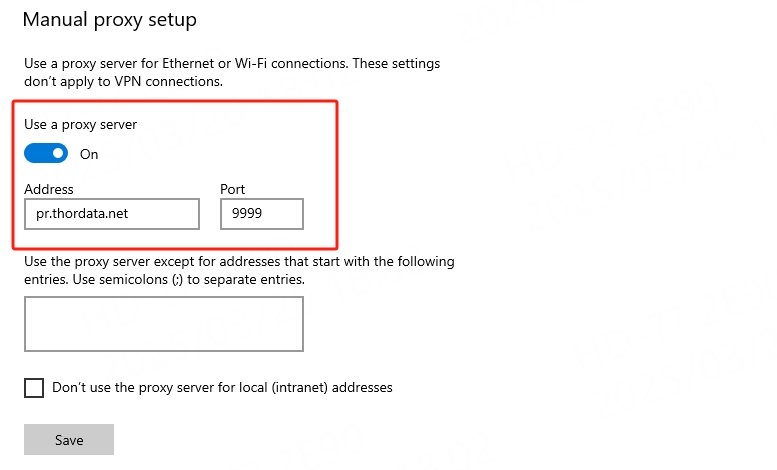
Most people stumble onto proxy settings when they get blocked from a website at work or notice their connection is throttled. The settings page is simpler than it looks, but the devil is in the details that nobody documents. I spent about three weeks last year debugging a proxy chain that kept dropping sessions every forty minutes across an entire engineering team, so I learned a few things the hard way. To get started, open Settings and navigate to Network and Internet, then select Proxy from the left sidebar. Toggle Use a proxy server to On and enter your proxy address and port in the fields below. That's the surface-level version. Here's what actually matters: Windows will apply this to every application that respects system proxy settings, which includes Edge, Chrome, and most UWP apps. But desktop apps written by individual developers often ignore the system proxy entirely. Your proxy won't help those unless you configure them manually or use a routing tool.
Unlock The Power Of Windows 10 Setting Up A Proxy Server A Simple Guide To Bypass Restrictions And Boost Productivity
There are two modes on this screen. The automatic setup uses a PAC file, which is a JavaScript snippet that tells your browser exactly which requests should go through the proxy and which should go direct. The manual setup is just a single address and port. PAC files are more flexible but introduce a whole class of bugs. If your PAC script has even a syntax error, Windows falls back to no proxy at all and you're left wondering why nothing changed. I once spent four hours chasing a proxy issue only to discover the PAC file was returning undefined instead of a string for one edge case in the return rules. When using manual proxy configuration, pay attention to the Exclude addresses you do not want to use the proxy for box. By default, Windows excludes localhost and private network ranges like 192.168.x.x and 10.x.x.x. If you're testing something on your local machine while the proxy is active, skip this exclusion and add the addresses manually. Otherwise you'll hit localhost services fine but everything else routes through the proxy, which creates confusing asymmetry. The real advantage of a proxy on Windows 10 isn't just bypassing restrictions. A properly configured proxy gives you centralized logging, bandwidth control, and the ability to intercept and inspect traffic. For a small team, setting up a transparent proxy with something like Squid or a commercial alternative lets you monitor what's actually leaving the network. I ran a Squid instance on a spare machine for about eight months and caught several employees downloading pirated software through direct IP connections that their browser would have flagged but their standalone installers bypassed entirely.
If you're using a proxy to bypass geo-restrictions or workplace blocks, be aware that Windows 10 caches DNS resolution independently of the proxy. This means if you resolve a domain before switching your proxy on, the cached IP might still route through your old path. Clear your DNS cache with ipconfig /flushdns after changing proxy settings. It takes two seconds and saves about twenty minutes of head-scratching. Another thing people miss: Windows 10 has a separate proxy configuration for the Microsoft Store and Windows Update. These don't always honor the same settings you configure in Network and Internet. If your proxy blocks certain traffic at the network level, the Store and Update services can fail silently without any obvious error message. You'll see spinning wheels or timeout errors that look like network problems but are actually the proxy dropping connection attempts from services that don't route through your configured proxy. For enterprise environments, Group Policy is the proper way to push proxy settings rather than having users configure them manually. The policy path is User Configuration followed by Administrative Templates then Windows Components and then Network. The option to force proxy settings through GPO takes effect immediately on the next policy refresh and doesn't get overwritten by individual user changes unless they have admin rights to modify the settings page themselves. I've seen too many helpdesk tickets go unresolved because someone manually typed a wrong port number and then couldn't figure out why the IT-deployed settings weren't sticking.
Get the Full Details
The main limitation nobody warns you about is latency. Every request gets wrapped, forwarded, and unwrapped. A direct connection to a CDN node might take 30 milliseconds. Through a proxy that's two hops away, it could be 120. For most browsing this is imperceptible. For real-time applications, online gaming, or large file transfers, the overhead adds up. If productivity is your goal and your proxy is geographically distant from your actual servers, you might end up slower than before you started. A transparent proxy on the local network solves some of this because traffic never leaves the building before hitting the proxy. But it requires router-level configuration or a dedicated device. If you're just running a proxy server on a VM inside your office, the latency difference is negligible and the management overhead is worth it. Some proxies also log your traffic. If you're using a free public proxy, assume everything you send through it is visible to the operator. This includes passwords, API keys, and any unencrypted HTTP traffic. Always use HTTPS destinations when possible. The proxy can still see the domain you're connecting to through SNI in the TLS handshake even if the content is encrypted, so pick a proxy provider you actually trust if you're handling sensitive work.
One more practical detail: if you need to switch proxies frequently, writing a small PowerShell script to toggle between configurations saves you from clicking through the settings UI every time. Set-ItemProperty on the registry path HKCU:\Software\Microsoft\Windows\CurrentVersion\Internet Settings with ProxyEnable, ProxyServer, and ProxyOverride lets you script the whole thing. I keep a pair of scripts on my desktop for switching between my home proxy and my work proxy. Takes about three seconds to run instead of the forty-five seconds it takes to navigate the GUI. If your main goal is simply blocking sites at the network level for a small office, a proxy is overkill. A DNS-level filter like Pi-hole handles that faster and with less infrastructure. Proxies shine when you need per-application control, traffic inspection, or authenticated access logging. Know what problem you're actually solving before you build the solution.