The IPA File Problem Nobody Warns You About
Most developers treat the .ipa as just a zip file with a different extension. It is, technically. But the moment you actually try to manage one at scale, the gaps in your understanding become expensive. I spent three weeks debugging a distribution failure that traced back to an outdated provisioning profile baked into an archive from four months ago. The build succeeded. The icon looked right. App Store Connect rejected it with a code-signing error that made zero sense until I opened the payload and checked the embedded.mobileprovision file. Mastering the iOS package archive isn't about memorizing Xcode menus. It's about understanding what lives inside that file and how each layer affects deployment.
Unlock The Power Of Ipa Mastering The iOS Package Archive For Flawless App Deployment
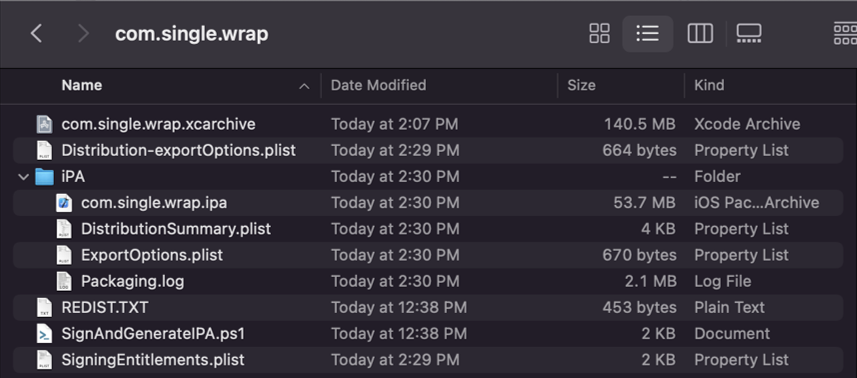
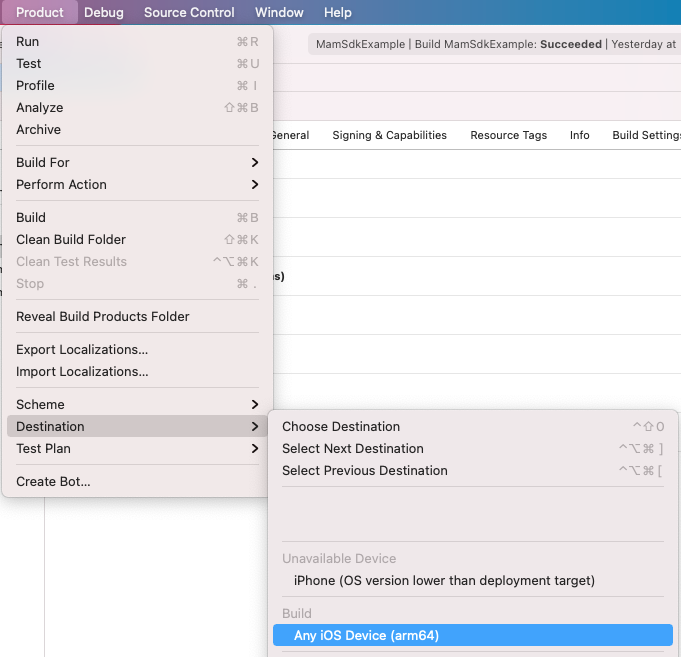
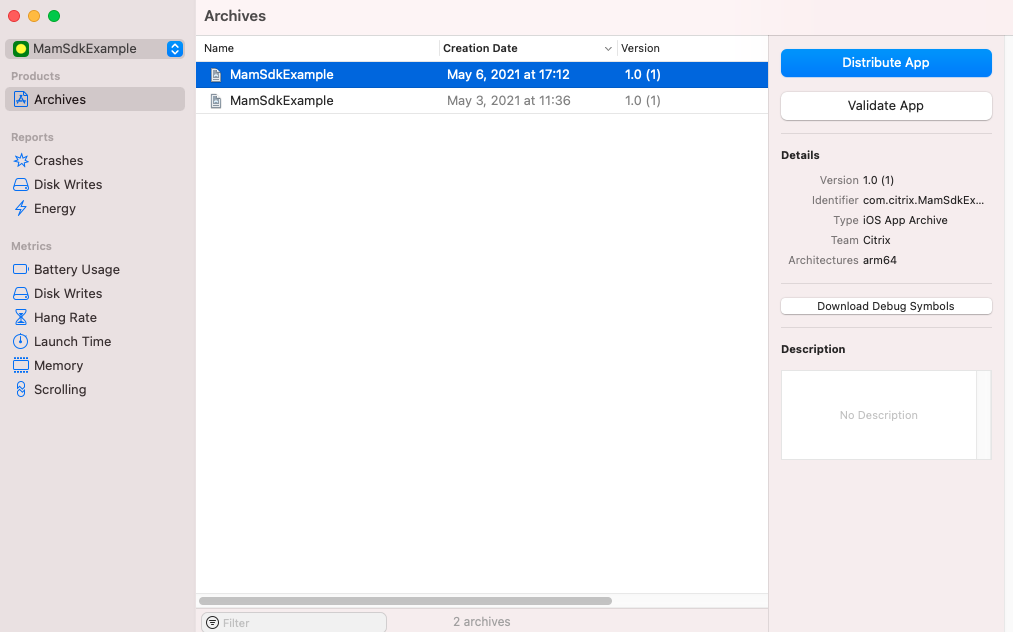
An .ipa file is built through Xcode's archiving system. When you select Product > Archive, Xcode bundles your compiled app binary, asset catalogs, embedded frameworks, entitlements, and the signing certificate into a single package. The result goes into your Organizer window, where you can export it for Ad Hoc, Enterprise, or App Store distribution. Simple in theory. The details are where things break. The first thing you need to understand is the difference between your development signing configuration and your distribution signing configuration. These are not the same. Your development profile might grant broad permissions like push notifications and entitlements that your distribution profile explicitly strips out. I once deployed a staging build using my development certificate by accident. The app installed fine on test devices, crashed immediately on release candidates, and the error logs pointed to a missing entitlement that wasn't in my distribution profile. Took me two days to realize the profile mismatch was the root cause.
What Actually Lives Inside An IPA
Open any .ipa with a decompression tool and you will see the following structure at the top level: Inside Payload/ your app bundle contains the executable, Info.plist, embedded.mobileprovision, and any nested frameworks or bundles. The embedded.mobileprovision file is the most common source of deployment failures. It encodes your team ID, bundle identifier, certificate fingerprint, expiration date, and allowed device profiles. When this file is stale or mismatched, the App Store will reject the upload or the device will refuse to install it. Xcode manages this file automatically during the archive process, but it only manages what you tell it to manage. If you switch teams, update your bundle identifier, or rotate your distribution certificates without clearing your derived data, you will get silent failures. The archive appears to build cleanly and then fails at a weird stage like upload validation or TestFlight distribution.
Get the Full Details
The Export Process And Where It Goes Wrong
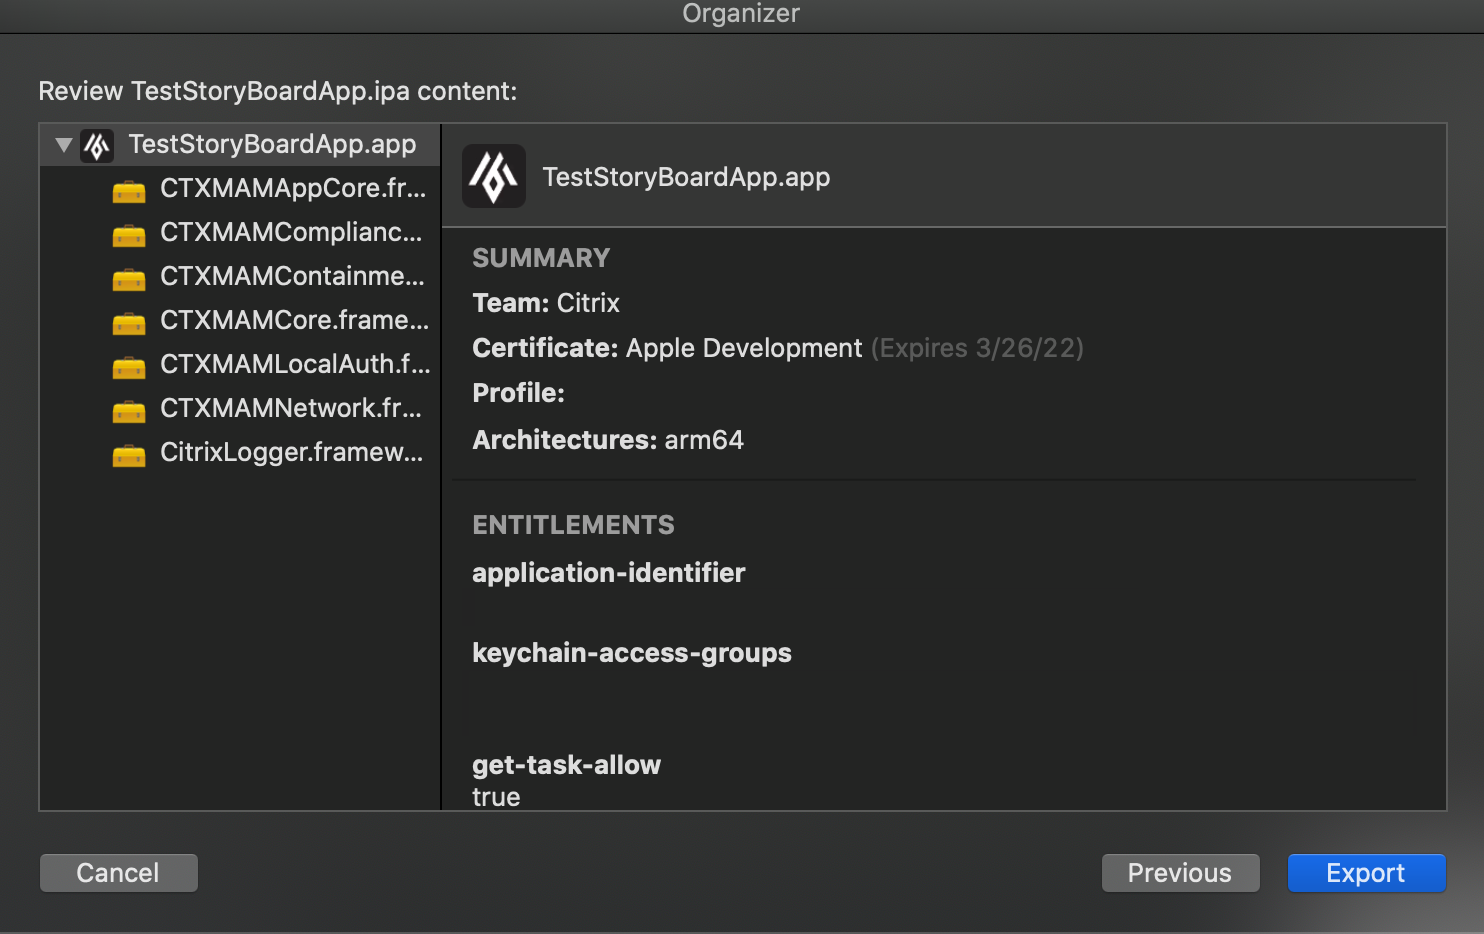
Exporting from the Archive window in Xcode gives you two paths. The first is the quick Distribute App button, which walks you through Apple's recommended options. The second is Export > Custom, which lets you select your provisioning profile manually and control the signing style. Most teams use the first option and then wonder why their deployment pipeline breaks in CI environments. The quick export method stores your signing settings in a local Xcode configuration file. Those settings do not transfer between machines. This means your local archive export works perfectly, but your Jenkins or GitHub Actions pipeline uses different credentials and produces a different signing outcome. The app itself is identical. The metadata around it is not. I solved this by switching to xcodebuild with explicit parameters instead of relying on the GUI export. The command line approach uses flags like CODE_SIGN_IDENTITY, PROVISIONING_PROFILE_SPECIFIER, and EXPORT_METHOD to lock in exactly what you want. It takes about three minutes to set up the build script correctly, but after that every build produces identical output regardless of which machine runs it. That consistency is what matters when you are handing off builds to QA or uploading to TestFlight regularly.
Debugging A Real IPA Failure
Here is a specific case that cost me an afternoon. We were deploying an app with a custom URL scheme registered in our entitlements file. The build passed. The archive succeeded. App Store Connect showed the processing status stuck at "Processing" for over two hours, which is already a red flag. When it finally failed, the error message mentioned a code signature issue with a specific framework inside our app. I opened the .ipa, navigated into Payload/, right-clicked the app bundle and selected Show Package Contents. I checked the embedded.mobileprovision file against our distribution profile in the Apple Developer Portal. They matched. I checked the Info.plist against the entitlements. They matched. I ran codesign -dvvv on the app binary and got a detailed signature dump. Everything looked correct. The problem was in a dynamically linked framework that I had added to the project. That framework had its own code signature, and when Xcode re-signed the main app binary during export, it did not re-sign the nested framework because the framework's build settings said it was already signed. The framework was compiled with my development certificate, not my distribution certificate. The mismatch triggered the App Store rejection.
The fix was adding ALWAYS_EMBED_SWIFT_STANDARD_LIBRARIES = YES to the framework's build settings and forcing a full rebuild with EXCLUDED_ARCHS removed. After that, every nested binary was properly re-signed during the export process. I learned to check every embedded framework's signing configuration before creating an archive from that point forward. I also added a post-build validation step that runs codesign --verify --deep on the exported .ipa and fails the pipeline if any nested binary has an invalid signature.
Common Pitfalls That Beginners Miss
One counter-intuitive issue is that having too many valid signing identities in your keychain can cause Xcode to pick the wrong certificate silently. If you have multiple development certificates or outdated distribution certificates floating around, Xcode may use an older one that looks valid but does not match your current provisioning profile. Clear out expired certificates from your keychain and refresh your provisioning profiles in the Apple Developer Portal before each major build cycle. Another issue is incremental builds. Xcode sometimes skips re-signing parts of your app during incremental compiles. This is not a bug, it is an optimization. But it means your archive might contain binaries signed with mismatched certificates if you built incrementally before archiving. Clean build folder before archiving when you are working on a release build. It adds two or three minutes to your workflow and prevents an hour of troubleshooting later. The third pitfall involves third-party SDKs and their embedded frameworks. Many popular SDKs ship with pre-compiled dynamic frameworks that carry their own signing. When you integrate them into your project, Xcode embeds them during the archive. If the SDK maintainer updated their framework between the time you last archived and now, and you did not clear your DerivedData folder, you may be embedding an old signed version alongside new unsigned code. This causes signature chain validation failures that are nearly impossible to diagnose without checking the timestamp and issuer of each embedded binary.
What IPA Mastering Cannot Fix
There are scenarios where no amount of IPA knowledge will help you. If your provisioning profile has expired, updating the archive settings will not revive it. If your bundle identifier conflicts with another app in the App Store Connect catalog, re-signing will not resolve it. If your app binary crashes due to an architecture mismatch on newer devices, the .ipa structure is irrelevant. These are infrastructure and product problems, not packaging problems. Additionally, the .ipa format itself is somewhat legacy. Apple has been pushing developers toward the XCFramework and the new App Store Connect upload API that accepts .xcarchive bundles directly. The manual IPA export process is still necessary for Ad Hoc and Enterprise distribution, but for pure App Store delivery, you can bypass the .ipa entirely and upload the archive directly from Xcode or through the API. This reduces one variable in your deployment pipeline and eliminates the middle step where most signing issues appear.
Practical Workflow That Actually Works
Here is what I use day to day. I maintain a clean keychain with only active certificates. I refresh provisioning profiles weekly. I use xcodebuild with explicit signing parameters for all production builds. I run codesign validation on the output before uploading anywhere. I clear DerivedData monthly or whenever I add a new framework dependency. I keep a log of which profile and certificate were used for each successful production archive so I can cross-reference if something goes wrong later. This is not glamorous. It takes more initial setup than relying on Xcode's default behavior. But it has never produced a failed upload due to signing issues in the eighteen months I have been running it. The alternative is spending hours digging through error messages that point in the wrong direction.

The Short Version
IPA mastery comes down to three things: knowing what the file contains, controlling how it gets signed, and validating the result before you submit it. The signing configuration is the part most people rush through. Treat it with the same care you give your code. The archive is only as good as its metadata, and the metadata is only as good as the certificates behind it.