Smartscreen is more annoyance than protection for most power users
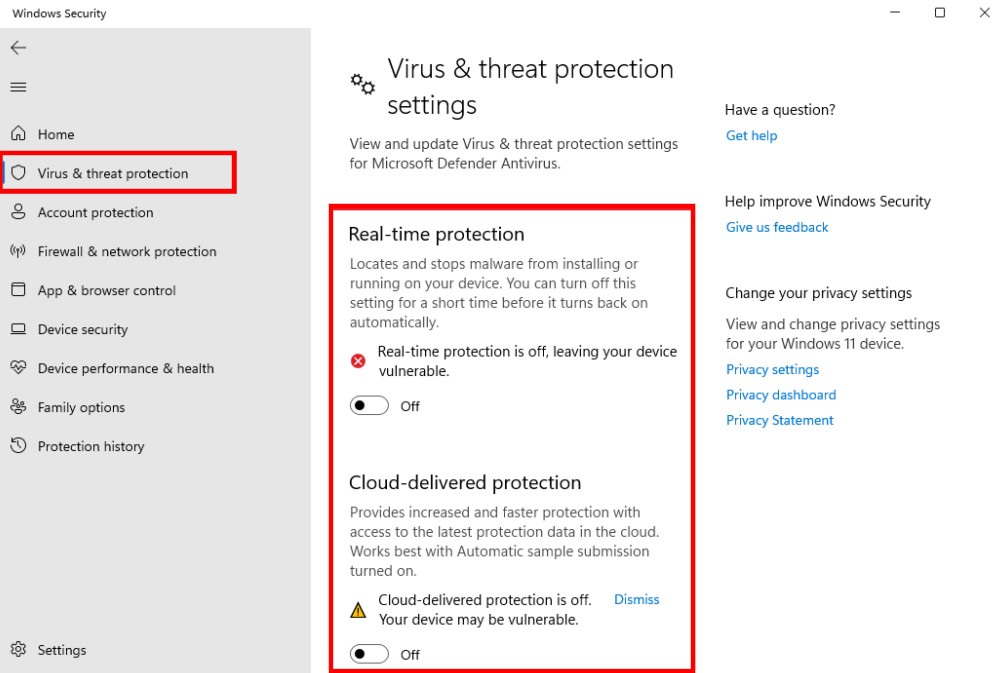
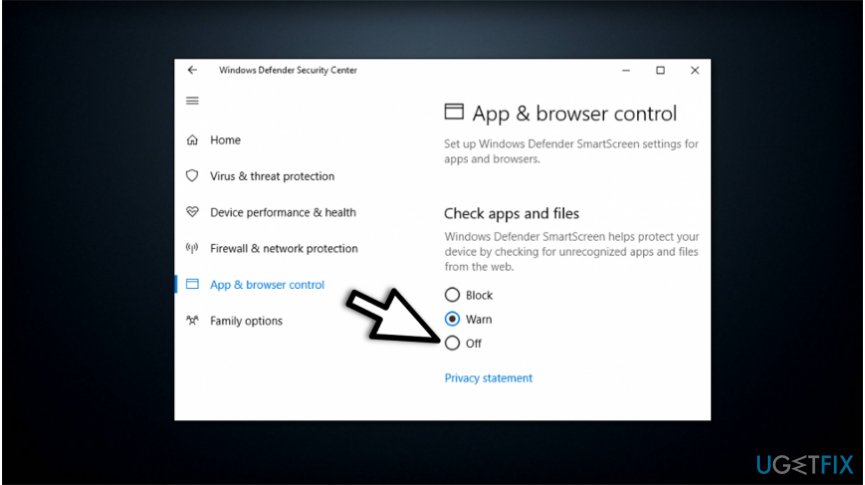
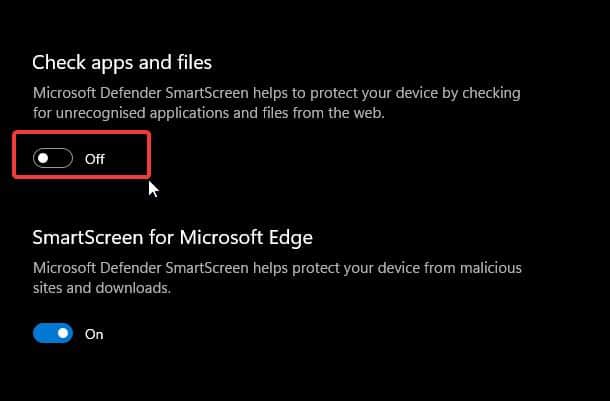
I disabled it on my main workstation after dealing with a blocked installer that was clearly legitimate. The workflow is straightforward, but the controls are spread across two or three places depending on what you want to gate. Open Settings, navigate to Privacy and security, then click Windows Security. From there you launch the Windows Security app and select Virus threat protection. The toggle for Smartscreen sits under App and browser control. You can turn it off for both Store apps and browser behavior, or limit it to just one lane. The quick settings link at the bottom of the same page works too, but some machines show a slightly different layout depending on the build. I use this on a machine where we run internal tooling that gets flagged constantly. One specific edge case I ran into recently involved a PowerShell script that invoked a signed executable from a network share. SmartScreen still threw the blue "more info" block even though the file had a valid code-signing certificate and the registry key was set to disabled. The workaround was to add the folder path to the Windows Defender exclusion list under Excluded folders, then restart the smartscreen process using taskkill /f /im msedge.exe or whatever browser was triggering the check. After that, the prompt stopped appearing. It took about ten minutes total.
The other common pitfall is that group policy overrides can silently re-enable Smartscreen on the next policy refresh. If you're managing this across multiple machines or using Intune, the per-user toggle you flipped in Settings isn't permanent. You need to deploy the corresponding policy preference under Computer Configuration or User Configuration to lock it in. The policy path is Administrative Templates\Windows Components\File Explorer\Configure Windows Defender SmartScreen and the setting name is Enable Windows Defender SmartScreen. Set it to Disabled and force gpupdate /target:computer or let the endpoint management tool push it out. There are real tradeoffs here. Disabling SmartScreen removes the phishing URL warnings in Edge and Chrome, blocks the download reputation check before execution, and stops the app reputation scan for non-Microsoft installers. That means a malicious .exe dropped onto the desktop won't get the familiar warning dialog. On the other hand, Microsoft Defender itself still runs file scans and ransomware protection in the background regardless of SmartScreen status. The two are not the same defense layer. Removing SmartScreen does not disable Defender. Another thing most people miss is that SmartScreen enforces different rules for Store apps versus desktop apps. Turning it off completely also disables the Store app reputation check, which catches some sketchy sideloaded UWP packages. If you only care about blocking desktop installers, you can leave the Store component on. The UI doesn't make that distinction obvious, but it works independently.
I also recommend keeping SmartScreen on for the browser if you or anyone else on the machine still uses it for general browsing. The phishing protection catches more threats than most users expect, and disabling it entirely leaves Edge's URL reputation engine blind. A middle-ground approach that works well is to keep browser SmartScreen enabled while disabling the app portion. That blocks the noisy prompts on known-safe tools without stripping the web safety net. Registry method exists if you prefer editing keys directly. Navigate to HKLM\SOFTWARE\Policies\Microsoft\Windows\System and create EnableSmartScreen as a DWORD value set to 0. Apply it, reboot, and verify under Settings that the toggle reflects the change. This is the method that survives most Group Policy refreshes unless an admin template explicitly overrides it, which is why the policy route is safer for managed environments. A final note on reliability. Some third-party antivirus suites install their own SmartScreen-style filters on top of Defender. Disabling the Microsoft version doesn't touch those, so you might still see blocking prompts even after the toggle is off. Check the security center for any additional installed products before assuming the job is done.
Get the Full Details