Sign in with Apple isn't hard, but the documentation makes it look harder than it actually is
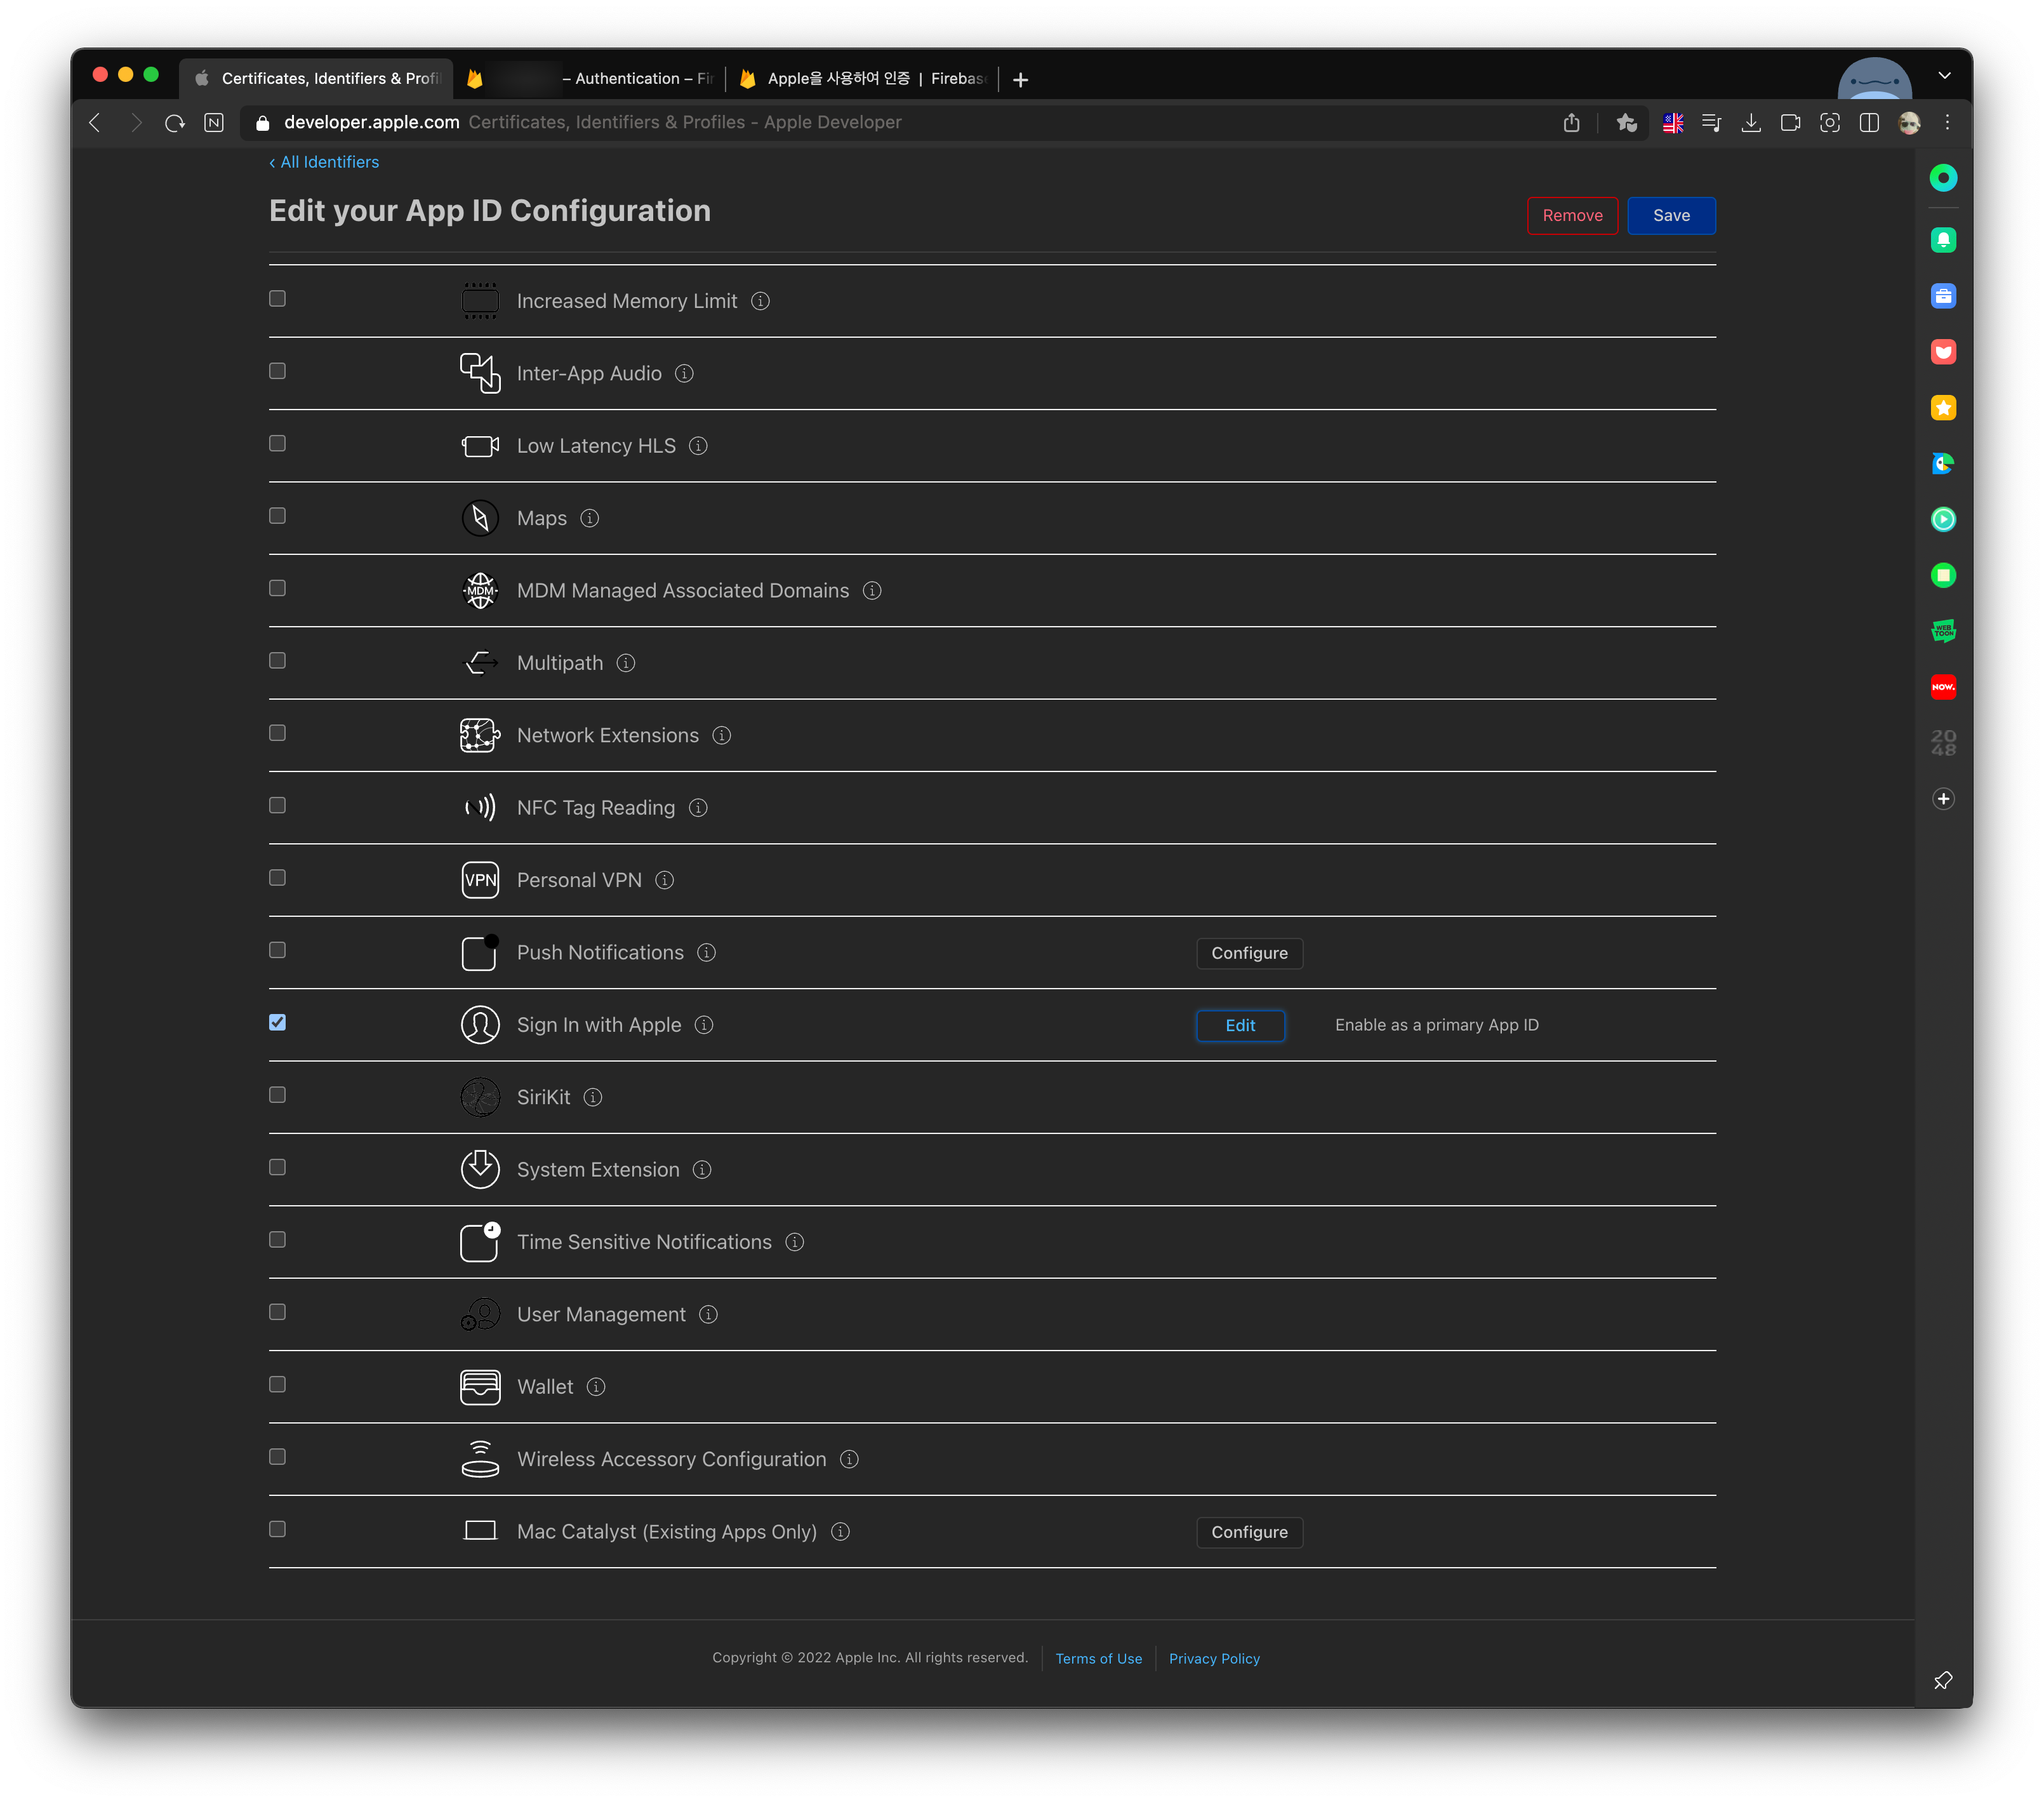
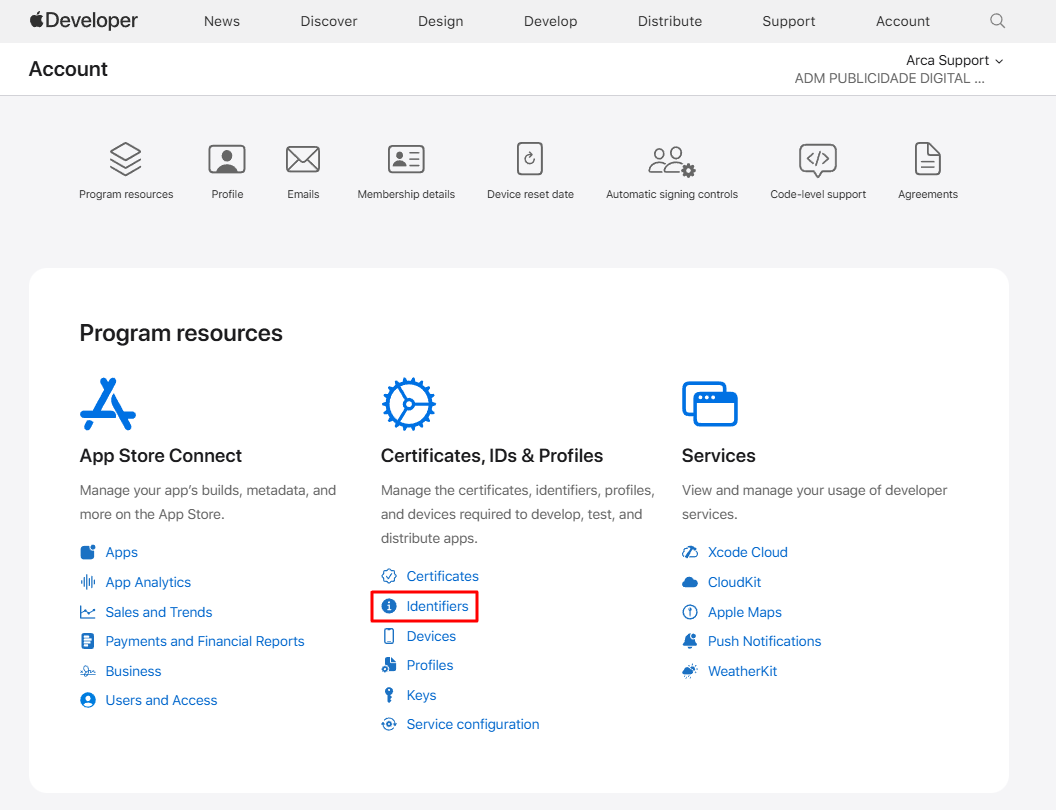
You need to set up an apple-app-site-association file on your server, configure a bundle ID with the Sign in with Apple capability, and handle two different auth flows depending on whether you're building for web or native. That's basically it. The stuff people get stuck on is usually the JWT token verification or forgetting to redirect users after they sign in, which is pretty basic but easy to miss if you haven't done it before. When I first integrated Sign in with Apple into a production app, I assumed the worst case was just wiring up the AppleIDCredential framework like you'd do with Firebase or Auth0. What actually tripped me up was that Apple requires HTTPS for every redirect URI, including localhost during development, and if you miss that even once your whole flow silently fails without any useful error message. I spent about four hours debugging something that boiled down to a missing certificate for my dev server. After that I always make sure mkcert is installed and running before touching any Apple-specific code. The server-side piece works by exchanging the authorization code you get from Apple for a JWT using your private key. That private key is generated through the App Store Connect portal under Keys. You download the .p8 file once and store it securely. Every time you need to verify the user's identity, you create a JWT with the header alg=ES256, the issuer set to your team ID, the key ID, the audience set to https://appleid.apple.com, and a subject that's your bundle ID. That token gets posted to https://appleid.apple.com/auth/token and you get back the user's email and a unique user ID, plus an ID token if you requested the open ID scope. The email field can come back as null if the user chose to hide it, which is Apple's privacy feature, not a bug in your code. You'll see this happen to maybe 30% of users and you need to handle it gracefully or your account creation logic will break.
For the client side, you create an ASAuthorizationAppleIDProvider instance and call performRequests with an ASAuthorizationAppleIDRequest. That request supports three scope parameters: full name, email, and the offline use flag. If you set the offline use flag, Apple gives you a refresh token that you can use to get new access tokens without bothering the user again. This is useful for background services that need to authenticate periodically, though most apps don't actually need it. The response comes back as an ASAuthorizationAppleIDCredential object containing the identity token, the authorization code, and optionally the user's real name and email. You pass the authorization code to your backend to exchange for the JWT session, and you store the user's Apple ID locally or in your database using the sub field from the JWT payload as the primary identifier. That sub value is stable per user but different across apps, so don't treat it as a global user ID. The web flow is different from the native one. On the web, you use the Sign in with Apple JavaScript SDK, which is essentially a wrapper around the ASAuthorization framework. You initialize it with your client ID, set the redirect URI, and listen for the signinwithapple response event. The big gotcha here is that Apple enforces strict origin validation. If your redirect URI doesn't exactly match what you registered in App Store Connect, including the trailing slash, the authorization will be rejected. I've seen this cost people half a day because they were testing with http instead of https or because the port number was wrong. Always validate your registered origins in the developer portal before assuming the client code is broken. There are also some edge cases that the official docs don't really emphasize. The nonce parameter in the authorization request is important for preventing replay attacks. If your backend verifies the ID token, it should also verify that the nonce in the token matches the one you sent. Apple doesn't require you to use a nonce, but skipping it leaves you open to someone intercepting a valid authorization response and replaying it. Another thing that catches people off guard is that Apple's server-time drift can cause token expiration issues. The ID tokens are valid for one hour, but if your server clock is more than a few minutes off from NTP, you might see unexpected token validation failures. Set up a proper NTP sync and you won't think about this again.
The refresh token situation is also worth understanding properly. When you request the offline_access scope during the initial authorization, Apple gives you a refresh token alongside the ID token. This refresh token is long-lived and can be used to get new access tokens indefinitely until the user revokes access or your app expires. But there's a catch: Apple limits the number of refresh tokens you can have active per user. If you create too many without cleaning up old ones, you'll start getting errors on subsequent refresh attempts. I learned this the hard way when our test suite kept spinning up new sessions and eventually hit the limit. The workaround is to store the refresh token centrally and reuse it, rather than generating new ones for every test run. One more thing that nobody mentions is the behavior when a user changes their Apple ID password or enables two-factor authentication. In those cases, Apple sends a server-to-server notification to your configured callback URL, which is called the User Data Removal Callback. You can use this to invalidate all existing sessions for that user and force them to re-authenticate. It's a good security practice, especially for apps that handle sensitive data. The callback payload includes the user's email and the timestamp of the change, so you can look up their account and take appropriate action. Apple Login Integration has real limitations too. The biggest one is that you can't customize the UI at all. The sign-in dialog is entirely controlled by Apple, and while that's usually fine, some apps need a branded experience or need to collect additional consent text before the user sees Apple's prompt. You can't do that with Sign in with Apple. Another limitation is that the user's email isn't always returned, and when it's not, you have no way to force Apple to give it to you. The user has to explicitly choose to share their real email during the authorization flow, and if they don't, you're working with a relay address that Apple provides, which forwards mail to their real inbox but isn't permanently stable.
Get the Full Details

If you need more control over the authentication experience or need to support enterprise SSO, Sign in with Apple might not be the right choice for you. In those cases, OpenID Connect providers like Auth0 or Okta give you more flexibility at the cost of adding another dependency to your stack. For most consumer apps though, Sign in with Apple is the right call. It's faster to implement than building your own auth system, it gives users a frictionless login option, and it reduces the burden of password management on your side. The actual implementation usually takes between 2 and 4 hours for a straightforward web or iOS integration if you've done OAuth before. If you're doing it for the first time, plan for a full day, mostly because of the configuration steps in the developer portal and the occasional cryptic error message from Apple's servers. The hardest part isn't the code, it's getting the certificates and keys set up correctly and making sure your redirect URIs match everywhere.