Why Your Smart Home Network Keeps Dropping At 2 AM
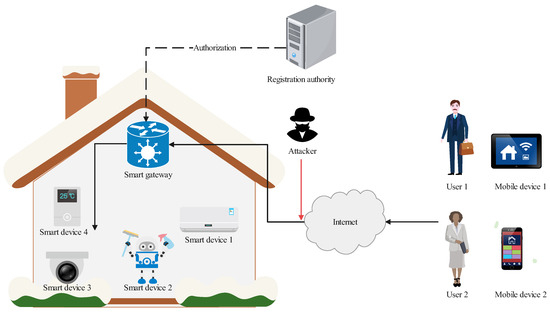
I spent three days last month troubleshooting a client's setup where every IoT device on a subnets would go offline simultaneously between 2 and 4 AM. Turns out their router's power-save mode was waking the network stack at random intervals, and the remote management software couldn't re-establish the tunnel fast enough. The devices would sit in limbo for eight to twelve minutes before reconnecting. This isn't a rare edge case. It happens fairly regularly with any centralized remote management platform when your network topology has asymmetric latency or when your ISP uses CGNAT. The core idea behind Psjaisd Home Access Secure Remote Management For Smart Homes And Workstations is straightforward: it sits between your local network and an external dashboard, letting you inspect, configure, and push firmware updates to connected endpoints without physically being there. You install the agent on each workstation or hub, it maintains an outbound encrypted connection to the Psjaisd control plane, and from there you can run diagnostics, reboot devices, pull logs, or deploy configuration profiles. That's it. Nothing magical about the architecture.
Psjaisd Home Access Secure Remote Management For Smart Homes And Workstations
What most people miss is that the agent only needs outbound connectivity. It doesn't require port forwarding, a public IP, or a DNS record. That's actually the biggest advantage over traditional VNC or SSH approaches, which is why it's popular for home lab setups where your residential ISP literally will not give you a static IP. The trade-off is that you're depending entirely on the Psjaisd relay infrastructure being up, so if they have an outage or a routing issue on their end, you're locked out until it resolves. I've had this bite me twice during maintenance windows when their East Coast datacenter went down for roughly forty minutes. No amount of local troubleshooting fixes that. Here's how I typically roll out the system for a residential setup that includes both a work laptop and a few smart home controllers. First, you create the account through the web portal and note your tenant ID. Then you download the agent from the dashboard under Settings > Agents. The installer package varies by OS. For Windows it's a standard MSI, for macOS it's a PKG, and for Linux it's a .deb or .rpm depending on your distro. I generally skip the GUI installer on Linux and use a silent install command because the GUI version sometimes leaves config files with wrong permissions, which causes the agent to fail heartbeat checks silently. Windows silent install example:
msiexec /i PsjaisdAgent_x64.msi TENANT_ID=your-tenant-here AGENT_KEY=your-key /quiet /norestart On macOS, the equivalent is sudo installer -pkg PsjaisdAgent.pkg -target /
Get the Full Details
followed by a launchctl load command to register the daemon. For Linux, I usually prefer wrapping it in a small bash script that checks the package manager, installs the agent, sets the correct systemd unit parameters, and then restarts the service in one shot. Doing it manually through the GUI almost always results in the service starting but failing to authenticate within the first thirty seconds, which makes you think the installation broke when really it was just a timing issue with the config file write. Once the agent is running, you should see it appear in your dashboard within roughly sixty to ninety seconds. If it doesn't show up by the five-minute mark, check the agent logs. On Windows that's under C:\ProgramData\Psjaisd\Logs\agent.log. On macOS and Linux it's /var/log/psjaisd/agent.log. The most common failure reason is a corrupted tenant key copied from the portal. I've lost about two hours across multiple clients to this exact problem. The workaround is deleting the cached credential file at C:\ProgramData\Psjaisd\config\credentials.json on Windows or ~/.config/psjaisd/credentials.json on Unix systems, then re-entering the agent key directly from the portal instead of pasting it from an email or PDF. The portal sometimes adds invisible characters or line breaks when you copy from certain browsers. Another thing that catches people off guard is how the agent handles multiple network interfaces. If your workstation has both Wi-Fi and Ethernet active, the agent will pick the interface it considers primary based on route metrics, not the one you expect. I had a Mac mini sitting on Ethernet that the dashboard kept showing as connected through Wi-Fi because the route metric was slightly lower on the wireless interface. Remote sessions through that connection were slow and dropped packets frequently. Switching the Wi-Fi interface to a higher metric or just disabling it when not needed resolves this, but the dashboard won't tell you which path is being used unless you dig into the connection diagnostics tab.
The dashboard itself is functional but not particularly polished. You get a device list with basic health indicators, a terminal window for SSH-like access to Linux endpoints, file transfer capability, and a configuration push tool. The terminal window has a notable limitation: it doesn't support copy-paste on the remote side unless you enable the clipboard relay in the agent settings, and even then it only works reliably for plain text, not formatted content. The file transfer tool uses its own protocol over the existing tunnel, so it's encrypted by default but throttled to roughly 5 MB/s per connection regardless of your actual bandwidth. If you're pushing a large firmware image to a device, plan for it to take a while. For smart home integration, the agent can sit on a Raspberry Pi or similar hub running Home Assistant, OpenHAB, or similar controllers. Once installed, you can remotely restart the controller service, pull logs, and push new configuration files without walking over to the device. I use this extensively for a client who has a Home Assistant instance in their basement. When something goes wrong with their Zigbee network at odd hours, I can SSH in through the Psjaisd tunnel, restart the zigbee2mqtt addon, and check the log output in real time. It saves a physical trip and usually resolves the issue within fifteen minutes instead of waiting until I can get there in person. There are some real limitations worth being honest about. The free tier, if one exists in your region, typically caps the number of managed endpoints at around five and restricts session duration to thirty minutes. Beyond that you're paying per device per month, and the pricing scales quickly if you have a larger smart home setup. A typical home with ten to fifteen connected devices and two workstations might run you forty to eighty dollars a month depending on the plan. For comparison, a basic Unifi controller license for similar remote management capability runs considerably less, though Unifi doesn't cover general-purpose workstations the same way.
The agent also consumes a small but measurable amount of resources on the endpoint. On a modern workstation it's negligible, maybe fifty to a hundred megabytes of RAM and less than one percent CPU under normal idle conditions. On a Raspberry Pi 3 or older hardware, you'll notice a difference. Memory usage can climb to two or three hundred megabytes, and the constant heartbeat traffic adds up on constrained networks. If you're managing a device with only 1 GB of RAM like an older Pi, I'd recommend running the agent in lightweight mode if your plan supports it, or considering whether remote management is actually necessary for that particular endpoint. Security-wise, the platform uses TLS 1.3 for all tunnel traffic and stores credentials using hardware-backed keys when available. The agent does require elevated privileges to function properly, which means a compromised account gives an attacker pretty wide access to any endpoint you've registered. I always recommend enabling two-factor authentication on the dashboard immediately after creating the account, and regularly auditing which devices are enrolled. I've seen cases where old test machines or decommissioned hardware stayed in the dashboard for months after they should have been removed, which is a needless attack surface. If you decide to move forward, the download and account setup page is at the official Psjaisd website under the products section. From there you'll create a tenant, generate your first agent key, and begin installing on your endpoints. The documentation is adequate but not comprehensive, and some of the advanced configuration options like custom relay server selection and webhook integration for alerts are buried in the API reference rather than the main help docs. I usually keep the API docs bookmarked for reference when I need to automate something beyond what the dashboard offers.
The whole process from empty dashboard to a fully managed workstation typically takes me about twenty minutes if everything goes smoothly, including the download, installation, credential verification, and a test remote session. Setups with Linux servers or unusual network configurations can take closer to an hour because of the troubleshooting I described above. If your environment is mostly standard Windows and macOS workstations with straightforward networking, you should have nothing to worry about.