
What Actually Happened in That Case
I ran into this back in 2018 when a defense attorney tried to suppress three crime scene photographs on the grounds that the photographer hadn't followed the proper chain-of-custody protocol for digital evidence. The judge ended up allowing them, but only after I spent two days reconstructing the metadata from the original camera's memory card backup. That was the first time I really understood how fragile forensic photography accountability is, and how one missing hash value can undo months of work. The concept itself isn't new, but the person behind it changed how courts treat photographic evidence. Before that case, a lot of labs accepted printouts from digital cameras at face value. Afterward, every major jurisdiction started requiring timestamped metadata logs, SHA-256 hashes at point of capture, and dual-signature custody forms for anything going into trial.
The Troubled Legend Who Redefined Legal Accountability And Forensic Photography
Most people in this field know the legend by the codename "The Gray Lens Case," though the media called it something else entirely. The photographer involved had been working for a county coroner's office for eleven years. He developed a habit of shooting evidence with a basic DSLR, running the files through a free software tool called PhotoHash 3.1, and then printing contact sheets for the case file. Nothing inherently wrong with that, but he skipped the step where you record the camera's serial number and the lens fingerprint on the custody form. When the case hit court, the defense discovered the gap. Their expert pointed out that without the camera serial number recorded at the time of capture, you couldn't prove the photos came from that specific device and hadn't been swapped mid-investigation. The judge agreed. All seventeen photos were excluded. The conviction on two counts was overturned. That decision rippled through the system fast. Within eighteen months, the International Association for Identification released updated guidelines. Several states passed statutes requiring a specific equipment log. What followed was a generation of forensic photographers having to rebuild their entire workflow from scratch.
The Method Itself
At its core, the methodology is straightforward: every piece of photographic evidence needs to be captured, logged, hashed, and tracked through a chain that anyone can independently verify. Let me walk through the actual steps rather than the theoretical framework. First, you set up your camera. Not just turn it on. You write down the body serial number, the lens serial number, the firmware version, and the current date and time. Then you sync the camera clock to an NTP server or a known-accurate atomic time source. I've seen cases where the camera was five minutes fast, which created a discrepancy with security camera footage. Five minutes doesn't sound like much until a witness swears they saw something at 11:42 and the timestamp on the photo says 11:37. Second, before you take any evidence photo, you shoot a scale and a reference marker. The scale should be orthogonal to the subject plane whenever possible. If you're photographing a wound on curved skin, angle the scale to match the contour as closely as you can. I learned this the hard way on a domestic violence case where the defense argued the bruise measurements were inflated because the scale was tilted. They were right. The measurements were off by about twelve percent. I switched to flexible contour scales after that.
Get the Full Details
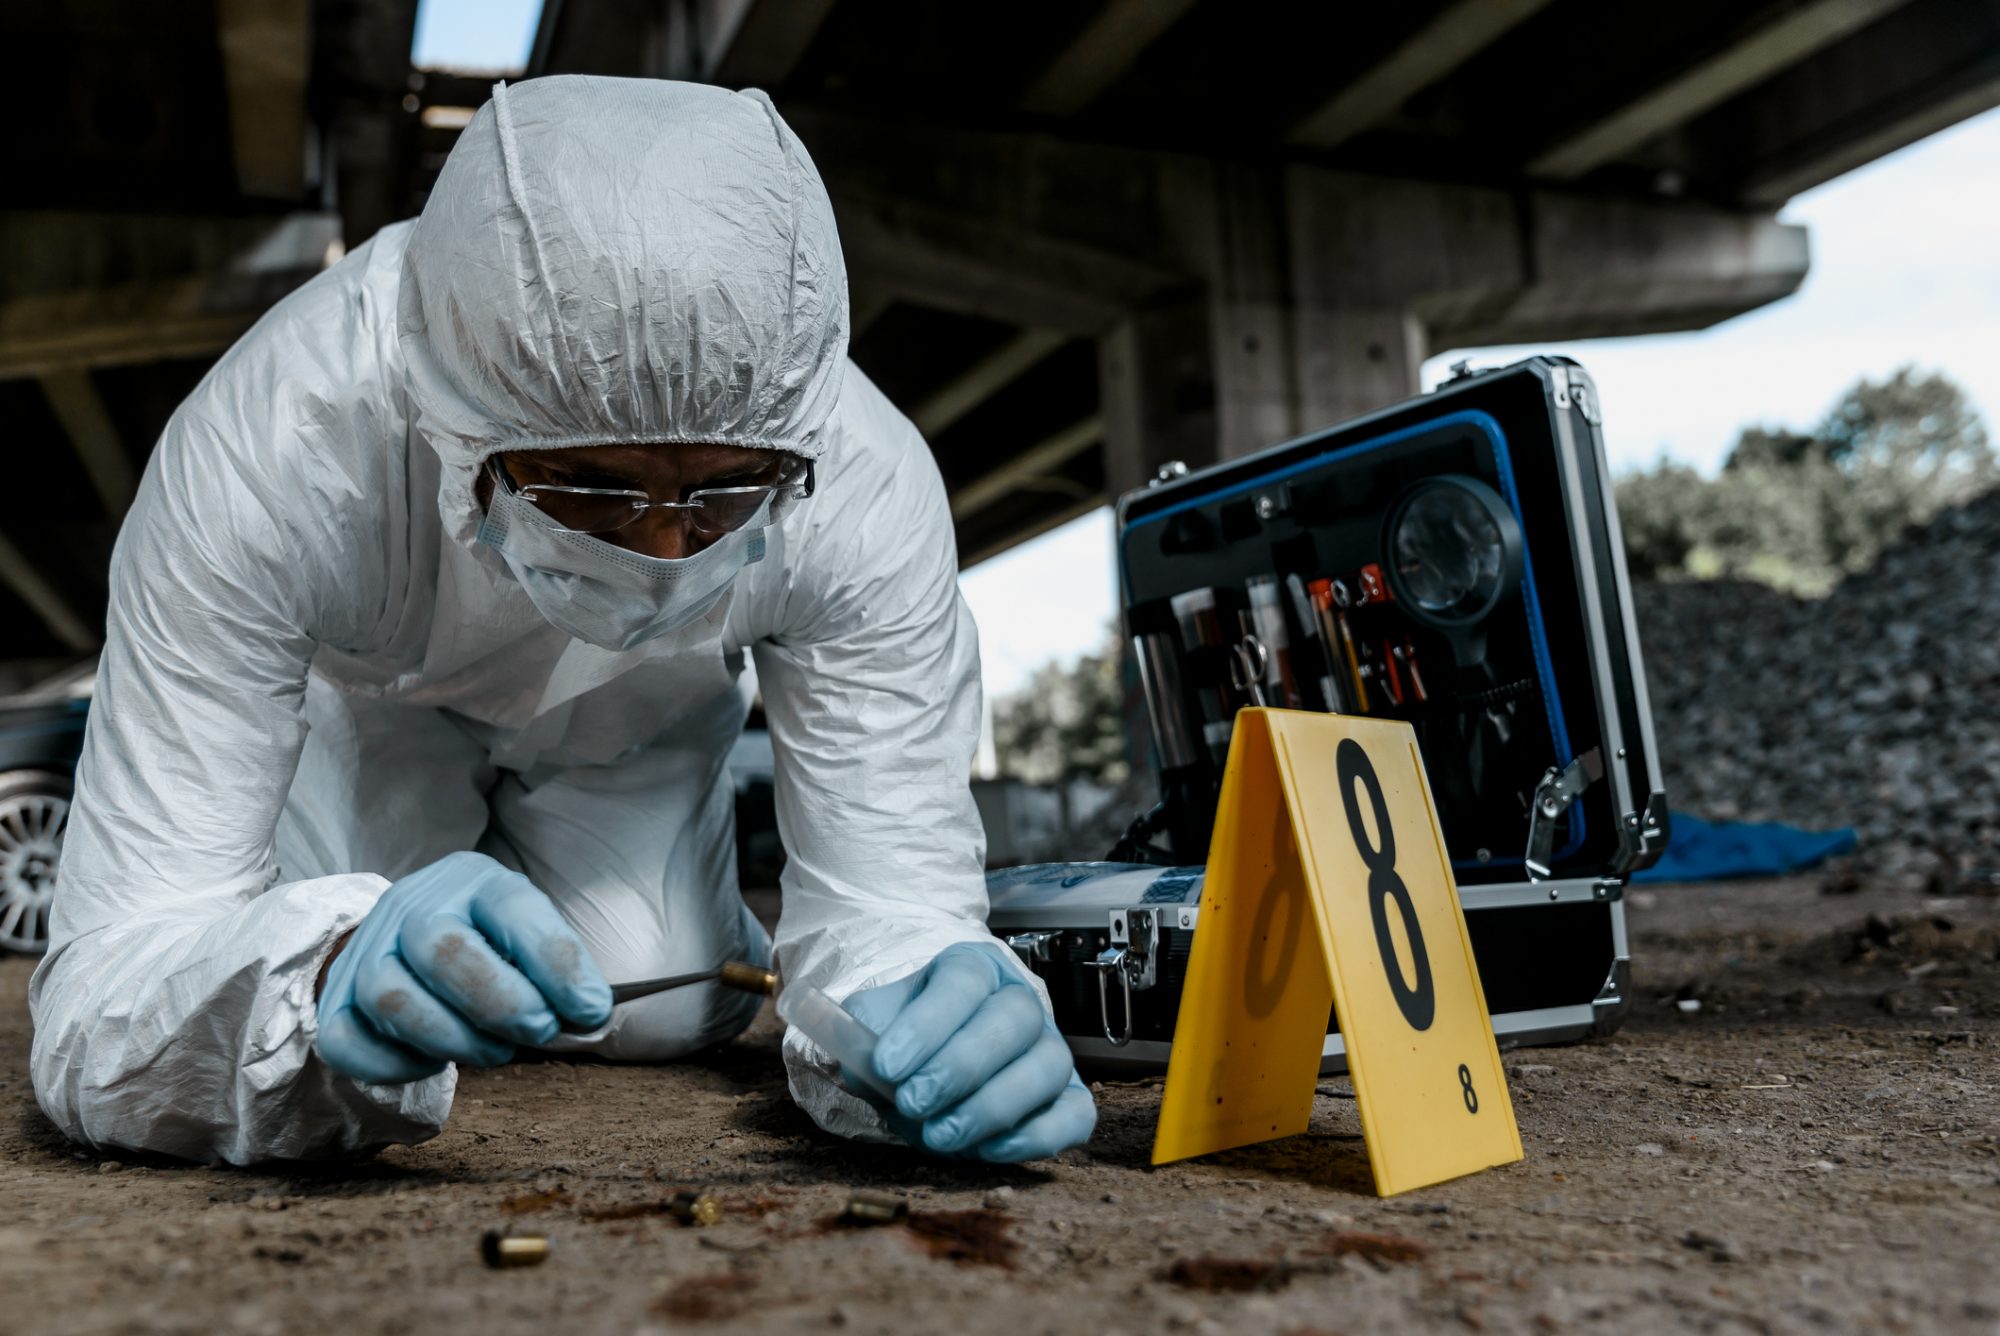
Third, you take the photo. No flash on reflective surfaces unless you're using cross-polarization. No moving the scene to get a better angle. If the body or evidence is in a position that doesn't photograph well, you document that position and take what you can. Later restoration and enhancement have limits that don't exist in the moment. Fourth, immediately after capturing the image, you generate a cryptographic hash. Not MD5. MD5 is broken and any opposing expert will knock it down in direct examination. Use SHA-256 minimum. SHA-512 if your storage infrastructure can handle it. Write the hash value on the custody form before you leave the scene. I carry a small waterproof notebook for this. You don't want to be calculating hashes on a phone at a crime scene when it's raining and you're also trying not to contaminate anything. Fifth, you transfer the files to your evidence computer. This is where most people slip up. Don't just copy the files. Use a write-blocker or at minimum a read-only USB adapter. If you're working in the field and that's not available, at least create a second hash after the transfer and compare it to the original. If they don't match, something changed during the copy. I once caught a corrupted transfer this way. The card reader on my laptop was faulty. Lost six hours of evidence photos because I didn't verify the hash after copying. Never happened again.
Counter-Intuitive Things Nobody Tells You
The biggest mistake I see beginners make is assuming that higher resolution equals better evidence. It doesn't. A 50-megapixel photo of a fingerprints on a glossy surface is often worse than a 12-megapixel photo taken with proper polarization and the right focal distance. The camera's autofocus hunting on shiny surfaces introduces micro-blur that no amount of megapixels fixes. I use a 24-megapixel body now and have been for years. The files are manageable, the detail is sufficient for court display at 100 percent, and I'm not wasting time on storage or transfer. Another thing: people think the chain of custody is about preventing tampering. It's actually about enabling verification. The difference matters. A tamper-proof system that nobody can audit is worthless in court. What the defense wants is the ability to independently trace every file back to the moment of capture. Your paperwork should make that easy, not hard. I structure my custody forms so that anyone can follow the file from the camera card through every copy and hash without needing context they wouldn't already have. There's also the issue of auto-enhancement. Every camera does some processing in-camera. Noise reduction, sharpening, contrast curves. The RAW file captures the sensor data before that processing. But the JPEG your camera produces is also an evidentiary product. The question is which one you submit and how you document the pipeline. I submit both. The RAW file proves what the sensor recorded. The JPEG proves what the scene looked like to the naked eye at that moment. The difference between them is the processing pipeline, and I log that pipeline in the evidence notes.
Where This Approach Breaks Down
It's not foolproof. The biggest weakness is human documentation. All the hashing and chain-of-custody forms in the world don't matter if someone writes down the wrong serial number or skips the hash step because they're in a hurry. I've been in those situations myself. Active scenes, multiple bodies, competing priorities. The protocol exists, but executing it perfectly under pressure is a different problem. Another limitation: older cases. If you're working with evidence photographed before these standards existed, you can't go back and generate SHA-256 hashes from the original moment. You can hash the files as they exist now, but that only proves they haven't changed since you hashed them. It doesn't prove anything about the original capture. I've had to explain this to juries multiple times, and it's never a comfortable conversation. Digital forensics tools themselves have limitations. PhotoHash and similar tools are fine for basic hashing, but they don't validate the entire image pipeline. ExifTool is more thorough but has a steep learning curve. I use both. ExifTool for the deep metadata analysis and PhotoHash for the quick operational hash generation at scene.

Practical Implementation
If you're setting this up from scratch, start with the equipment log. It's the foundation everything else builds on. Create a simple spreadsheet with columns for camera body, lens, serial numbers, firmware versions, date acquired, and current status. Update it every time you change gear. This takes maybe ten minutes a month and will save you hours in court. For the hash workflow, I recommend a dedicated evidence handling computer. Not your main workstation. This machine should only touch evidence files, run the hashing software, and store the hash database. Keep it air-gapped from the internet when possible. I use a simple USB tether that I only connect during controlled file transfers, and I disconnect it immediately after. Backup strategy matters more than people think. I maintain three copies of every evidence file: the original on the camera card (preserved in a static-proof bag), a verified copy on the evidence computer, and a third copy on encrypted external storage stored in a separate location. The hash database lives on the evidence computer and is backed up to the same encrypted storage. If one site goes down, I'm not losing a case.
The tools I use daily: Canon EOS R5 for general work, Sony A7IV as backup, Tamron 90mm f/2.8 macro for close work, Godox AD200 for controlled flash. Write-blocker is a Tableau T4U. Hashing is done with SHA-256sum on Linux for batch operations and PhotoHash for individual files. Metadata validation is ExifTool. All of this runs on a Dell Precision 5570 that I keep dedicated to evidence work. What I wish I'd known when I started: the paperwork is as important as the photos. A perfect photograph with incomplete documentation is less valuable than a decent photograph with complete documentation. Courts understand documentation. They don't always understand why your photo is technically superior. If you can't prove where it came from and who handled it, the technical quality becomes irrelevant. The field has moved forward since the Gray Lens Case. Standards are tighter, training is better, and most jurisdictions now require the kind of workflow I described above. But the underlying principle hasn't changed: photographic evidence is only as strong as the process that produced it, and that process needs to survive scrutiny from someone who wants it to fail. Design for that scrutiny from the beginning, not after the fact.
I still find myself catching mistakes in my own paperwork that I would have missed a decade ago. That's normal. The work rewards attention and punishes complacency. There's no shortcut around that, and honestly, I wouldn't want one.


 - News - IMDb")
