What OSCP Actually Gets You in the US Job Market
The OSCP certification is one of those credentials that shows up on résumés constantly, but the salary numbers people throw around are rarely complete. When I started looking into this for a team hire back in 2019, the job boards showed a wide range, and the gap wasn't just about location. It was about what kind of work the role actually required and whether the candidate could prove they could do it beyond passing an exam. I remember a specific case where a junior analyst had the OSCP and a clean GitHub, but couldn't navigate a real network discovery scenario in an interview. He aced the cert — the 33-hour lab exam is brutal and you need to earn it — but he'd never touched a Fortune 500 environment. The role needed someone who could write readable reports and explain findings to non-technical stakeholders. That person wasn't him. He's doing fine now, three years later, but the timeline matters.
Oscp Salary In The Us Uncovering The True Value Of Oscp Certifications
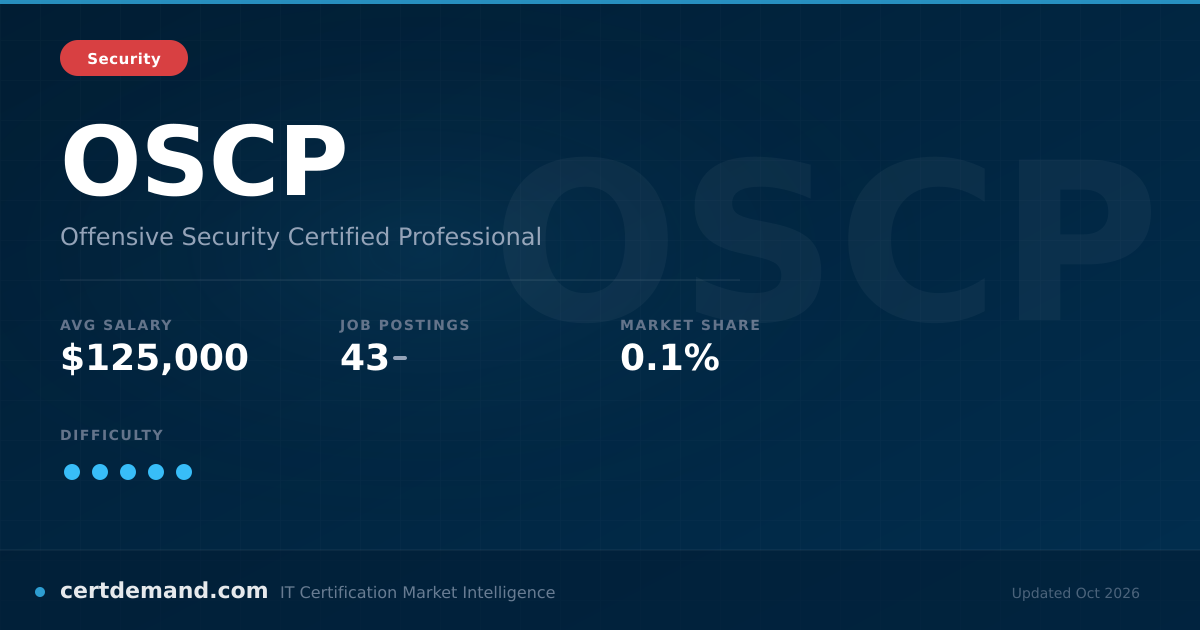
Entry-level penetration tester roles with OSCP in the US typically land between $65,000 and $85,000. That's the base number you'll see on Glassdoor and Payscale, but the median sits closer to $72,000. The outlier cases — people making over $100,000 straight out of college with only OSCP — exist, but they're uncommon and usually tied to location or a unique background in military cyber operations. Mid-level roles, two to five years in, push into the $90,000 to $125,000 range. Senior pen testers with OSCP plus additional certs like OSCE or CISSP can see $130,000 to $160,000 in major markets like San Francisco, New York, or Washington D.C. The D.C. area skews higher because government contracting dollars flow through there, and OSCP meets the DoD 8570 compliance requirement for certain positions. Here's a detail most guides miss: the cert itself doesn't guarantee the salary jump. What matters is the work you've done since getting it. A candidate with OSCP who's spent two years doing web app assessments for a boutique firm often commands more than someone with OSCP and three years of general IT support. The hiring manager can see that on a take-home exercise.
I ran into this exact situation when a hiring manager brought me a candidate who'd been passing exams but hadn't written a single engagement report. We put him through a mock assessment, and he couldn't structure a findings section without coaching. The OSCP report writing component is actually where most people struggle — not the technical parts. That's a practical skill, and it's the one that separates the certificate holders from the employable ones.
Get the Full Details

The Numbers Break Down By Role And Location
Penetration tester roles on the West Coast tend to pay 10 to 15 percent more than national averages. San Francisco Bay Area hits around $95,000 to $115,000 for mid-level. Seattle follows closely. The East Coast mirrors this in D.C. and Boston. Texas and the Southeast run lower, roughly 5 to 10 percent below national figures, but the cost of living adjustment makes those numbers competitive in practice. Red team roles pay more because the scope is wider and the responsibilities carry further. An OSCP holder moving into red team operations typically sees $110,000 to $145,000 at the mid level. The jump from penetration testing to red teaming isn't automatic though — it requires experience with adversary simulation, custom tooling, and evasion techniques that go well beyond the OSCP curriculum. Security consulting firms often pay slightly less than product companies for the same role. They make it up through billable hours and rapid career progression. A consultant with OSCP might start at $70,000 but hit $100,000 within two years if they're shipping engagements. The trade-off is less stability and more travel, which not everyone wants.
The one area where OSCP doesn't move the needle as much is in purely defensive roles. If you're applying for SOC analyst or incident response positions, the cert helps but it's not a salary multiplier the way it is for offensive security roles. Employers in those spaces value SANS certifications or CISSP more heavily for progression. I've seen OSCP holders pivot to purple teaming successfully, but that's a specific path that requires deliberate effort.
Why The Salary Range Is So Wide
One reason the numbers stretch from $65,000 to over $150,000 is that OSCP covers different career stages. The cert doesn't expire, but your experience does. A fresh OSCP holder with no professional background is entry-level, regardless of how hard the exam was. That's a hard truth to accept when you've spent weeks on the 24-hour exam, but it's how hiring managers evaluate candidates. Another factor is the type of employer. Managed service providers need volume and pay accordingly. Government contractors have fixed pay scales tied to position levels. Startups might offer equity instead of base salary, which changes the total compensation picture entirely. I've seen offers where the base was $80,000 but the equity package could be worth $50,000 or more at maturity, depending on the company's trajectory. Some employers also weigh OSCP differently based on team structure. A small team might treat OSCP as a baseline requirement and pay market rate. A large organization with multiple certification tiers will use it as a promotion gate, not a hiring differentiator. Understanding where you fit in that system matters when you negotiate.

The certification is a threshold, not a destination. It opens doors that stay closed without it, especially for penetration testing roles that list OSCP as a hard requirement. But once you're in the room, everything else determines your salary: years of hands-on experience, the complexity of work you've handled, your ability to communicate technical findings, and your track record of delivering results.
What The Exam Teaches You That Matters Later
The OSCP lab format teaches persistence more than anything else. You spend 24 hours trying to breach machines, then another 9 hours writing reports. The time pressure mirrors real assessment work, where you're often competing against a clock and a client deadline. I've seen candidates who bombed the exam initially come back six months later and pass on the second attempt, usually because they'd developed better note-taking habits and a more methodical approach to reconnaissance. The report writing component is what actually translates to higher salaries. In the field, your findings document is the deliverable that gets billed. A well-written report with clear risk ratings, actionable remediation steps, and executive summaries commands more trust from clients and leads to better retention. That's the skill that separates technicians from consultants, and it's the one that drives the upper end of the salary range. The technical content is solid for building foundational skills. Privilege escalation on Windows and Linux, basic web app exploitation, and network pivoting are all covered. Where the cert falls short is in areas like cloud security, container exploitation, and modern authentication bypasses. These aren't covered deeply because the exam scope hasn't caught up with the industry yet. If you want to stay current in those areas, you need additional training beyond OSCP.
Alternatives And Complements To Consider
GPEN from SANS is another penetration testing cert that some employers prefer for government work. It costs significantly more but includes formal training. For pure salary comparison, OSCP generally outperforms GPEN in the private sector while matching it in government contexts where both satisfy the same compliance requirements. OSCP plus a cloud security cert like CCSK or AWS Security Specialty creates a stronger profile than OSCP alone. The penetration testing market is getting crowded at the entry level, and adding cloud skills differentiates you. I've seen candidates with OSCP and basic AWS knowledge land roles at $110,000 to $120,000 that would have gone for $85,000 with just the cert. CISSP is the other major comparison point. It pays more at the senior level, but it requires five years of verified experience and covers a much broader domain. OSCP is the faster route into offensive security. CISSP is the longer-term play for management-track positions. They're not interchangeable, and smart candidates use them sequentially rather than picking one.
The Reality Check On Salary Expectations
If you're planning your career around OSCP, don't expect the cert alone to push you past $90,000 in your first role. That number typically requires either prior IT experience, a relevant degree, or a position in a high-cost metro area. The realistic entry point is $65,000 to $80,000, and the growth comes from what you do after you pass. Some people take OSCP and then plateau because they treat it as a finishing line instead of a starting line. The market rewards continuous skill development, not static credentials. I've watched colleagues with OSCP who stopped learning stagnate while peers without the cert but with consistent upskilling pulled ahead in both responsibility and pay. The certification has real value, but it's conditional value. It proves you can handle technical assessments and write professional reports. It doesn't prove you'll be effective in a specific environment, work well with a team, or stay current as the threat landscape shifts. Those come from experience, and that's what the salary data ultimately reflects.