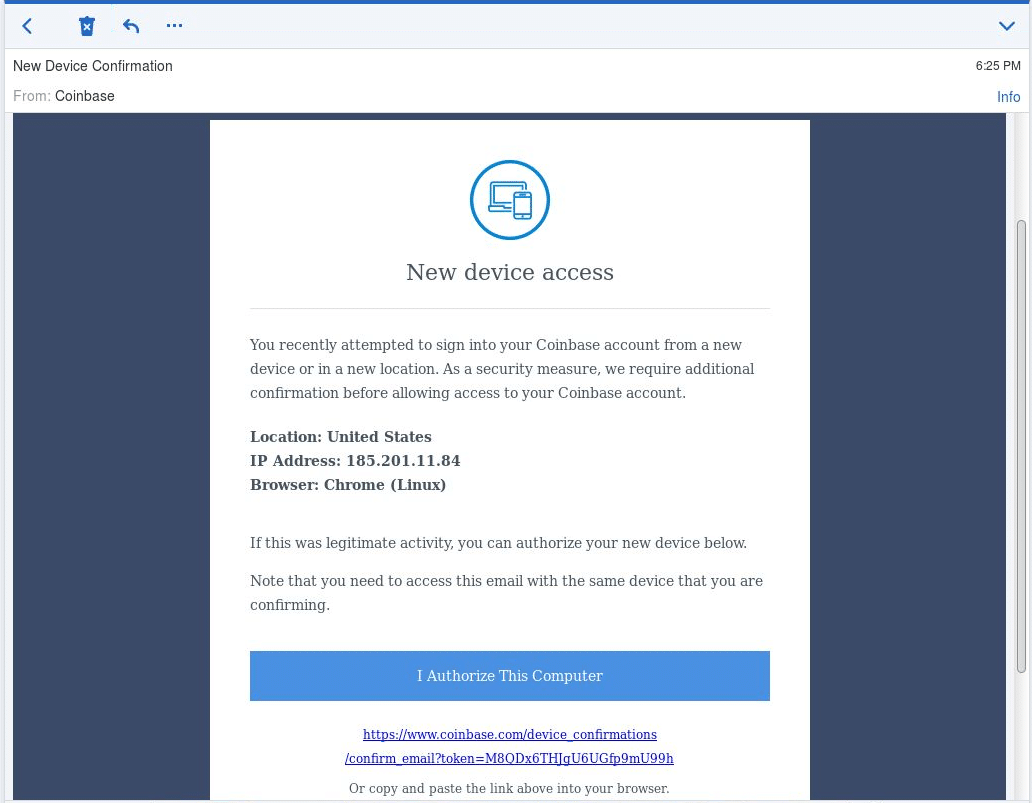
Those texts aren't from Coinbase, and the number on your screen is lying to you
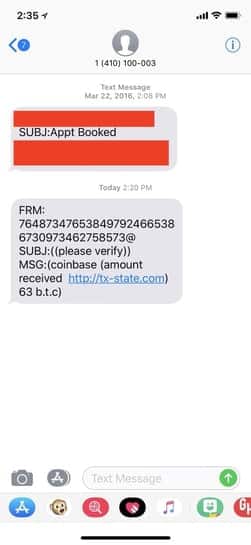
I've been dealing with phishing stuff since the early 2010s, and the Coinbase text scam is one of the more polished operations I've seen. They don't use one number. That's the first thing to understand. They rotate through hundreds, sometimes thousands, of lines daily. Some look like regular mobile numbers in your area code. Others show up as short codes that mimic legitimate notification systems. The number itself is basically irrelevant because it's been spoofed via SS7 signaling vulnerabilities or cheap bulk SMS platforms that let anyone pick a display name. Here's what actually happens. You get a text that says your account is locked, or there's suspicious activity, or you've received a deposit you didn't expect. It always has urgency baked into it. There's a link. You tap it. You type your credentials into a page that looks exactly like Coinbase's login screen. Two days later, your account is empty and the scammer has moved your funds through mixers before you even realize something's wrong. The whole flow takes maybe three minutes from tap to drain on a good day for them.
What Number Do Coinbase Text Scams Use Unmasking The Truth Behind The Spoofed Texts
The honest answer is: they use whatever number they want. Scammers operate through services like Twilio, Plivo, and various overseas SMS aggregators that allow display number customization. There are also botnets that hijack real phone lines. I've seen texts come from numbers that are actual working mobile lines belonging to people who had no idea their phones were being used to send phishing messages. That's why blocking a single number never works. You'll block one and they'll flip to another within hours. The ones that slip through most often are the ones that look local. A text showing a number with your own area code feels safer than one with an international prefix, so people lower their guard. Coinbase doesn't text you from random US mobile numbers for security alerts. Their official communications come through verified channels or at least numbers registered in their corporate SMS profiles, which you can sometimes verify through third-party services like Truecaller or Hiya, though even those databases lag behind the scammer rotation speed. I ran into a specific case last year where a friend nearly handed over his seed phrase after getting a text from what appeared to be a Coinbase support number. The message claimed he needed to "verify his identity to prevent permanent suspension" and included a link to what looked like a legitimate Coinbase security page. The URL was slightly off—c0insbase.com instead of coinsbase—and the SSL certificate was issued only two days prior, but he was panicked and didn't check either detail. I walked him through it and we reported the number and domain to the FTC and to Coinbase's phishing team. What really tipped him off was that the page asked for his seed phrase, which Coinbase support will literally never ask for. That's still the single most reliable tell.
How to actually protect yourself instead of chasing numbers
Most people focus on the wrong thing. They try to memorize which numbers are fake or set up block lists. That's a losing game because the scammers change numbers faster than any block list can update. The practical approach is to change your behavior around unexpected messages, not around specific sender IDs. If you get a text about your Coinbase account, do not tap anything in that message. Open your browser manually, type coinbase.com yourself, and check your account from there. If there's a real issue, it will show up in your dashboard. If the dashboard is fine and the text is the only alarm, it's a phishing attempt. Period. This alone blocks probably 90 percent of these attacks because the whole mechanism depends on you interacting with the link in the message. Enable two-factor authentication on your Coinbase account if you haven't already, and use an authenticator app rather than SMS-based 2FA. I know that's slightly ironic given we're talking about SMS scams, but SMS can be intercepted through SIM swapping, which is another vector these operators use. If a scammer gets your phone number ported to their SIM, they can bypass your SMS 2FA and then use the phishing link to grab your password. App-based 2FA or a hardware key breaks that chain.
Get the Full Details
Register your phone number with Coinbase's official fraud reporting channel at phishing@coinbase.com. Send them the message, the sender number, and the link if there was one. They track these and sometimes take down the domains, though the takedown speed varies. It's still useful because if enough people report the same domain, search engines and browser vendors deprioritize or flag it faster.
The technical details most people skip
What makes these scams work at scale isn't the quality of the lures. It's the infrastructure. scammers lease compromised email accounts in bulk, register phishing domains through privacy-protected registrars, and use bulletproof hosting providers that ignore DMCA takedowns. A single operation can spin up thousands of phishing pages in a day, each with unique URLs and slightly different copy to avoid pattern-matching filters. The SMS delivery side runs through SMPP gateways that cost pennies per thousand messages. A scammer can blast a hundred thousand texts for under fifty dollars. Even if ninety-nine point nine percent of recipients ignore the message, the remaining one point one percent funding the operation handsomely. That's why you'll see the same template popping up from different numbers constantly—it's literally the same script rerun against new batches of phone numbers scraped from data brokers and past breaches. One counter-intuitive thing most people don't realize: the Coinbase-branded phishing pages are often more sophisticated now than Coinbase's own transaction alert emails. The scammers have A/B tested their landing pages for conversion rates. Some of them include fake chat support widgets that press operators chat with victims in real time to guide them through handing over funds. I've seen screenshots where the "support agent" was typing responses within thirty seconds, which is only possible if it's a human on the other end paid per conversation.
What to do if you already tapped the link
Change your Coinbase password immediately from a device you haven't used recently. Revoke all active sessions in your account settings. If you reused that password anywhere else, change it there too. Then check your account for any unauthorized trades, withdrawals, or linked payment methods that weren't added by you. Enable withdrawal whitelisting if Coinbase offers it for your region—that adds a mandatory delay before any new recipient address can receive funds, which buys you time to catch things. Contact your bank or card issuer if you entered payment details on the fake page. Report the incident to IC3.gov if you're in the United States. It won't necessarily recover your money, but it creates a paper trail that helps law enforcement track the operation. And flag the original text as spam on your phone so your carrier can route similar messages away from other users. The hardest part to accept is that the number you saw doesn't matter anymore. It was never really Coinbase. It never will be. The only thing that matters is how you respond to the message itself.