The State Of Digital Identity Right Now
Most people don't think about their digital identity until something goes wrong. An account gets locked. A name mismatch flags a verification system. A background check service surfaces a profile that conflates three different people who share your address history. The infrastructure around who you are online is older and more brittle than most organizations admit. The concept traces back to the late 1990s when email addresses and forum usernames became the default identifiers. You created an account, you had a name. Simple. By 2008, social graphs replaced standalone identities. Facebook made real names the standard. LinkedIn did the same with legal names and employer affiliations. This was the first major fracture between how people actually identify themselves and what systems required them to verify. Here is what nobody on the consumer side sees. Identity proofing happens in layers. There is something you claim to be, something documents say you are, and something behavioral telemetry suggests you are. The first two have existed since the dawn of government ID. The third is new and wildly inconsistent in how it gets weighted across platforms.
How Identity Systems Actually Work Under The Hood
When you sign up for a modern service, the backend is running at least three separate checks. Device fingerprinting, known device association, and identity graph reconciliation. If you've ever had a legitimate account flagged for "suspicious activity" simply because someone else with a similar IP range opened an account with the same first initial and birth month, that's the identity graph doing exactly what it was designed to do. It's not always correct. Those false positive rates sit somewhere around four to eight percent depending on the vendor and the jurisdiction. I spent about six months dealing with a client whose enterprise SaaS platform was rejecting valid customer accounts because the behavioral biometrics didn't match their document-based identity. The workaround wasn't elegant. We built a custom risk tier that routed low-confidence matches into async human review instead of auto-rejecting them. Processing time dropped from two weeks of manual work per batch to under four hours. The key was separating the verification signal from the acceptance decision. Most platforms conflate those two things and pay for it.
The Core Components You Need To Understand
Legal identity is what governments issue. Driver's licenses, passports, national ID cards. This is the baseline layer. Digital identity is the collection of accounts, handles, and credentials you accumulate across services. Reputation identity is the signal that other systems generate about you based on transaction history, social connections, and behavioral patterns. The problem is that these three layers rarely align cleanly. A person can have a clean legal record and a damaged reputation identity because an algorithm attributed their activity to fraudulent behavior. I've seen this happen to legitimate business owners whose payment processing accounts get frozen after a chargeback spike triggered an automated risk model. The model doesn't distinguish between a legitimate business having an off quarter and a fraud ring. The appeal process is slow and usually requires submitting the same documents twice.
Get the Full Details
Self-Sovereign Identity And What It Actually Means
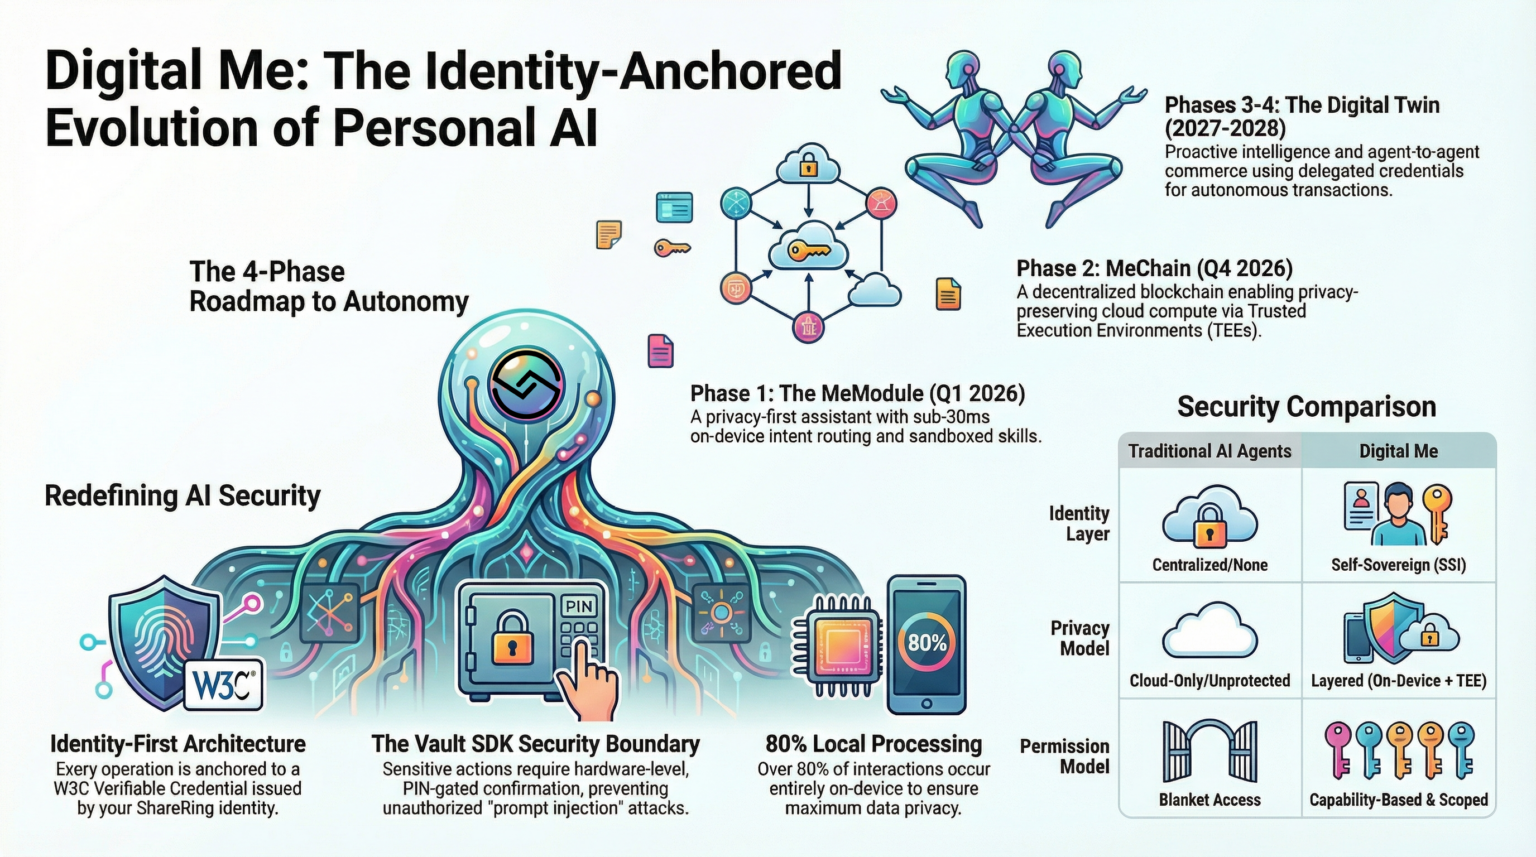
Self-sovereign identity, or SSI, is the framework where individuals hold and control their own verifiable credentials rather than relying on centralized providers. The technology exists. The problem is adoption friction. Decentralized identifiers use cryptographic keys stored in digital wallets. Credentials are issued by trusted issuers and verified by relying parties without requiring a central database lookup. In practice, this means you could present a verifiable credential proving you're over twenty-one without revealing your exact birthdate, address, or full name. That selective disclosure is the theoretical advantage. The practical disadvantage is that very few systems accept SSI credentials at this point. Most haven't even implemented the underlying W3C standards. Until the network effect hits, SSI remains more of an architectural concept than a usable tool for everyday identity management.
Common Pitfalls People Run Into
The biggest issue I see repeatedly is identity fragmentation. A person accumulates credentials across dozens of platforms, each using different verification standards and data retention policies. Some require video KYC. Some accept a selfie against a passport. Some just ask for an email confirmation. When a breach occurs, you have no central view of which identities are exposed. The average person has somewhere between forty and sixty active digital identities based on survey data from identity management firms. Another pitfall is over-reliance on a single identity provider. When you use one service as your primary authentication layer across multiple platforms, you create a single point of failure. I've watched this play out when a major social login provider temporarily suspended accounts during a security incident. Dozens of dependent services became inaccessible simultaneously. Users who hadn't set up independent login methods were locked out for days.
What To Do If Your Digital Identity Gets Compromised
First, document everything. Screenshots of the compromised account, any communication from the platform, dates and times. Most recovery processes require a timeline. Second, contact each affected service individually. Don't assume a report to one platform covers the others. Third, if financial accounts are involved, place a fraud alert with the credit bureaus. This costs nothing and stays on your file for one year. Fourth, consider a credit freeze if the compromise involves full PII. Freezes prevent new accounts from being opened in your name and are stronger than fraud alerts. The process of cleaning up a compromised identity typically takes between three and eight weeks depending on how many accounts were affected and how responsive the institutions are. I've seen cases stretch to six months when international jurisdictions are involved because the compromised data crossed borders and multiple law enforcement agencies need to be notified.

The Tradeoffs Nobody Talks About
Stronger identity verification means slower onboarding. Every additional check you add to a registration flow increases drop-off rates. Industry benchmarks show that each extra field or verification step can reduce completion rates by two to five percent. This is why most consumer platforms optimize for speed over thoroughness and push deeper verification to high-risk transactions only. There is also the surveillance dimension. Every identity verification event generates data about where you are, what devices you use, and who you associate with. The infrastructure that verifies your identity is also infrastructure that profiles you. That isn't a conspiracy. It's just how the data flows once it's collected. Most privacy policies acknowledge this indirectly by allowing data retention periods of up to seven years for verification records. If you want more control, the current practical options are limited. You can maintain separate identity profiles for different life contexts. You can use alias email services for non-critical registrations. You can avoid linking phone numbers to accounts where possible. None of this is perfect. It requires ongoing maintenance and awareness. But the alternative is letting every platform accumulate as much identity data as they can legally collect.