Understanding Windows Kernel Files and the Myths Around Them
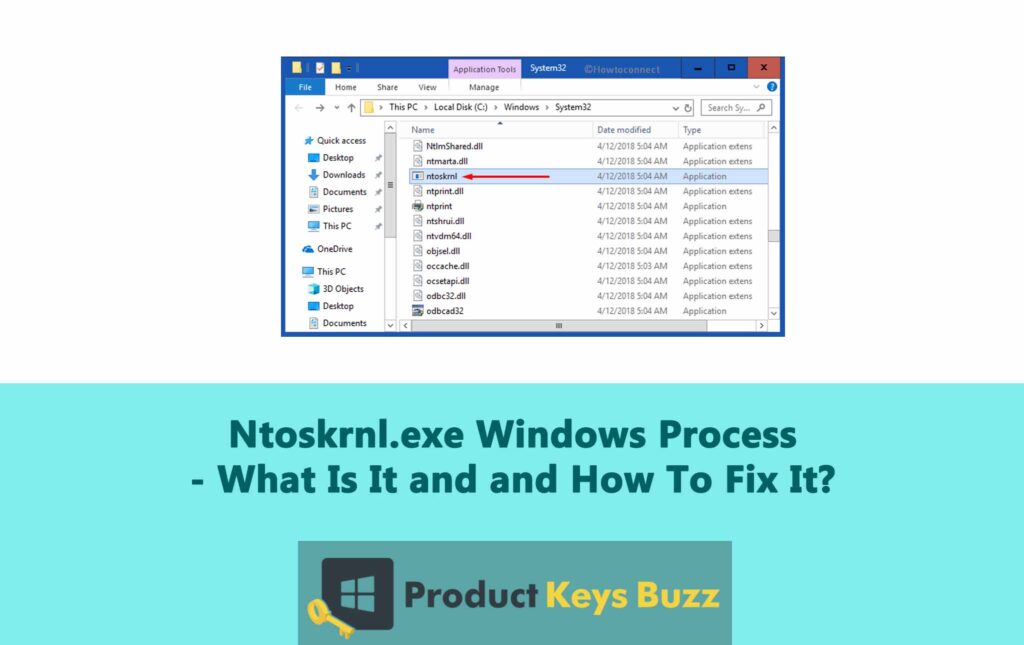
The file that gets most of the confusion is ntoskrnl.exe. It lives in C:\Windows\System32 and it is the core executable for the Windows NT kernel. It handles thread scheduling, memory management, hardware abstraction, and interrupts. It is not optional. If it disappears, the system does not boot. That is the entire story, stripped down. "Ntoskrnlexe" is not a real filename. It is a mangled spelling that circulates in scareware articles, forum posts, and YouTube videos that try to frighten people about a file they have never heard of. The actual file is ntoskrnl.exe. The "x" gets inserted somewhere in the middle by people copying bad sources or misreading the name, and then that misspelling gets repeated until it forms its own little ecosystem of false claims. Here is what I have seen repeatedly over the years. Someone runs a system scan, sees ntoskrnl.exe flagged, panics, searches the name, and lands on pages that have already corrupted the spelling. They then read articles claiming this file is a virus, a rootkit, or a backdoor. None of that is accurate for the genuine Microsoft-signed file. What IS accurate is that malware sometimes disguises itself with a similar name, or drops a fake copy in a random temporary folder and hopes you will not notice the difference.
I dealt with one case where a user's Event Viewer was flooded with 0x80070005 access denied errors tied to a file named ntoskrnl.exe sitting in C:\Users\Public\AppData\Local\Temp. The real kernel file was untouched in System32. The imposter had no valid digital signature from Microsoft. The workaround was straightforward: verify the path, check the signature via properties, and delete the off-path copy. The system stabilized immediately after. The real ntoskrnl.exe had nothing to do with the errors. There are a few things most people miss when they look at this file. First, the file size changes between Windows versions and service packs. On Windows 10 it typically ranges from about 4 MB to 7 MB depending on the build. On Windows 11 it is larger, often around 6 to 9 MB. If someone tells you the file should be exactly a certain size and it is not, that is a red flag, but you need to know which build you are running before you make that judgment. Second, the file is protected by Windows Resource Protection. You cannot delete it while the system is running. You cannot rename it from a normal administrator account. This is by design. If you see a guide telling you to force-delete ntoskrnl.exe from a running system, stop reading that guide. It is either outdated, written by someone who does not understand how Windows locking works, or it is deliberately misleading.
Third, the file is not the only kernel component. There is also hal.dll, the hardware abstraction layer, and various minidriver files that work alongside it. When people blame ntoskrnl.exe for a crash, they are often seeing a bug check that involves a driver, not the kernel executable itself. The bug check code and the loaded module information in a memory dump will tell you which driver actually caused the failure. Looking at ntoskrnl.exe as the culprit without checking the dump is like blaming the foundation of a house because a window broke during an earthquake. There is also a common claim that ntoskrnl.exe connects to Microsoft servers and "phones home." The kernel does send crash reports and telemetry data, but that is handled through separate mechanisms like WerFault.exe and the Diagnostic Service Host. The kernel executable itself does not maintain persistent outbound connections. If your firewall logs show ntoskrnl.exe initiating connections, investigate further. That behavior is not normal for the stock file, and it may indicate a modified or replacement binary. Another practical note: if you ever need to inspect the file, do not trust the Properties dialog alone. Check the SHA-256 hash and compare it against known good values for your specific Windows build. Microsoft publishes catalog files and you can verify signatures using tools like sigcheck or the PowerShell Get-AuthenticodeSignature cmdlet. A valid signature from Microsoft Windows or Microsoft Corporation means the file has not been altered since it left the factory. Anything else warrants a closer look.
Get the Full Details

I ran into a situation once where a third-party optimization tool had replaced ntoskrnl.exe with a stripped-down version that supposedly improved boot times. It did not. The system became unstable, developed random STOP errors, and the boot time was actually slower because the kernel had to fall back on compatibility routines. Restoring the original file from the Windows installation media fixed everything. These kinds of modifications are rare but they do happen, usually from so-called "tweaks" that promise performance gains without understanding what they are touching. The bottom line is simple. The real file is ntoskrnl.exe. It belongs in System32. It is signed by Microsoft. It does exactly what the name implies: it is the NT operating system kernel. Anything else is either malware, a misunderstanding, or a copy of the file placed somewhere it should not be. Verify, do not panic, and do not follow instructions from sources that cannot even spell the name correctly.