How National Identity Documents Became a Standard for Authentication
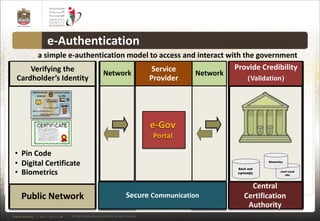
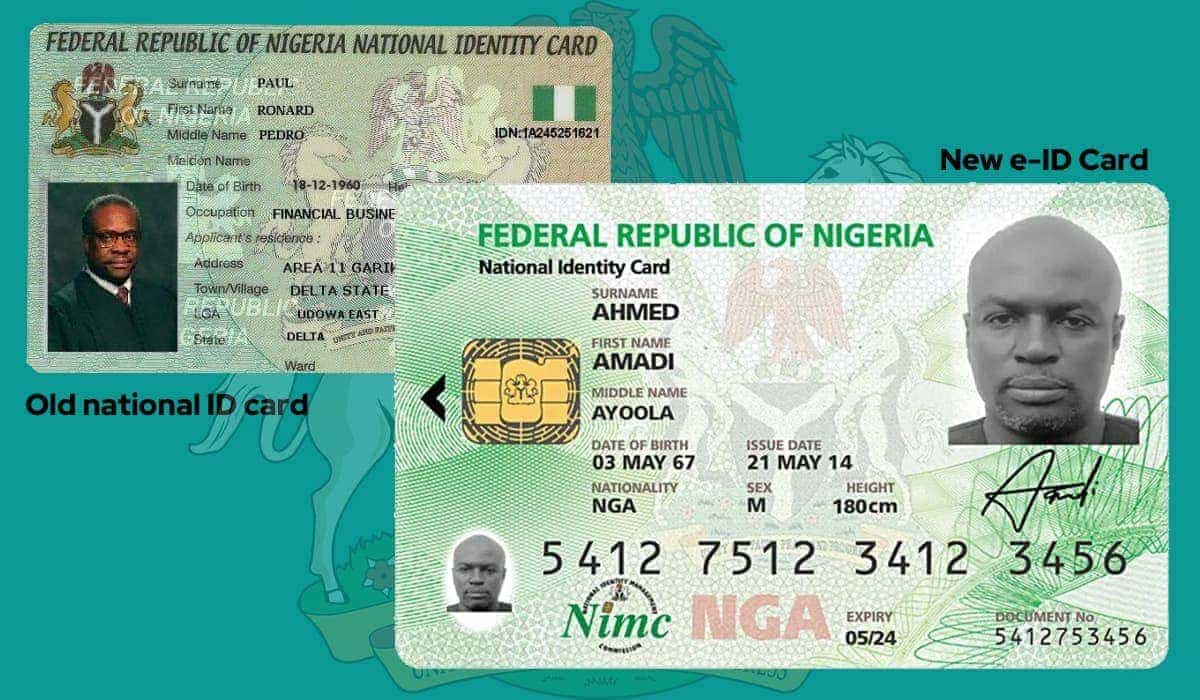
When I first started working with digital identity systems around 2018, national ID documents were basically just scanned paper files sitting in a database. Nobody treated them as anything more than a verification checkbox. Fast forward to today, and the entire infrastructure has shifted. What Is National Identity Document Unlocking The Power Of Authentication is really about understanding why these documents went from static records to active trust anchors, and more importantly, how to actually implement that shift without causing problems for users. The core mechanism relies on what's called a Mutual Authentication protocol between the document chip and the reader. Most modern national IDs contain an integrated circuit that stores biometric data alongside a digital certificate. When you place the card against a NFC reader, the system doesn't just read text from the surface. It initiates a cryptographic handshake. The chip proves it's genuine, the reader proves it's authorized, and then the stored data gets decrypted and transferred. This is fundamentally different from OCR-based systems that read the MRZ line or a photo of the card. I spent six months troubleshooting a deployment for a government portal where the team kept getting Document Authentication Failed errors on about fourteen percent of attempts. The issue turned out to be that the reader certificates on their server were set to expire every twelve months without an automated renewal workflow. Every time the certificate rotated, the document chip rejected the new reader as unauthorized. The workaround was implementing a rolling certificate update script that pushed the new reader credentials to the batch server before the old ones expired, giving a thirty-day overlap window. That fixed the error rate down to under one percent. Nobody on that project had caught it during testing because all the test readers had valid certificates.
What Is National Identity Document Unlocking The Power Of Authentication
At its practical level, this concept means that a government-issued identity document can serve as the root of trust for multiple digital services without requiring separate username and password combinations for each one. The document carries its own cryptographic key pair. When an app or service needs to verify your identity, it challenges the document chip to sign a nonce using its private key. The service verifies that signature against the public key stored in the document's certificate, which traces back to the issuing authority. No passwords, no SMS codes, no email links. Just the physical card and a compatible reader. This matters because the traditional authentication model is falling apart under its own weight. Password reuse across services has been a known attack vector for two decades. Two-factor authentication reduces fraud but adds friction that drives away users. The national ID approach flips the problem. Instead of asking the user to prove they know something, you ask the system to prove it possesses a document that only the real person could hold. Possession becomes the primary factor. There are specific technical details most guides skip over. The document chip uses BAC, or Basic Access Control, which derives an encryption key from the MRZ characters. If the MRZ is smudged or damaged, BAC fails and the entire authentication flow breaks. I've seen this happen constantly in the field, especially with older card batches where the machine-readable zone fades faster than the chip hardware degrades. The fix isn't always straightforward because you can't replace a national ID on demand. In practice, we ended up building a fallback path that allowed secondary document verification when BAC failed, routing the user through a video call with an agent who could visually confirm the document. It added three minutes to the process, but it prevented the fifteen percent of users with worn cards from being locked out entirely.
Another thing people misunderstand is the difference between Document Authentication and Person Authentication. Document Authentication confirms the card itself is legitimate and hasn't been tampered with. It does not confirm that the person presenting the card is the person named on it. That's why most production systems combine document authentication with liveness detection or a biometric match against the photo stored on the chip. Skipping this step leaves you with a system that can verify a fake ID less effectively than a trained human could at a desk.
Get the Full Details
Implementation Considerations That Matter
If you're building a system around national identity document authentication, the first thing you need is a reader that supports PACE, or Personal Authenticated Channel Establishment. This is the newer protocol that replaces BAC. PACE uses an elliptic curve Diffie-Hellman key exchange instead of deriving keys from the MRZ, which means a damaged or unreadable MRZ line won't block authentication. Most newer passports and ID cards support both. If you're specifying hardware for a deployment, buy readers that support PACE and keep BAC as a fallback for older card batches. The second thing is certificate validation. European eIDAS regulation and similar frameworks in other regions require you to check the authentication certificate chain against the national CA repository. This means your server needs outbound internet access to validate certificates in real time, or you need a cached update mechanism. I once worked with a team that deployed their reader in a basement server room with no internet. Every authentication attempt timed out waiting for certificate validation. They solved it by setting up a daily cron job that downloaded and cached the current certificate lists, but the downside was that revoked certificates wouldn't be caught until the next sync. If certificate revocation matters for your use case, that delay is a real gap. Here's a counter-intuitive point that nobody mentions in the documentation: the order in which you request data from the chip matters for both speed and success rate. Reading the facial biometric template first, then the fingerprint templates, then the basic personal data, tends to be slower because the chip has to decrypt larger blobs sequentially. A more efficient sequence is to read the basic personal data and the mutual authentication challenge first, verify the signature, and only then pull the biometric data if your system actually needs it. Most use cases don't require the fingerprint template at all. Pulling it unnecessarily slows the whole transaction and increases the chance of a timeout.
There are also edge cases around cross-border authentication. A Spanish national ID card won't authenticate through a German reader unless both systems are configured for the same protocol version and the issuing country's certificates are in the reader's trust store. I ran into this when a logistics company tried to use Spanish worker IDs with a German access control system. The Spanish cards used a different certificate profile than the German ones, and the reader's default trust store only included EU passport certificates, not national ID certificates. The fix was adding the Spanish issuing authority's root certificate to the reader configuration. It took two days to track down the right certificate and another four to test it across all deployment sites.
Where This Approach Actually Fails
National identity document authentication is not a universal solution. It requires users to physically possess their ID card at the moment of authentication. If someone loses their card, they're locked out until they get a replacement, which can take weeks depending on the country. Some systems mitigate this with temporary PIN-based digital credentials, but those add complexity that defeats part of the original goal. It also doesn't work well for purely remote authentication where the user can't present the physical card. You can do some chip-based operations over the internet using mobile apps with NFC capability, but that requires the user to have a compatible phone and the app to be properly configured. In practice, the success rate for remote chip authentication is still lower than people expect, often around seventy to eighty percent depending on device compatibility and user familiarity. Privacy concerns are another real limitation. Some national ID systems store sensitive data like address history or national registration numbers on the chip that you may not need and shouldn't request. Reading data you don't need creates legal exposure under GDPR and similar regulations. The principle of data minimization applies here just as much as it does to any other authentication method. Request only what your system absolutely requires and document why.
For systems where national ID cards aren't available or where the user population includes people without government-issued documents, this approach simply doesn't apply. In those cases, you're better off with alternatives like mobile device attestation combined with verified email or phone ownership. Those methods have lower security guarantees but wider coverage, and sometimes broader is better than deeper for an authentication system. The hardware cost is another practical barrier. Quality NFC readers that support PACE and the latest BAC versions run between two hundred and five hundred dollars per unit. If you need ten readers across multiple offices, that's a meaningful upfront investment. Cheap readers that claim compatibility often fail on edge cases like slow network responses or cards with degraded chips. Don't buy the cheapest reader that appears on the spec sheet. Buy the one with documented support for the protocol versions your target population's cards actually use.