The Nuts and Bolts of Serial Numbers
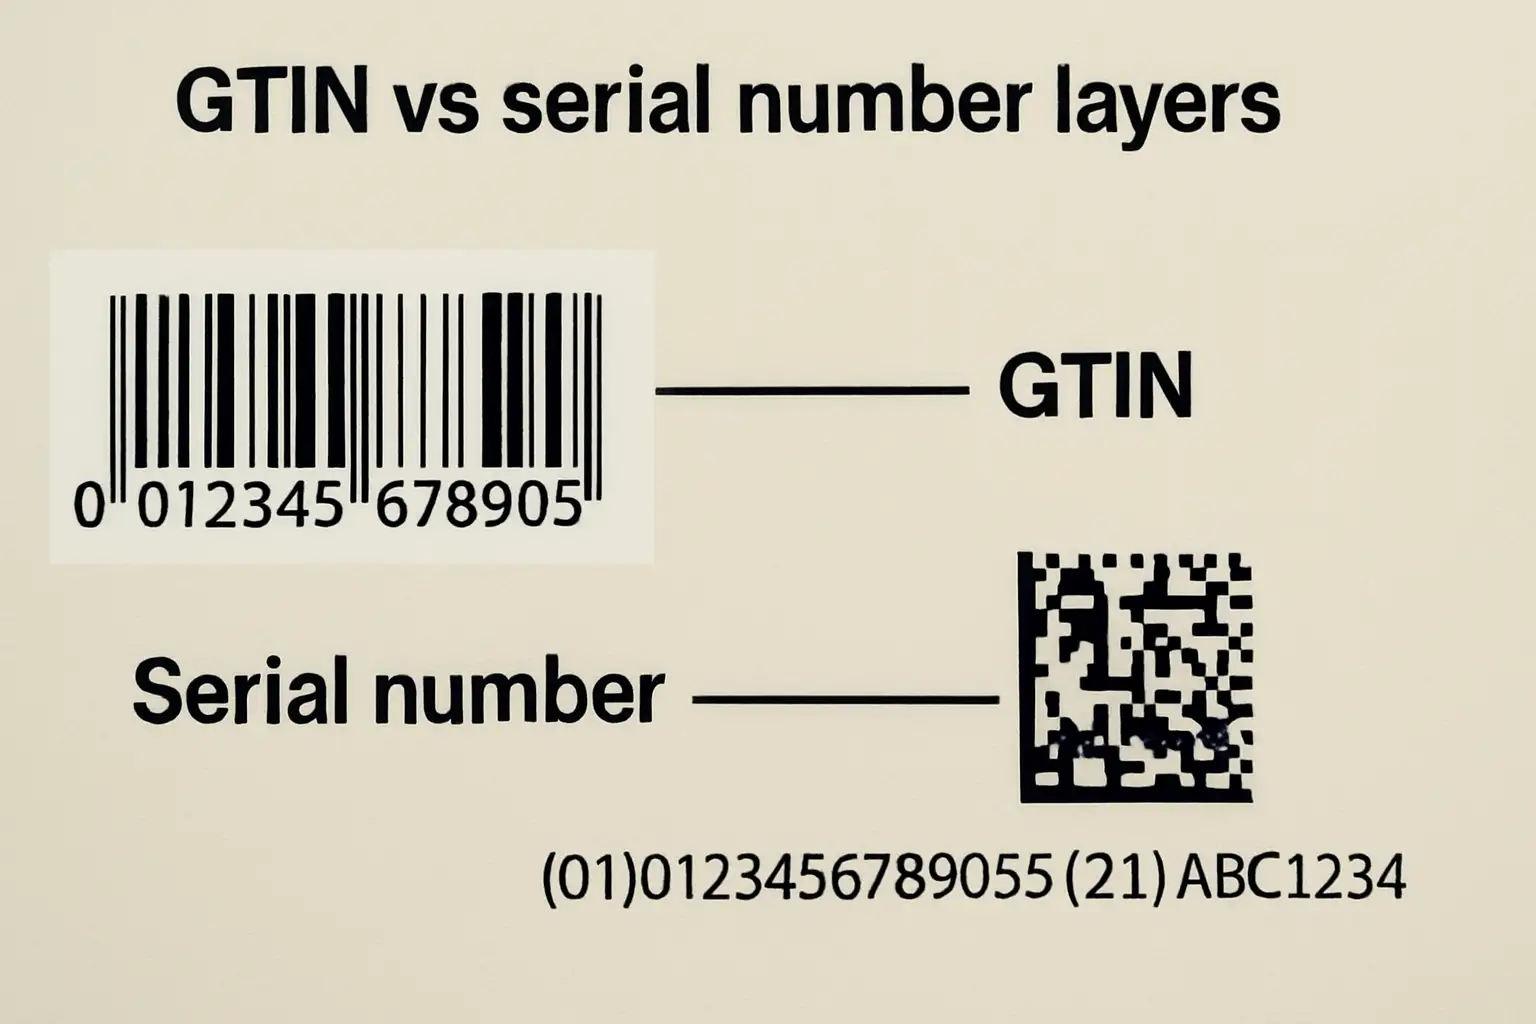
Serial numbers are arbitrary unique identifiers assigned to individual units of a product, component, or asset. They are not hashes, not checksums, and not encryption keys. They are simply strings that allow you to look something up in a database or trace it through a supply chain. That's it. The security around them, the verification workflows, the whole ecosystem — that's where things get messy. There are two fundamentally different approaches to serial number systems, and most people conflate them. The first is sequential numbering: 000001, 000002, 000003. Simple, cheap, easy to validate. The second is random or pseudo-random generation, often combined with encoding schemes like GUIDs or UUIDs. Sequential numbers are trivially guessable. If you're using them for anything security-related, you've already made a mistake. But sequential numbering has real advantages — auditability, order correlation, deterministic generation — which is why legacy manufacturing and government procurement still insist on them decades later.
What Is A Serial Number The Definitive Guide To Identification Security And Verification
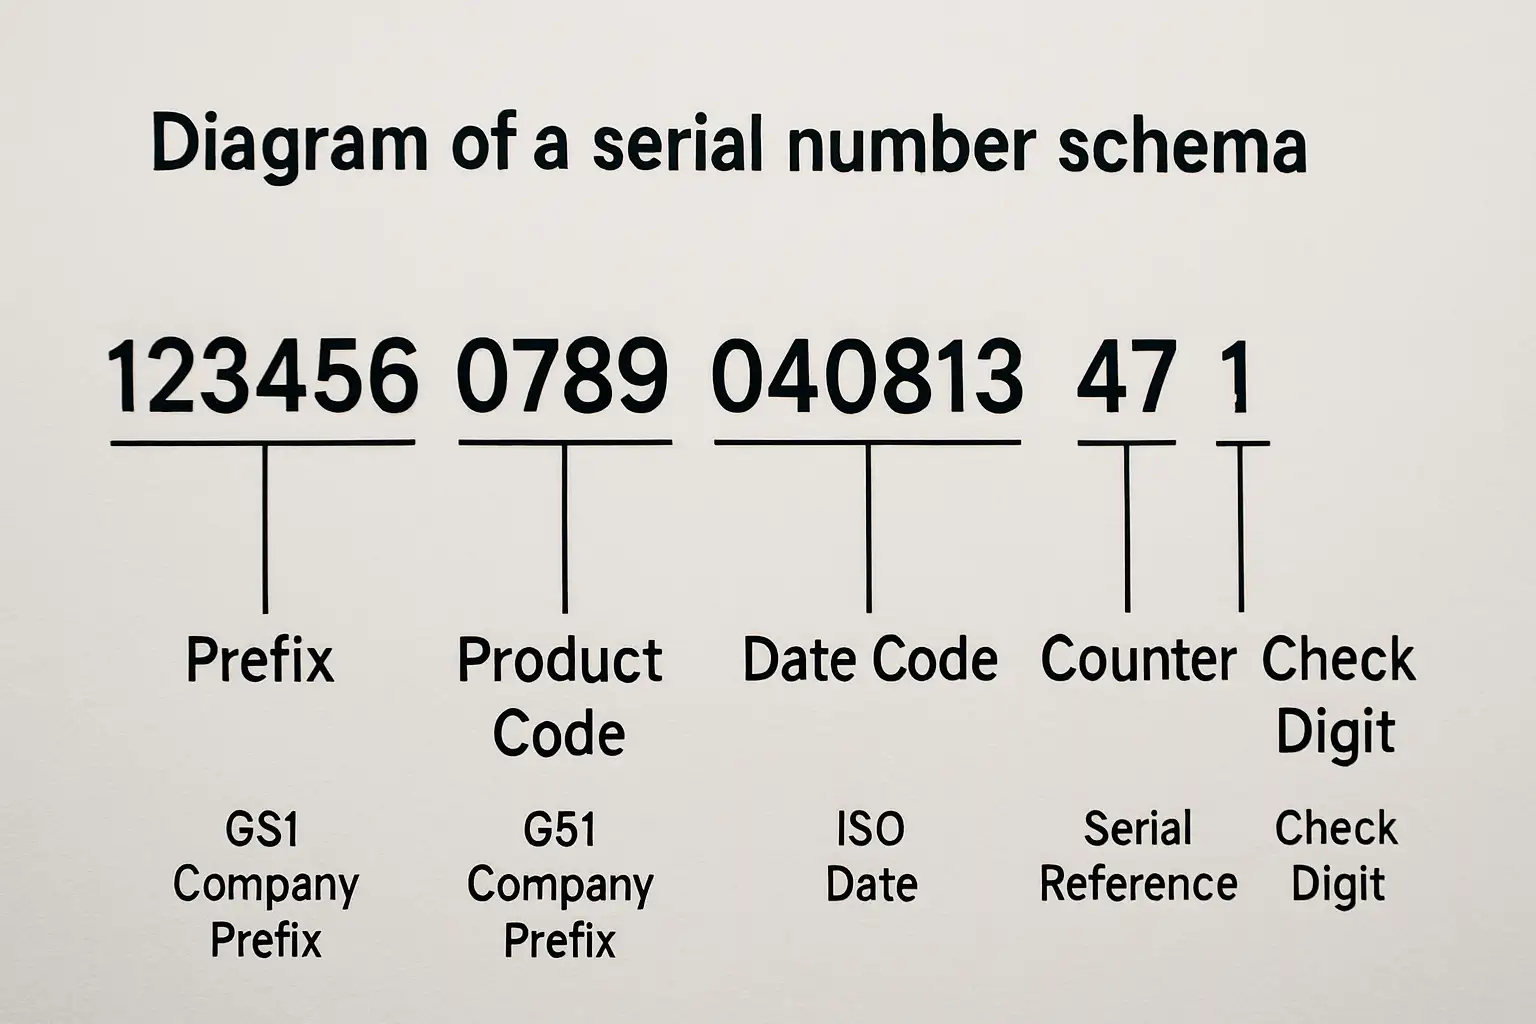
I spent three years working with serialized hardware assets for a defense contractor. Our serial numbers looked like this: a two-letter plant code, a six-digit sequential block, a check digit, and a two-character year code. Format like AB-123456-C-24. The check digit was a simple mod-10 algorithm applied to the numeric portion. It caught about 98% of typographical errors and was completely trivial for anyone with basic math skills to reverse-engineer. Here's the thing nobody tells you about serial number verification: the format itself is usually the weakest link. People obsess over database security and hashing while the actual string format leaks more information than any other single component. A sequential serial number published in a product manual tells a competitor exactly how many units you've shipped. A date-encoded serial lets insurance fraud investigators reconstruct when a claimant purchased an item. I once identified a pattern in a client's warranty claims by cross-referencing serial number batches with known shipment dates — found a whole production run that had been documented as "shipped" but was actually sitting in a warehouse for eight months.
Verification Methods That Actually Work
The most common verification approach is a direct database lookup. You input the serial number, the system queries the registered records, and returns the associated metadata. This works when your database is accurate, which is rare. In practice, serial number verification fails most often because the underlying data is wrong, not because the verification logic is broken. I've seen systems where the verification returned "valid" for a serial number that had been reassigned to a different product line three years earlier. The old record was just never purged. For high-security applications, you need something beyond a plain database lookup. Challenge-response protocols are standard in NFC-based authentication. The reader sends a random challenge, the device signs it with a stored key, and the verifier checks the signature against an expected value. This prevents clone devices from simply replaying a captured serial number. The downside is that every verification round-trip takes 200-500 milliseconds on a typical implementation, which adds up fast in a retail or field-service environment where you're checking dozens of items per minute. Another approach that gets overlooked is cryptographic binding between the serial number and the physical device. Instead of storing the serial number in plaintext on the device itself, you embed it in a secure element alongside a private key. Verification requires a hardware-level challenge-response. This is how Apple does it with Device UID, how TPMs work in enterprise laptops, and how high-end payment terminals prevent hardware cloning. The cost per unit goes up significantly — we're talking $2-8 per secure element depending on volume — but it makes serial number forgery computationally infeasible rather than trivially easy.
Get the Full Details
Common Pitfalls and Edge Cases
Serial numbers collide. It sounds obvious, but the majority of collision problems I've encountered came from systems that generated serials in separate sub-systems without coordination. A manufacturer might have one system generating serials for the European market and another for the Americas, each with overlapping ranges. When those markets merge or when products are gray-market traded, the same serial number legitimately exists twice in different databases. Your verification system has no way to know which one is correct without additional context like region codes or timestamps. Another issue is serial number reuse in warranty and repair contexts. When a component is replaced under warranty, the service center often needs to decide whether to keep the original serial number or assign a new one. I worked on a system for a medical device manufacturer where the answer depended on whether the replacement was within the same assembly group. If it was, the serial stayed. If it wasn't, a new serial was generated and a cross-reference record was created linking the old and new. This seemed straightforward until an auditor asked why some devices had three serial numbers in the history. The answer was that intermediate replacement parts had also triggered new serial assignments, creating a chain that nobody had documented properly. Check digit algorithms are another area where people get complacent. The mod-10 Luhn algorithm catches about 98% of single-digit errors and most adjacent transpositions. But it has known weaknesses — it doesn't catch all twin errors (like 11 becoming 22), and it can be deliberately crafted around. I've seen fraud rings use serial numbers that passed Luhn validation but were clearly fabricated because the numeric prefix corresponded to a defunct product line. The verification system accepted them because the checksum was correct. The format should have been validated against an allowed prefix table before the checksum was even checked.
What This Actually Looks Like in Production
A well-implemented serial number verification pipeline looks something like this. First, format validation: the input string is checked against a regex or structured parser that enforces the expected format, length, and character set. Second, prefix validation: the leading characters are checked against a registry of valid manufacturer and product codes. Third, checksum validation: the check digit or hash portion is verified. Fourth, database lookup: the serial number is queried for existence and status. Fifth, contextual validation: additional checks like date-of-manufacture vs. current date, geographic consistency, and status flags (active, recalled, deactivated). Each of these steps can fail independently, and each failure mode has different implications. A format error usually means user input mistake. A prefix error might indicate a counterfeit product. A checksum error suggests typos or tampering. A database miss could mean the product is unregistered, already sold, or the database is incomplete. The response to each should be different — a format error gets a user-friendly message, a prefix error might trigger a fraud alert, and a database miss might require escalation to a human reviewer. I once spent two weeks debugging a verification system that was incorrectly flagging legitimate products as suspect. The issue was that a product line had been discontinued and its serial range de-registered from the active database, but products from that line were still circulating in the secondary market. The verification logic treated "not in active database" as "invalid" rather than "potentially retired but authentic." We added a separate "retired but valid" status code and a lookup against a historical registry. This took about three days to implement once we identified the actual problem.
When Serial Numbers Aren't Enough
Serial numbers alone cannot solve authentication problems at scale. They are a tracking mechanism, not a security mechanism. A serial number proves that something exists in a database. It does not prove that the physical object you're holding is the one registered to that serial number. That requires a physical link — a tamper-evident label, a holographic sticker, a secure element, a cryptographic challenge-response. Without that link, serial numbers are just numbers that anyone can print on a label. The counterfeiting industry has adapted to this reality. High-quality counterfeiters now produce serial numbers that pass format and checksum validation and even exist in stolen databases. The serial number verifies correctly. The product is fake. The only thing that would have caught it is the physical authentication layer that the counterfeiters replicated perfectly. This is why multi-layered verification — combining serial number checks with physical authentication and cryptographic proof — is the standard for anything above consumer-grade products. If you're building a serial number system from scratch, start by deciding what problem you're actually solving. If it's warranty tracking, a simple database with format validation and a check digit is sufficient. If it's anti-counterfeiting, you need physical authentication layers. If it's security-critical verification, you need cryptographic binding. Mixing these requirements without being explicit about which problem you're solving is the most common mistake I see, and it's the reason most serial number systems end up doing everything poorly.