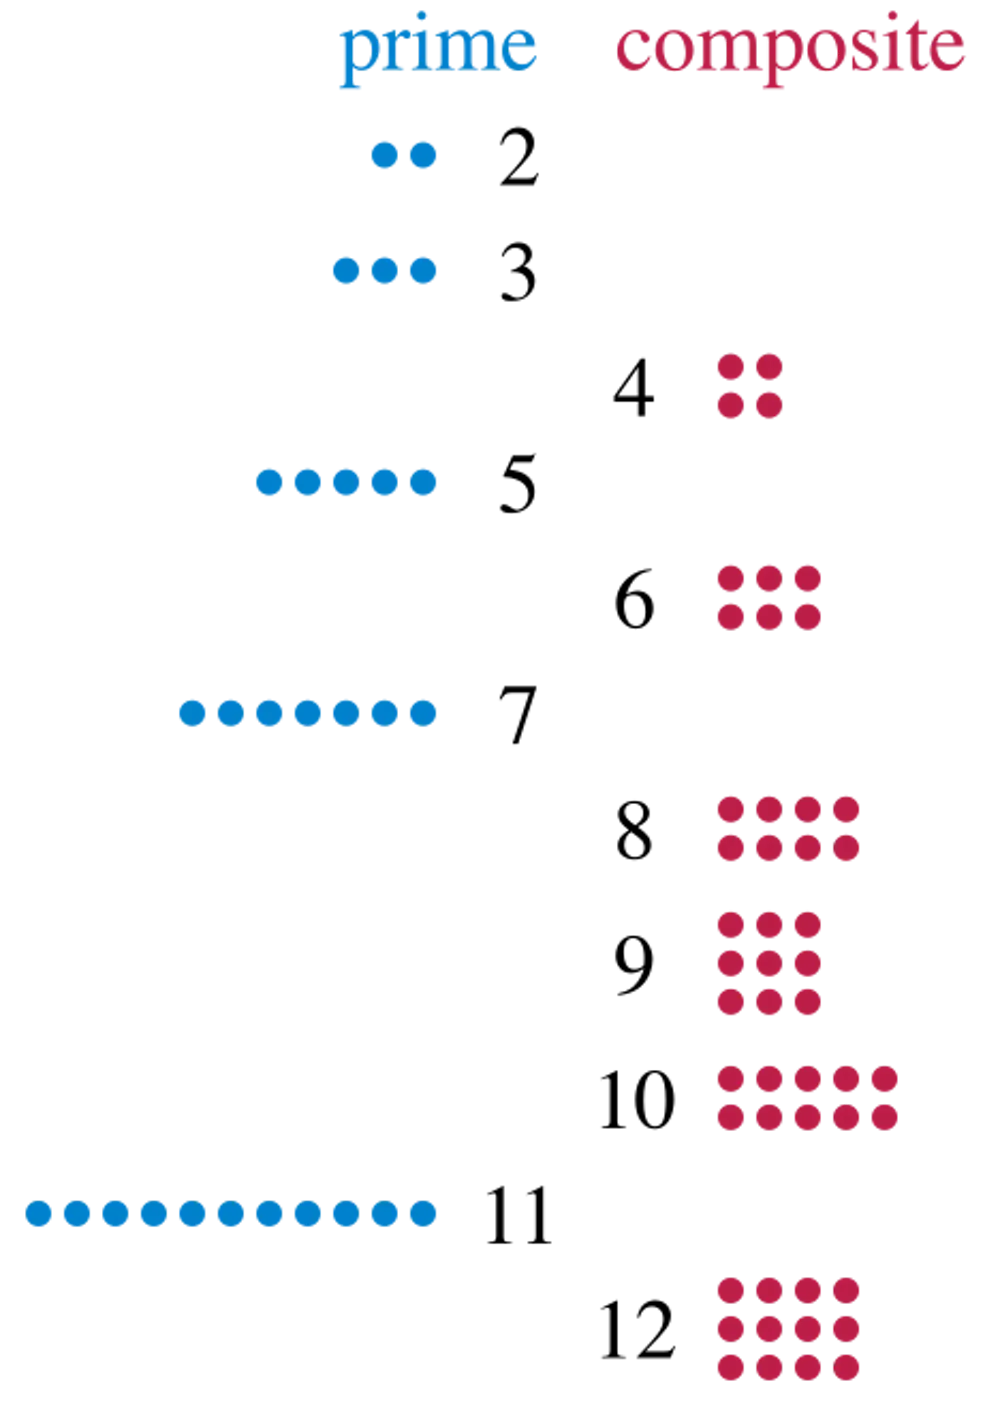
Let's talk about what primes actually are and how people use them.
A prime number is a whole number greater than 1 that cannot be divided evenly by anything except 1 and itself. That's it. Two is prime. Three is prime. Four is not, because it divides cleanly by two. Twenty-three is prime. Twenty-five is not, because five goes into it twice. Most people encounter this in seventh or eighth grade math and never think about it again until they hear the phrase What Is A Prime Number In Math The Unbreakable Building Blocks Of Mathematics floating around some article and get mildly curious.
What Is A Prime Number In Math The Unbreakable Building Blocks Of Mathematics
The fundamental theorem of arithmetic says every whole number greater than 1 is either prime or can be broken down into a unique set of prime factors. Forty-eight breaks into 2 × 2 × 2 × 2 × 3. There is no other combination of primes that multiplies to forty-eight. That uniqueness is why people call primes the building blocks, though "building blocks" implies they're stacked neatly together, which they aren't really. They're scattered in ways that still don't make complete sense. Let me walk through how you actually work with them before going further into definitions. If you need to test whether a number is prime by hand, the method is straightforward but tedious. You divide the number by every integer starting from 2 up to its square root. If none divide evenly, the number is prime. Testing 97 requires checking 2, 3, 4, 5, 6, 7, 8, and 9. None divide evenly. So 97 is prime. Testing 91 requires checking the same range. Seven goes into 91 exactly thirteen times. Not prime. The square root ceiling matters here because once you pass it, you're just repeating factor pairs you already checked.
For numbers under a few thousand, this manual approach works fine. Above that, it becomes impractical very quickly. A number with twenty digits would require roughly 4.5 billion divisibility checks at worst. Nobody does that by hand. Nobody even does it in a typical script without getting bored waiting for it to finish. I ran into this exact problem years ago while writing a small key generation tool for a internal project. The script was testing primality by trial division on random odd numbers around 10^12. It worked for a while, then started timing out on larger candidates. I switched to the Miller-Rabin probabilistic primality test with enough rounds to push the error probability below 1 in a trillion, and the whole process went from taking several minutes down to under two seconds per candidate. The tradeoff is that Miller-Rabin is probabilistic, not deterministic, but for practical purposes the chance of a false positive at those parameters is negligible. There are deterministic versions like the AKS primality test, but they're computationally heavier and rarely used outside of theoretical work. The Atkin sieve is another option if you're generating a list of primes up to a limit rather than testing individual numbers. It's faster than the Eratosthenes sieve for larger ranges, though for most everyday use that difference is academic.
Get the Full Details

One thing people consistently miss is that 1 is not prime. This isn't a trick question. It's baked into the definition because if 1 were prime, the fundamental theorem of arithmetic would fall apart. You'd get infinite factorizations since 1 could appear any number of times. Mathematicians agreed on this centuries ago, and it still trips up students on exams. Another common blind spot is assuming primes are evenly spaced. They aren't. You can find sequences of consecutive composite numbers of any length you want. Take any integer n greater than 1. The n consecutive numbers starting from n! + 2 are all composite. n! + 2 is divisible by 2. n! + 3 is divisible by 3. And so on. There is no upper limit to how far apart two consecutive primes can be, even though primes keep appearing forever. The gap between 7 and 11 is 4. The gap between 887,459 and 887,551 is 92. Gaps get wider as numbers get larger, on average, but irregularly. The Prime Number Theorem describes the average distribution. It says the density of primes near a large number n is roughly 1 / ln(n). That's an asymptotic result, not a precise prediction for any single number. It tells you that primes thin out, but it doesn't tell you where the next one will appear. There's no formula that generates the nth prime directly. If someone hands you a closed-form formula for prime generation, they're either joking or wrong.
Here's where it gets practically relevant. RSA encryption, which secures most of your internet traffic, depends on the fact that multiplying two large primes is easy but factoring their product back into those primes is hard. A 2048-bit RSA key uses two 1024-bit primes. Multiplying them takes microseconds. Factoring the result with current methods would take thousands of years on existing hardware. That asymmetry is the whole point. The catch is that quantum computers change this equation. Shor's algorithm can factor large integers in polynomial time on a sufficiently large quantum machine. We don't have one yet that can break real RSA keys, but the math is sound. Cryptographers are already moving toward post-quantum algorithms based on lattice problems and other approaches that don't rely on integer factorization. If you're just learning about primes and want to practice, write a simple script that finds all primes up to 10,000 using the sieve of Eratosthenes. It's a clean algorithm, runs in under a tenth of a second, and gives you immediate feedback. The sieve marks multiples of each prime starting from 2, then leaves the unmarked numbers as prime. It's elegant in a boring way, which is the right kind of elegant for this topic.
Don't bother memorizing lists of primes past 100. You won't use them. Understanding why they're defined the way they are and how they behave at scale is more useful than knowing that 97 is prime by rote. Twin primes—pairs like 11 and 13, or 17 and 19—are an open problem. There's no proof that infinitely many twin prime pairs exist, though strong evidence suggests they do. The twin prime conjecture has been around since Bernoulli and Goldbach were corresponding in the early 1700s. Zhang Yitang made progress in 2013 by showing there are infinitely many prime pairs with a gap of at most 70 million. That bound has been reduced dramatically since then, but the full conjecture remains unproven. Some questions in number theory just resist every technique we've developed. The practical takeaway is that primes are simple to define and surprisingly difficult to predict. Their scarcity grows logarithmically, their distribution hides patterns we haven't decoded, and their mathematical properties are what keep digital infrastructure functional. If you want a concrete reference for further reading, the online encyclopedia entry on prime numbers covers the definitions and theorems in detail, and the Wolfram MathWorld page on primes has more rigorous treatment if you need it.