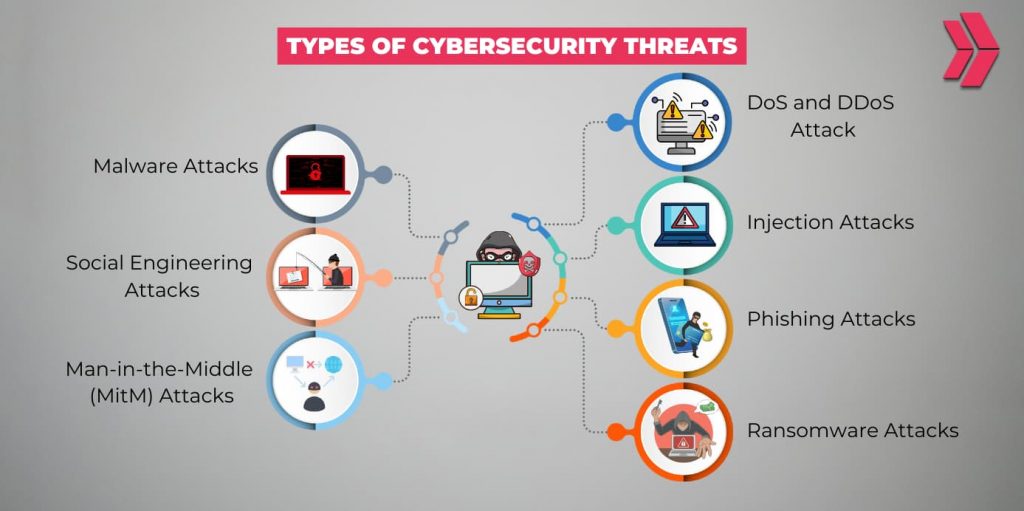
Understanding "Insecure" Across Two Very Different Worlds
Insecure is one of those words that shows up everywhere and means completely different things depending on where you see it. You will find it in browser address bars, in system configuration files, in performance benchmarks, and also in late-night thoughts about whether you are good enough at your job. Both uses are valid. Both are annoying when misunderstood. In cybersecurity, insecure refers to a state where a system, application, or communication channel lacks adequate protections against unauthorized access, data exposure, or manipulation. It is not a formal technical classification you will find in any RFC document. It is a practical label used by developers, security teams, and browsers to communicate that something needs attention. When Chrome displays a Not Secure warning next to an HTTP URL, it is telling you that traffic between your browser and the server is transmitted in plaintext. Anyone on the same network — an ISP, a coffee shop Wi-Fi operator, a malicious actor on a compromised router — can read what you send and receive. That is the baseline technical meaning.
But insecure in a broader security context goes beyond just HTTP versus HTTPS. A system can run HTTPS and still be insecure. I have seen this repeatedly in penetration testing work. A payment API served over TLS with a proper certificate, valid chain, and strong cipher suite. But the endpoint accepted SQL injection because the developer treated input validation as optional. The connection was secure. The application was insecure. These are not the same problem. Common categories of insecurity I encounter include unpatched software with known CVEs, misconfigured permissions that grant broader access than intended, hardcoded credentials in source code, missing rate limiting on authentication endpoints, and insecure direct object references where changing an ID parameter lets you access another user's data. Each one is straightforward to fix in isolation. They become exhausting when you are responsible for an entire fleet of services and half of them were built by contractors who moved on six months ago. There is a specific edge case that costs me about two hours of investigation every time it surfaces. It involves mixed content warnings that browsers flag incorrectly under certain redirect chains. You serve a page over HTTPS, but a JavaScript file loaded from that page triggers a redirect to an HTTP endpoint. The browser marks the entire page as insecure, even though the initial connection was encrypted. The workaround is to audit every asset URL with a tool like OWASP ZAP or even a simple curl verbose dump through the redirect chain, then update the internal base URLs to be protocol-relative or explicitly HTTPS. This usually catches the issue in under 20 minutes once you know what to look for. The first time you hit it without that knowledge, expect a longer afternoon.
Here is something beginners often miss: insecurity is not always binary. You do not simply have it or not have it. Security is a series of layers, and each layer has a different failure mode. TLS protects transit. But if your database stores passwords in MD5, the TLS layer is irrelevant to that problem. People conflate these frequently. They install a certificate and call themselves secure. It does not work that way. You need to evaluate each attack surface independently. Another counter-intuitive point is that making something more insecure on the surface can sometimes improve actual security. Enabling CORS with strict origin allowlists, for example, looks like it opens a door. But properly configured CORS prevents CSRF attacks that would otherwise go unnoticed on same-origin requests. The configuration requires more work and more scrutiny. Done poorly it is a liability. Done correctly it adds a meaningful defense layer. This is why blanket recommendations to disable CORS are usually wrong, and blanket recommendations to enable it are also wrong. The correct answer is almost always to configure it deliberately with a documented rationale. The personal side of insecure operates on a completely different frequency. This is the voice that tells you you missed something important in a security audit, that someone else on your team understands things you do not, that you are one misconfigured firewall rule away from a major incident. It is real in the sense that the anxiety produces real physiological stress. It is unreliable as a signal for actual competence.
Get the Full Details

I have sat in post-incident reviews where the person who felt most insecure about their role was actually the one who caught the root cause. I have also sat in reviews where the most confident person in the room was wrong about three separate things. Feeling insecure does not correlate cleanly with either being competent or being incompetent. It correlates more often with being aware of how much you do not know. That awareness is valuable. The paralysis that sometimes accompanies it is not. The overlap between the two meanings shows up in security culture. Teams that normalize admitting insecurity — meaning admitting uncertainty about their own security posture — tend to find vulnerabilities faster and fix them sooner. Teams that treat insecurity as a personal failure tend to hide problems until they become incidents. This is one of those organizational dynamics that is impossible to measure precisely but extremely obvious if you have been in enough security review meetings. Practical approach to assessing whether a system is insecure: run automated scanners first, but treat their output as a starting list, not a conclusion. Nessus, OpenVAS, and Burp Suite Community cover the common cases adequately. Then manually verify the findings. Automated tools miss context. They do not understand your business logic. They will tell you that a cookie lacks the Secure flag. They will not tell you that the application only handles public data and the cookie is inconsequential. That judgment call is yours.
For personal insecurity, the practical approach is less about fixing it and more about managing it. Write things down. Document your decisions, your assumptions, and your open questions. When you feel uncertain, check whether there is an actual gap in your knowledge or whether you are just carrying the weight of unknown unknowns. The former is fixable with study. The latter is fixed by accepting that nobody knows everything, including the people who sound like they do. The biggest limitation of this kind of analysis is that insecurity is dynamic. A system you assessed as secure last quarter may be insecure today because a new vulnerability was published, a dependency changed its behavior, or a configuration drifted. There is no final state. There is only continuous assessment. The same applies to personal doubt. Competence does not eliminate it. It just gives you better tools to act despite it. If you are dealing with a specific insecure system right now, start with the asset inventory. You cannot secure what you do not know you have. Then prioritize by exploitability and impact, not by how scary the vulnerability sounds. An unpatched file inclusion bug on an internal admin panel is usually more urgent than a theoretical timing attack on a publicly facing API that has no sensitive data behind it.
The word insecure is useful precisely because it is vague enough to cover a wide range of problems. That is also its weakness. Being specific about what is insecure, why it is insecure, and what would make it secure is what separates actual security work from anxiety wearing a security costume. Both involve the word. Only one involves the work.