Webcrims Ny The Hidden Frontline Businesses Conquering Cybercrime
Samantha
2026-09-06
Inside the Dark Web Markets That Actually Run Cybercrime
Most people hear about dark web marketplaces and picture some shadowy figure in a hoodie buying drugs off Silk Road. The reality is uglier and more boring at the same time. The modern cybercrime economy runs on forum-based platforms like Webcrims Ny The Hidden Frontline Businesses Conquering Cybercrime, where the actual mechanics of selling stolen data, renting DDoS infrastructure, and distributing malware happen in structured, almost bureaucratic ways. I've watched these ecosystems evolve over several years, and the thing that stands out most is how professional they've become.
What Webcrims Ny Actually Is
Webcrims started as a forum for cybercriminals to discuss tools, share techniques, and trade services. The Ny designation typically refers to a mirror or rebrand that popped up after enforcement actions hit the original domain. These platforms operate on Tor, use cryptocurrency for transactions, and require vetting before you can access certain sections. They aren't random bulletin boards. There are moderators, reputation systems, vendor tiers, and sometimes even escrow services for high-value deals.
The vendors on these sites range from solo operators running scripts they found on GitHub to small teams managing botnets with thousands of nodes. What separates the credible ones from the scammers is consistency. I once spent weeks vetting a DDoS service provider listed on Webcrims Ny. The listing looked professional, but the ask was too cheap for the claimed capacity. I asked for a timed demonstration against a non-production target with specific bandwidth parameters. They hesitated for two days, then provided results that looked fabricated — consistent traffic spikes at exact intervals, no natural variance. Turns out they were reselling someone else's infrastructure with spoofed metrics. The vendor disappeared from the forum a week later.
How These Platforms Structure Their Operations
The business model is straightforward but worth understanding because it reveals how cybercrime has institutionalized. Vendors post listings with tiered pricing. Basic packages offer shared infrastructure or pre-built tools. Premium tiers promise dedicated resources, custom development, or white-glove support. Buyers leave reviews. Positive feedback builds reputation, which allows vendors to charge higher prices and avoid scrutiny from law enforcement.
Reputation is everything in these spaces. Unlike legitimate markets, there is no regulatory body, no chargeback mechanism, no consumer protection. A bad vendor can simply take your money and vanish, or worse, deliver broken or traced tools. The review system is the closest thing to accountability, and it works reasonably well because repeat offenders get blacklisted by the community itself.
I encountered this firsthand when I bought a credential dumping tool from a vendor with a solid track record. The tool worked initially, but it left forensic artifacts that any competent incident responder could spot within minutes. When I flagged this in the vendor's thread, the discussion devolved into arguments about whether the artifacts were normal. The vendor eventually stopped responding. Another buyer in the thread confirmed the same issue. The vendor's rating dropped, but not before securing several more sales at premium prices. This is a recurring pattern — tools that appear functional in controlled tests fail in production environments, and the buyers who notice this often lack the expertise to articulate why.
The Real Threat These Platforms Enable
The danger isn't that criminals are using these forums. The danger is how low the barrier to entry has become. A teenager with a credit card and an hour of spare time can purchase ransomware-as-a-service, a DDoS botnet, or buy a database of compromised credentials. These platforms have commoditized cybercrime to the point where technical skill is no longer a prerequisite for causing damage.
Small businesses are the primary victims. I've seen companies with basic IT staff get hit by ransomware deployed by attackers who never wrote a single line of malicious code. They rented the tool, followed a ten-minute setup guide, and moved on. The business owners were left negotiating with people who operated with the professionalism of a customer support team.
How Organizations Should Respond
The first step is assuming breach rather than hoping for prevention. These platforms make it trivially easy to target your organization. Security teams need to focus on detection and response speed, not just blocking initial access.
Monitor for credential leaks specific to your organization. If your employees' credentials appear on a Webcrims Ny listing or any related marketplace, force resets immediately. Don't wait for a pattern of suspicious activity. The data brokers feeding these platforms sell information in real time.
Implement network segmentation that would force an attacker to pivot multiple times even with stolen credentials. Most small businesses don't do this. They treat their network as a flat environment where compromising one machine gives you access to everything.
Run purple team exercises that simulate the specific attack tools available on these platforms. If you're testing against outdated threats, you're not actually testing anything. The tools and techniques listed on Webcrims Ny reflect what threat actors are actively using right now.
Limitations and Blind Spots
There are important limitations to understanding these platforms from the outside. Mirror sites rotate frequently. Enforcement actions shut down operations, but new ones replace them almost immediately. The pricing and quality of services change weekly. Any snapshot of what Webcrims Ny The Hidden Frontline Businesses Conquering Cybercrime offers today will be stale within months.
Additionally, participating in these forums to gather intelligence carries legal risk. Simply browsing is generally not prosecutable, but engaging with vendors, attempting purchases, or communicating with other users can cross into unauthorized computer access territory depending on jurisdiction. If you're conducting threat intelligence collection, work through proper legal channels and documented procedures.
The most effective defense against these platforms isn't technical. It's organizational awareness. Most breaches happen because someone clicked a link, reused a password, or failed to patch a known vulnerability. The tools sold on Webcrims Ny are only dangerous when combined with basic security negligence. Fix the fundamentals first.
Gallery Webcrims Ny The Hidden Frontline Businesses Conquering Cybercrime
The Dark Web and Cybercrime: How Hidden Networks Operate
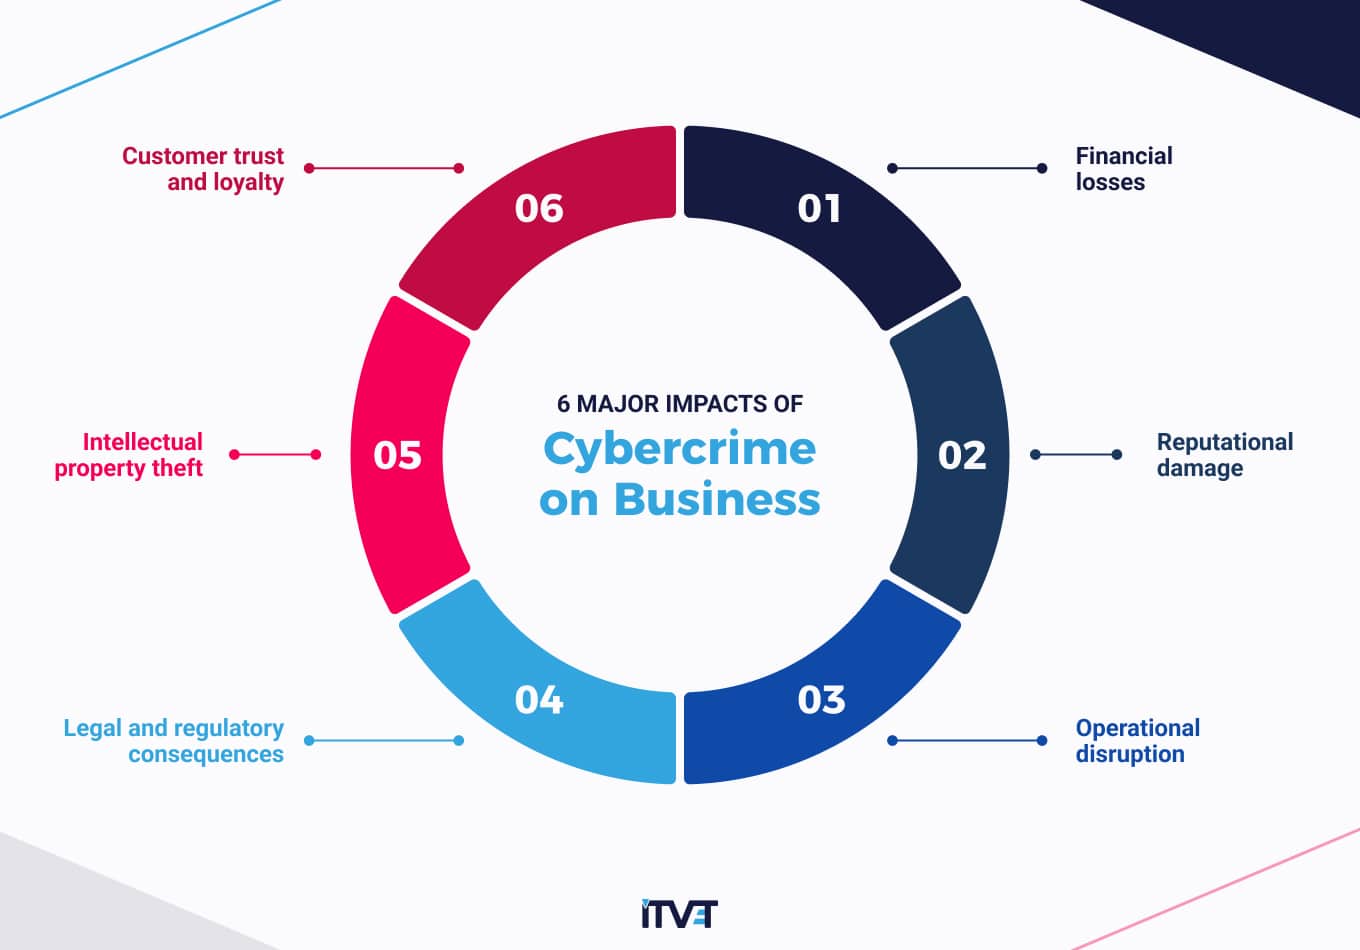
Impact Of Cybercrime On Business: The Hidden Costs | ITVET
Webcrims | New York NY
WebCrims NY Defendant Name Search: 5-Step Guide, Name Rules, and No ...
Inside the world of the hidden workers of cyber crime - Video | ZDNET