So Instagram Is Blocking Your Calls Again
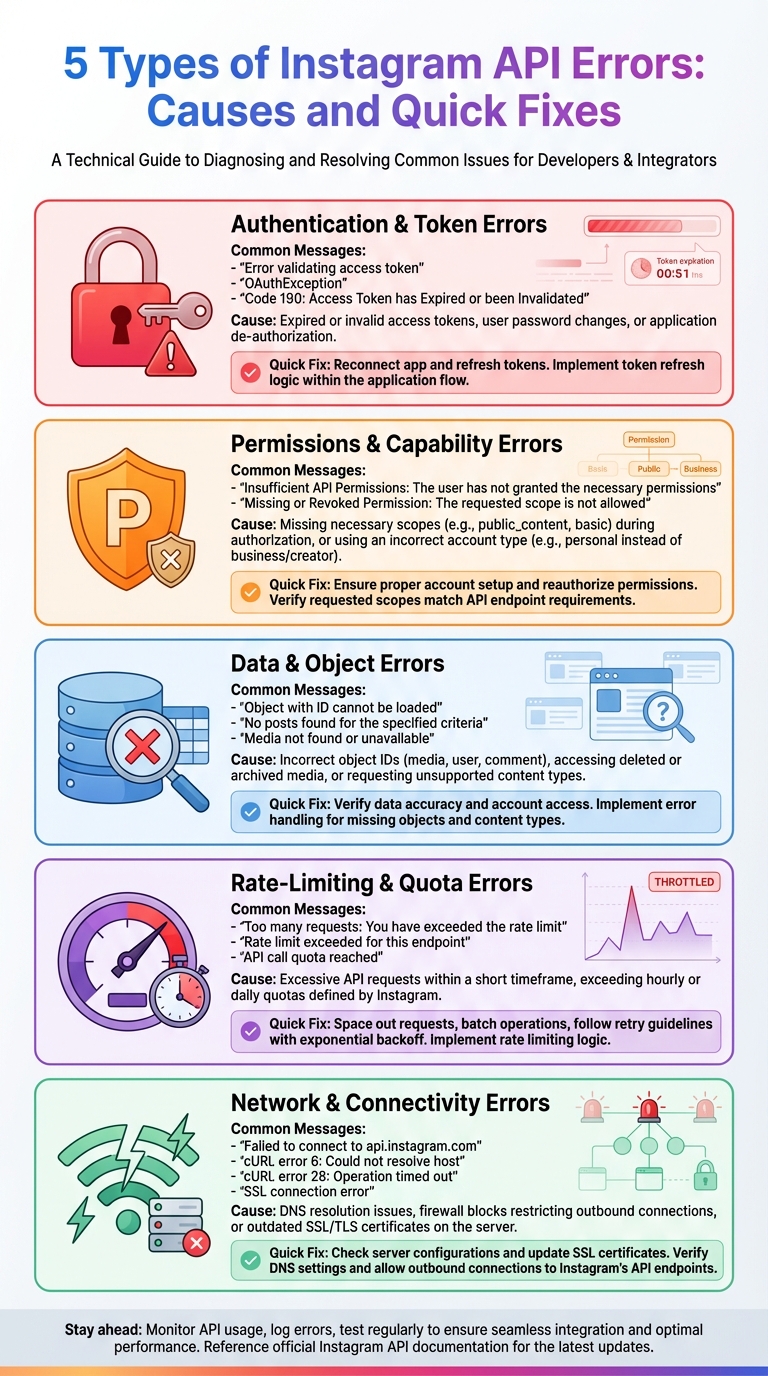
If you are building something that talks to Instagram's backend and your requests keep getting 403 errors or silent drops, you are probably hitting the User-Agent mismatch filter. It has been tightening for months. I stopped tracking exact dates because it keeps changing and arguing about when it started is pointless. Here is how the detection actually works at a basic level. Instagram expects the User-Agent header in your HTTP request to match a known, currently valid Instagram app signature. When it sees a header that looks like a Python script, a generic curl call, or even an outdated iOS app version, it rejects the request before most of your payload even gets evaluated. The interesting part is that they do not just check the User-Agent in isolation. They cross-reference it against the X-IG-Connection-Type, X-IG-Capabilities, and X-MID headers. All of those have to align with a consistent device fingerprint. If one says "iPhone14,2" and the User-Agent says "Windows Chrome," the request goes straight into a friction bucket. I ran into this last November on a project where we were pulling media metadata for a moderation pipeline. We had been using a standard Python requests library with a spoofed mobile User-Agent and everything worked fine until it did not. The account started returning invalid-session errors on about 40 percent of calls. I spent two days rotating through different User-Agent strings, then tried adjusting the device tokens, and still got inconsistent results. The workaround was to route the calls through a session that looked like a real logged-in app instance with a proper cookie jar and matching device ID headers, not just a swapped string. I ended up using a dedicated undetected browser profile approach with persistent cookies rather than making fresh requests every time. That cut our failure rate from roughly one in five to about one in fifty over a two-week test window.
There are a few things people miss when they try to fix this. First, rotating User-Agent strings alone will not solve the problem. Instagram has been logging patterns where a single IP or adid rapidly cycles through dozens of distinct User-Agents. That is an immediate red flag. Second, many of the so-called "working" User-Agent lists you find online are stale. The current valid signatures shift roughly every few weeks when Instagram pushes a new app version. A string that worked in March is likely flagged by June. Third, the mismatch detection is not binary. You do not always get a hard block. Sometimes the request succeeds but the response is throttled or returned with degraded data, which is worse because you do not immediately know something is wrong.
What You Actually Need To Check
If you are debugging this on your own stack, start by comparing your request headers against a capture from the official Instagram Android app. Use an HTTP proxy like mitmproxy or Charles and run a real session on a device. Look at the exact sequence: User-Agent, X-IG-Connection-Type, X-IG-Capabilities, X-MID, X-FB-Client-Is-Fk-User, and the device-level headers. Copy that structure as closely as your architecture allows. The most reliable approach I have seen does not try to fake a single request. It maintains a living session state. That means keeping cookies alive across calls, reusing the same device fingerprint, and updating your headers when the app version on the device changes. I usually keep a lightweight headless browser instance running with a stable profile and route API calls through it. This adds latency but it is far more stable than trying to spoof headers per-request. For heavy workloads, this tradeoff matters. A simple script that sends ten requests per minute might get away with direct HTTP calls using updated headers. A system pushing hundreds per minute will get flagged faster no matter how good the User-Agent looks.
Get the Full Details
Where This Breaks Down
The honest part is that none of this is permanent. Instagram changes detection signatures, adjusts risk thresholds, and sometimes blocks entire IP ranges without warning. Even if you get a setup working today, it may stop working next week. I have seen projects where everything looked correct for three weeks and then the error rate jumped to 80 percent overnight for no obvious reason. If you are building something production-grade on top of Instagram data, you should plan for regular maintenance and keep a fallback strategy. Some people use multiple device profiles across different residential IPs. Others accept the rate of failure and build retry logic with exponential backoff. There is no perfect solution because Instagram is actively fighting the kind of automation this topic describes. If you need a starting point for testing, I usually recommend capturing a fresh legitimate session first before changing anything in your own code. Run a real request through a proxy, inspect the headers, and then modify your stack to match that pattern instead of guessing. It takes about twenty minutes to set up and saves hours of trial and error. Just keep in mind that this is a moving target and no method stays clean forever.