Understanding the Visual Studio Code Login System
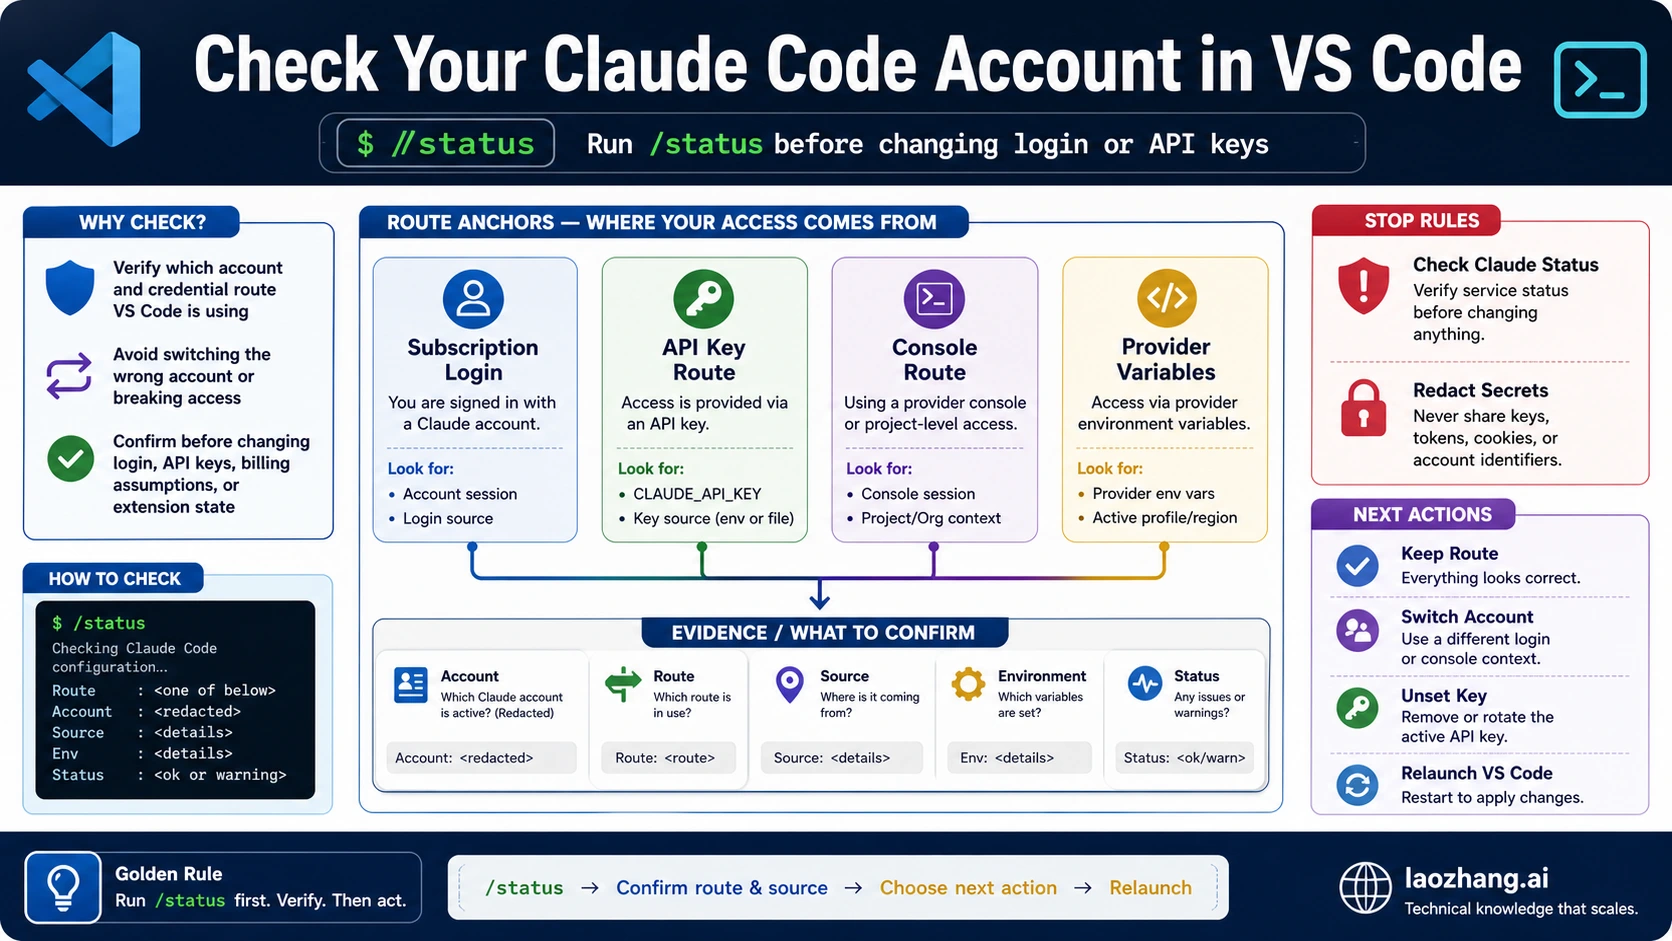
The authentication flow in Visual Studio Code handles several different identity providers, and each one behaves differently. Most users encounter the Microsoft account path when they're trying to sync settings, use the marketplace, or connect to Azure resources. There's also a separate GitHub sign-in path for extensions like GitHub Pull Requests and Issues. They do not share tokens, which causes confusion. I need to clarify something right away. There isn't a single unified login system inside VS Code. When people search for a VS Code login guide, they are usually running into one of three things: the Microsoft account sign-in popup, the GitHub authentication flow, or the credential store that gets created after you successfully sign in. Knowing which one is failing matters because the troubleshooting path diverges immediately. The Microsoft authentication flow works like this. You click the account icon in the bottom-left corner, select Sign In, and choose the provider. VS Code opens a system browser to the OAuth consent screen. After you approve it on the web, a callback URL sends the token back to the editor. The extension then stores the token in your OS credential manager. That's it. That's the whole mechanism.
When it breaks, which it does regularly, the problem is almost never the password. It's usually the credential store, the refresh token, or the browser session getting out of sync. I spent about three weeks last month dealing with a client who kept getting signed out every time they restarted their machine. The error was subtle. The Microsoft Account Manager extension was reporting an expired refresh token, but the credentials panel showed the account as active. We ended up deleting the cached token from the Windows Credential Manager under the MicrosoftVSCode entry, restarting VS Code, and re-authenticating through the system browser instead of the embedded one. The embedded browser is where most of these silent failures come from because it maintains a separate cookie jar from your system browser. Here is the practical way to troubleshoot this without reinstalling the editor or pulling your hair out.
Step-by-step troubleshooting process
Start by checking which identity provider is causing the issue. Look at the activity bar on the left side. If you see a Microsoft account with a warning badge, you are dealing with the Microsoft flow. If you see a GitHub icon with a red circle, that's a separate problem. The first thing to verify is whether your browser can reach the authentication callback. Open a terminal and navigate to the VS Code user data folder. On Windows, that is usually %APPDATA%\Code\User. On macOS, it is ~/Library/Application Support/Code/User. On Linux, it is ~/.config/Code/User. Check if there is a file called globalStorage storing auth tokens. Open the storage.json file and look for the keys ms-toolsai.vscode-auth or the GitHub equivalent. If those keys exist but the tokens look malformed, clear them. Clearing the tokens means deleting the relevant entries from that JSON file and also removing the corresponding credentials from your operating system. On Windows, open Credential Manager, go to Windows Credentials, and look for entries starting with MicrosoftOffice16 or MicrosoftVSCode. Delete them. On macOS, open Keychain Access and search for VS Code or Microsoft. Remove the matching certificates. On Linux, it depends on your desktop environment, but usually GNOME Keyring or KWallet is involved.
Get the Full Details
After clearing the stored credentials, restart VS Code and attempt to sign in again. This time, make sure you are signing in through the system browser, not the embedded Chromium window. The embedded browser sometimes has issues with corporate proxies, multi-factor authentication push notifications, and certain OAuth redirect URIs that the system browser handles correctly.
Common edge cases and what to do about them
Corporate networks are the biggest source of login failures. Many organizations use ZTNA solutions like Zscaler or cloud web firewalls that intercept TLS traffic. When VS Code's embedded browser tries to complete the OAuth handshake, these intermediaries often break the redirect. The solution here is to use the system browser for authentication and configure VS Code to allow that. You can set the auth provider to use the system browser by going into settings and searching for browser. Set the browser path to your system default. Another edge case involves multiple Microsoft accounts. If you have a personal Outlook account and a work account both stored, VS Code can get confused about which tenant to authenticate against. I encountered this when a user had both accounts and kept seeing invalid_grant errors. The fix was to sign out of both accounts completely, clear the credential store entries for both tenants, and then sign in with only the work account first. After that worked, the personal account could be added separately without conflicts. There is also the issue of extensions that bypass the standard login flow entirely. Some extensions handle their own authentication and store credentials in their own globalStorage subdirectory. If you are troubleshooting a specific extension login problem, check the extension's folder inside the globalStorage directory rather than the root auth entries.
What the system cannot do for you
VS Code's authentication system does not support SAML-based enterprise SSO out of the box. If your organization uses Okta, Azure AD with SAML federation, or any non-OAuth SSO provider, you will not be able to sign in through the standard VS Code UI. The workaround is to generate a personal access token from your identity provider and configure it manually in the extension settings. This is not ideal because it requires manual updates whenever the token expires, but it is the only path available without third-party tooling. The system also does not persist sessions across major VS Code updates reliably. I have seen cases where a successful login before an update would show as expired after the update, even though the underlying credentials were unchanged. The token format or storage location sometimes shifts between versions, and the extension has to re-establish the session. This is more common with the GitHub integration than with Microsoft accounts. If you are managing VS Code logins across a team or deployment, consider using extension management policies through VS Code's Enterprise features. These let you pre-configure authentication providers and restrict which ones users can switch between. It reduces the number of support tickets significantly, even though it adds administrative overhead upfront.
When to stop trying to fix it yourself
If you have cleared the credential store, used the system browser, verified your network path, and you are still getting authentication errors, the problem may be on the identity provider side. Check the status pages for Microsoft account services or GitHub's auth infrastructure. Sometimes the outage is not local at all. I have wasted hours debugging what turned out to be a GitHub OAuth service degradation. Those situations are rare but they do happen, and diagnosing them requires checking the provider status rather than digging deeper into the local configuration. Another scenario where further local troubleshooting makes no sense is when your organization's identity policy explicitly blocks VS Code's OAuth callback URLs. This happens more often than you would think with strict zero-trust networks. In that case, the only solution is to work with your IT department to whitelist the redirect URIs used by VS Code, which are documented in the extension manifests.