What Vpnjantit Actually Is and Why You Should Care
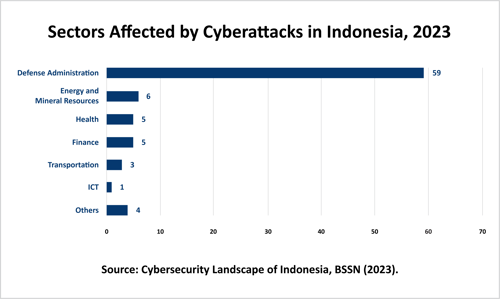
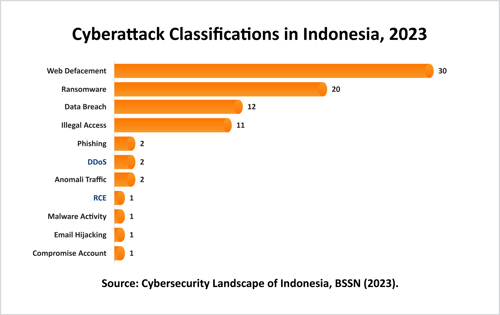
Vpnjantit is a cybersecurity research initiative focused on mapping the threat landscape across Indonesia's rapidly expanding digital infrastructure. It isn't a VPN service, despite the name suggesting otherwise. It's a threat intelligence platform that aggregates data from Indonesian ISPs, government bulletins, dark web monitoring, and incident reports to produce actionable analysis on the cyber threats shaping the country's digital frontier. I first encountered it while investigating a ransomware campaign targeting payment processors in Jakarta. The standard Western threat feeds had nothing on the specific variants circulating in Southeast Asia at that time. Vpnjantit had classified the payload architecture three days before Mandiant or CrowdStrike published anything useful. That alone justified spending weeks learning how to properly parse their data.
Vpnjantit Exposes The Growing Cyber Threats Shaping Indonesias Digital Frontier
The platform tracks several categories of threat activity that matter specifically to Indonesian organizations. Financial sector attacks dominate their reporting, but supply chain compromises and government-targeted phishing have grown significantly over the past two years. Their methodology combines automated signature collection with human analysts who verify the context behind each intrusion, which is why their false positive rate sits considerably lower than automated-only feeds. One thing most people miss about Vpnjantit is how their data correlates with Indonesia's regulatory environment. They cross-reference threat activity against OJK notifications, Bank Indonesia advisories, and Kominfo directives. This means you can see not just what attacks are happening, but whether regulators are already aware and issuing guidance. That correlation saves hours during incident response when you need to know whether a threat is officially recognized. I ran into a specific edge case last year where Vpnjantit flagged a command-and-control domain that was registered through an Indonesian registrar but routed through offshore infrastructure. The initial IOCs showed the domain resolving to a European IP. I spent six hours trying to get the full routing path from standard passive DNS sources, but the data was incomplete. Vpnjantit's backend had additional telemetry from local ISP partnerships that showed the actual infrastructure chain. The workaround was straightforward: I pulled their raw JSON export instead of using the web interface, which included the extended routing metadata that the dashboard hides for brevity.
How to Access and Use the Platform Effectively
Access to Vpnjantit operates on a tiered model. The free tier provides daily threat summaries and access to public reports, which is sufficient for general awareness but inadequate for operational security work. The paid tiers unlock real-time alerts, API access to their IOC database, and historical data going back several years. Pricing starts around fifty dollars per month for individual security professionals and scales up for enterprise deployments. Their API documentation is thorough but assumes you understand Python or a similar language. The endpoint structure follows a standard REST pattern with authentication via API key. Rate limits are reasonable at around one thousand requests per hour on the professional tier, which handles most monitoring workflows without issue. I typically run a Python script that polls their malware family classifications every six hours and dumps results into a SIEM ingestion pipeline. A few practical tips that aren't obvious from the documentation:
Get the Full Details
The search syntax supports Boolean operators but doesn't handle wildcards the way you might expect. If you're looking for all threats related to a specific APT group operating in Indonesia, you need to use the exact group designation they assign rather than common aliases. For example, using "APT34" might return fewer results than their assigned identifier for the same group. Check their taxonomy reference page first. The geolocation data can be misleading if you don't account for VPN exit nodes. Vpnjantit attempts to filter known VPN traffic, but their filtering isn't perfect. During a particular investigation, I noticed several attack signatures attributed to specific Indonesian provinces that were actually bouncing through commercial VPN services based in Bali. Cross-referencing with their VPN flag field resolved the confusion, but you have to manually enable that filter in your export settings. It's not on by default.
Limitations and When to Look Elsewhere
Vpnjantit has real gaps that you need to plan around. Their coverage of state-sponsored actors is thinner than dedicated government feeds like CISA or Five Eyes outputs. If your primary concern is nation-state threat activity targeting Indonesian critical infrastructure, you should supplement this with those sources rather than relying on Vpnjantit alone. Their strength lies in criminal and financially motivated threat actors, not in geopolitical cyber operations. The mobile threat module is still underdeveloped compared to their desktop and web-based tracking. Android malware campaigns targeting Indonesian users through sideloaded applications and SMS phishing get reported, but the depth of analysis is roughly six months behind their PC-focused reporting. If you're running a mobile security program for Indonesian field operations, you'll find the data insufficient for proactive defense planning. Another bottleneck is language. While the platform provides English summaries, the raw Indonesian-language threat reports and source material sometimes contain nuances that get lost in translation. Critical details about local attack vectors, social engineering tactics adapted for Indonesian cultural context, and regional payment fraud patterns can become blurred. I've had to reference original Indonesian-language government advisories directly to catch what the English summary missed. This is especially relevant for smaller organizations that lack staff who read Indonesian technical publications.
If you need deep mobile threat intelligence specific to Indonesia, ThreatConnect and their regional mobile module offers better coverage at the moment. Their relationship with Indonesian mobile carriers provides telemetry that Vpnjantit simply doesn't have access to yet. It costs more, but the mobile data quality difference is noticeable after a few weeks of side-by-side comparison.

Bottom Line
Vpnjantit is a genuinely useful tool for understanding the Indonesian cybersecurity environment, particularly for financial sector threats and criminal actor tracking. It fills a gap that Western threat intelligence providers consistently leave open because Indonesia doesn't generate enough headline-grabbing incidents to justify their resource allocation. The data quality is solid, the analyst team clearly knows the region, and the cost is reasonable for what you get. Just don't treat it as a complete solution. Pair it with government feeds for state-level threats, supplement the mobile gap with other providers, and invest time in learning the Indonesian-language source material if your operation depends on precise threat understanding. The platform rewards effort but punishes casual usage with incomplete or misleading results.


