VNC Authentication Is a Mess and Here Is How You Actually Set It Up
VNC was never designed with security as a priority. It shipped in the early 90s when most people still ran local networks without firewalls. That shows everywhere you look today, especially around authentication. The default setup is essentially a password gate with weak encryption, and that is why so many people end up with exposed desktops or broken connections they cannot fix. I have been configuring VNC servers for hardware labs, remote workstation setups, and legacy application access for over a decade. One of the things that catches people off guard is how many different authentication modes exist depending on which VNC implementation you are using. TightVNC, RealVNC, TigerVNC, and UltraVNC all handle passwords differently. They are not interchangeable. If you migrate from one to another without understanding the differences, you will spend an afternoon wondering why the same password suddenly stopped working.
Vnc Server Credentials What You Need To Know Before Secure Remote Access
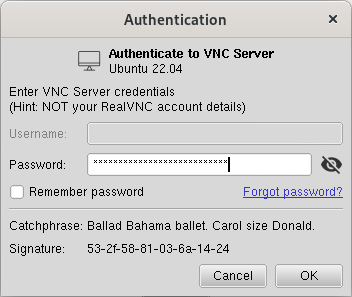
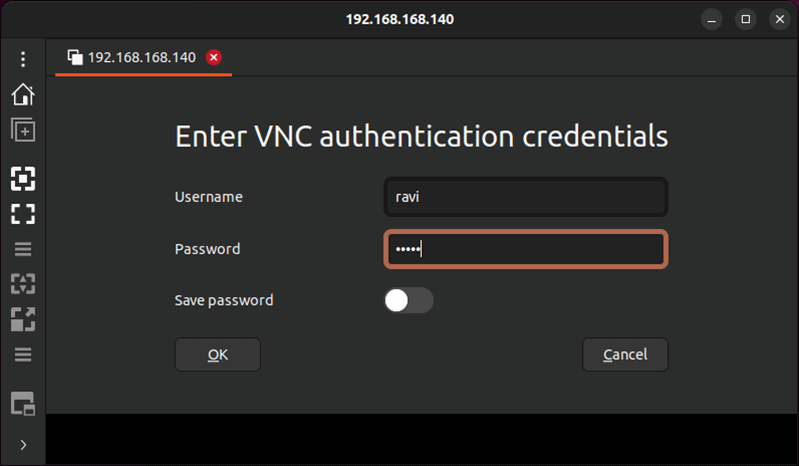
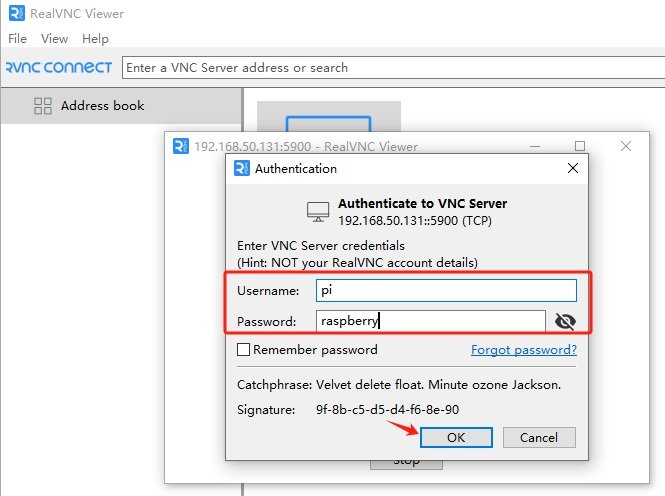
Let us get into the practical steps first, because that is usually where things go wrong. When you install a VNC server, the first thing you need to do is generate credentials in the correct format for that specific software. Most modern VNC servers use an encrypted password file rather than storing plaintext. On Linux systems using TigerVNC, you run vncpasswd and it creates a .vnc/passwd file with a proprietary hash. That password then only works with TigerVNC clients. If you connect with a RealVNC client to a TigerVNC server, it will reject the credential even though it is technically correct. For Windows systems running RealVNC Server, the password is stored in the registry under HKEY_LOCAL_MACHINE\Software\RealVNC\vncserver. The value type is encPass, which means it is already encrypted. You cannot simply edit that value with another tool and expect it to work. You have to use the built-in VNC configuration utility or run the server's built-in password change command. I learned this the hard way when I tried to push a standardized VNC password across forty machines using a config script. Thirty-nine of them broke because I pasted raw encrypted bytes into the registry instead of using the proper API call. Network-level authentication, sometimes called noVNC auth or SSL-based auth depending on your setup, is a completely different beast. This is where the VNC connection goes through an SSH tunnel or TLS wrapper before the VNC protocol ever touches the wire. In this mode, the VNC password becomes almost secondary because the outer encryption layer does the heavy lifting. This is also the mode that causes the most confusion. You might configure an SSH tunnel perfectly, set up port forwarding, and then still get kicked out because the inner VNC server is still demanding its own password and you only authenticated at the SSH level.
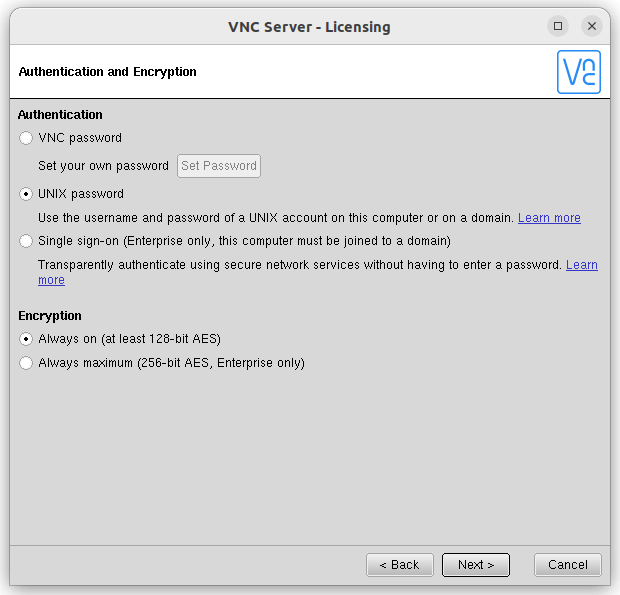
Here is a specific scenario that took me about six hours to track down last year. We had a TigerVNC server behind a pfSense router with port 5900 forwarded to the internal machine. The connection worked fine from inside the network but failed from outside. Every log entry showed authentication success, but the session would immediately close after login. No error message, just disconnect. I spent hours checking firewall rules, SSH configs, and VNC server files. The issue turned out to be that the pfSense captive portal was intercepting the initial VNC handshake, seeing it as unauthenticated web traffic, and redirecting to the login page. The VNC client received HTML instead of a protocol response and dropped the connection. Switching the forwarding rule to explicitly exclude the captive portal's source range fixed it. If you are dealing with unexpected disconnects on managed networks, check whether something between you and the VNC server is trying to authenticate web traffic first. Setting up a proper VNC server involves more than just choosing a password. You need to decide which authentication method matches your threat model. View-only passwords are a separate credential from full control passwords in most implementations. This is useful if you need to let someone observe a presentation or debug a display issue without giving them the ability to inject keystrokes. Setting a view-only password follows the same command pattern as a full password in TigerVNC, but you pass a different flag. In RealVNC, it is a checkbox in the security settings panel labeled View Only Password. The default security types vary by implementation. TigerVNC uses VeNCrypt by default, which supports TLS-encrypted sessions and several authentication mechanisms including plain password, X509 public key, and secure channel. RealVNC defaults to TLSv1 with X509 authentication on newer versions, falling back to plain if the client does not support encryption. TightVNC uses Tight authentication by default, which is a proprietary encryption method that is faster but less transparent than TLS. If you are working in an environment where audit compliance matters, VeNCrypt or TLSv1 is the safer choice because the encryption is standard and verifiable rather than relying on an opaque implementation.
Get the Full Details
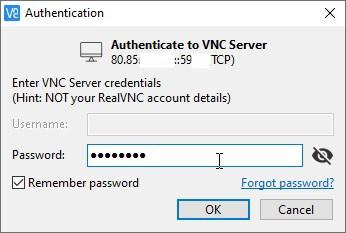
One thing beginners consistently miss is that VNC credentials are tied to the user account that created them. On Linux, if you run vncserver as your regular user, the password applies only to that user's display. Logging in as root and setting a VNC password does nothing for your user session. I have seen this bite people multiple times in containerized environments where the VNC server runs as a non-root user but the administrator assumes the root password will cover all displays. The fix is simple but easy to overlook: run vncpasswd under the same user account that will start the VNC server instance, or configure the server to read credentials from a central location like /etc/vnc/passwd if the implementation supports it. Another counter-intuitive detail is how clipboard sharing interacts with credentials. Many VNC implementations use the clipboard as an out-of-band channel for certain authentication handshakes during the initial connection. If you have a strict firewall rule that blocks UDP or certain TCP ports between client and server, clipboard sharing may silently fail. The connection will succeed but paste operations will not work. This is especially noticeable when people restrict VNC to a single port like 5900 and wonder why their clipboard redirection stops working after a firewall update. The workaround is either opening the clipboard relay ports or disabling clipboard sharing entirely if you do not need it. Let me be blunt about the limitations. VNC over an unencrypted connection should never cross an untrusted network. Period. The passwords are weak enough that brute force is realistic, and without TLS or SSH tunneling, the entire session is visible to anyone on the path. Even with encryption, the VNC protocol itself has known vulnerabilities including session hijacking through sequence number prediction and information leakage through screen updates. This is not fearmongering. These are documented issues that affect widely used implementations.
If you need true remote access security, you are better off using SSH with X11 forwarding, RDP with Network Level Authentication, or a zero-trust remote access solution. VNC makes sense in very specific cases: legacy hardware that only supports VNC clients, embedded systems with limited resources, situations where you need to remote into a machine before the OS has fully loaded, or environments where the network is already isolated and monitored. Outside of those scenarios, VNC is a compromise you accept for convenience, not a security decision. That said, when VNC is the right tool, getting credentials right matters. Use TLS or SSH tunneling. Keep passwords at least ten characters with mixed case, numbers, and symbols. Change view-only and full-control passwords independently. Test your configuration from outside the local network before relying on it for anything important. And if you ever see your VNC port open to the world on an attack surface scanner, close it or move it behind a VPN before something else decides to try it.