What People Actually Get Wrong About VirtualBox Hardening
Most guides you'll find online stop at enabling extended authentication and locking down shared folders. That's a decent starting point, but it leaves the actual attack surface almost entirely untouched. Real lockdown requires understanding that VirtualBox, like any hypervisor, makes assumptions about trust between host and guest that default configurations never question. Those assumptions are where the problems live. The first thing most people miss is that VirtualBox Lockdown Manager exists as a built-in mechanism and most admins don't know how to use it beyond setting a password. When you create a settings.vbox file with restricted profiles, you control exactly what the API can do. Without it, any process with access to the VBoxManage CLI or the COM interface can modify CPU count, memory allocation, network attachment, and storage controllers on a running VM. That's not theoretical. I had a container orchestration platform automatically spawn and tear down test VMs for integration testing. After three months of unmonitored VM creation, we found that one of the automation scripts was passing raw disk paths from the host into the VM configuration. The VM could see host filesystem mounts it had no business accessing. It took me about four hours to track down because the VBoxManage log output was buried under hundreds of successful provisioning commands. VirtualBox enables several network-related features by default that introduce attack surface. The host-only adapter creates a virtual network bridge between your host and guests, and it starts automatically when you install the software. Disable it if you're not using it. The NAT network feature is similarly enabled by default and creates an additional routing path. If you need isolated networking, stick to one method and remove the others.
USB passthrough is another area that people rarely lock down. By default, VirtualBox will allow any USB device matching a filter to be passed through to any VM that requests it. If you run multiple VMs on a single host, one compromised guest could theoretically enumerate and claim USB devices belonging to another VM. Set USB controller policy to deny by default and explicitly whitelist only the devices that are required for each VM's operation. This cuts down the USB enumeration attack surface to something manageable. Clipboard sharing between host and guest is bidirectional by default in the GUI. A guest with malicious intent can read clipboard contents from the host, and vice versa. If you're running untrusted workloads, disable clipboard sharing entirely. Even if you need it, restrict it to manual paste direction and turn off automatic clipboard synchronization. The performance hit is negligible. The risk reduction is measurable.
Lockdown Profiles and the Settings File
The real enforcement layer lives in your settings files. When you enable authentication in VirtualBox, you're not just protecting the GUI. You're adding a gate to the COM API, the VRDE interface, and the command-line tools. Here's how that actually works: VirtualBox reads a settings.vbox file for each VM, and within that file you can define a ExtraData section that controls locking behavior. The key entries are VBoxInternal/CPUM/DisableAccel, VBoxInternal/Devices/usb/0/Protocol, and the authentication-related properties under MachineRegistry. The most important setting is VBoxManage locking. When you set this to readonly, no modifications to the VM can be made through the API except read operations. This means even if someone gains access to your host with elevated privileges, they cannot change network configuration, add storage, or alter the VM definition without first removing the lock. I learned this the hard way when a colleague accidentally ran a bulk VM modification script that targeted the wrong host environment. Because I had the lockdown profiles in place on production VMs, the script failed gracefully rather than corrupting VM configurations across three dozen machines.
Get the Full Details

Network Isolation That Actually Works
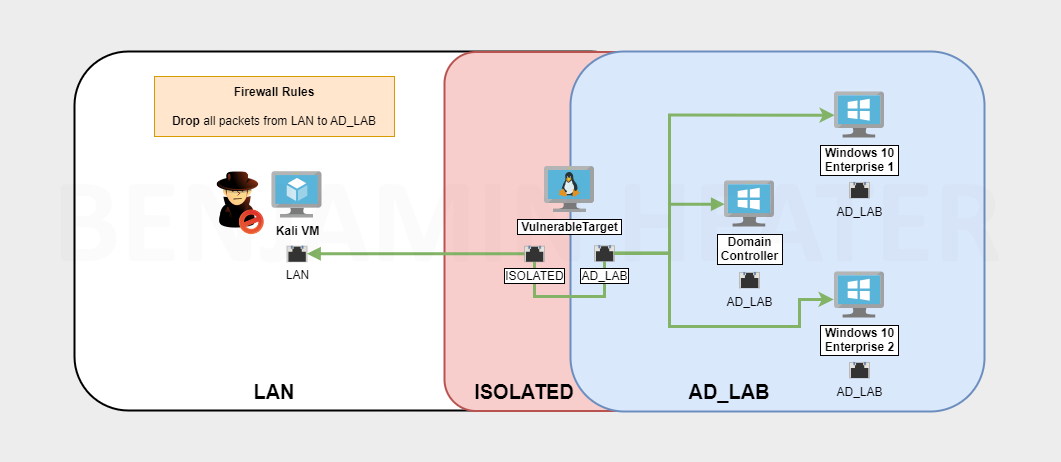
Most people configure a single bridged adapter and call it good. Bridged networking puts the VM directly on your physical network segment, which means it has the same exposure as any other device on that LAN. If you're not on a properly segmented network, you're giving the VM access to everything that host can reach. The better approach is to use a host-only network combined with a carefully configured NAT router VM. The router VM acts as a controlled gateway between the isolated guest network and the outside world. You can apply firewall rules on the router VM itself, monitor all outbound traffic, and prevent any direct host-to-guest communication except through explicit ports you've opened. This adds complexity but it also adds observable control over what the VM can actually reach. If you're running this in a multi-tenant environment, consider using separate VirtualBox instances with distinct VBoxXML data directories. This prevents VM A from being able to list or interact with VM B's configuration files. The default installation puts everything under ~/.VirtualBox or %APPDATA%\VirtualBox, which is a single shared directory. Splitting these directories means each tenant or workload gets its own isolated VirtualBox instance with its own authentication database.
Storage-Level Protections
VirtualBox uses VDI files by default, but VDI has known vulnerabilities related to image format parsing. Consider using VMDK or VHD formats instead, particularly when dealing with VM images from untrusted sources. VMDK has more mature input validation in the VirtualBox codebase and has been the subject of more extensive security review. Snapshot management is a hidden risk vector. Each snapshot creates a delta disk file that stores all changes from the base image. If a snapshot chain gets too deep, you're essentially running multiple layered storage volumes, and errors in delta file handling can lead to data corruption or, in worst-case scenarios, host filesystem access. I recommend keeping snapshot chains to three or fewer levels deep, and backing up the base VDI before applying any major patches or guest additions updates. One of my test environments had a snapshot chain with seventeen levels because nobody cleaned them up over eighteen months. When we tried to compact the base disk, the operation failed and corrupted the top two deltas. Recovering those VMs took nearly a day.
Guest Additions: Necessary but Dangerous
VirtualBox Guest Additions provide the shared folder implementation, clock synchronization, and improved graphics support that most people depend on. They also introduce a kernel driver on the host side that runs with elevated privileges. This driver, vboxdrv, is the most privileged component in the entire VirtualBox stack and the most likely attack vector for host compromise. If you don't need shared folders, disable them. If you don't need mouse integration, disable it in the VM settings. Each enabled feature is an additional kernel-level pathway between guest and host. I once audited a VirtualBox deployment where twenty-three VMs all had shared folders mounted from the same host directory. One misconfigured permissions entry on that directory meant any guest could write arbitrary files to a location the host used for build artifacts. The fix was straightforward: remove shared folders from all VMs and use an SFTP-based file transfer mechanism instead. It added about thirty seconds to the file transfer workflow and eliminated the kernel driver dependency entirely.
What VirtualBox Can't Protect You From
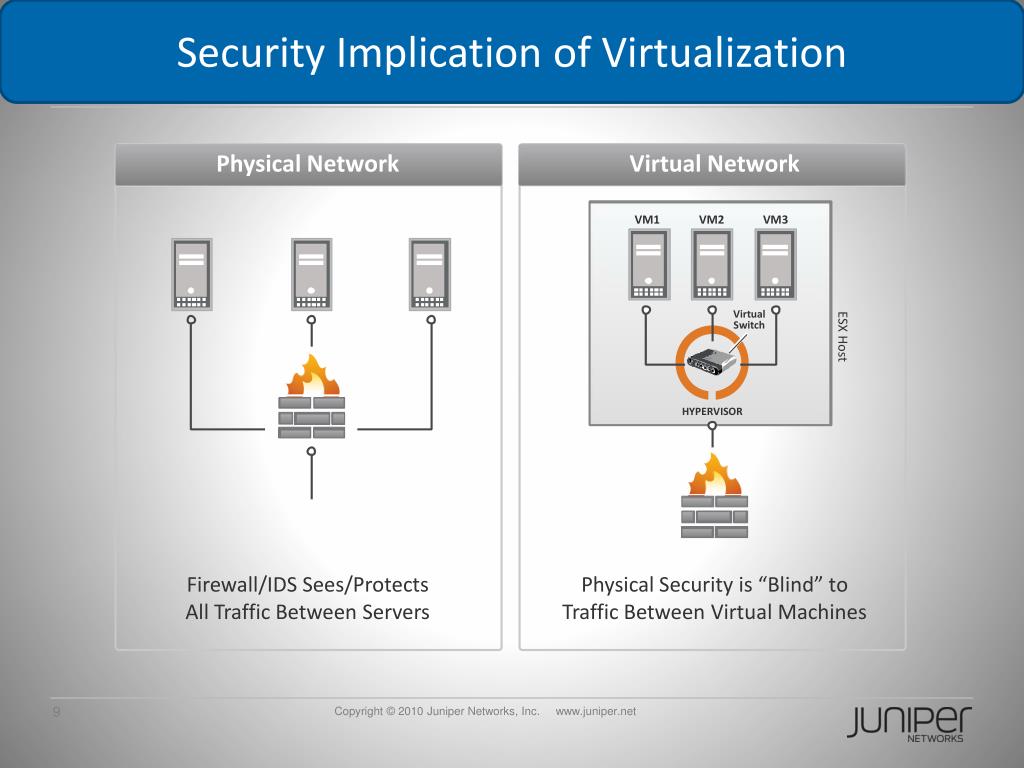
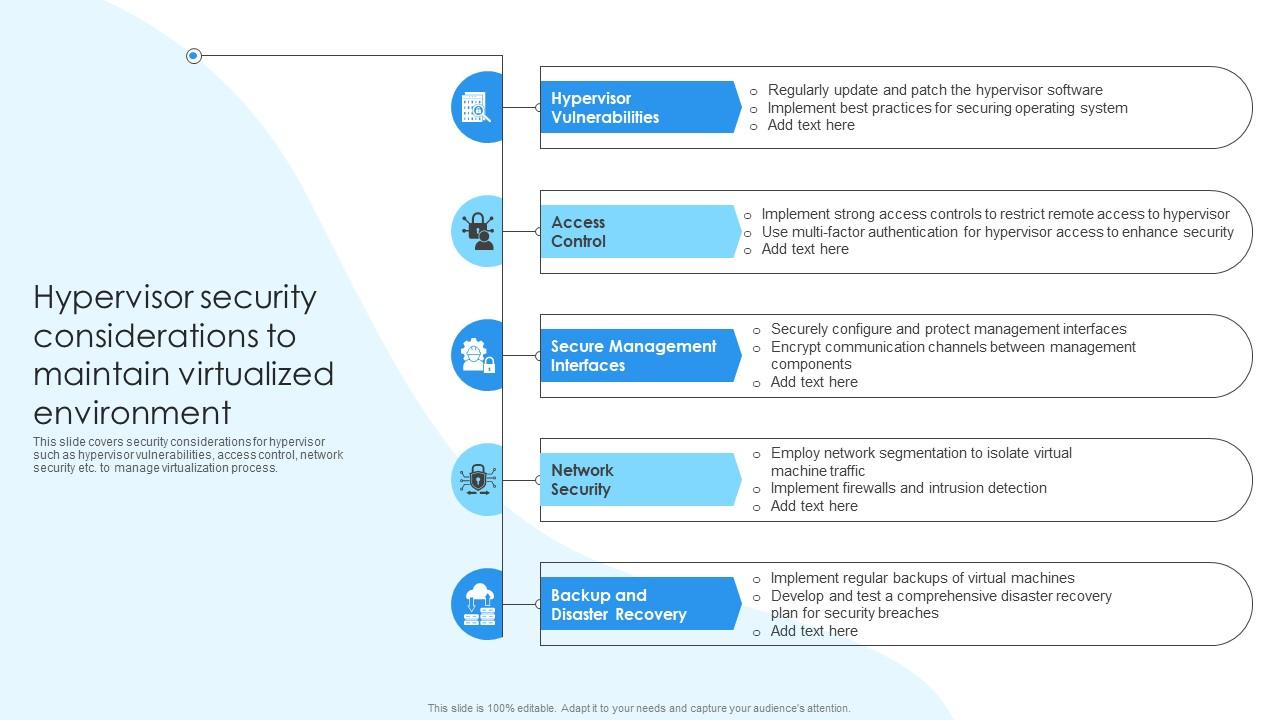
There are scenarios where VirtualBox security lockdown simply doesn't matter. If your host operating system is already compromised, VM-level restrictions are irrelevant. The attacker controls the hypervisor process, the kernel driver, and the network stack. VirtualBox cannot protect against a host-level compromise because the trust boundary runs through the host. In those situations, the only real mitigation is hardware-level isolation like Intel VT-d or AMD-Vi with DMA protection, and even those have documented bypasses. Similarly, if you're running VMs that execute untrusted code as a regular part of your workflow, VirtualBox provides defense in depth but not definitive containment. For that use case, consider a dedicated secure execution platform like Qubes OS, Firecracker microVMs, or a container runtime with proper seccomp profiles and namespace isolation. VirtualBox was designed for usability and compatibility, not as a security boundary. It's good at reducing risk. It's not designed to eliminate it. The practical result of all this is that VirtualBox security lockdown should be treated as a layered approach. Enable authentication, restrict the API, minimize shared features, isolate the network, and accept that the host OS remains the single point of failure. Any additional protection you need has to come from the infrastructure around VirtualBox, not from VirtualBox itself.