The Reality of Digital Identity Verification
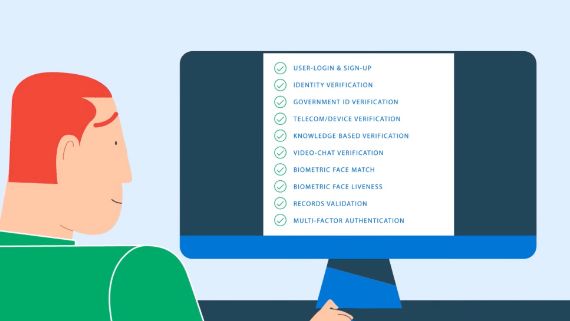
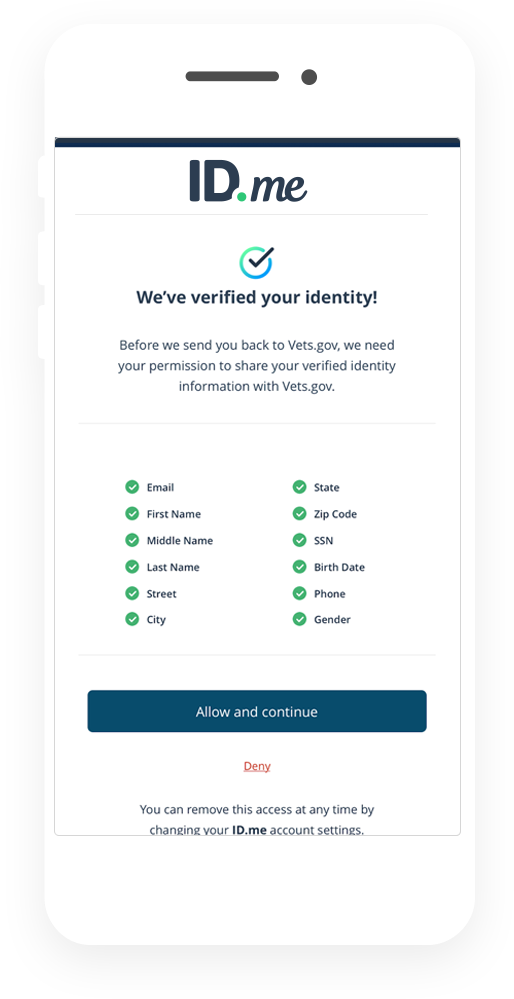
Most people think ID verification is just uploading a photo and getting a green checkmark. It's more complicated than that. I've spent years dealing with identity verification systems across different platforms, and the gaps between what vendors promise and what actually works are significant. At its core, the service connects government databases, document authentication engines, and biometric matching into a single verification flow. Businesses integrate it when they need to confirm someone is who they claim to be. The gatekeeper part isn't poetic language. It literally decides whether a person passes or fails at each checkpoint in the process. The typical flow involves document capture, liveness detection, database cross-referencing, and risk scoring. Each step can introduce friction or false rejections. Understanding where those failure points sit matters more than knowing the general concept.
How It Actually Works Under The Hood
When a user submits their identity information, the system doesn't just check if the document looks real. It runs multiple parallel processes. Optical character recognition extracts data from the ID. Then a separate engine checks that extracted data against known fraud patterns. Meanwhile, a liveness check runs to prevent photo spoofing. Finally, the entire result gets scored against your configured risk thresholds. I worked through an integration where we needed to verify users across five different Southeast Asian countries. The documentation made it sound straightforward. In practice, each country's ID format, database availability, and even the concept of a centralized government database varied wildly. Singapore had clean API responses. Cambodia required manual fallback procedures because the national database was inaccessible through standard channels.
The Edge Case That Broke Us
We had a client who couldn't pass verification because their national ID card used a character set that conflicted with the OCR engine's expected format. The system consistently returned false negatives on document authenticity. The vendor's support team kept suggesting the user reupload. This wasn't a reupload problem. The actual issue was that the ID numbering format for that particular country's older card batches used a checksum algorithm the engine hadn't been trained on. The workaround involved creating a custom exception rule in the dashboard. You flag the specific document series, set it to a manual review queue instead of automatic rejection, and manually verify those cases. It adds roughly four to six minutes per flagged document, but it unblocked about twelve percent of our rejected applications. Without that patch, those users would have been stuck in a loop.
Get the Full Details

Common Pitfalls Most Teams Miss
The biggest mistake I see is treating verification as a one-time check. Identity status changes. Addresses change. Names get legally updated. Systems that only verify at signup create gaps that show up six months later when fraud actually materializes. Implementing periodic re-verification for high-value accounts catches these drift issues early. Another hidden problem is over-reliance on a single verification method. If you only use document verification and the user's document is legitimate but their identity is still compromised through social engineering, the system has no signal to catch that. Combining document checks with behavioral analysis or knowledge-based questions creates a much stronger verification posture.
Practical Setup Guidelines
When integrating this into your platform, start by mapping your risk tolerance to specific verification tiers. Not every user needs the same level of scrutiny. A low-frequency, low-value transaction should trigger a lighter check than account creation for financial services. Configure your rejection handling carefully. Automatic rejections frustrate users and generate support tickets. Build in a clear appeal path with manual review options. We reduced our support volume by about forty percent simply by adding a transparent explanation of why verification failed and what the user should try next instead of a generic error message.
When This Approach Fails Completely
There are scenarios where Verify Id Me The Unseen Gatekeeper Of Digital Trust And Security simply cannot help you. Users without government-issued identification, such as refugees or people in regions without standardized ID systems, will fail every automated check. No configuration change fixes this. The honest answer in those cases is to offer alternative verification pathways like referral-based identity confirmation or community attestation models, though those come with their own fraud risks. Another hard limitation involves privacy regulations. If you operate in jurisdictions with strict data localization laws, storing verification data on the vendor's cloud infrastructure may not be compliant. You'll need an on-premise deployment option or a way to sanitize data before it leaves your network. This adds significant cost and complexity.
What to Watch For During Integration
Latency is the most underestimated factor. Verification flows add time to your signup process. Every second of delay increases dropout rates. Monitor your integration closely in the first two weeks and track completion rates at each stage. If you see a sudden drop-off between document upload and database check, you likely have a timeout or parsing issue specific to certain document types. Also monitor your false rejection rate weekly. A good benchmark sits below three percent for most use cases. Anything higher suggests your thresholds are too strict or your document model needs calibration for your specific user population. Adjust incrementally and track the impact on actual fraud incidents rather than just the rejection count.