Getting an Eauth Account Actually Works, Most of the Time
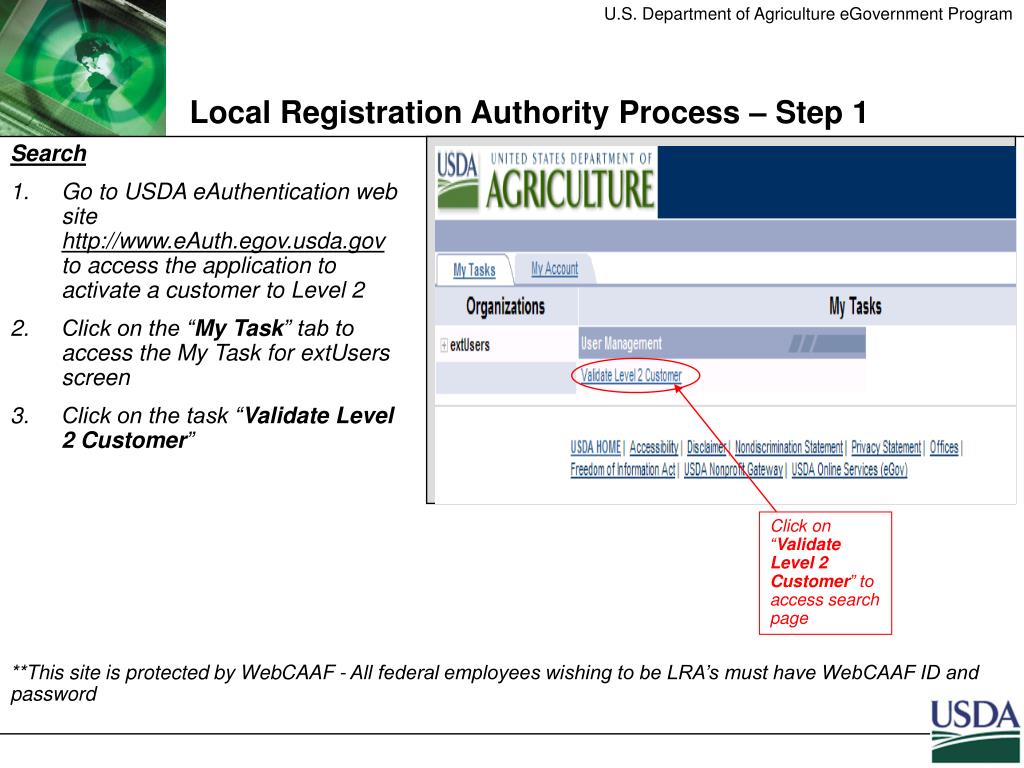
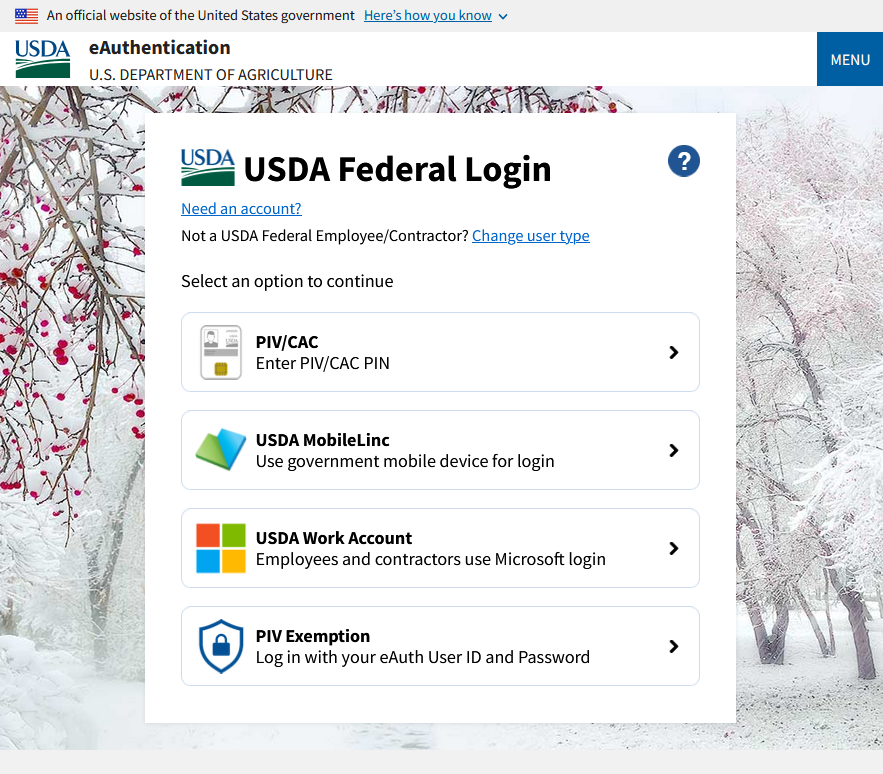
USDA EAuthentication is the single sign-on system that lets federal employees and contractors access USDA intranet resources. It's built on PIV/CAC standards, which means your authentication isn't just a username and password—it's a cryptographic certificate stored on a smart card or embedded in a mobile device. The login flow goes through FedRAMP-authorized identity providers, and once you're in, that session token maps to the specific resource you're trying to reach within the USDA network. The first thing people get wrong is assuming they can log in from any browser. It works fine on Chrome and Edge. Firefox occasionally throws certificate chain errors if your system hasn't been properly configured with the required CA roots. Safari on macOS tends to be the smoothest experience, honestly. If you're hitting constant redirect loops, clear your cookies and your stored certificates, then restart the browser. This usually resolves it within five minutes instead of sending someone down a support ticket rabbit hole.
Usda Eauthentication Your Essential Guide To Eauth Accounts And Security
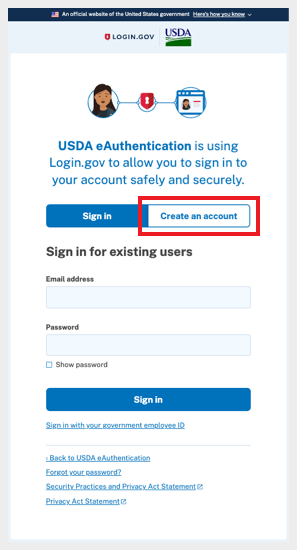
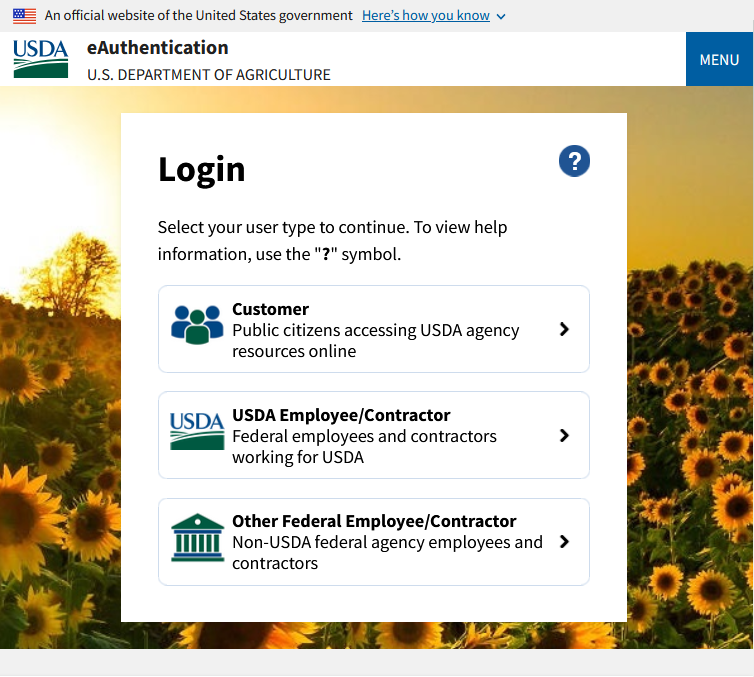
Here's how the enrollment process actually works. You need a valid PIV or CAC card first—you can't create an Eauth account without one. Go to idmanagement.gov and request enrollment through your agency's sponsoring office. The typical turnaround is three to five business days, though I've seen it drag to two weeks during peak hiring seasons. Once your enrollment is approved, you receive an activation email with a temporary link that's only valid for 72 hours. I've lost accounts more than once because I didn't activate them immediately. Don't make that mistake. After activation, you set up a personal recovery method—usually a security question or a verified mobile number. This is important because if you lose your card or it gets damaged, your Eauth credentials are tied to the card, not your personal identity. Recovery involves submitting a Hardware Identity Card Loss/Damage Report to your agency's PIV coordinator, and that process alone takes anywhere from one to three business days depending on how responsive your ISSO is. Let me give you a specific problem I ran into last year that the documentation doesn't really cover. I was trying to access the USDA Farm Service Agency's payment tracking portal while traveling, and my CAC was recognized by the machine but Eauth kept rejecting the certificate. The error code was vague—something like "credential validation failed." Turns out, the issue wasn't with my card at all. The portal I was accessing had an outdated trust anchor in its configuration. The certificate chain on my card included a root CA that had been rotated, but the portal's SP (service provider) metadata hadn't been updated. I worked around it by using the direct FAS portal URL instead of the general USDA SSO landing page, which pointed to a different identity provider that was already using the new root. Took about ten minutes of trial and error. Usually this kind of issue requires you to open a ticket with the specific program's help desk and wait 48 hours for a response.
The security architecture here is actually more robust than most people realize. Eauth implements multifactors out of the box—you need possession of your card, knowledge of your PIN, and in some cases biometric verification depending on the sensitivity of the resource you're accessing. The sessions use SAML 2.0 for federation, which means your credentials never touch the individual application servers. They only validate the assertion. This also means that if one USDA service gets compromised, your Eauth session data doesn't automatically leak across every other system. But there are real limitations. The system does not work well with virtual machines or sandboxes. If you're running USDA resources through a remote desktop session or a cloud VM, the smart card reader passthrough often fails silently. The certificate never makes it to the browser, and you get a generic "authentication failed" message with zero diagnostic information. The workaround is to use the USDA VDI environment directly or to configure a dedicated workstation with the card reader properly mapped. I've seen contractors waste entire afternoons troubleshooting this because the error messages are deliberately vague for security reasons. Another thing nobody warns you about: session timeouts. Eauth sessions typically expire after 15 minutes of inactivity for most systems, though some higher-visibility programs use a 5-minute timeout. When your session expires, the SAML assertion becomes invalid, and you have to re-authenticate entirely—you can't just refresh the page and continue. If you're working on long data entry tasks, keep a separate document open and paste your work there periodically so you don't lose everything when the clock runs out. This is one of those design choices that makes sense from a security perspective and absolutely sucks from a productivity perspective.
Get the Full Details

For people who need elevated access beyond standard Eauth—things like handling classified attachments or accessing systems that require SIPRNet-level credentials—you'll need additional authorization through your agency's information system security officer. That process alone can take two to four weeks and requires a background check refresh. Plan accordingly if your role involves sensitive program data. There's no shortcut around this, and trying to access restricted resources without proper authorization triggers automatic alerts to the USDA Office of Inspector General. If you're setting up your first Eauth account, start by verifying that your card reader is functioning correctly before you begin enrollment. Run the NIST SP 800-78 compliance test—most agencies have a diagnostic page at idmanagement.gov/test. If that passes, you're in good shape. If it doesn't, fix the reader or driver issue first. Trying to troubleshoot both the hardware and the enrollment simultaneously is how people end up wasting a full business day on something that should take an hour.