Showing Your IP Address in Linux
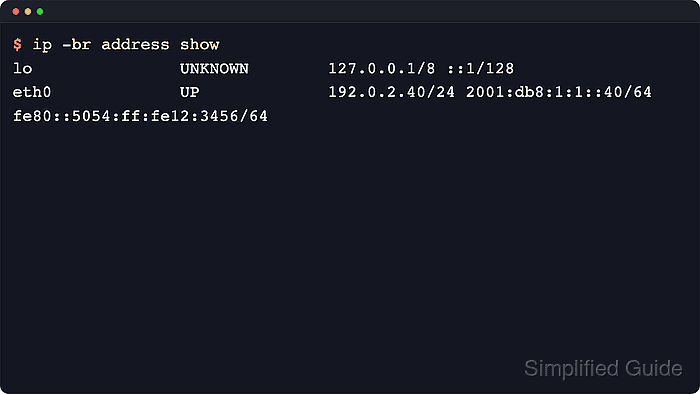
Linux gives you several ways to see your IP address, and picking one depends on what exactly you need. The quick commands work fine for most situations, but there are edge cases that trip people up if they only know one method. The ip addr command is the modern standard. Type it in your terminal and you get output showing every network interface on the system, along with IPv4 and IPv6 addresses, broadcast addresses, and the state of each link. The ifconfig command used to be the go-to tool, but it comes from the net-tools package which many distributions no longer install by default. You might still find it on older systems or legacy servers, but if you are setting up something new you probably will not have it available without installing extra packages. For just seeing your public IP address from outside your network, you can reach out to a service that tells you what external address you have. Commands like curl ifconfig.me or wget -qO- ifconfig.me do this in a single line. The result shows your public-facing address as seen by the internet. This is useful when you are troubleshooting NAT issues or confirming that port forwarding is working correctly on a router.
A Case That Caught Me Off Guard
I was setting up a containerized application on an Ubuntu server a while back, and the service was unreachable from the outside even though everything looked correct inside the container. The IP address shown by ip addr was there, the firewall rules were in place, and the container was running. The problem turned out to be that I was looking at the wrong interface. Docker creates its own virtual bridge network by default, and the containers get addresses on docker0 rather than on the physical eth0 interface. Running ip addr show showed me both, but I had been checking the wrong one in my scripts. The fix was using docker inspect to find the actual container IP, or binding directly to 0.0.0.0 when starting the container so Docker would map the port correctly to the host network. When you run ip addr, the output has a lot of information packed into each line. The interface name like eth0 or wlan0 tells you which physical or virtual adapter you are looking at. The inet line shows the IPv4 address with its CIDR notation, which indicates the subnet mask. A /24 means 256 addresses in that range. The scope field shows whether the address is global, link-local, or host-only. Link-local addresses start with 169.254 and are only valid on the local network segment. They are useful for services that need a consistent address without external routing. The state field at the end of each interface block tells you whether the link is UP, DOWN, or UNKNOWN. An interface can have a valid IP address assigned but still show as DOWN if the physical connection is not active. This happens sometimes with virtual machines or when a network cable gets disconnected. The mtu value at the bottom of each block shows the maximum transmission unit, which affects how large packets can be on that interface. Most Ethernet interfaces use 1500, but some VPN tunnels or specialized networks use smaller values like 1280 to avoid fragmentation issues.
Showing Your Private vs Public Address
Linux systems often have multiple IP addresses at the same time. The private address is what other machines on your local network use to reach you. This is usually in the 192.168.x.x range for home routers, or 10.x.x.x for larger networks. The public address is what the internet sees after the NAT translation on your router. These two addresses are different, and confusing them causes problems when setting up remote access or VPN connections. If you need to check which interface is getting the public address, run ip route to see the default gateway. The output shows which interface traffic goes out through when connecting to external networks. The gateway IP in that line is your router's internal address, and the interface name tells you which physical adapter handles the outbound connection. This is important when you have multiple network cards and want to ensure traffic is going through the right one.
Get the Full Details

Unveiling The Power Of Linux How To Show Ip Address With Ease
Once you understand the basic commands and how to read their output, managing network addresses on Linux becomes straightforward. The ip command gives you more detail than the older tools, and it works consistently across most modern distributions. The hostname -I shortcut shows all IP addresses assigned to the system in a compact format, which is handy for quick checks when you do not need the full breakdown. There are limitations to be aware of. The ip addr command shows addresses assigned to interfaces, but it does not always tell you which address is actually routable from outside your network. Virtual interfaces, Docker bridges, and VPN tunnels all add complexity. If you are working in a containerized environment or on a cloud server, the IP address you see locally might not match what external services see. Always verify with an outside check using curl or wget against a public service to confirm your actual public-facing address. For persistent configurations that survive reboots, the approach depends on your distribution. Debian-based systems use /etc/network/interfaces or Netplan configuration files. RHEL-based systems use NetworkManager or the /etc/sysconfig/network-scripts/ directory. Static IP addresses need to be set in these configuration files rather than just assigned with commands, because command-line assignments are lost when the network service restarts or the system reboots.
Some administrators prefer using nmcli for network management on systems with NetworkManager. It provides a command-line interface to the same graphical network settings, and it handles both wired and wireless connections well. Running nmcli device show gives detailed information about each network device, including IP addresses, DNS servers, and connection status. This is useful when you need to troubleshoot why a wireless connection is not getting an address from DHCP. When checking IP addresses remotely over SSH, the hostname -I command is concise enough to paste into automation scripts. It returns just the addresses separated by spaces, which makes parsing easier than the verbose output from ip addr. For logging purposes or automated monitoring, this compact format saves time when you need to collect address information from multiple servers in a loop. Advanced users sometimes need to see IP addresses for specific protocols or address families. The ip -6 addr command shows only IPv6 addresses, which is helpful when you are troubleshooting dual-stack configurations. IPv6 addresses are longer and use a different notation, but the command syntax stays the same. Some systems may have multiple IPv6 addresses on the same interface for different purposes, like link-local addresses for router discovery and global addresses for external communication.
Network namespaces add another layer of complexity on modern Linux systems. Containers and virtualization tools use namespaces to isolate network stacks, which means the same machine can have completely different IP addresses visible from different namespaces. Running ip addr inside a namespace shows only the addresses assigned within that isolated network view. This isolation is why checking your IP address from within a container sometimes gives a different result than checking from the host system. Older tutorials sometimes recommend ifconfig without mentioning that it is deprecated on many systems. The net-tools package that provides ifconfig is no longer maintained and may not be installed on fresh systems. Using ip addr instead avoids compatibility issues and gives you more current information. The command syntax is slightly different but the output is more detailed and reliable for troubleshooting real network problems. When setting up services that need to bind to specific addresses, understanding which IP is which becomes critical. A service bound to 127.0.0.1 will only accept connections from the local machine, while binding to 0.0.0.0 accepts connections on all interfaces. The distinction matters for security and accessibility. Misconfiguring this can leave a service unreachable from the network or exposed to unwanted connections depending on your intent.

The ss -i command shows socket statistics including the local and remote IP addresses for active connections. This is useful when you need to verify that a service is actually listening on the expected address and not silently falling back to a different binding. Combined with netstat alternatives, it gives visibility into connection states that ip addr alone cannot provide. For automated scripts that extract just the IP address without extra output, using ip -4 addr show scope global | awk '{print $2}' | cut -d/ -f1 gives you a clean single IPv4 address. This approach filters for global scope addresses, extracts the address field, and removes the CIDR suffix. It is more reliable than parsing ifconfig output because the ip command format is consistent across versions and distributions. Cloud instances and virtual machines sometimes have multiple network interfaces with different purposes. The primary interface handles general traffic while secondary interfaces might be used for storage networks or management traffic. Each interface can have its own IP address, and knowing which one to use depends on what you are trying to connect to. Running ip addr show lists all of them so you can pick the right one for your task.
DNS resolution and IP address reporting are separate concerns. The dig or nslookup commands show how domain names resolve to IP addresses, but they do not tell you what IP address your own system has. Knowing your system's IP is different from knowing where a website resolves. Both pieces of information are useful in networking, but they come from different commands and serve different diagnostic purposes. When diagnosing connectivity issues, checking your IP address is often the first step. If the address is missing or shows as 169.254.x.x, your system failed to get a proper address from DHCP. This indicates a network configuration problem or a router issue rather than a problem with the checking command itself. The link-local address is a self-assigned fallback that only works on the local segment and will not reach external networks. Some enterprise environments use DHCP reservations or static leases configured on the router. In these cases, your IP address might change if the lease expires or if you connect through a different port on the switch. Keeping track of address assignments in a spreadsheet or network documentation tool helps when troubleshooting intermittent connectivity problems that seem random but are actually tied to DHCP lease renewal timing.
The hostname command with different flags shows various address information. hostname -i resolves the local hostname to IP addresses using the system resolver, which may return different results than ip addr if DNS or /etc/hosts entries are configured in a particular way. Understanding this distinction prevents confusion when scripts return unexpected addresses based on hostname resolution rather than interface configuration.