So You're Moving PHI to the Cloud. Let's Actually Talk About HIPAA Compliance.
Most organizations approach cloud HIPAA compliance backwards. They look at a list of required controls, check off what they can, and assume they're done. That's how you get fined. The framework isn't a checkbox exercise. It's a continuous state of evidence that your business associate handles protected health information exactly the way you promised you would, and that your covered entity responsibilities haven't disappeared just because data now lives in someone else's infrastructure. I spent about four years managing compliance for a mid-size health system that migrated from on-prem to AWS. We went through two audits, one incident investigation that turned into a reportable breach, and roughly a dozen security assessment rounds with our third-party vendors. Here is what actually matters when you're dealing with HIPAA and cloud compliance, the parts nobody puts in their marketing deck.
Unveiling The Cloud What You Should Know About Hipaa And Cloud Compliance
First thing to understand: HIPAA doesn't actually certify clouds. There is no "HIPAA certified AWS" stamp. Amazon, Azure, Google, Oracle — none of them hand you a certificate that absolves you of responsibility. What they give you is a Business Associate Agreement template and an attestation that they have implemented certain safeguards. Your obligation is to evaluate whether those safeguards are adequate for your specific use case, configure the environment correctly, and maintain evidence continuously. The 2013 Omnibus Rule made this clearer. Covered entities are now directly liable for their business associates' compliance failures. Before that, you could point at your vendor and say it was their problem. Now the HHS OCR treats your BAA as a binding chain of accountability. If your cloud provider has a gap and PHI is compromised, both you and they can be fined. Not one or the other. Both. Here is the configuration reality that most teams miss: HIPAA's Security Rule requirements around encryption at rest and in transit are straightforward on paper but completely dependent on which service and which settings you enable. S3 default encryption is not on. RDS default encryption might be on in some regions but you need to verify. DynamoDB encryption needs to be explicitly enabled per table. KMS key rotation happens automatically only if you configure it. This is not theoretical. In my experience, a single unencrypted Redshift cluster sitting behind a VPN tunnel was the exact vulnerability that came up in a 42-day audit cycle we had running. The auditor didn't even flag it as malicious — they just noted it as an incidental finding that required immediate remediation. We had to document the risk assessment, implement encryption, and produce a corrective action plan within three weeks.
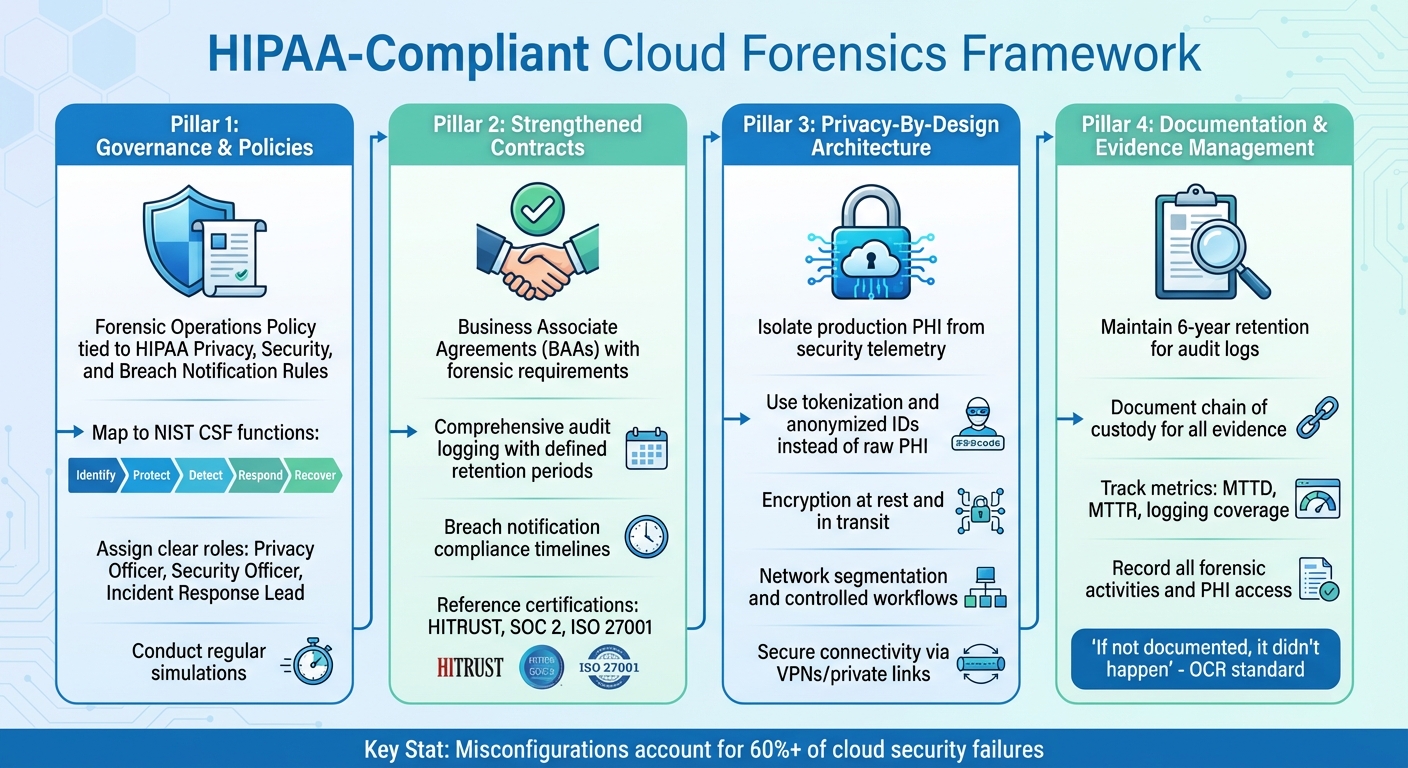
The access control piece is where organizations consistently underinvest. MFA on console access is table stakes and easy to implement. What people overlook is the granularity of IAM policies for service accounts and automated processes. A hardcoded API key with broad S3 bucket access might function fine for your development team until it leaks in a public GitHub repo. That happened to a client I consulted for. Their "service account" credentials were exposed in a commit from 2019. The breach wasn't discovered until a routine penetration test in 2022. The impact was limited because there was no bulk PHI access, but the compliance fallout alone — documentation review, remediation plan, updated monitoring — cost roughly forty thousand dollars in professional services and internal engineering time over six weeks. Let me address something that comes up constantly: shared responsibility models. AWS and Azure both publish these documents and most teams read them once and file them away. The shared responsibility model means the cloud provider secures the infrastructure. You secure everything inside it. That includes your logging configuration, your backup strategy, your key management, your incident response procedures, your workforce training records, and your risk analysis documentation. If you assume the provider handles logging, you will discover during an audit that CloudTrail logging was disabled on three out of five accounts in your organization. I've seen this multiple times. The audit trail requirement under HIPAA is particularly unforgiving. You need to maintain logs that show who accessed what PHI, when, and from where. In a cloud environment this means centralized logging across multiple accounts and services. CloudWatch Logs, CloudTrail, VPC Flow Logs, RDS Audit Logs — they all feed different pieces of the puzzle. Most teams pick one or two and ignore the rest. That is insufficient. A proper implementation aggregates all of these into a single SIEM or logging platform with tamper protection and retention policies that meet or exceed HIPAA's six-year requirement for certain documentation.
Get the Full Details
One counter-intuitive point about business associate agreements: having a BAA with your cloud provider is necessary but not sufficient. If you then connect that provider to a subcontractor — a backup service, a monitoring tool, a third-party analytics platform — you need a BAA with that subcontractor too. HIPAA requires the chain to be unbroken. I've seen organizations skip this step with lightweight SaaS tools that seemed harmless. A patient data visualization dashboard with no explicit BAA became the sole vector in a breach that resulted in a $3 million settlement. The tool processed aggregated data but had access to full PHI through API integration. The OCR ruling was clear: any entity that creates, receives, maintains, or transmits PHI on behalf of a covered entity is a business associate regardless of how small or seemingly innocuous their role appears. Backup and disaster recovery are another area where compliance and operational reality diverge. HIPAA requires contingency planning with data backup and disaster recovery procedures. The regulation does not specify frequency, retention period, or geographic distribution. But the interpretation during an audit is strict. If you claim daily backups, you need to demonstrate that daily backups actually exist and are recoverable. If you claim geo-redundancy, you need to prove failover works. I ran a quarterly restore test for our environment. Two out of five restores failed in the first year due to misconfigured backup policies. One failure was because a developer had changed an IAM policy that blocked the backup service from reading recent snapshots. Another was because a replication setting had been accidentally disabled. These are not edge cases. They are routine operational problems that only surface under testing. The human factor deserves attention here too. Workforce training is a HIPAA requirement and cloud environments change faster than most training programs can keep up. Moving from on-prem to cloud introduces new access patterns, new threat vectors, new compliance considerations. A nurse who understands password policies on a hospital server doesn't automatically understand IAM roles and cross-account trust relationships. I built a quarterly training module specifically around cloud security for our clinical and administrative staff. It wasn't glamorous but it reduced our phishing click rate from about eighteen percent to under four percent over eighteen months. More importantly, it created a culture where people reported suspicious activity instead of ignoring it.
Documentation is probably the single biggest source of compliance friction in cloud environments. HIPAA requires a written risk analysis that is updated at least annually. Most teams treat this as an annual checkbox exercise. The regulation implies continuous risk management. When you deploy a new service, modify an existing one, or integrate a new vendor, the risk landscape changes. If your documentation doesn't reflect those changes, you're non-compliant even if your actual security posture improved. I've worked with organizations that invested heavily in automation tools to handle compliance monitoring. Some of them work well. Tools like AWS Config Rules, Azure Policy, and third-party platforms like Drata or Vanta can automate a significant portion of evidence collection and continuous monitoring. But they introduce their own complexity. Misconfigured rules produce false positives that drown your security team. Overly broad policies create compliance fatigue where everything gets flagged and nothing gets attention. The sweet spot is typically a hybrid approach: automated monitoring for known controls, manual review for novel or complex scenarios, and human judgment for risk acceptance decisions. Cost is another factor that gets minimized in compliance discussions. HIPAA cloud compliance for a mid-size organization typically runs between one hundred thousand and four hundred thousand dollars annually depending on infrastructure size, complexity, and whether you outsource the compliance function. This includes personnel, tools, audit fees, and incident response reserves. Smaller practices can do it for less but the minimum viable approach still requires dedicated security expertise, not just a part-time IT person checking boxes.
If you're starting from scratch and need a practical entry point, here's what I'd recommend based on actual implementation experience: begin with a documented risk analysis that covers every system touching PHI, regardless of where it lives. Then implement the lowest-hanging controls first — MFA everywhere, encryption at rest and in transit with verified configurations, centralized logging. Get your BAAs in order before you migrate any data. Run restore tests quarterly and document the results. Invest in continuous monitoring tools rather than relying on annual point-in-time assessments. And build a relationship with a compliance professional who understands both HIPAA and cloud architecture before you need them during a crisis. The technology will keep changing. The regulations will too. What stays constant is the principle that compliance is an ongoing practice, not a destination. Cloud environments make some aspects easier through automation and centralized visibility while making others harder through scale and complexity. The organizations that get it right treat it as a core operational discipline rather than a regulatory obligation to minimize.