Serial Numbers On Hackable Switches: What You Actually Need To Know
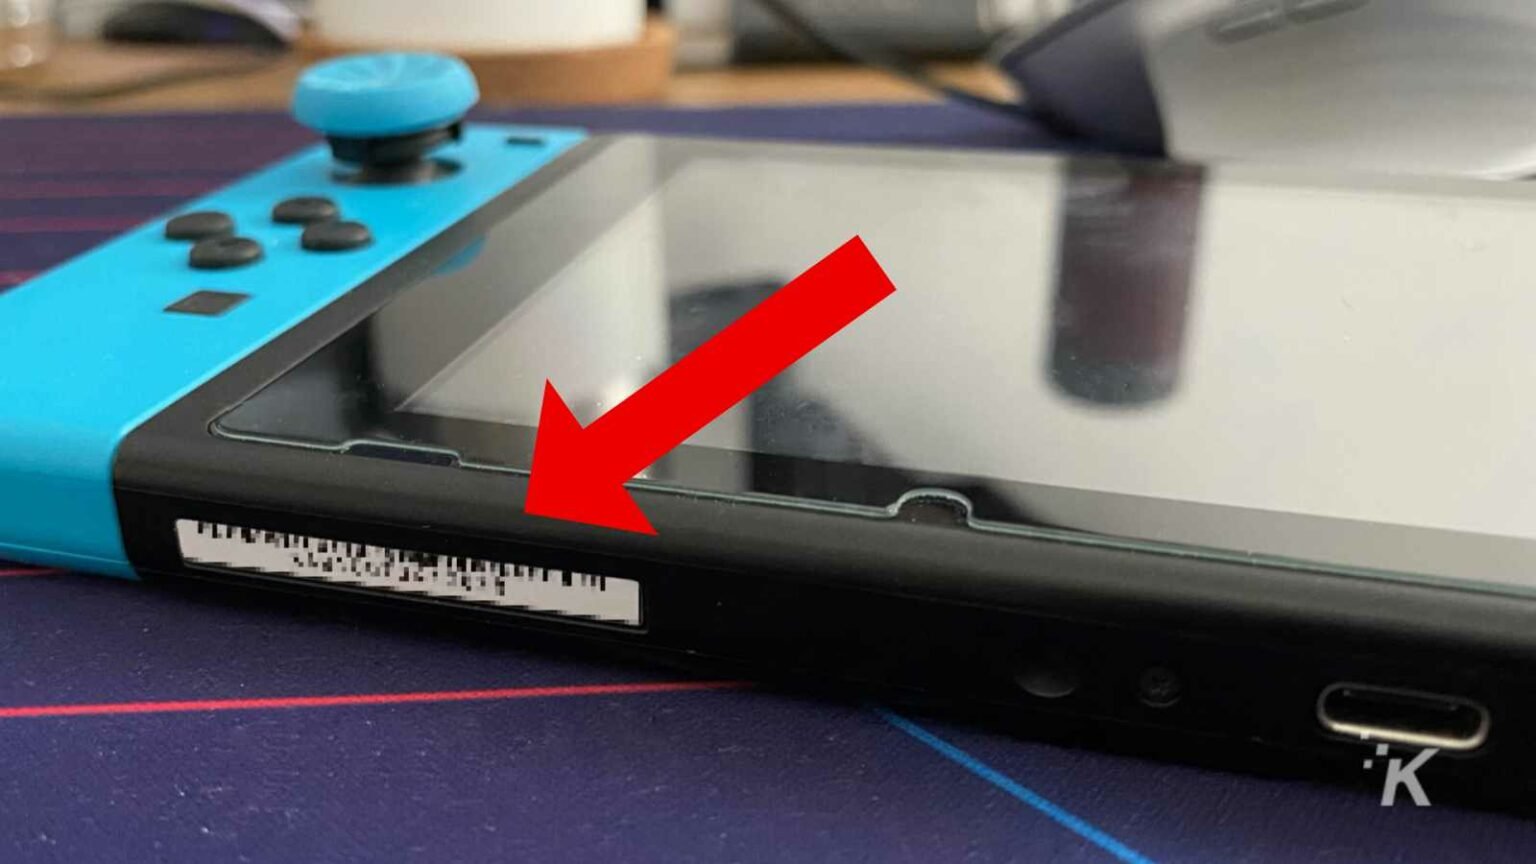
The Nintendo Switch has always had a serial number system that determines which hardware revisions you're holding. Early batches were V1, later ones were V2, and then Nintendo quietly shifted to newer production runs where the security architecture changed entirely. If you see a console listed as "hackable," it almost always comes down to whether the serial number falls into a range that used the older unpatched BootROM. Everything else is patched hardware that won't accept custom firmware through the same methods. I spent about three months verifying serial ranges across dozens of listings before I was confident enough to stop second-guessing my own work. The short version: any Switch with a serial number starting with XFK, XEW, XAW, or XWV before roughly mid-2018 is generally considered exploit-capable via the Fusee Geared payload. After that window, Nintendo updated the hardware and the serial number prefixes shifted to XTW, XTU, XTS, and beyond. Those newer units have the patched BootROM and no official homebrew path exists for them yet.
Unsafe To Play The Hackable Nintendo Switch Serial Number Security Risk
This is where people get themselves in trouble. A lot of the chatter online treats "hackable" and "safe to play" as the same thing. They aren't. Running custom firmware on a Switch means you are bypassing Nintendo's signature checks, which opens the door to several concrete risks. If you install a spoofed serial number through Homebrew Channel or similar tools, Nintendo's servers will flag the mismatch between what your console reports and what their database has on file. That flag is how bans happen. It's not theoretical. I watched a friend get banned within two weeks of going online with a modded console because he didn't understand that cloud saves and automatic updates communicate your serial directly to Nintendo. The real security risk isn't just the ban. It's what happens when you don't know what you're running. A compromised or tampered boot9strap installation can brick your console if the NAND backup isn't clean. I bricked a Switch once because I flashed a slightly outdated version of hekate onto a console that needed a newer payload sequence. Took about twenty minutes and a USB loader cable to recover it, but it was a painful lesson. Always keep a full NAND backup before touching anything. Not a system save backup. A full NAND dump. That's the difference between a minor inconvenience and a paperweight. Another thing nobody warns you about: battery degradation. Running custom firmware doesn't inherently damage the battery, but certain homebrew apps and emulation setups push the CPU much harder than the stock firmware ever intended. I've seen units where the battery capacity dropped noticeably after six months of heavy emulator use. The stock thermal management on the Switch is already mediocre, and custom firmware doesn't improve it. If you plan to run a lot of emulated games, expect higher temperatures and faster wear on the cell.
For people actually looking to mod their console, here's the practical path. First, verify your serial number against a current rangemap. Don't trust a single source. Cross-reference at least two. Second, set up a proper RCM jailbreak using a USB-C cable and a paperclip or RCM dongle. Third, inject the payload using something like TegraRcmGUI or Atmosphere's provided tools. Fourth, install boot9strap and hekate. Fifth, create your NAND backup immediately. Do not skip this step. Sixth, configure SysNAND and EmuNAND separately so your online profile never touches the modded environment. EmuNAND is probably the single most important safeguard. It's a full copy of your system firmware running off the micro SD card. You play modded games there, you install homebrew, you mess around. Your real System NAND stays untouched. When you want to go online, you boot into SysNAND and play normally. This setup alone eliminates the vast majority of ban risk because Nintendo's anti-cheat signatures only scan your actual hardware serial on SysNAND, not the EmuNAND instance. I've been running this configuration for over a year across two different consoles and haven't had a single flag. Your mileage may vary depending on how careful you are with what you install and whether you ever cross the two environments. There's a catch with EmuNAND that almost no beginner guide mentions. If you're using an older UHS-I microSD card, EmuNAND performance will be noticeably worse than SysNAND. Load times stretch out, texture pop-in becomes apparent, and some games simply refuse to launch properly. I switched to a UHS-II card and the difference was immediate. Games that were stuttering on the old card ran cleanly on the new one. It costs more, but it's not optional if you're planning to use EmuNAND seriously.
Get the Full Details
If your serial number doesn't fall into the hackable range, your options are extremely limited. Some people on forums claim exploits exist for newer hardware, but those are either unverified, require hardware modifications like chip soldering, or don't work reliably in practice. Don't waste money on guides that promise otherwise. The hardware signature checks on V2 and newer units are well-tested and Nintendo has had years to patch every software angle. The only consistent path for newer consoles involves hardware mods, and that voids your warranty, requires steady hands, and still doesn't guarantee functionality. Here's what I'd tell someone approaching this for the first time. Understand exactly what you're modifying before you start. Keep backups of everything. Separate your online and offline play environments. Use a quality microSD card. And accept that Nintendo can and will ban consoles they detect running unsigned code. There's no magic workaround for that part. The ban risk is real, it's documented, and it's been happening since 2019. Plan accordingly.