Unraveling The Mystery Of Duplicate Ip Addresses How Advanced Ip Scanners Resolve Issues
Samantha
2026-06-14
When Two Devices Claim The Same Address
Duplicate IP addresses show up more often than most network admins want to admit. One machine grabs a static address that someone else already assigned by accident. Or a DHCP pool runs out of scope and hands out the same lease to two hosts at once. The result is intermittent connectivity, dropped sessions, and hours of confusion that could have been avoided with proper scanning.
The core issue is simple. When two devices on the same broadcast domain respond to ARP requests with the same IP, traffic flips between them unpredictably. Your workstation might reach the gateway one second and lose it the next. Printers stop responding. VPN tunnels drop. The symptoms look like hardware failure, but the root cause is purely address collision.
Unraveling The Mystery Of Duplicate Ip Addresses How Advanced Ip Scanners Resolve Issues
Advanced IP scanners go beyond basic pings. A standard ping sweep only tells you what is alive. It does not resolve conflicts. A proper duplicate IP scanner probes the network with ARP grants, ICMP echo requests, and sometimes WMI queries against Windows endpoints. It builds a table of IP-to-MAC mappings and cross-references them against the DHCP lease database when one is available. The moment it sees two MAC addresses sharing the same IP, it flags the collision and logs the timing.
In practice, these tools work by sending targeted probes to suspected conflicting addresses. They capture the ARP reply and compare the source MAC. If the MAC changes between probe rounds, the scanner knows something is wrong. Some scanners also send gratuitous ARPs to force the network to refresh its address cache, which can temporarily restore connectivity while you hunt down the real culprit.
I learned this the hard way during a server migration at a client site. We moved three file servers from one VLAN to another, and within hours half the department lost access to shared drives. The error messages were vague. "Network path not found." "Cannot contact server." I spent forty minutes checking switch port configs, verifying VLAN assignments, and blaming the DNS server. None of it was the problem. The actual issue was a leftover static IP on a network printer that matched the new server's address. The printer and server were both answering ARP requests for the same IP, and the switch's CAM table was flipping between them. A dedicated IP scanner with ARP conflict detection would have caught this in under five minutes. I ended up using a command-line script that sent repeated ARP requests to the suspected IP and logged the source MACs over sixty seconds. When the MAC addresses swapped back and forth, I knew exactly where to look. I found the printer, changed its address, and the network stabilized.
How Scanners Detect Conflicts Step By Step
Most enterprise-grade scanners follow a similar detection pattern. They start by building a baseline. The tool maps the entire subnet and records every IP-MAC pairing it discovers. This baseline becomes the reference point for future checks. If an address suddenly appears with a different MAC, the scanner raises a flag.
The second phase involves active probing. The scanner sends ARP requests specifically targeting suspected duplicate IPs. It listens for responses and records the source hardware address. If two different MAC addresses respond to the same IP within a short window, the tool marks a conflict. Some scanners also send DHCP INFORM requests to check whether the address was legitimately leased or statically assigned.
Timing matters during this process. A single ARP exchange is not enough to confirm a duplicate because ARP caches can be stale. Modern scanners send multiple probe cycles over ten to thirty seconds. They compare results across cycles and only report a conflict when the inconsistency is sustained. This reduces false positives caused by transient network conditions or cached entries.
Common Pitfalls That Make Detection Harder
Network segmentation hides duplicate IPs. If the conflicting devices are on different VLANs or behind a router, a scanner on one segment will never see the collision. The conflict only manifests at the router level or in routing tables. In those cases you need to scan the upstream gateway or use span port mirroring to capture traffic from both segments simultaneously.
MAC address randomization on modern devices also complicates detection. Laptops and phones that use randomized private WiFi addresses will show different MACs over time even when they are the same device. A scanner that does not account for this behavior may flag legitimate devices as duplicates. The workaround is to correlate by IP lease timing and DHCP transaction logs rather than relying on MAC comparison alone.
Static DHCP reservations create another layer of confusion. When an administrator assigns a static lease in DHCP but the device also has a manual static IP configured, the DHCP server and the device itself are both claiming the same address. Some scanners miss this because they only compare ARP responses. A thorough scan includes DHCP lease table analysis to identify cases where the server believes it leased an address and the device believes it owns it statically.
What To Do When You Find A Duplicate
Immediate mitigation usually involves isolating the conflicting device. If the duplicate is a rogue access point or unauthorized host, disconnect it from the network physically or through a switch port shutdown. If it is a legitimate device with a misconfigured IP, change its addressing scheme to remove the conflict. Document the original MAC addresses and timestamps so you can verify the resolution later.
Long-term fixes require structural changes. Review your DHCP scope sizes. Undersized pools are the most common cause of dynamic duplicate IPs because the server exhausts available leases and starts reusing addresses before older ones expire. Expand the scope or implement DHCP snooping on managed switches to prevent unauthorized DHCP servers from handing out conflicting leases.
For environments that rely heavily on static addressing, maintain a centralized IP address management system. Spreadsheet tracking works for small networks but breaks down quickly. Dedicated IPAM tools enforce allocation policies, track assignments across subnets, and warn you before you assign an address that is already in use.
Tool Selection Considerations
Not all IP scanners handle duplicates equally. Free tools like Angry IP Scanner and advanced IP scanner offer basic sweep functionality but lack built-in conflict detection. They will show you active hosts but will not tell you when two hosts share an address. For that you need tools with ARP monitoring capabilities, such as Nmap with custom scripts, SolarWinds IP Address Manager, or PRTG Network Monitor.
Nmap remains the most flexible option if you are comfortable with the command line. The script nmap --script arp-scan --system-dns combined with a timed repeat can reveal conflicts without expensive licensing. A typical scan of a /24 subnet takes about three to five minutes and produces a CSV export you can filter for duplicate MAC patterns. Enterprise tools add scheduling, historical logging, and integration with ticketing systems, which matters when you need audit trails for compliance.
Limitations You Should Know About
Scanners cannot resolve everything. If the duplicate IP exists on a different subnet separated by a layer 3 boundary, a local scan will never see it. You must examine the router's ARP table or configure span ports to mirror traffic across segments. Some WAN and SD-WAN implementations also hide true source MACs behind NAT or overlay tunnels, making MAC-based conflict detection unreliable in those environments.
Firewall rules and ACLs can block scanner probes entirely. If your network enforces strict inbound filtering, ICMP and ARP requests from the scanner may be dropped before they reach the target device. The scanner then reports the host as offline when it is actually present and conflicting. In those cases you need to adjust scan permissions or use alternative detection methods like DHCP lease log analysis.
The biggest limitation is human error after detection. Finding a duplicate IP is only useful if someone actually fixes the root cause. In many organizations the scanner flags the conflict, the alert goes to a team that is already overwhelmed, and the issue sits unresolved until it causes a major outage. Automation through network access control systems that quarantine conflicting devices is one way to close that gap without adding headcount.
Building A Repeatable Detection Routine
Set up scheduled scans rather than reacting to complaints. A daily scan of each subnet takes roughly fifteen minutes for a /24 and can be automated to run overnight. Configure the scanner to email or webhook alerts when duplicates appear. Integrate the results with your existing monitoring stack so that duplicate IP events sit alongside other network incidents in a single view.
Keep historical logs of all detected conflicts. Patterns emerge over time. You might notice that certain VLANs consistently produce duplicates due to misconfigured scopes, or that specific switch models have firmware bugs that cause CAM table entries to flip incorrectly. That kind of institutional knowledge prevents the same problem from recurring indefinitely.
Network documentation should be updated immediately after each resolution. Record the conflicting IP, both MAC addresses, the device types involved, and the corrective action taken. This creates a reference that makes future investigations faster. When the same IP collides again six months later, you can check the log and know exactly what went wrong last time instead of starting from scratch.
Gallery Unraveling The Mystery Of Duplicate Ip Addresses How Advanced Ip Scanners Resolve Issues
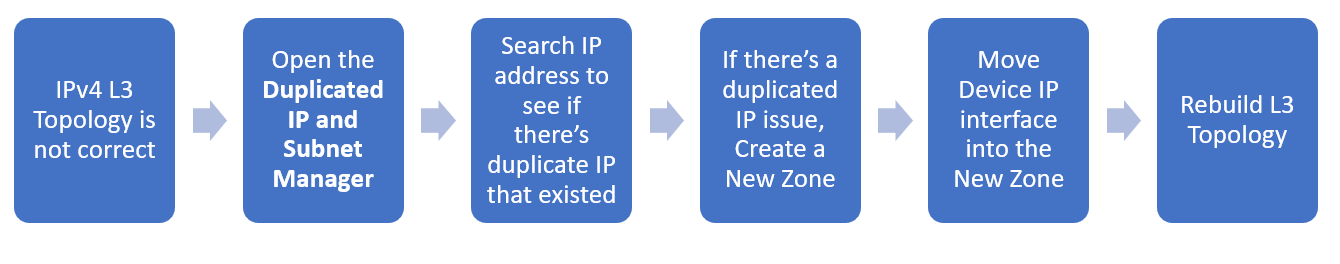
Resolve Duplicated IP Issues
lan - Why does the Advanced IP Scanner return more IP addresses than ...
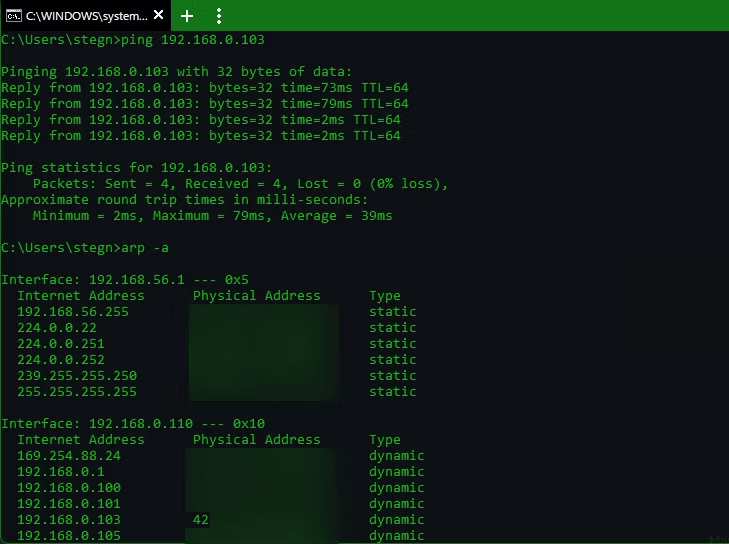
Duplicate IP Addresses - YouTube
Resolving IP Address Conflicts: Fixing Duplicate IP Issues - Life ...
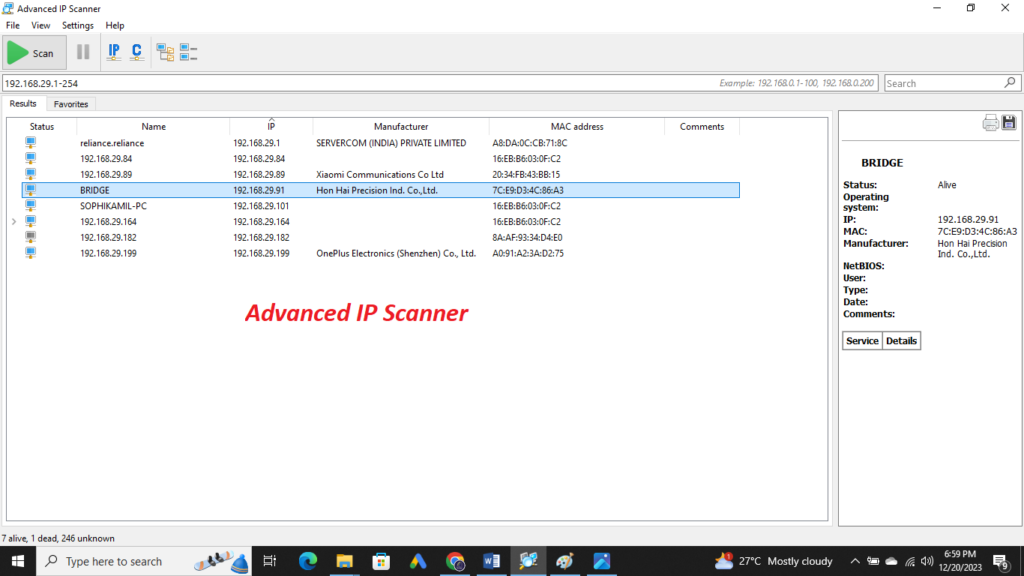
Advanced IP Scanner,A Powerful Network Management Tool - BRIDGE