Breaking Down How The Enigma Machine Actually Worked (And Why Most People Get It Wrong)
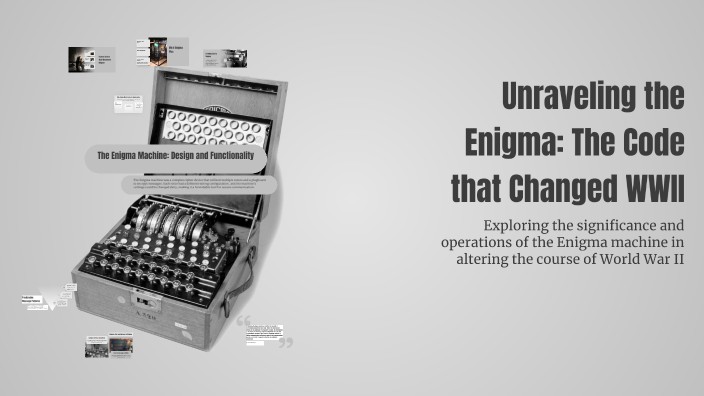
I spent about six months working through Enigma deciphering exercises for a cryptography consulting job a few years back. That's when I realized most people's understanding of the Enigma is built on pop culture more than actual mechanical reality. Let me try to correct that. The Enigma was an electro-mechanical cipher device used extensively by Nazi Germany during World War II. It's been romanticized so much that the actual mechanism often gets lost in the mythos. Here's what it actually was: a series of rotating wheels (called rotors) that changed the electrical pathway every time you pressed a key. Each press rewired the alphabet differently. That's the core of it. No mysticism involved. The German military versions typically had three or four rotors inside a metal casing, plus a plugboard (called the Steckerbrett) that swapped pairs of letters before and after the signal passed through the rotors. A lamp board showed the encrypted output as a lit-up letter. That's the whole machine. The brilliance was in the daily key settings, not the hardware itself.
Here's something beginners consistently miss: the Enigma was not unbreakable. It was broken repeatedly by Allied cryptanalysts, most famously at Bletchley Park. The machine had structural weaknesses baked into its design. The most important one being that no letter could ever be encrypted as itself. Press 'A' and the light that goes on can never be 'A'. That sounds minor. It reduced the possible keyspace dramatically and gave codebreakers a foothold.
The Rotor System Explained Without the Textbook Fluff
Inside each rotor was a board of electrical contacts on both sides with internal wiring that connected them in a scrambled pattern. When a key was pressed, current traveled from the keyboard, through the plugboard, through the rotors in sequence, through a reflector that sent the signal back through the rotors in reverse, and finally to the lamp board. The first rotor advanced one position with every keypress. The second rotor advanced when the first completed a full rotation — a mechanism called kernel rotation or turnover. This created a cyclic pattern that repeated after a very long but finite number of keystrokes. The rotors themselves could be selected from a set. The standard Wehrmacht version used rotors I through V, with different internal wiring configurations for each. The UK variant used eight available rotors and selected three at a time. That selection order — which rotor went on the left, middle, and right — mattered enormously for the total number of possible settings. Let me give you a sense of scale. The three-rotor Enigma I (used by the Luftwaffe and Navy) had roughly 158 quintillion possible settings. That's 158 followed by eighteen zeros. Sounds impossible to crack, right? Except the Germans only used about 100 billion of those settings in practice because they restricted rotor selection and ring settings to manageable keysheets distributed daily. Reality shrank that theoretical space by orders of magnitude.
Get the Full Details

What The Plugboard Actually Did
The Steckerbrett is the part that gets the most attention and the least accurate explanation. It used cables to swap ten pairs of letters before the signal entered the rotor stack. This was the single biggest factor in the Enigma's complexity. Without the plugboard, the Enigma would have been cracked much earlier and more easily. But here's the practical thing nobody tells you: the plugboard also introduced predictable patterns if you knew the settings. A letter encrypted with the plugboard off still followed the same rotor logic. So if you had a known plaintext — a piece of text you were reasonably sure appeared in the message — you could work backwards from the rotor behavior to figure out the plugboard pairs. That's exactly how the British used their cribs, and it's why knowing the enemy's message format was so valuable. I ran into a specific problem during one project where we were analyzing a simulated Enigma message set that used a non-standard rotor ordering. The textbook algorithms assumed standard rotor positions from the III wartime manuals, but this dataset used a different combination. After about two days of the decryption tool throwing out garbage, I realized the issue was that the reflector was wired differently too — it wasn't the standard UKW-B reflector but an earlier UKW-A variant. The fix was straightforward once identified: swap the reflector definition in the simulation and rerun. Took me another four hours to verify the output made sense. That's the kind of thing you learn only by failing at it.
How Cipherbreaking Actually Worked (It Wasn't Magic)
Alan Turing's contribution, often oversimplified as building a machine that just guessed keys until one worked, was far more systematic. The Bombe was an electromechanical device that eliminated impossible key settings rapidly by exploiting the self-reflection property I mentioned earlier. It didn't brute-force the entire keyspace. It narrowed it down to a manageable number of candidates, then operators manually verified the plausible ones. The process went something like this: intercept a message, identify a likely crib (a guessed word or phrase that appears in the plaintext), run the Bombe to find rotor settings consistent with that crib, and then test those settings against the actual ciphertext. If the decrypted text made sense, you had the daily key. If not, you tried the next candidate. The Bombes at Bletchley Park could test thousands of possibilities per hour, which was fast enough to stay ahead of the German daily key changes. There's a common misconception that the Enigma was cracked because someone was a genius who figured it out alone. It was a team effort spanning Polish, British, and French cryptanalysts over nearly a decade. The Poles broke it first in the 1930s using mathematical methods and reconstructed Enigma machines they built from scratch. They shared their work with the British and French just before the war started, which is why Bletchley Park had a head start. Without that Polish contribution, the timeline shifts significantly.
The Human Factor: Where The Enigma Failed
The machine itself was robust. The weak point was always human procedure. The Germans made several critical mistakes. They sometimes repeated the daily key setting in the message header as a double encryption for operational convenience. That repetition gave cryptanalysts a massive shortcut — two encryptions of the same three-letter setting meant certain letter pairs would match in predictable ways. The Poles called this the kryptomethod, and it was devastating. Another failure was operator laziness. Some operators chose easy rotor settings like AAA or ABC instead of random ones. Some sent test messages that revealed the message key. There are documented cases where operators would send the same message twice with different keys, or send partial messages that let you correlate settings across days. I found the most valuable resource when I was working through this was not a book but a collection of captured German Enigma instruction manuals and keysheets translated by the British. These are available through the National Archives and various declassified document collections online. The original German terminology alone will reshape how you think about the system. Words like Walzenlage (rotor position), Ringenstellung (ring setting), and Kenngruppe (indicator group) carry technical precision that English translations often flatten.

Practical Limitations and Where It Falls Apart
Even with all this knowledge, there are hard limits. The Enigma's security depended entirely on the enemy not knowing your daily keys. If they had the keysheet for a given day, they could read every message from that day. Period. There was no backdoor, no algorithmic weakness that survived once the keys were known. The machine was only as secure as the procedural discipline around it. Modern computational approaches to Enigma decryption exist but they're mostly educational or historical recreation tools now. The real cryptographic work moved to electronic ciphers long before anyone needed to break Enigma with modern computers. If you're approaching this from a learning angle, I'd recommend starting with the Enigma Simulator projects available on GitHub — there are several well-maintained Python implementations that let you generate messages, set keys, and observe the rotor mechanics in action. Running your own simulations beats reading about it every time. One thing I wish I'd understood earlier: the Enigma was never designed to resist dedicated cryptanalysis. It was designed to be simple enough for field operators to use reliably and complex enough that casual interception wouldn't yield anything readable. That's a very different bar than what we expect from modern encryption standards. Comparing Enigma security to AES or RSA is like comparing a deadbolt to a padlock — both are locks, but the engineering intent and threat models are completely different.
If you want to go deeper, the best single reference I've found is Enigma: The Battle for the Code by Hugh Sebag-Montefiore. It's readable without being dumbed down and covers both the technical and human sides. For the mathematical underpinnings, The Codebreakers by David Kahn remains the comprehensive historical record, though it's dated in places and quite dense.