Why The OSI Model Still Matters Even Though Nobody Talks About It Anymore
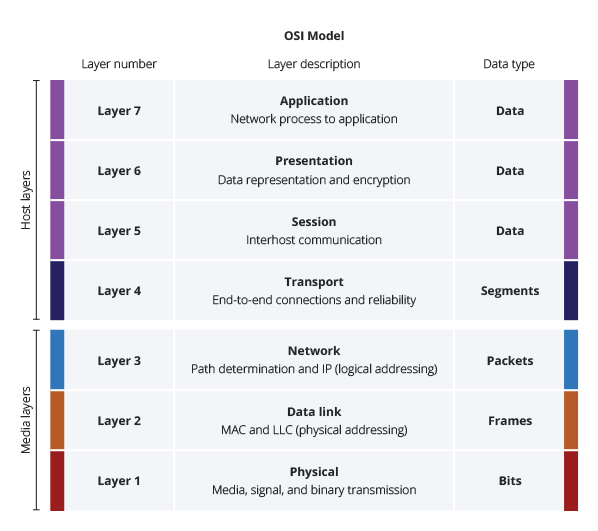
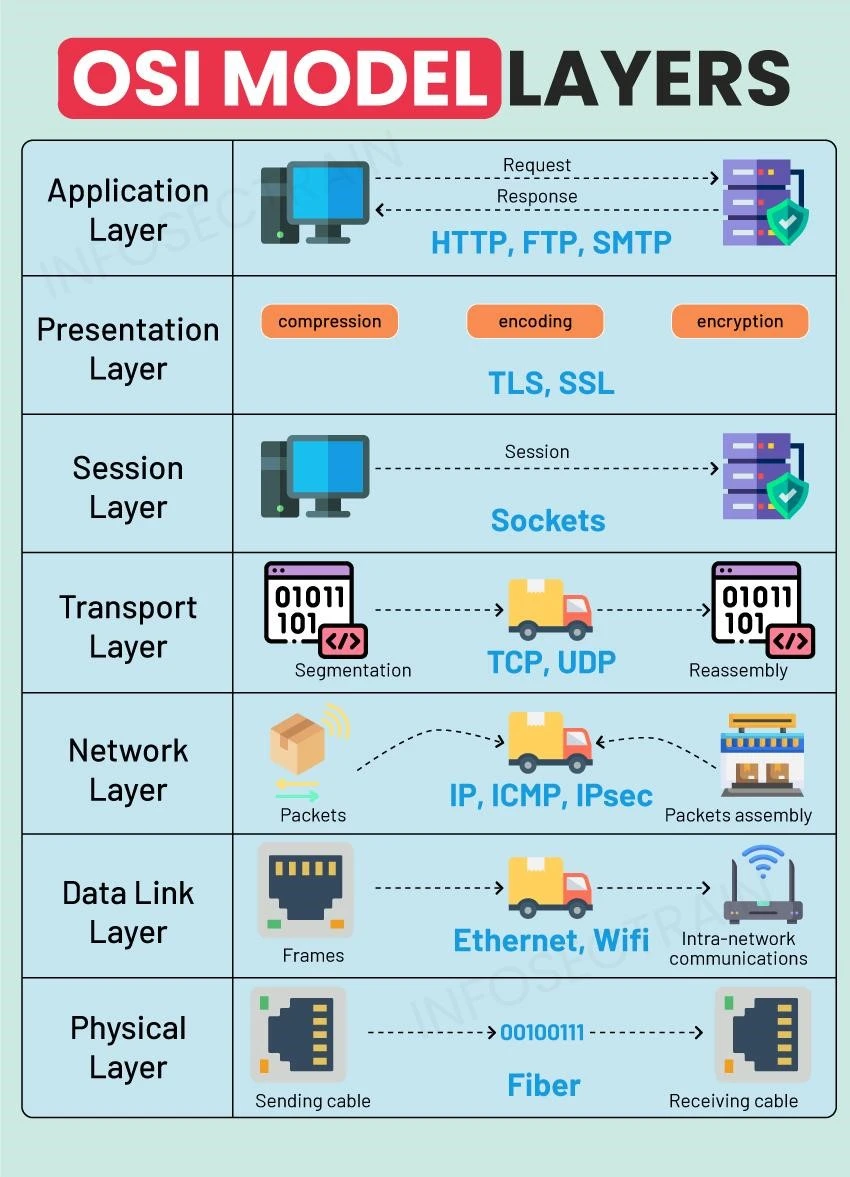
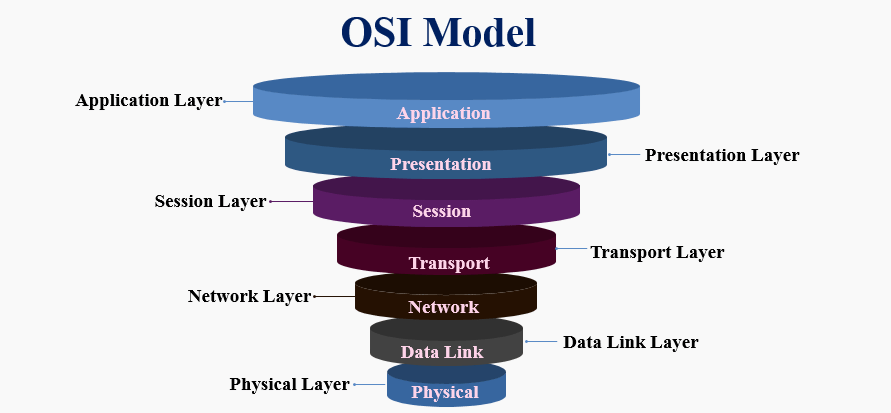
I've been troubleshooting network issues for long enough to remember when people actually used the OSI model as a practical framework instead of a textbook exercise. The reality is that most networking equipment behaves in ways that don't map cleanly to any single layer, and that mismatch is where things go wrong. I spent three days once tracking down a multicast routing problem that turned out to be a Layer 2 switch doing transparent bridging on a VLAN where the router expected to see pure Layer 3 traffic. The OSI model didn't help me directly, but understanding where the layers blur did. Let's skip the standard seven-layer definition recitation. You can find that anywhere. Here's what actually matters in practice. Layer 1 (Physical) is where most people's problems start and end without them realizing it. Fiber modal strippers, bad SFPs, and CRC errors on Gigabit Ethernet ports account for a massive percentage of intermittent failures. I once replaced forty feet of Cat6a cable and the "mysterious latency spikes" vanished. The cable had a crushed pair. Not dramatic. Just happens constantly.
Layer 2 (Data Link) introduces MAC addresses, VLANs, and spanning tree. This is where switches live. The thing nobody warns you about is that modern switches are increasingly blurring the line between L2 and L3. A typical enterprise access switch will do VLAN tagging and spanning tree while also routing between those VLANs if you enable IP routing on it. That means the same physical box is making decisions at two layers simultaneously, and troubleshooting requires you to know which one it's using at any given moment. Layer 3 (Network) is routers and Layer 3 switches. IP addressing, routing protocols, ACLs. The critical insight here is that routers don't care about your MAC addresses at all. They care about routes. I've seen engineers spend hours debugging what they thought was a routing issue only to discover the problem was actually an ARP table that had stale entries because of an incorrect VLAN configuration upstream. The symptom looked like L3. The cause was L2. Layers 4 through 7 get increasingly application-specific. Load balancers operate at L4 and L7. Firewalls now do deep packet inspection that spans multiple layers. Proxy servers, VPN concentrators, WAFs — none of these fit neatly into one layer anymore. A next-generation firewall might inspect Layer 3 headers for IP addresses, Layer 4 for port numbers, and Layer 7 for application signatures, all in the same pass. Treating these devices as belonging to a single OSI layer will get you confused fast.
How To Actually Use This When Something Breaks
The OSI model is useful primarily as a diagnostic framework, not as a description of how devices work. When something is broken, the question isn't "which layer is this device?" It's "at which layer does this symptom manifest, and what could be failing above or below it?" Take a simple connectivity problem. Host A can't reach Host B. Start at Layer 1: is the link up? Check interface counters. Is there carrier? Are there CRC errors? Move to Layer 2: can Host A resolve Host B's MAC address via ARP? Is the traffic hitting the right VLAN? Check the switch MAC address table. Layer 3: is there a route? Check the routing table. Can the gateway respond to pings? Each layer has its own verification method. Jumping straight to "check the route" when the cable is unplugged wastes time. Here's a scenario I dealt with last year that illustrates why layer-by-layer thinking matters. A client reported that certain applications worked while others didn't, all from the same host. The network looked fine at L1 and L2. At L3, the routing was correct. But the applications were hitting different destination ports, and the firewall was doing deep packet inspection on one set of ports but not the other due to an inconsistent rule ordering. The issue was real but lived at the boundary between L4 and L7. If I'd stopped checking at L3, I would have spent days looking for routing problems that didn't exist.
Get the Full Details
Common Misconceptions That Cost Time
One major misconception is that OSI layers are strict boundaries. They aren't. VLAN hopping attacks, for example, exploit the interaction between L2 and L3. MACsec encrypts at L2 but the key management happens at higher layers. SDN controllers manage L2 and L3 state through APIs that operate at L5 and above. The model is a framework for thinking, not a description of hardware implementation. Another misconception is that you need to understand all seven layers to troubleshoot networking. You don't. Most enterprise network problems live at L1, L2, and L3. Application-layer issues are usually application problems, not network problems. I've seen too many engineers spend time investigating TLS handshake failures as if they were network issues when the actual problem was a certificate expiration or an application misconfiguration. Know where to stop. The real limitation of the OSI model is that it doesn't account for modern virtualization well. Virtual switches, overlays like VXLAN, and container networking all blend layers in ways the original model didn't anticipate. VXLAN encapsulates Layer 2 frames inside Layer 3 UDP packets, which means you're doing L2 over L3 over L2. The OSI model can describe this if you're careful, but it gets awkward. In practice, I think in terms of encapsulation stacks rather than strict layer assignments when dealing with overlay networks.
What Actually Happens When Packets Move Through Devices
When a frame arrives at a switch, the hardware examines the destination MAC address and forwards it out the appropriate port based on the CAM table. That's Layer 2. If that frame is destined for the switch's own IP interface and the switch is configured for routing, it then looks at the IP header and makes a Layer 3 forwarding decision. The same silicon is doing both. This is why you'll sometimes see a Layer 2 flood on a VLAN and then the same traffic get routed correctly by the same device — there's no hard separation in the data path. Routers work differently. They strip the Layer 2 header, examine the Layer 3 destination, make a routing decision, and re-encapsulate with a new Layer 2 header for the next hop. This is why routers separate broadcast domains. Switches forward based on MAC addresses within a broadcast domain unless they're doing inter-VLAN routing, in which case they also strip and re-encapsulate but at the VLAN interface level rather than the physical interface level. The practical takeaway is that understanding what header information each device type reads and modifies lets you predict where problems will appear. A Layer 2 switch won't touch IP addresses. A router won't forward based on MAC addresses. A Layer 3 switch does both but in sequence, not in parallel for a single packet. Getting this sequencing wrong in your mental model is a common source of confusion when reading packet captures.
A Real Workaround I Use Regularly
When I'm dealing with a situation where the layer boundary is unclear — say, a problem that could be L2 or L3 — I use a combination of packet captures and targeted interface statistics rather than guessing. I'll grab a capture on both the source and destination sides, then use Wireshark's I/O filters to isolate traffic by protocol and examine the exact headers at each hop. This usually takes about ten minutes and resolves questions that would otherwise require a day of trial-and-error configuration changes. For the VXLAN overlay issue I mentioned earlier, the workaround was straightforward once I stopped trying to force it into OSI layer boxes. I verified the underlay IP connectivity first — that's pure L3. Then I checked the VTEP advertising and the BUM traffic handling — that's L2 over L3. Then I confirmed the guest VM's MAC was reachable across the overlay. The problem turned out to be a mismatched VXLAN Network Identifier between two segments. The OSI model didn't tell me that. Being methodical about what to verify at each encapsulation level did. The OSI model is a useful reference framework, but treating it as a literal description of how networks operate will limit your troubleshooting. The layers are analytical tools, not hardware constraints. Modern devices operate across them simultaneously, and the most common failures happen precisely at the boundaries where the model gets fuzzy.