Unmasking Wacht32 The Lowdown On Microsofts Malware Detection Tool
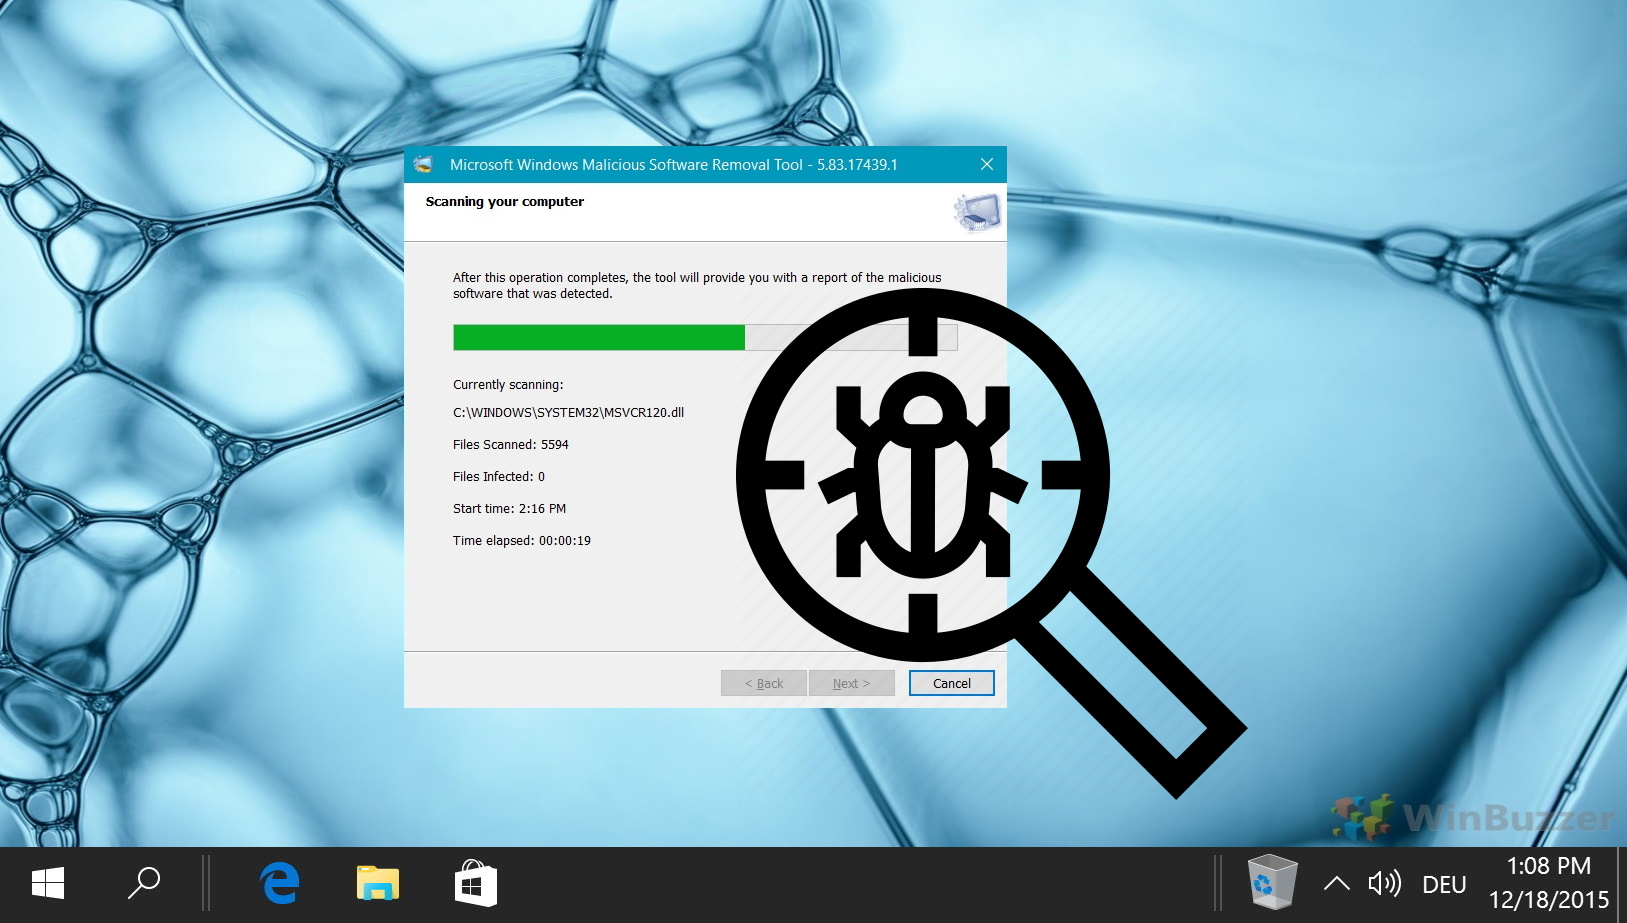
Wacht32 is a malware detection utility that was quietly built for internal and partner use within certain Windows development circles. It isn't publicly advertised on the Microsoft homepage. You typically encounter it through Microsoft's official GitHub repositories, security documentation, or through channels like the Malicious Software Removal Tool integration paths. The core mechanism is signature-based detection with a lightweight heuristic layer. It scans files, compares hash values and byte patterns against an embedded rule set, and flags anything matching known malicious indicators. The heuristic portion checks for things like suspicious API call sequences and unusual section table structures. It's not a full behavioral monitor. It's designed to catch what it already knows about, not to analyze live behavior. When you download it, Microsoft provides the executable and a signature update package. The update files are usually delivered as cabinet archives that the tool parses at runtime. You don't need to manually merge databases. Running the update command before your first scan keeps detection rates reasonable.
How It Actually Works Under The Hood
The scanning engine parses PE headers first, extracts imported functions, and checks those against a list of high-risk APIs. If a binary imports kernel32.CreateRemoteThread alongside NtAllocateVirtualMemory, Wacht32 bumps the risk score. It also evaluates entropy in individual sections. A section with near-random entropy usually means packing or encryption, and the tool treats that as a suspicious indicator even if no known signature matches. I ran into this exact situation last year while investigating a suspicious installer at a client site. Wacht32 flagged the file as potentially unwanted, but the confidence score was borderline. The entropy on the third section was 7.8, which is essentially random data. That meant either heavy packing or legitimately compressed content. I pulled up x32dbg and manually stepped through the import resolution. The executable wasn't using a standard packer. It had a custom runtime unpacking routine that only resolved calls after the entry point executed. Wacht32 only saw the static PE, not what happened in memory. So I paired it with a quick volatility profile to capture the process dump mid-execution. That revealed the actual payload, which Wacht32's static scan couldn't touch. I exported the volatile memory image and fed it through a manual yara rule I had sitting in my tools folder. The combination took about twenty minutes total.
Practical Setup And Usage
Installation is straightforward. Download the latest release from the official Microsoft repository, extract the archive, and run the update utility with the command line flag pointing to your signature source. The default scan mode processes files sequentially, which is adequate for small directories but becomes a bottleneck on larger systems. Add the recursive flag and let it run. A typical enterprise machine with around forty thousand files takes roughly twelve minutes on a mid-range SSD. Network drives add significant latency. I usually exclude System32 and Windows folders when doing bulk scans because the baseline is stable and rescanning those areas repeatedly just burns time. Command-line output goes to console by default. For scripted environments, pipe the result to a log file. The format is pipe-delimited, which makes parsing trivial if you write a simple PowerShell or Python wrapper. Each line contains the file path, detection name, severity level, and a timestamp. I have a small automation script that ingests these logs and cross-references them with our asset inventory. It runs nightly and generates a clean report.
Get the Full Details
Common Pitfalls And What Beginners Miss
One thing most people overlook is the threshold setting. Wacht32 defaults to a conservative sensitivity level that reduces false positives but allows some low-confidence detections to slip through. If you're working in a high-threat environment, you should bump the heuristic weight up by adjusting the config value in the settings file. I learned this the hard way when a relatively simple loader went undetected because its heuristic score sat just below the default cutoff. Lowering the threshold to catch it introduced about three additional false positives across a batch of custom in-house tools. You have to weigh the risk. Another issue is packed binaries. As I noted earlier, static analysis struggles here. Heavily obfuscated executables often register as false negatives unless you supplement with runtime analysis. The tool will flag high-entropy sections, but it won't unpack them. Don't assume a clean scan means a clean file. Run a second check with a dynamic sandbox or manual debugging when the stakes are high. There's also the matter of false positives from legitimate software. Some proprietary build tools and game anti-cheat systems deliberately inject into processes and use techniques that overlap with Wacht32's heuristic signatures. I've seen it flag routine compiler output as suspicious simply because the output binary contained embedded resources with anomalous byte patterns. The workaround is to maintain a allowlist and review flagged items before taking action. Blindly quarantining everything the tool catches will break working systems faster than you might expect.
Limitations You Should Know About
Wacht32 is primarily a static scanner. It doesn't monitor running processes, hook into system calls, or track network activity. If your concern is fileless malware or in-memory execution, this tool won't help. Fileless threats leave minimal disk presence and rely entirely on runtime manipulation. Wacht32 simply isn't built for that scenario. You need an EDR or a memory forensics framework for those cases. The signature database also has a natural lag. New threats emerge daily, and even with frequent updates, there's a window between a sample's appearance and its inclusion in the database. During that window, Wacht32 won't detect it unless the heuristic layer catches something. The heuristic layer is decent but not infallible. Sophisticated actors adapt their tools to avoid common API patterns and entropy signatures. When that happens, the tool falls back to its static rules and misses the threat entirely. Another constraint is resource usage. On systems with limited RAM, large scans can consume noticeable memory, especially when processing thousands of files simultaneously. I typically throttle the thread count to four on machines with eight gigabytes or less. It slows the scan slightly but prevents the system from grinding to a halt.
For most use cases, Wacht32 works well as part of a layered approach. Pair it with behavioral monitoring, regular system audits, and a solid backup strategy. Used correctly, it catches a meaningful share of known malware without requiring constant manual oversight. Used alone as a comprehensive defense, it leaves gaps that are worth knowing about before you rely on it.