Unmasking The Power Of Zoom Meeting Id Revolutionizing Remote Conferences And Beyond
Samantha
2026-05-25
What a Zoom Meeting ID Actually Is
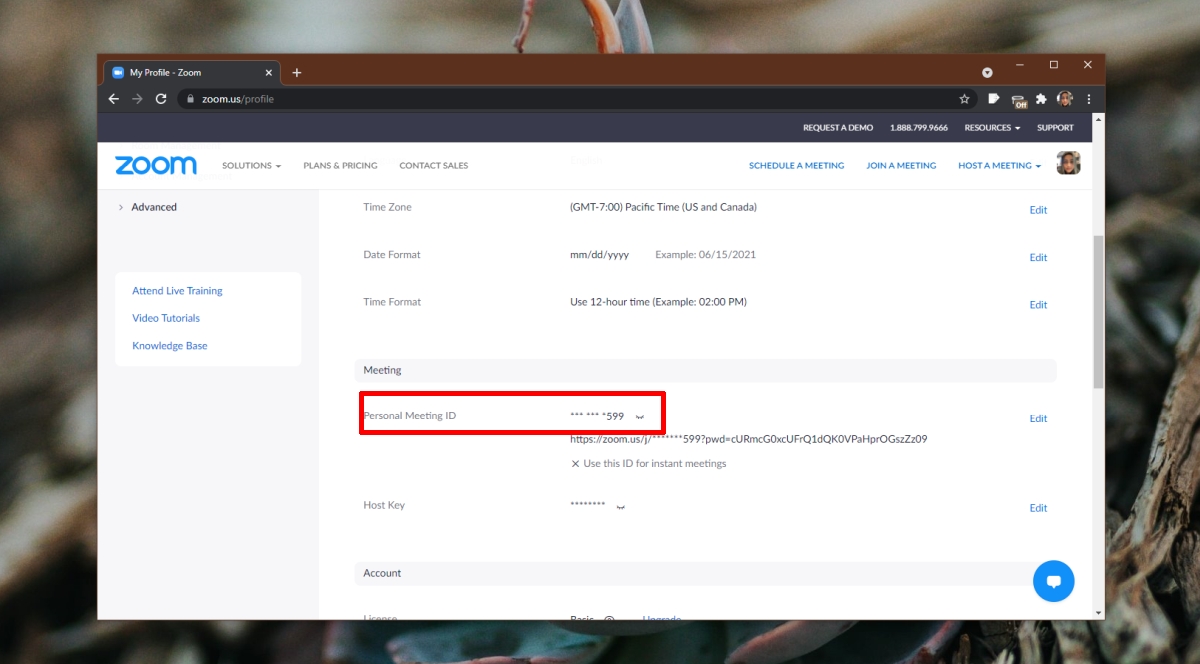
A Zoom Meeting ID is a nine-character alphanumeric string that identifies a scheduled meeting. When you create a recurring meeting, Zoom assigns one fixed ID and reuses it every occurrence. For instant meetings, each new session gets a fresh ID drawn from a pool. The format used to be ten numeric digits, then Zoom migrated to an eleven-character mix of letters and numbers. People still call it a "meeting ID" even though it functions more like a weak authentication token.
Unmasking The Power Of Zoom Meeting Id Revolutionizing Remote Conferences And Beyond
The real value of the Meeting ID isn't in the branding. It's in the fact that it removes the need for passwords in most setups. If your account has "Allow join before host" enabled and password protection disabled, anyone with the ID and your invite link can walk in. That's the feature most people underestimate until they're dealing with an unrushed classroom of sixty participants instead of twelve.
I ran into this firsthand during a departmental retreat last year. We had three back-to-back sessions, and the organizer reused the same Meeting ID across all of them without resetting the waiting room. By the second session, people from the first had the ID cached in their chat logs and drifted into the second room mid-presentation. The fix was straightforward but slow: I created new instances for each track with distinct IDs and manually removed the stragglers who'd already joined the wrong one. It took about eight minutes to sort out. After that, I switched every recurring meeting to use the default "Use personal meeting ID" setting instead, which forces a new ID per occurrence and breaks the replay attack surface entirely.
How to Work With Meeting IDs
Creating a new scheduled meeting with a unique ID takes thirty seconds. Open Zoom, click Schedule, leave the default ID field untouched so Zoom generates a fresh one, and save. The ID appears in the calendar invite and on the confirmation screen. If you want a custom ID, you can type one in, but there are constraints. The field only accepts letters and numbers. Special characters get rejected. You also can't reuse an ID that's already assigned to another active meeting on the same account, which creates friction when you're trying to match a legacy internal numbering scheme.
For recurring meetings, the choice matters more. Using a single Meeting ID means participants always join the same room, which is convenient but creates a permanent broadcast channel. Anyone who shares that ID externally keeps getting access to future sessions unless you change the meeting's password or rotate the ID. Using a unique ID per occurrence means every session is isolated, but participants need the updated link each time. In practice, I recommend unique IDs for anything with external attendees, and a single recurring ID only for internal team standups where the participant list never changes.
Common Misunderstandings
Meeting IDs are not passwords. They are easier to guess or intercept. A brute-force attack against a ten-digit numeric ID would take less time than most people realize, which is why the alphanumeric format exists. Even so, collision attacks are theoretically possible, especially across large organizations where multiple hosts generate IDs simultaneously. The probability of collision stays low for a single account but climbs when you factor in millions of daily meetings across the platform.
Another misconception is that enabling a meeting password neutralizes the ID. It doesn't. The password and the ID are two separate gates. Most people treat the ID as the only security layer because they disable passwords by habit. Removing the password from your settings doesn't make the ID weaker, but it does make the ID the sole gatekeeper, which is a fragile position.
Security-Adjacent Habits That Actually Help
I use three concrete practices that cut down the noise of unwanted joiners. First, I enable the waiting room on every meeting that isn't a private one-on-one. It adds roughly five seconds to the join process but stops ID guessing from succeeding. Second, I rotate Meeting IDs whenever I suspect one has been shared beyond the intended group. This happens more often than you'd think after a conference panel gets recorded and posted publicly. Third, I switch off "Allow participants to rename themselves" for large sessions, because it has nothing to do with the ID directly but reduces the overall attack surface when combined with a waiting room.
The tradeoff with these habits is friction. Waiting rooms create support tickets from impatient attendees. Rotating IDs forces you to resend calendar invites. Disabling self-renaming annoys people who genuinely want to use stage names. The math usually favors the friction, but it depends on your audience.
When Meeting IDs Fail You
There are scenarios where the Meeting ID approach collapses. If you're hosting a webinar with five thousand attendees, the ID alone can't manage capacity. You need a separate registration flow, an attendee list, and often a custom domain link. Meeting IDs don't scale past a few hundred participants without significant manual intervention.
Another failure mode is when your organization enforces SSO or requires authentication before entry. In that case, the Meeting ID becomes almost decorative, because the real gate is the identity provider. Relying on the ID in those environments gives a false sense of control. You still configure the permission rules correctly, but the ID isn't doing meaningful work.
Platform Changes That Matter
Zoom shifted from pure numeric IDs to alphanumeric ones around 2021. The migration wasn't automatic for existing recurring meetings. Some hosts still carry legacy numeric IDs that look wrong next to modern ones, and certain third-party dial-in systems break when they encounter letters in the field. If you're integrating Zoom with a legacy PBX or aVoIP gateway, test the ID format against that system before committing to a new schedule.
The platform also introduced enhanced encryption for paid accounts. With enhanced encryption enabled, the Meeting ID still routes the call, but the media path changes. Guests on older clients may fail to connect even with the correct ID. I learned this the hard way during a hybrid event where half the room joined via Zoom and the other half via a legacy video conferencing codec. The Meeting ID was fine, but the encryption flag silently blocked the legacy path. Downgrading to standard encryption for that specific meeting restored connectivity, though it reduced end-to-end security for everyone.
Gallery Unmasking The Power Of Zoom Meeting Id Revolutionizing Remote Conferences And Beyond
Beyond Zoom Fatigue: The Future of Technology in Remote Work ...
PPT - Webinar Wonders: Unleashing the Power of Zoom Meetings for ...
How to Join Zoom with Meeting ID + Alternatives
Zoom generate meeting id automatically - parpoi
Join a Zoom Meeting with ID & Password (2-Minute Guide) - YouTube