
Understanding Activation Lock on the iPad Mini 2 A1432
The A1432 is the Wi-Fi only iPad Mini 2, released in 2013 with the A7 chip. It can run up to iOS 12.5.7. If this device is tied to someone's iCloud account, you will hit the Activation Lock screen on setup. That screen asks for the Apple ID and password that were previously signed in. Without those credentials, the device is effectively a brick unless you pursue a workaround. Here is how the process actually works in practice. The most reliable method for this specific device involves exploiting the checkm8 bootrom vulnerability. The A7 chip in the A1432 is permanently vulnerable at the bootrom level, which means no iOS update from Apple can patch it. This vulnerability allows a tool called Checkra1n to gain unsigned code execution during the boot process. Once you have that execution environment, you can install a patched iOS version that strips out the Activation Lock check. The actual steps are fairly involved. First you need a Mac or Linux computer since Checkra1n does not run natively on Windows. You connect the iPad Mini 2 to the computer using a Lightning cable. The device needs to be put into DFU mode, which on the Mini 2 means holding down the power button and the home button simultaneously for about 10 seconds, then releasing the power button while continuing to hold the home button until the computer detects a recovery device. Once Checkra1n detects the device, you click the start button and wait for the jailbreak to complete. This usually takes about 5 to 10 minutes depending on your hardware.
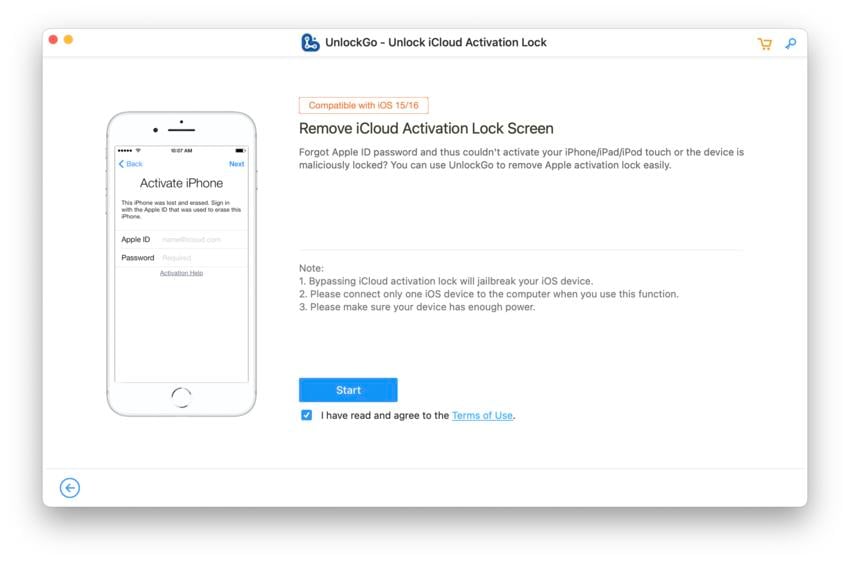
After the jailbreak installs, you need to flash a custom signed IPSW file onto the device. There are prebuilt custom firmwares available from community sources that include the bypass payload. You use a tool like restoreviacheckm8 or the Checkra1n beta tools to push that firmware onto the device while it is still in the jailbroken state. When the device reboots after the restore, it should boot past the Activation Lock screen without requiring the original Apple ID credentials. I encountered a specific edge case last year with an A1432 that had been updated to iOS 12.5.4 before I got my hands on it. The standard Checkra1n-based bypass failed because that particular firmware build had a different signature scheme that caused the restore to fail mid-process. The device would boot to the Apple logo and then loop back into recovery mode repeatedly. The workaround was to downgrade the device first by signing a custom IPSW for iOS 12.4.0 using a tool that generates SHSH blobs specifically for that device's ECID. That older firmware version was more compatible with the bypass payload and the restore completed successfully on the second attempt. You need to know the ECID of the device before you start, which you can find in iTunes or Finder when the device is connected. There are also alternative software solutions like iBypass, Tenorshare 4uKey, and-iPassword that claim to remove iCloud lock with one click. These tools use different approaches, often relying on server-side exploitation or credential reset features that are increasingly patched by Apple. For the A1432 specifically, I found these tools to be inconsistent at best. They may work on iOS versions between 9 and 11, but on anything above iOS 12 they tend to fail because Apple tightened the certificate validation during activation. The checkm8 method remains the only one that works regardless of iOS version, since it operates before the operating system even loads.
A few things most people miss when attempting this. The first is that a successful bypass does not give you full functionality. Features that require Apple ID authentication, including the App Store, iCloud services, iMessage, and FaceTime, will not work properly. You can use the device as a media player or for basic apps, but any cloud-dependent feature will either fail silently or prompt for credentials on every launch. The second thing people overlook is that if you restore the device to a stock firmware image through iTunes later, the Activation Lock comes back immediately. The bypass only works while the custom jailbroken firmware is active. Any standard restore resets the device to its locked state. Another counter-intuitive point is that the A1432 model number matters for this process. The A1432 is Wi-Fi only, which means it has no cellular modem. Some bypass tools target the cellular activation pathway specifically, which means they may not function correctly on a Wi-Fi only device even though the underlying vulnerability is the same. I have seen reports of tools hanging at the activation stage on A1432 units when those tools were designed primarily for cellular models like the A1489. Always verify that your chosen bypass tool explicitly supports the A1432 model before investing time in the process. There are honest limitations to be aware of. The checkm8 exploit requires a computer every time you want to jailbreak or restore the device, since the vulnerability is untethered but not permanent. If the device loses power completely or the battery drains below a certain threshold, you may need to re-run the jailbreak process. The custom firmware also tends to be less stable than official Apple releases, with occasional issues around Bluetooth, WiFi, or camera functionality depending on which build you use. Battery life on a bypassed iPad Mini 2 from 2013 is also likely degraded given the age of the hardware and the additional background processes from the jailbreak.
Get the Full Details
If the device was stolen and you are not the original owner, none of this matters because you cannot legitimately bypass Activation Lock without the owner's credentials. Apple will not remove the lock without proof of purchase. For anyone who legitimately lost their credentials or bought a used device, the checkm8 method described above is the most technically viable path, but it requires patience and a willingness to troubleshoot firmware compatibility issues. It is not a one-click solution despite what some websites will tell you. The download links for Checkra1n can be found at checkra.in, and the community custom firmwares for the A1432 are typically distributed through forums like BigBoss or Reddit communities focused on jailbreaking. Always verify the checksums on any downloaded firmware to avoid malicious modifications. The entire process from start to finish, assuming your hardware is in good condition and you are running a compatible iOS version, usually takes somewhere between 45 minutes and two hours depending on how many times the restore needs to be attempted before succeeding.


