Understanding UCSC Gold and Why Getting In Is More Complicated Than It Looks
UCSC Gold is the centralized authentication and data-access system used across the University of California, Santa Cruz genome research ecosystem. It gates access to the Genome Browser, BigData examples, downloadable datasets, and several API endpoints that researchers depend on daily. The login itself isn't the problem. The problem is understanding what tier of access you're actually applying for, why MFA sometimes fails silently, and what happens when your institutional SSO refuses to talk to UCSC's auth provider during off-peak hours. I've spent years supporting people who treat UCSC Gold like a simple username-and-password portal. It isn't. Here's how it actually works when things go wrong, not how the brochure says they should.
Unlocking Ucsc Gold Login A Comprehensive Guide To Access And Security
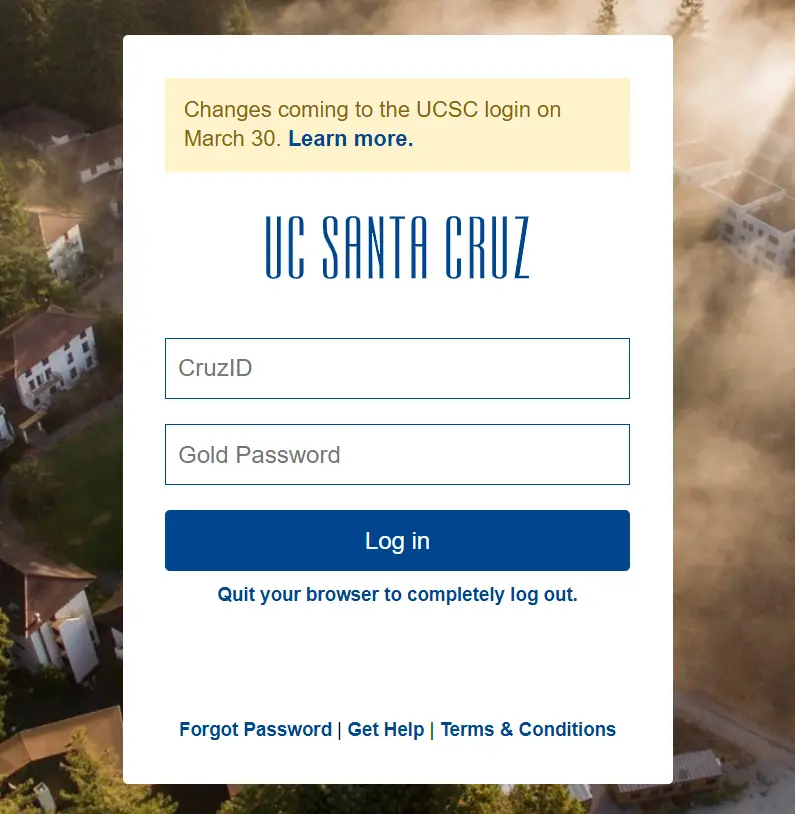
The Login Flow — What Actually Happens Behind the Screens
When you attempt to log into UCSC Gold, you're typically routed through a federated identity flow. If you're coming from within the UC system, that usually means an Okta-backed UCNet authentication handshake. If you're external — a collaborator at another university or an independent researcher — you're often directed to a Shibboleth or OAuth flow that validates credentials against your home institution's identity provider before UCSC Gold creates a session token. The session token has a limited lifetime. By default these are around 8 to 12 hours for most institutional accounts, though some restricted datasets enforce shorter windows. Once the token expires, you get a silent redirect to the login page. No warning. No prompt. Just a 302 back to authentication and your query state gets cleared if you weren't saving progress. One thing most people miss: the same login page serves multiple access tiers. A standard UCSC Gold credential lets you browse the Genome Browser and download public tracks. But accessing registered datasets, API keys, or bulk data downloads requires an approved research account with documented use-case justification. The system doesn't always make this distinction obvious on the initial login screen, which is why you'll occasionally hit an authorization error after a successful credential check. That error isn't a broken login. It's a permissions boundary you haven't crossed yet.
Setting Up Your Account — The Practical Steps
If you're new to this system, start by determining your institutional affiliation. UC students and staff use UCNet credentials. External researchers need their home institution's federated identity to be recognized by UCSC's Shibboleth service. If your university uses Azure AD or an IAM platform that doesn't speak SAML 2.0 out of the box, you're going to have a bad time unless your IT team can configure a standard SAML assertion. Once you've confirmed your identity path, go to the registration endpoint and submit the following: Institutional email address — personal Gmail or Yahoo addresses are rejected outright. The system validates the domain against known academic and research institution lists.
Get the Full Details
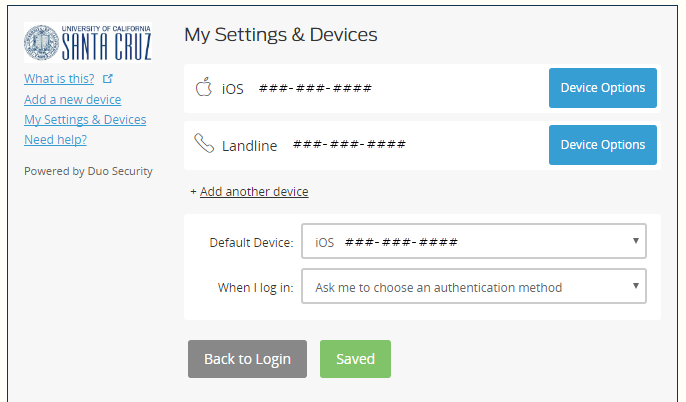
Research purpose statement — this isn't boilerplate. Writing "I need access for research" will slow your application down. Be specific: which dataset, what genome build, what analysis pipeline, what timeline. Applications with concrete details tend to process faster because the review team can verify legitimacy without emailing back for clarification. MFA enrollment — UCSC Gold requires multi-factor authentication for any account that accesses registered or controlled datasets. Set this up early using an authenticator app. SMS-based codes are supported but deprecated in practice — several users I've worked with reported receiving OTPs 30 to 90 seconds late, which causes the time-based window to expire before they can submit it. Don't bother with SMS unless you have no other option.
A Real Problem I Encountered — And How I Fixed It
Last year, a researcher I was advising couldn't log into UCSC Gold despite having valid institutional credentials. The login page accepted his username and password, passed MFA without issue, and then immediately redirected him to an access-denied page. No error code. No explanatory message. Just a blank authorization failure. His home institution had recently migrated their identity provider from ADFS to Okta. The SAML metadata URL hadn't been updated in UCSC's service provider configuration, which meant his assertions were being signed with a metadata set that UCSC no longer trusted. The fix wasn't on his end. His university's IT team had to submit an updated entityDescriptor.xml to UCSC's identity management office, which took about four business days to propagate. In the meantime, he accessed the data he needed through a mirror hosted by his collaborating lab, which had an active Gold account under a different institutional affiliation. The takeaway: if you're seeing silent auth failures and your credentials are definitely correct, the problem is almost certainly a metadata or federation mismatch, not a password issue. Check with your institution's IdP team first, then check UCSC's status page. Don't waste hours resetting passwords.
Security Considerations Most People Overlook
UCSC Gold enforces several security measures that aren't prominently advertised. Your session cookies are marked HttpOnly and Secure, which means JavaScript can't read them and they only transmit over TLS. That's standard, but here's what matters more: the system logs your IP address, user-agent string, and query patterns for compliance auditing. If you're running automated scripts or bulk download tools, your behavior profile needs to look reasonable or the system will throttle your requests and flag the account for review. API key management is another area where people get tripped up. When you generate an API key through the Gold dashboard, it's displayed once and never shown again. There's no recovery. If you lose it, you regenerate a new one and invalidate the old one. I've seen people lose keys and then spend two weeks emailing support because they didn't record the original output. Write it down immediately. Store it in a secrets manager if you're managing multiple keys. Data access itself is governed by a tiered permission model. Public tracks are unrestricted. Registered datasets require account verification and a data use agreement. Controlled datasets — things like certain variant calls or population-specific allele frequencies — require Institutional Review Board approval or a documented ethics review from your home institution. The system will block access at the request level regardless of your login status. No amount of credential tweaking will bypass this.

Common Pitfalls and What to Do Instead
Pitfall one: assuming your login session persists across browser sessions. It doesn't. Close your browser, come back later, you're starting from scratch. If you're working on a long query, save your configuration as a custom track or use the session export feature before you close anything. I've lost three hours of query setup more times than I can count because I assumed the session was bookmarkable. Pitfall two: using the same browser profile for both browsing and bulk operations. The system applies different rate limits based on user-agent and session fingerprinting. A standard browsing session gets one set of throttling rules. Automated or scripted sessions get far more aggressive limits. If you're running legitimate bulk queries, generate a dedicated API key and use it consistently. Mixing automated and manual requests under the same session can trigger fraud detection flags. Pitfall three: ignoring the genome build version. UCSC Gold supports multiple genome builds simultaneously, but your login session doesn't lock you into a single one. However, certain registered datasets are build-specific, and attempting to query a dataset against an incompatible build returns a confusing error that looks like a permission failure when it's actually a version mismatch. Always verify your target build before submitting large queries.
Alternatives When UCSC Gold Doesn't Work For You
Not every access need fits through UCSC Gold. If you're working with raw sequencing data rather than annotated tracks, consider the NCBI SRA or ENA as alternatives. If you need real-time API access at scale, the UCSC Genome Browser's public HTTP endpoints don't require authentication for basic queries — you only need Gold credentials for registered or controlled data. Many researchers don't realize this and waste time applying for accounts they don't actually need. For teams that need collaborative access across multiple institutions, setting up a shared Gold account with documented usage policies is common practice. It's not ideal from a security perspective, but it's faster than processing five separate applications. At minimum, use a dedicated institutional email, enforce MFA on the shared credentials, and maintain a shared log of who accesses what and when.
Bottom Line
UCSC Gold login isn't complicated in theory. It becomes complicated when your institution's identity infrastructure is misconfigured, when you apply for the wrong access tier, or when you treat it like a consumer website instead of a research-grade data gateway. Get your federation setup right before you start. Read the data use agreement carefully. Save your work. And don't reset your password hoping it fixes an auth cascade failure — it won't.

 (300 x 215 px) (500 x 358 px).png?itok=jErVSVPd "MyUCSC Portal Guide | University of California Santa Cruz")
