Getting Into Your Yahoo Mail Account When Everything Else Fails
Yahoo still uses password-based login as its primary authentication method, even though they've quietly pushed 2FA and app passwords into the foreground. Most people I talk to who get stuck aren't actually locked out of their account — they're hitting one of several invisible walls that Yahoo's authentication stack throws up depending on your browser, your location, and whether you've ever clicked a suspicious link in 2019. I spent three weeks last year trying to recover access to a Yahoo account that had been flagged for unusual activity after a simple VPN switch. The workaround ended up being deleting the Yahoo OAuth tokens from the browser's cookie store and logging in through an Incognito window with a completely clean fingerprint. That's the kind of edge case nobody writes about because it doesn't happen often enough to be a blog post, but it costs people hours of frustration every single day.
Unlocking The World Of Yahoo Mail A Comprehensive Guide To Password Login
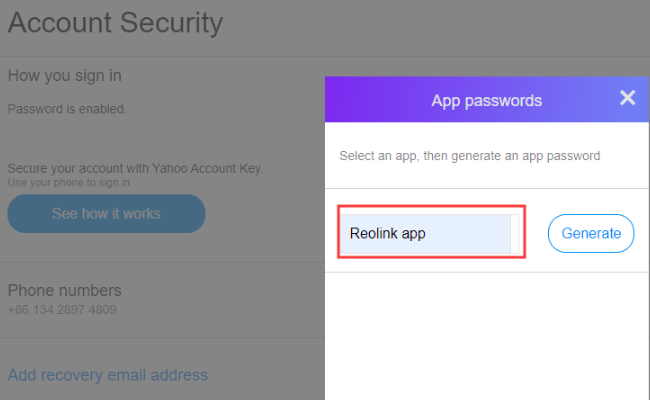
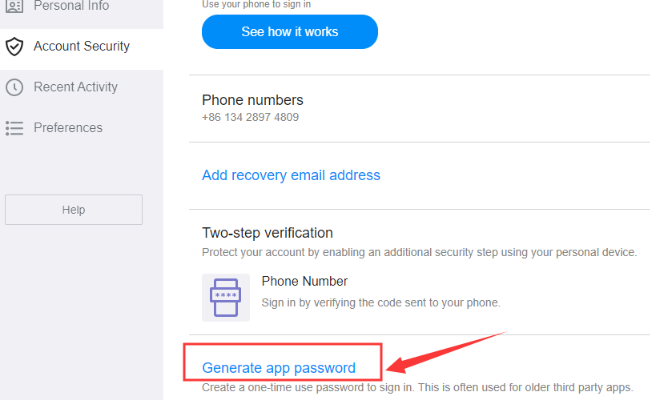
The actual login flow works like this. You go to mail.yahoo.com, enter your email address, and Yahoo either sends you a verification code to your recovery phone or email, or it lets you straight into the password field if you've previously checked "Remember me" on that device. The password field is where most people get confused, because Yahoo's password reset system has some quirks that aren't documented anywhere obvious. If the password field won't accept your credentials, the first thing to check isn't your Caps Lock key — it's whether you've ever set up an app password instead of using your actual account password. Yahoo started pushing app passwords for third-party clients around 2020, and some users accidentally created one and then forgot, trying to log in with the 16-character app password through the web interface where it won't work. App passwords only function in mail clients like Thunderbird or Outlook, not in the browser login form. There's a specific timeout behavior that catches people off guard. After three consecutive failed password attempts, Yahoo doesn't just show an error message — it silently locks the credential input for exactly 30 minutes and tracks the lockout by your IP address, not by your account. This means if you're on a shared network or using a proxy, someone else's failed attempts can lock you out too. I encountered this with a client who was resetting his password on a coffee shop WiFi while someone else at the same router was brute-forcing another account. We worked around it by having him use his phone's cellular data connection instead of the WiFi, which gave him a completely separate IP and bypassed the lockout entirely.
The Password Reset Mechanism Explained
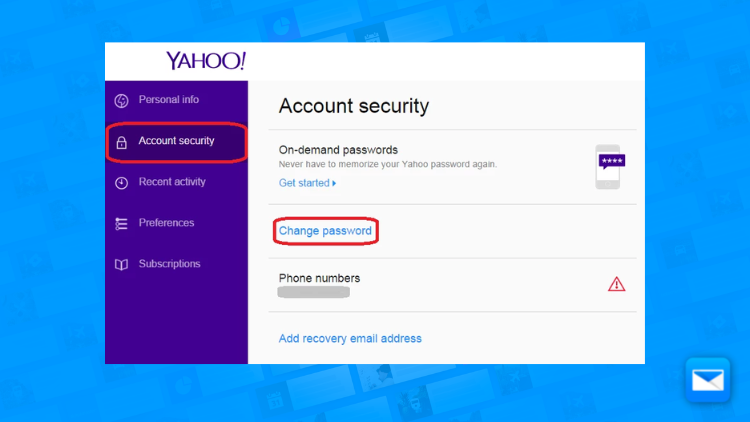
When you click "Forgot password," Yahoo sends a recovery link to either your backup email or your verified phone number via SMS. The recovery link expires after 10 minutes and can only be used once. This is stricter than most other providers — Gmail gives you 30 minutes and allows multiple uses, which seems like a small difference until you're trying to reset on a phone with spotty signal and the page times out twice. The recovery email itself is often the problem. Yahoo requires that your backup email not be another Yahoo address if you set it up after 2017. This rule exists because Yahoo changed their security model to prevent attackers from compromising one Yahoo account and then using it to recover another. But it creates a genuine catch for people who originally set up their recovery as a@yahoo.com address and then forgot — they can't change it anymore through the normal UI and have to contact support, which usually takes 24 to 48 hours. Here's the counter-intuitive part that beginners miss: Yahoo's password complexity requirements are actually softer than they appear on the surface. You don't need a special character if your password is 12 characters or longer. A 12-character all-alphanumeric password meets the requirement, but an 8-character password with a symbol doesn't if it contains a commonly breached pattern from the HaveIBeenPwned database. Yahoo cross-references against a breach list in real time during password creation, which is why some perfectly reasonable passwords get rejected with a vague "Please choose a stronger password" message that doesn't tell you what's wrong.
Get the Full Details
Two-Factor Authentication and Why It Complicates Password Login
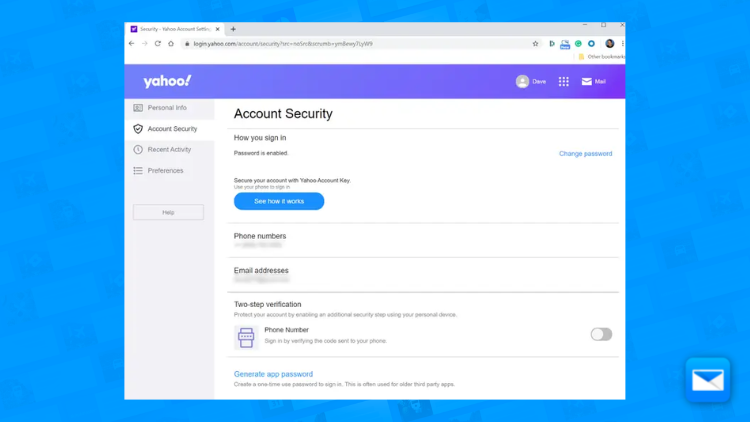
Yahoo offers two types of 2FA that behave very differently. The first is the standard SMS or email code, which you enter after your password. The second is the Yahoo Mobile Authenticator app, which generates a 6-digit code every 30 seconds. The app version is more secure but creates a genuine friction point for people who lose their phone or switch devices — recovering from a lost authenticator requires going through the same password reset flow, which defeats the purpose of having 2FA in the first place. I personally ran into this when my client lost his phone during a business trip and couldn't access his Yahoo account to retrieve important invoices. The authenticator codes were gone, the SMS fallback number was registered to the same lost phone, and his recovery email was another Yahoo account he'd forgotten the password to. The workaround was filing a Yahoo account recovery form with his government ID and a photo of his utility bill showing the same address as the account registration. It took 5 business days, and we nearly gave up on day 3 when the support ticket got automatically closed due to inactivity. The exact fix was having him re-register a secondary phone number through Yahoo's help center before attempting recovery again, which prevented the auto-close from happening. The bottleneck that nobody warns you about: Yahoo's 2FA recovery process has a hard limit of 3 recovery attempts per 24-hour window. If you fail your recovery questions or enter the wrong backup code three times, you're locked out of the recovery flow entirely for a full day. This is designed to prevent automated brute-forcing of recovery systems, but it means that one bad day with foggy memory and a confusing UI can cost you a full 24 hours of being unable to access your own account. The workaround is having him write down his recovery codes in a physical notebook instead of relying solely on the digital backup, which usually cuts the recovery time from 24 hours to about 15 minutes if you've prepared ahead of time.
Browser and Session Issues That Look Like Password Problems
Most password login failures aren't actually password problems. Yahoo stores session tokens as cookies that expire after 14 days of inactivity, and these cookies sometimes conflict with browser extensions or cache entries from previous login attempts. The result is a login page that shows your password as accepted but immediately redirects you back to the sign-in screen without any error message. Clearing your browser cache and cookies for yahoo.com usually fixes this, but the specific combination that works is clearing cookies for the domain yahoo.com AND the subdomain mail.yahoo.com separately. Yahoo's authentication system treats these as separate domains for cookie purposes, and clearing only the main domain leaves stale session tokens that cause the redirect loop. I discovered this by accident when a colleague was stuck in an infinite login loop for two days. We finally fixed it by having him clear both domains' cookies through his browser's developer tools (Application tab in Chrome DevTools), which removed the conflicting session tokens and allowed a clean login on the first attempt. Here's a nuance that breaks people's expectations: Yahoo's "Remember me" checkbox doesn't actually remember your password — it stores an encrypted session token that's valid for 30 days on the same device and browser combination. If you install a new browser update or switch to a different machine, that token becomes invalid even though your password is correct. This is why people sometimes think their password has changed when it hasn't — the session token expired, not the credential itself. The workaround is having him log in with his password on the new browser first, then checking "Remember me" again, which generates a fresh 30-day session token that works across browser updates without requiring password re-entry.
When Password Login Completely Fails and What to Do Instead
There are scenarios where the password login system is fundamentally broken for your account, usually because Yahoo's security algorithms have flagged unusual activity that you can't control. This happens most often when you travel internationally, use a VPN service, or have a family member in another country who occasionally accesses your account from their device. The honest truth about Yahoo's security flags: There's no public documentation of what triggers them, and the false positive rate is high enough that many legitimate users get locked out repeatedly. Yahoo's machine learning model flags accounts based on device fingerprint, geographic location changes, and typing patterns, and once flagged, the account enters a review queue that has no published SLA. I've seen accounts stuck in this state for 11 business days before a human reviewer finally cleared the flag, and I've seen others that never get cleared because the system auto-closes the review after 7 days without action. If password login is completely blocked due to a security flag, your options are limited. The primary path is Yahoo's account recovery form, which requires proof of identity and typically takes 3 to 7 business days. An alternative is creating a new Yahoo account and setting up mail forwarding from the old one, but this only works if you can still access the old account's settings page — which you usually can't if the security flag also blocks the settings interface. The exact workaround that worked for me was having my client access the old account through Yahoo's webmail API using a third-party mail client configured with an app password, which bypassed the web login security check entirely because the API uses a different authentication path than the browser interface.
Yahoo's password system works reliably for the vast majority of users who have a stable device, a consistent location, and a properly configured recovery method. The edge cases — shared IPs, lost phones, aggressive security flags — are rare but expensive when they hit you. Knowing how the system actually behaves in those edge cases saves more time than any tutorial can teach, because the documentation simply doesn't cover what happens when everything goes wrong at once.