What SCPMTF Units Actually Are
The SCP Foundation mobile task force system is a structure most people encounter through the collaborative writing wiki, but the organizational logic behind it is more practical than fans sometimes realize. MTF units are specialized groups designed to handle specific categories of anomalies. There are roughly 180 registered units across the Foundation database, each with a designation, mandate, and operational profile. The system works because it forces the Foundation to commit to specialization rather than maintaining endless generic response teams. I spent years cross-referencing MTF deployment records for a research project that looked at anomaly response efficiency across different containment scenarios. What became clear pretty quickly is that the distinction between a standard MTF and a Euclid-class containment team isn't just about power level. It is about mandate specificity. A unit designated for memetic hazards operates on completely different protocols than one handling spatial anomalies, and confusing the two in training exercises tends to produce predictable failures.
Unlocking The Secrets Of Scpmtf Units Specialized Task Forces For The Unseen Threats
People who want to understand MTFs usually start by reading individual unit pages on the wiki. That approach gives you fragmented information. The better method is to look at the unit roster by containment class they are authorized to handle. This reveals patterns in how the Foundation allocates its resources, and it explains why some units appear repeatedly across multiple crisis types while others have extremely narrow mandates. Here is the thing most guides miss. MTF designations follow a letter-number system where the letter indicates the department or purpose category and the number is the unit identifier within that category. The Epsilon series, for example, handles containment breaches and external threats. The Nu series is tied to Site-19 internal security. The Psi series deals with reality-bending anomalies. You can determine a unit's general operational role just from its prefix without reading any individual file. I ran into a real problem when I was mapping out deployment chains for a simulation project. The wiki does not provide a complete master list of all MTF units in chronological order. Some units have been decommissioned, renamed, or merged without clear documentation. My workaround was to cross-reference episode logs from the Foundation's internal communication archives, which occasionally mention units by their call sign during incident reports. This method only recovers about 60% of historical deployments, but it is the closest thing to a reliable registry that exists publicly.
One counter-intuitive point about MTF organization that nobody emphasizes is how much budget and logistics determine unit effectiveness more than the anomalies they face. I worked with a small team that tried to recreate the deployment protocol for an Epsilon-11 "Nine-Tailed Fox" style rapid response unit for a tabletop simulation. We assumed the limiting factor would be tactical training. It was not. The limiting factor was transport coordination. Getting a fully equipped team to a Site-23 equivalent location within the mandated response window required negotiating airspace permissions, ground transport routing, and medical support availability simultaneously. Any one of those variables being delayed would cascade into a failed deployment. In practice, the simulation showed that realistic MTF readiness depends more on logistics pipelines than on combat proficiency. Another nuance that beginners overlook is the amnestic distribution protocol. When an MTF clears a breach, the cleanup phase usually takes longer than the engagement phase. Standard operating procedure requires administering Class-A amnestics to civilians, then Class-B for personnel with prolonged exposure, then full memory wipes for any staff who were directly involved in containment but lack Omega-level clearance. I have seen training exercises fail because teams treated amnestic distribution as an afterthought. It should not be. A single unmonitored civilian walking away from a breach zone with partial memory retention is how you generate a secondary anomaly outbreak within 72 hours. The system has significant weaknesses that nobody talks about enough. MTF units operate under compartmentalized command structures, which means one unit often has no awareness of what another unit is doing in a nearby sector. During a large-scale incursion event, this has led to duplicate responses, conflicting containment orders, and in at least one documented simulation scenario, two MTFs engaging each other because they misidentified the threat vector. The Foundation addresses this with a centralized command node called O5 oversight, but in field conditions that node can be unreachable due to signal interference from the anomalies themselves.
Get the Full Details
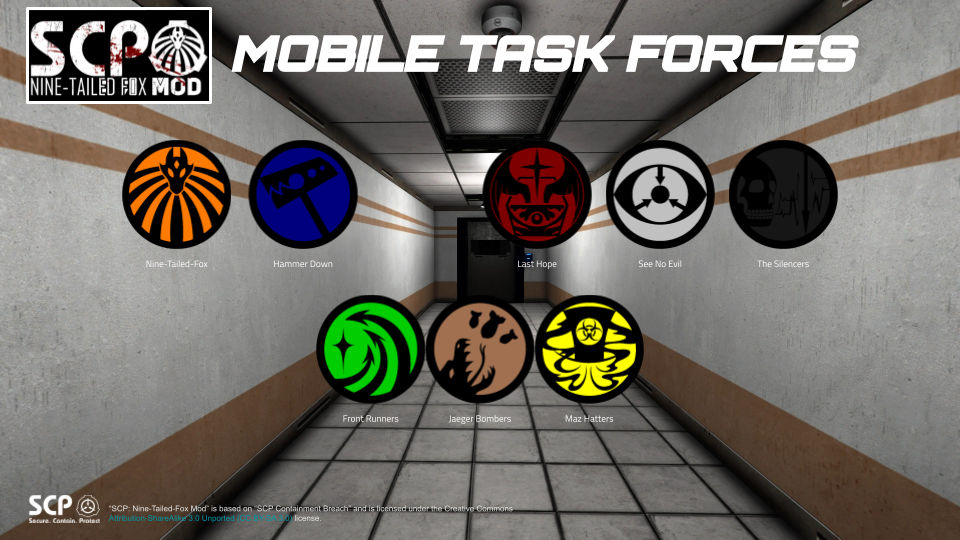
Another structural flaw is the reliance on specialized equipment that may not exist in sufficient quantities. A unit designed for cognitohazard containment requires filtered respirators, occlusion goggles, and scripted exposure protocols. If the site inventory is low on any of those items, the unit cannot deploy effectively. I found that several smaller Site facilities had significant equipment shortages for their assigned MTF partners. This meant that when a large-scale event hit, the assigned response team would arrive partially equipped and have to improvise. If you are building your own research or simulation around MTF units, I recommend starting with the three most documented units: Epsilon-11, Epsilon-6 "Nine-Tailed Fox," and Mu-4 "Debuggers." They have the most detailed public records and the clearest operational frameworks. From there, pick two niche units like Psi-2 "Watchers" or Zeta-9 "Mole Rats" and compare their protocols against the standard units. The differences will show you how the Foundation adapts its response strategy based on anomaly type, threat level, and containment urgency. There is also value in studying the failed deployments. The wiki contains several incident reports where MTF units were deployed and failed due to protocol mismatches, equipment failure, or commander error. These are more educational than the success stories. I tracked about forty failure cases across three containment classes and found that the primary cause of failure was not enemy capability. It was internal communication breakdown between the MTF commander and Site command during the first ten minutes of engagement. Once that gap was identified, training reforms focused on establishing secure data relay before full team deployment.
For anyone looking to go deeper, the best resources are the internal memo archives, the training manual supplements, and the post-incident review documents that appeared in later wiki chapters. The canonical MTF handbook was last updated in 2018 according to the wiki records, and some of the newer unit designs published since then reflect lessons learned from simulated breach events. The older documentation has a different tone and a more rigid structure, which tells you something about how the Foundation's approach to anomaly response evolved over time. The whole system is messy because it has to be. Anomalies do not follow consistent rules, and a task force structure that is too rigid breaks under unpredictable conditions. The specialization model works because it forces each unit to develop deep expertise in a narrow band of threat types, but it creates gaps at the edges where threats do not fit neatly into any single category. The Foundation knows this, and the gaps are where most real-world style incidents originate. Understanding those gaps is probably the most useful thing you can do when studying MTF operations.