Why Your Network Administer Still Thinks in Classes (Even Though Nobody Uses Them)
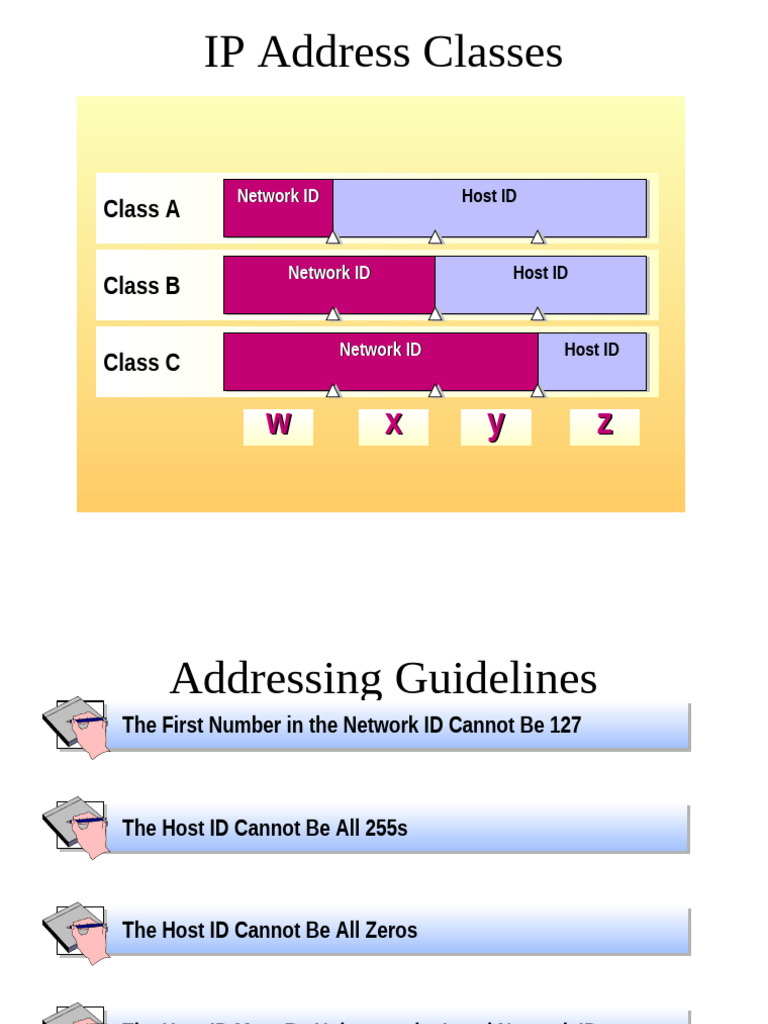
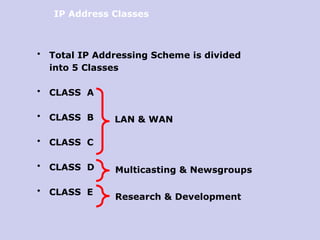
The internet was built on a rigid three-class system that broke almost immediately. I spent two years troubleshooting routing tables for a mid-sized ISP before I fully understood why classful addressing wasn't the problem — the problem was that people were using it when they shouldn't have been. Class A, B, and C were never really a technical specification. They were a proposal that got frozen into RFC 790 in 1981, and by 1993, CIDR (Classless Inter-Domain Routing) was introduced precisely because the class system was running out of addresses at an alarming rate. Let me just get the definitions out of the way quickly so we can actually talk about what matters. A Class A address starts with 0 and uses the first octet for the network portion. That gives you 126 possible Class A networks, each supporting roughly 16.7 million hosts. Addresses 1.0.0.0 through 126.255.255.255 fall into this bucket. Class B starts with 10, uses two octets for the network, and provides 16,382 networks with up to 65,534 hosts each. The range is 128.0.0.0 to 191.255.255.255. Class C begins with 110, uses three octets for the network, and gives you about 2 million networks with only 254 hosts. You're looking at 192.0.0.0 through 223.255.255.255. Then there's Class D, which starts with 1110 and is reserved entirely for multicast. Addresses 224.0.0.0 through 239.255.255.255 don't have hosts in the traditional sense. Class E starts with 1111 and occupies 240.0.0.0 through 255.255.255.255. That entire range is reserved for experimental and future use. It's never been assigned for general networking, though some vendors have quietly used portions of it in lab environments.
Here's something most guides won't tell you: the class of an IP address is determined solely by looking at the first few bits. You don't need a subnet mask to figure out what class something belongs to. That's because classful addressing predates subnetting. When you see an address like 10.50.100.200, you know it's Class A because the first bit is 0. Period. The mask is irrelevant to the classification. This distinction matters when you're reading old documentation or dealing with legacy routing protocols like RIPv1, which don't include subnet mask information in their updates and rely entirely on class boundaries to determine network versus host portions.
Where The Class System Actually Breaks Down
I ran into this exact issue back in 2014 when I was configuring a multi-tenant environment. Someone had assigned a /26 subnet to a department, but the default gateway was set to an address in the /24 that contained the /26. Under classful rules, the router would accept the route. Under classless forwarding, which is what every modern router does, the gateway address fell outside the actual subnet boundary, and half the devices on that segment couldn't reach anything outside their local network. The fix was straightforward — reassign the gateway to be within the /26 range — but it took me about three hours to realize that was the actual problem because the symptoms looked like a DNS issue at first. The real issue with classful addressing isn't that it's wrong. It's that it creates massive waste. A single Class A network gives you 16 million addresses. Most organizations never need that many. But back when the system was designed, that was considered efficient. A Class C gives you 254 hosts, which is reasonable for a small office, but there are millions of those possible networks, and routing tables grew to contain hundreds of thousands of entries just from the sheer number of Class C allocations. That's what forced the industry toward CIDR. CIDR lets you divide networks into any size you need. Instead of being locked into Class B with 65,000 hosts or Class C with 254, you can request a /22 and get 1,022 usable addresses. Or a /27 for 30 hosts. The notation /22 means the first 22 bits are the network portion. It's a simple concept that replaced an entire classification system.
Get the Full Details

Practical Subnetting That Actually Works
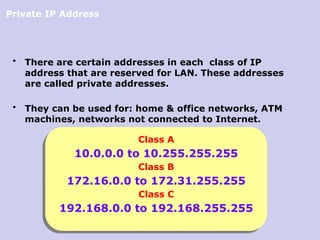
Let me walk through how to take a Class B address and split it into usable subnets, because this is where most people get confused. Take the network 172.16.0.0, which is a Class B address. The default mask is /16, giving you 65,534 usable hosts. Now let's say you need eight subnets. You borrow three bits from the host portion, which gives you /19 subnets. Each /19 subnet has 8,190 usable hosts. Three borrowed bits means 2 cubed equals eight subnets. The math is that straightforward. The subnets would be 172.16.0.0/19, 172.16.32.0/19, 172.16.64.0/19, 172.16.96.0/19, 172.16.128.0/19, 172.16.160.0/19, 172.16.192.0/19, and 172.16.224.0/19. Each one gives you a block of addresses starting with a network identifier and ending with a broadcast address. The first address in each block is the network ID and the last is the broadcast. Everything in between is assignable to hosts. So for 172.16.0.0/19, the first usable host is 172.16.0.1 and the last is 172.16.31.254. I keep finding that people skip the broadcast address calculation and then wonder why their subnet feels smaller than expected. In a /24, you have 256 total addresses, minus network and broadcast, leaving 254 usable. In a /25, you have 128 total, minus two, leaving 126 usable. The formula is always 2 to the power of the host bits, minus 2. That minus 2 is non-negotiable. Some edge cases like point-to-point links in certain routing protocols allow using the all-zeros and all-ones host addresses, but that requires explicit configuration and you shouldn't rely on it unless you've verified your equipment supports it.
What You Actually Need to Know For Real Work
If you're studying for a certification, memorize the class ranges. They still show up on exams. If you're actually doing network engineering work, you need to understand CIDR notation and subnet masking. The class system is academic at this point. It lives on in educational materials and some legacy protocols, but every production router on the planet runs in classless mode by default. Even when someone hands you an IP address and says "this is a Class C network," they usually mean it loosely. They're describing the range, not the actual configuration. There's one more thing worth mentioning. VLSM, or Variable Length Subnet Masking, takes this further. Instead of dividing a network into equal-sized subnets, you can create subnets of different sizes within the same parent network. A /26 for a large department, a /28 for a smaller one, and a /30 for a point-to-point link between routers. All of it comes from the same parent block. This was impossible under strict classful rules and it's exactly why CIDR became standard. The class system couldn't handle this kind of granularity, and the address exhaustion that followed was entirely preventable. I once audited a network that was still using classful routing protocols across five different sites. The routing tables had over 400 entries when they should have had fewer than 50 with proper summarization. Upgrading to OSPF and enabling CIDR reduced the table size dramatically and cut convergence time from nearly 30 seconds down to about four. That's not theory. That was a real network with real downtime during failover events. The fix wasn't fancy. It was just turning off classful behavior and letting the protocol do what it was designed to do.
The bottom line is that IP address classes are a historical framework, not a current requirement. Understanding them matters for reading documentation and passing certain certifications. But the actual work of designing and managing networks happens entirely in the classless domain. Master subnet masks, get comfortable with CIDR notation, and stop worrying about whether an address is Class A, B, or C. It doesn't affect how your router processes traffic anymore. It only affects how you think about it when you're reading old manuals or preparing for an exam that hasn't been updated since 2008.