Getting past the login screen on Relias
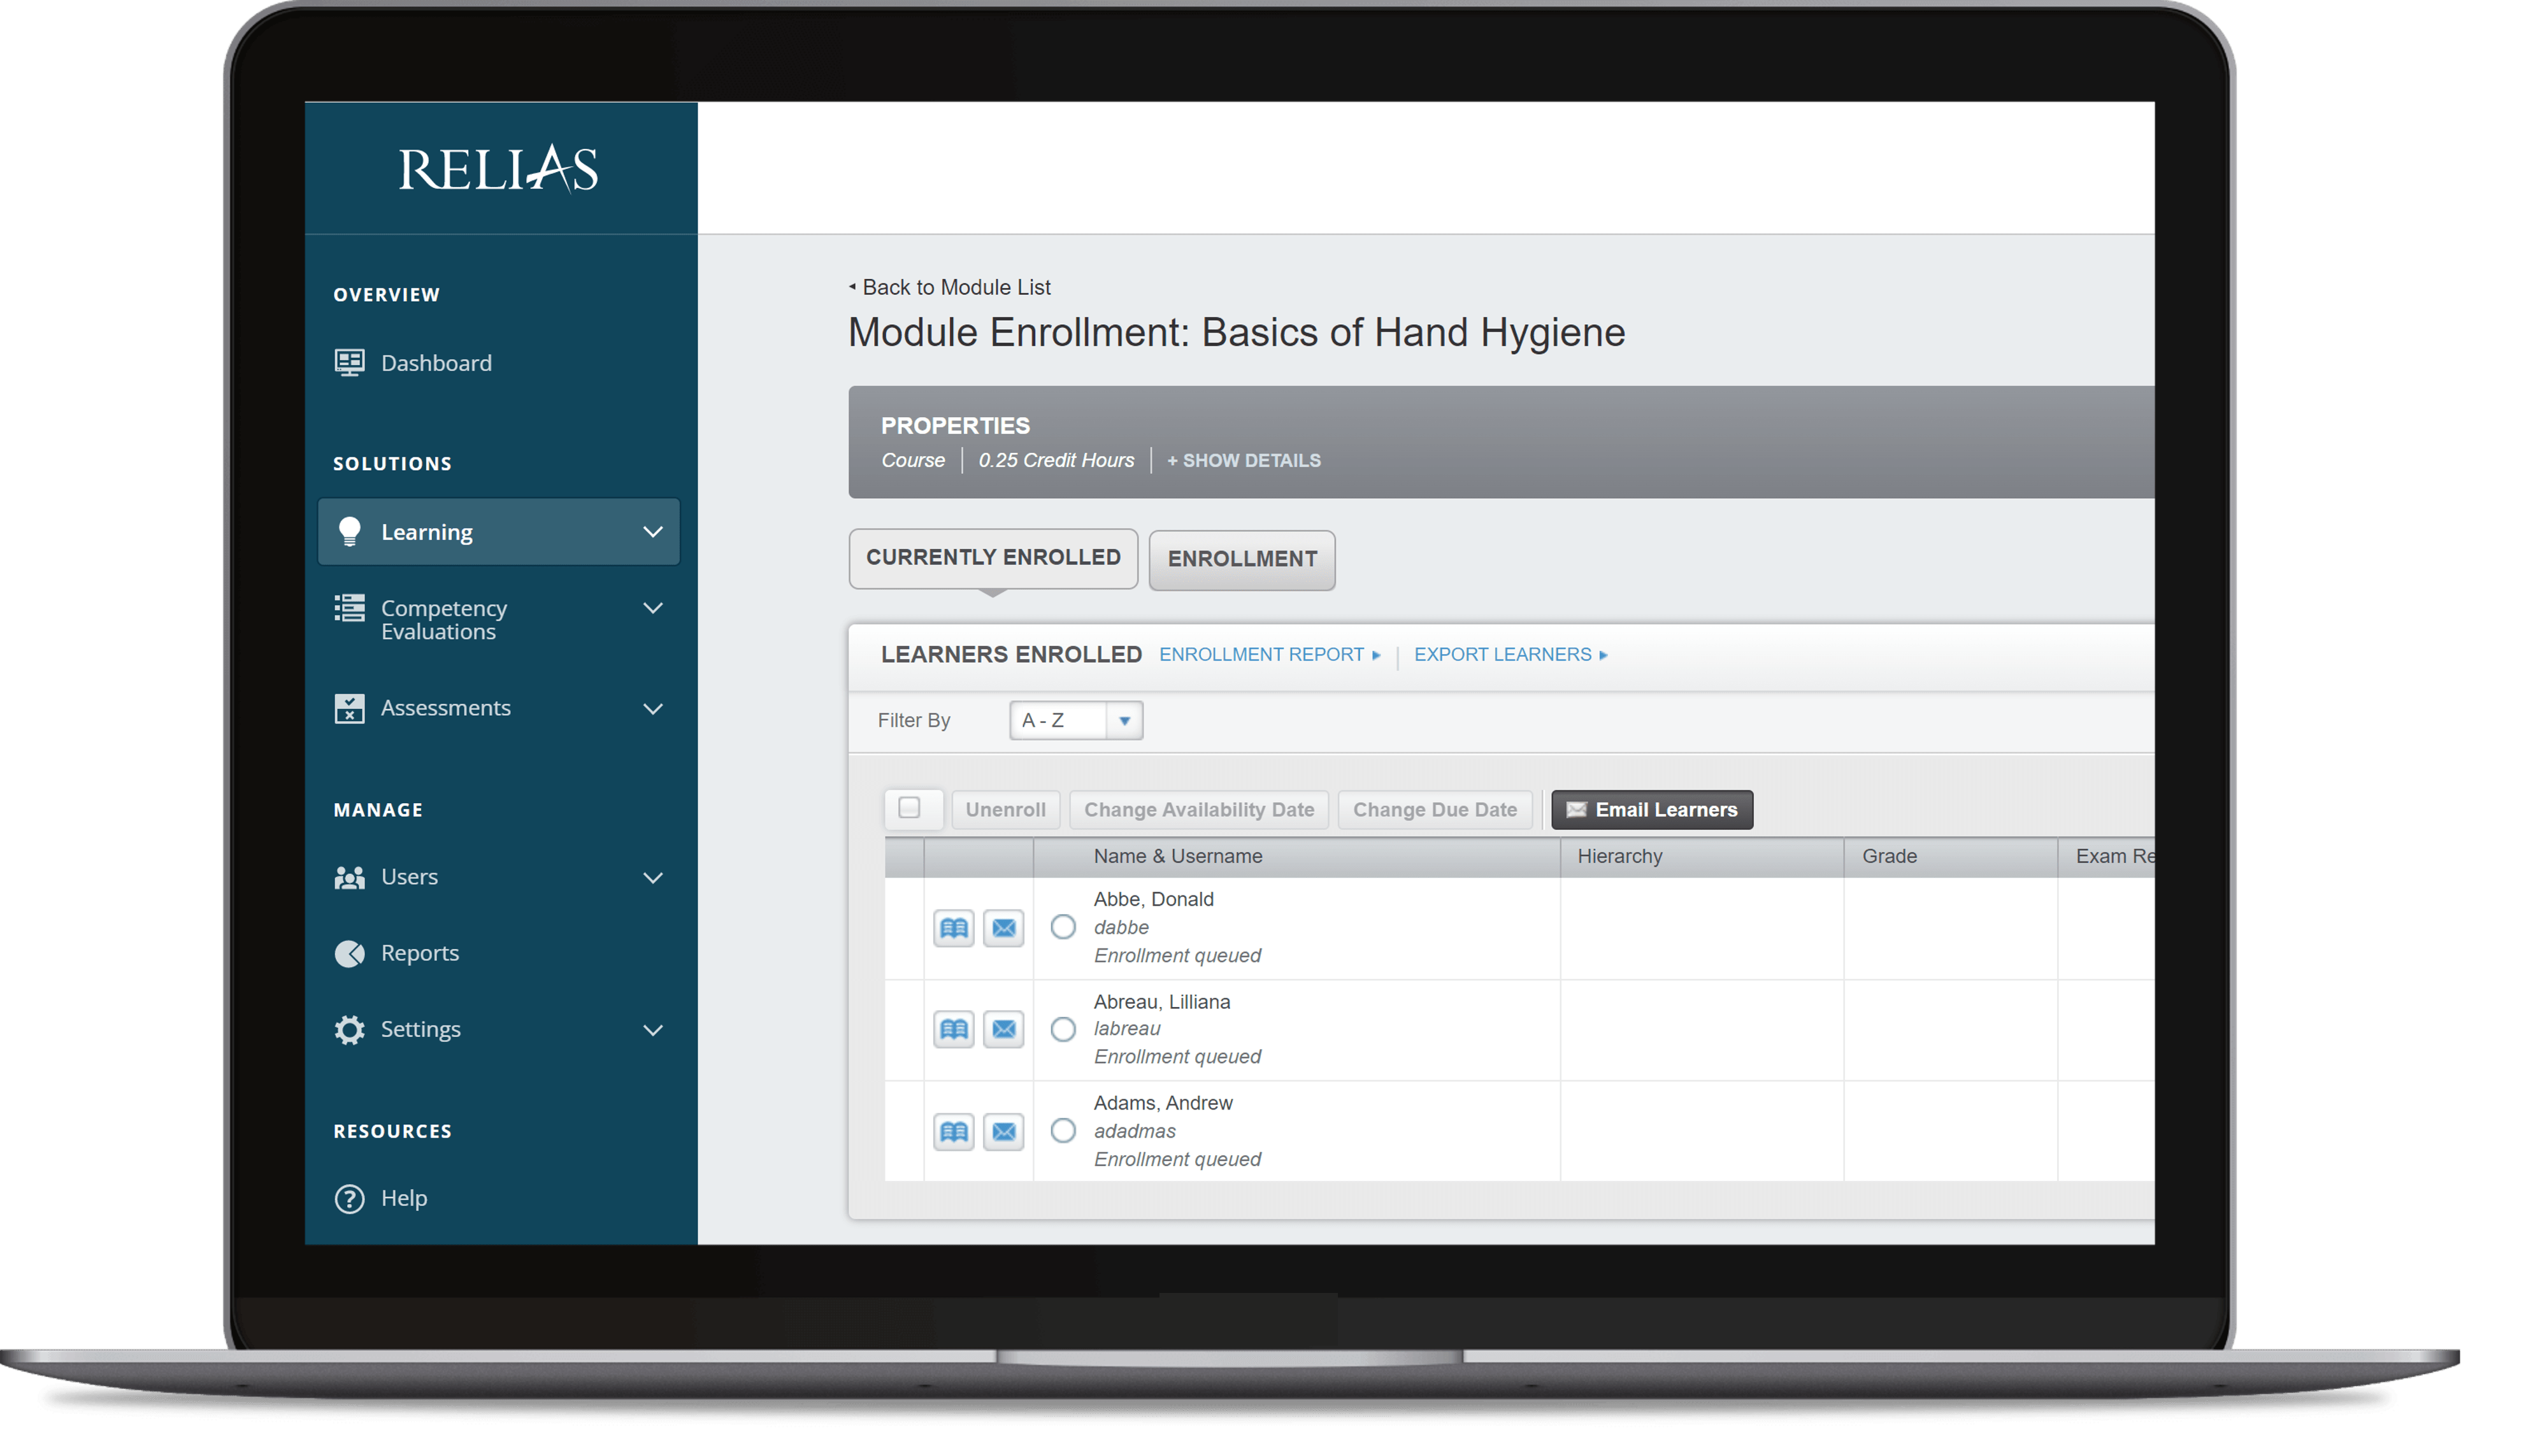
Most people treat Relias login as just another chore. You go in, type credentials, click submit, and move on with your day. But the platform is built for healthcare organizations that need to track compliance across dozens of facilities, hundreds of staff members, and shifting regulatory requirements. Getting the login piece right matters more than most administrators realize. Relias (now part of ReliasLLC, acquired by Relias Learning) is a cloud-based compliance and training platform used by hospitals, nursing homes, home health agencies, and clinics. It handles mandatory training modules, competency tracking, license management, and audit readiness. The login process itself seems straightforward on paper. Add SSO, OIDC, or basic credential authentication to the mix and suddenly it becomes a support ticket waiting to happen.
Unlocking The Power Of Relias Log In Revolutionizing Healthcare Training And Education
Here is how the login flow actually works when everything is set up correctly, and more importantly, what breaks when it is not. You start by navigating to your organization's assigned Relias portal URL. This is not the public Relias homepage. Each customer gets a subdomain, usually formatted as yourorgname.reliasllc.com or similar. Your IT or compliance team provisions these accounts. If you were assigned a username, it is typically an email address or an employee ID, depending on your organization's configuration. The first attempt at login will ask for your credentials. If your organization uses single sign-on through Okta, Azure AD, or another identity provider, the page redirects you to their authentication portal before returning to Relias. This redirect is where most issues surface.
I spent three weeks untangling a problem at a regional health system where roughly forty percent of their nursing staff could not complete their annual compliance modules. The root cause was not the training content. It was the SSO redirect loop. Their Okta tenant had a misconfigured ACS URL that caused the Relias SP to reject the SAML assertion as malformed. Users would hit the login page, get redirected to Okta, authenticate successfully, then get bounced back to Relias with a white screen. No error message. Nothing. They just sat there refreshing the page thinking their internet was broken. The workaround was to bypass SSO entirely for those users and provision them as local Relias accounts with email password authentication. This gave them immediate access to their modules while the identity team fixed the ACS configuration on the Okta side. It took us about four hours to migrate those forty accounts from the failed SSO path to local authentication. During that window, those staff members could complete their required training without escalating it to a compliance issue. If you are dealing with a similar situation, check whether your identity provider is sending the NameID format that Relias expects. Relias typically expects email as the NameID. If Okta or Azure AD is configured to send a GUID or username attribute instead, the SAML response arrives at Relias looking invalid. You can verify this by pulling the SAML response XML from your IdP logs and checking the NameID element. It should contain the user's email address, not an internal identifier.
Get the Full Details

Common login problems and what they actually mean
Let me walk through the ones that show up most often, because the error messages Relias gives you are not always accurate. Error: Invalid credentials or account not found. This is the most common message and it is almost never about the password being wrong. If you have recently changed your email address at work or your organization merged two facilities, your Relias account may still be under the old email. I have seen this repeatedly during M&A activity. The fix is to contact your Relias administrator within your organization and request an account merge or email update. Do not create a second account. That creates duplicate employee records that will trip up your compliance reporting later. Error: Account locked after multiple attempts. Relias has a lockout policy, typically after five failed attempts within a ten-minute window. This is designed to prevent brute force attacks but it catches people who are already frustrated. If you hit this, wait fifteen minutes before trying again. Do not keep resetting the password. Each reset attempt counts toward the lockout counter on some configurations. I learned this the hard way with a long-term staff member who kept triggering the lockout because she was entering her password from a sticky note rather than checking her credentials in the identity provider.
SSO works but the user lands on an empty dashboard. This means the authentication succeeded but the user has no active enrollments or courses assigned. This happens constantly when new hires are onboarded and the HR integration between your ATS or HRIS and Relias has a delay. The employee can log in, but there is nothing to do. The person handling onboarding needs to verify that the Relias integration job has run. Check the Relias admin console under integrations or HR data imports. If the new hire's record shows a status of "pending import" or "failed," that is your bottleneck. Password reset emails land in spam or bounce. Relias sends password resets from an address that varies by deployment. Some organizations see it come from noreply@reliasllc.com. Others see it from a subdomain tied to their specific instance. If your email security gateway flags it as suspicious, add the sending domain to your allowlist. Otherwise, your staff will sit idle waiting for a reset link that never arrives. I had a facility where the entire radiology department was blocked from receiving Relias communications because their mail filter saw "reliasllc.com" and categorized it as potentially deceptive domain activity. We spent two days working with the network team to whitelist the domain before anyone could reset their credentials.
What the login process actually enables
Once you are authenticated, Relias unlocks a specific set of capabilities that most healthcare organizations rely on for daily compliance operations. Compliance tracking across multiple sites. A hospital system with twelve locations can manage training requirements differently per site while maintaining a unified reporting view. Each location can have its own role-to-course mappings. An nurse at Location A might need different mandatory training than a nurse at Location B if state regulations differ. The login system ties every activity to a specific employee record, so auditors can trace exactly who completed what and when. Audit trail generation. Every login event, course start, module completion, quiz attempt, and certification renewal is logged with timestamps and IP addresses. During a TJC or CMS survey, the compliance officer pulls this data and produces a report. The quality of that report depends entirely on the accuracy of the underlying login and session data. If SSO is misconfigured and users are authenticating inconsistently, your audit trail gets gaps. Those gaps look bad in front of an auditor even though they are just a technical artifact.
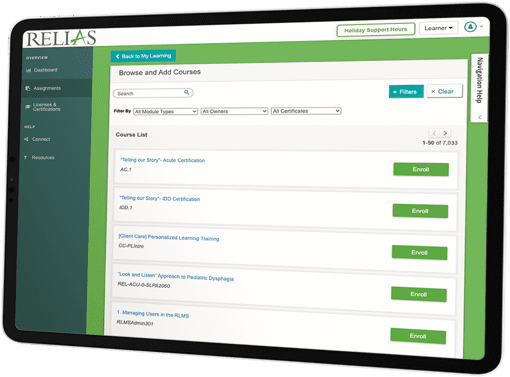
Role-based learning paths. Relias assigns courses based on job role, department, and sometimes individual licensing requirements. A respiratory therapist needs different modules than a phlebotomist. When you log in, the platform filters the course catalog to show only what is relevant to your role. This reduces noise and completion times. A staff member who sees thirty relevant assignments finishes them faster than one who sees two hundred and has to figure out which ones apply. Mobile access for non-desk staff. Many healthcare workers do not have a dedicated computer. Nurses, aides, and technicians use their phones or shared devices. The Relias mobile app mirrors the web experience and allows course completion on mobile browsers or through the dedicated app. Login works the same way but there are additional considerations. If your organization requires MFA, mobile users may struggle with push notification approval if they lose their enrolled device. Having a backup MFA method like SMS or a hardware token available is something I would recommend before your staff hits a deadline with a broken phone.
Things Relias does not handle well
I want to be direct about the limitations because vendors will not volunteer this information. Cross-organization transfers leave data behind. If an employee moves from one Relias customer to another, their training history does not transfer. The new organization starts from zero. There is no standardized export-import process for individual training records between separate Relias deployments. You can sometimes work around this by having the employee recomplete critical modules, or by manually documenting completed training in a separate system and using that as evidence during audits. Neither option is ideal. Large-scale account provisioning is slow. Importing hundreds of new accounts through CSV takes time and is error-prone. I have watched compliance teams spend entire afternoons cleaning up name formatting errors, duplicate email entries, and mismatched department codes in bulk upload files. A single missing field can cause half the file to fail. Automating this through an HRIS integration is significantly more reliable but requires upfront development work and ongoing maintenance.
Offline course access is limited. Some modules support offline download through the mobile app, but not all content types are available offline. Video-based lectures, interactive simulations, and assessment-heavy modules usually require an active internet connection. If your staff works in areas with poor connectivity or uses devices that do not support the app, you will see higher completion delays during survey season. Custom branding costs extra. The base Relias platform provides a standardized interface. Organization-specific branding, custom color schemes, and white-label options are typically part of higher-tier licensing agreements. Smaller clinics and private practices often find themselves stuck with the generic Relias login page, which can confuse staff who are used to seeing their organization's name and logo on training portals. It is a minor issue but it adds to the perception that the system feels impersonal.

Practical steps to set up reliable login access
If you are responsible for getting your organization's staff into Relias without constant support requests, here is the sequence that actually works. First, confirm your SSO configuration before the go-live date. Test with at least five accounts representing different departments. Do not test with administrator accounts only. Administrator permissions behave differently in SSO flows and will not surface the same issues that frontline staff encounter. Verify that each test user can authenticate, land on a dashboard with assigned courses, and complete a module without encountering errors. Second, establish a clear communication plan. Send staff a brief email with their login URL, their username, and instructions for password reset. Include the support contact for the IT help desk. Do not assume people know how to find their portal. Most will try Google and land on the wrong site.
Third, set up automated monitoring for failed login attempts. Relias provides reporting on authentication failures. Review this weekly during the first month after launch. A spike in failures usually indicates a configuration drift or a new staff onboarding issue that needs attention. Fourth, maintain a local account fallback. Keep a small pool of local Relias accounts that bypass SSO entirely. When your identity provider goes down during a critical training deadline, these accounts let your staff complete their requirements without waiting for IT to restore the SSO service. This is not a best practice for normal operations but it is a practical safety net. The login process itself is not complicated. What makes it difficult is the environment around it. Multiple identity providers, merging organizations, staff turnover, and tight compliance deadlines all converge on that single authentication step. Getting it right means understanding where the failures happen before your staff hits them.