Setting Up NFS Sharing Without Breaking Your Server
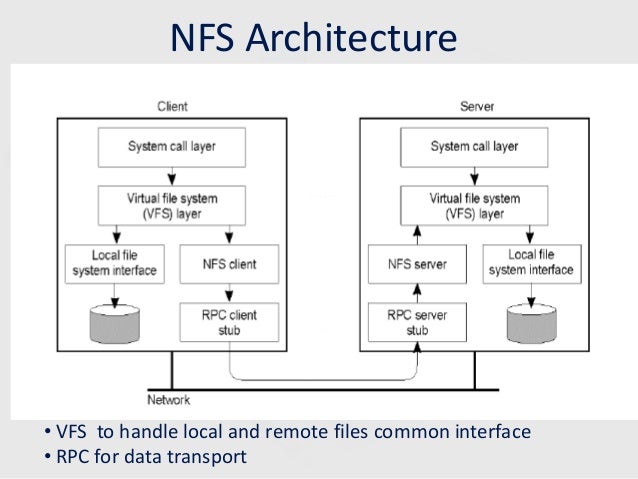
NFS has been around since the early 80s and it still shows up everywhere. When you need a quick file share between Linux machines without setting up Samba or a full NAS stack, nfsd is the default route. The problem is that most guides treat it like a two-command setup and then skip every piece that matters for security and reliability. I've spent years fixing NFS issues that came from people following incomplete tutorials. Here's what actually works. First, a word on terminology. "Nfsd portals" isn't really a standard phrase in the Linux community. What people usually mean when they say this is the combination of NFS daemon configuration, port mapping via nfs-utils, and the firewall rules needed to make it actually work. The nfsserver kernel module handles the daemon side, while nfs-utils provides the userspace tools like exportfs and the mountd/rquotad services. There isn't a single package you download called "nfsd portals." The closest thing to a comprehensive guide on this topic would be a collection of server hardening practices, firewall configuration, and export management steps. Here's how I approached a recent deployment where a client needed shared storage across twelve compute nodes running CentOS Stream. The export file looked straightforward on paper. The reality was messier.
Installation and Basic Configuration
On Debian-based systems, you install the NFS server packages with a single command. On RHEL-family distributions, it's slightly different but equally simple. The key package is nfs-kernel-server on Debian or nfs-utils on RHEL. After installation, you need to create your export directory and define it in /etc/exports. That file uses a specific syntax that trips people up regularly. A typical entry looks like this: /data/shared 192.168.1.0/24(rw,sync,no_subtree_check) The options matter more than most people realize. Sync means writes are committed to disk before the server acknowledges them. This prevents data loss if the server crashes, but it slows things down. Async is faster but risky. no_subtree_check avoids a performance hit when directories inside the export change frequently. If you're sharing a single directory tree, you might also want no_root_squash, though that's a security tradeoff worth understanding before enabling.
Once exports are defined, you reload the configuration with exportfs -ra. The nfs-kernel-server service needs to be running. Verify with systemctl status nfs-server. On some systems it's called nfs-server.service and on others the naming differs slightly.
Get the Full Details
Port Management and Firewall Configuration
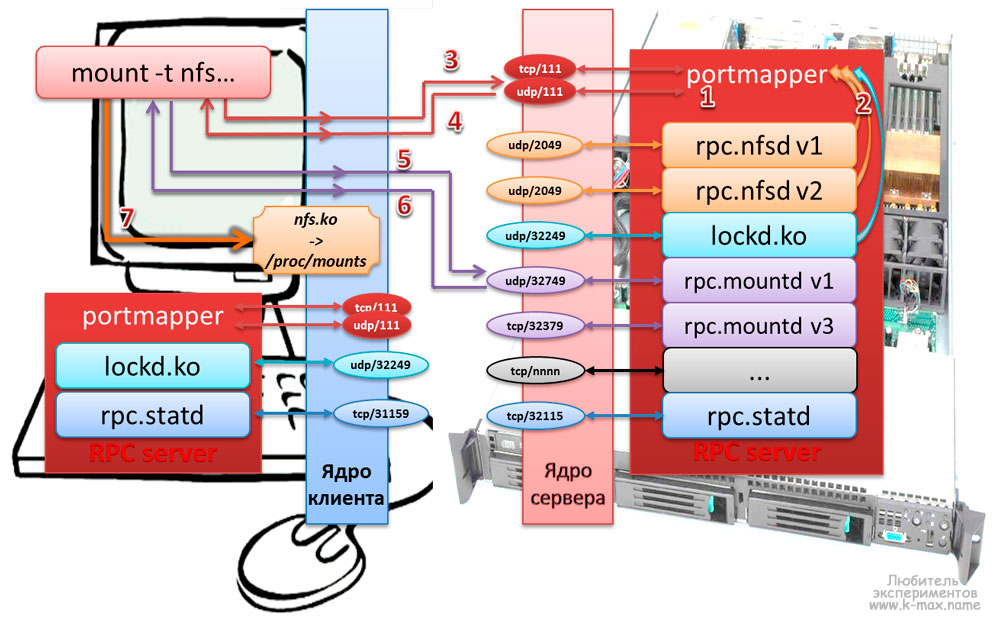
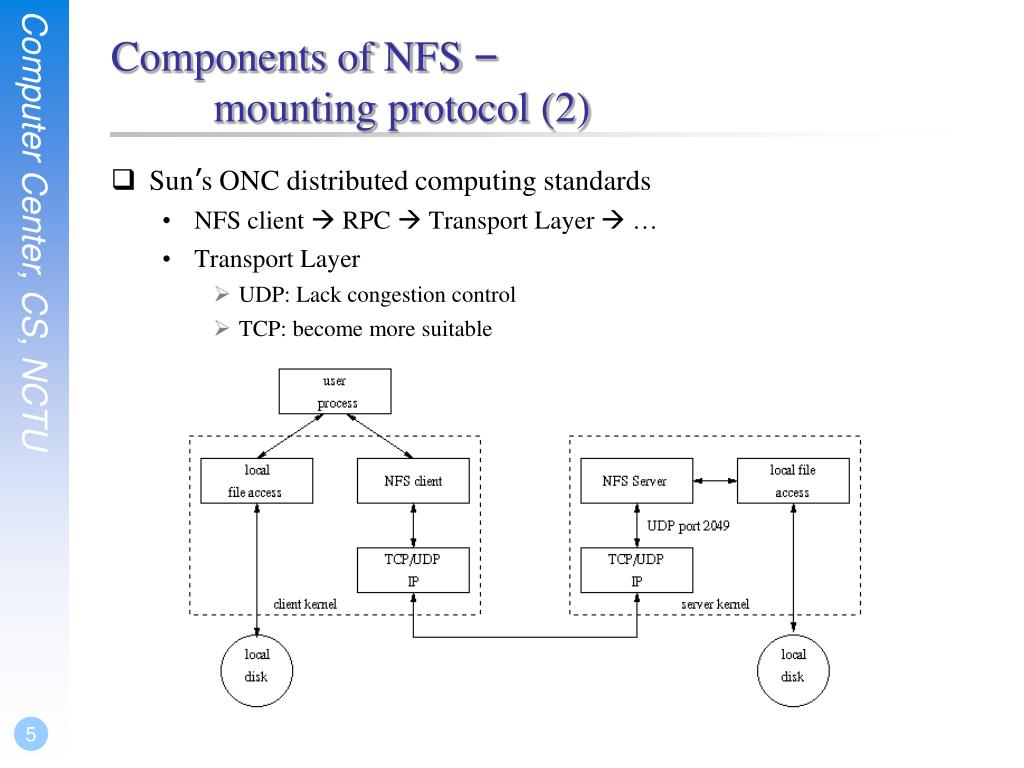
This is where most deployments fail silently. NFS doesn't use a single port. The main nfsd daemon listens on port 2049, but mountd, statusd, and other supporting services bind to dynamic ports. That's what "portals" people refer to when they talk about this confusing setup. If your firewall only opens 2049, clients can authenticate and mount, but operations will hang unpredictably. The fix is to either configure static ports for the supporting services or open the full ephemeral range. I prefer the static approach because it's cleaner for firewall rules. Add these lines to /etc/sysconfig/nfs or /etc/nfs.conf depending on your distribution: MOUNTD_PORT=892
STATD_PORT=893
LOCKD_TCPPORT=894
LOCKD_UDPPORT=894
RQUOTAD_PORT=895
Then restart the NFS services and open those specific ports in your firewall instead of the entire 1024-65535 range. This matters if you're dealing with a strict security audit or a cloud environment with limited egress rules.
Security Considerations That Actually Matter
Everyone mentions Kerberos and encryption, but the realistic threat model for internal NFS is different. The biggest issue I see is over-permissive exports. The default behavior of NFS is trust-based. If a host is in your export list, it gets whatever access you specified. There's no per-file permission layer. This means a compromised compute node with NFS access can read everything in that export tree. My workaround for a sensitive deployment was to use separate export trees with different IP ranges and restrict mounts to specific subdirectories using bind mounts. It's not perfect but it limits blast radius. For the actual credential management, I switched from host-based authentication to IDMAPD with a centralized NIS domain. The default behavior of IDMAPD is to map everything to nobody, which causes permission errors that are incredibly difficult to debug if you don't know what to look for. Another thing people miss: NFSv3 over TCP is still the most reliable choice for most workloads. NFSv4 is technically superior but introduces complex state management that fails silently under high load. I've seen production environments where switching from v3 to v4 caused random file lock deadlocks that took days to diagnose. The workaround was reverting to v3 with the sec=sys mount option and accepting the authentication model that comes with it.
Common Pitfalls and How I Fixed Them
I spent three days debugging an issue where files created by one client appeared with wrong ownership on another client. The root cause was a mismatch in the idmapd.conf files between servers. Each server had a different Domain value. NFS ID mapping uses that Domain field to translate between numeric UIDs and human-readable names. When the domains don't match, the translation fails and everything falls back to UID 65534, which is nobody. The fix was ensuring the Domain line was identical across all participating servers. It should be a fully qualified domain name, not a short hostname. Another issue that cost me a weekend involved NFS locks disappearing after a server reboot. The nfsmount options included nobg and intr, which are outdated. Modern kernels handle background mounting and signal interruption differently. Removing those options and letting the kernel use its defaults resolved the lock inconsistency. Documentation for NFS often lags behind current kernel behavior by several release cycles.
What NFS Still Can't Do Well
Let's be honest about the limitations. NFS is not encrypted by default. There is no native TLS support in the core protocol for NFSv3, and NFSv4.2 has minimal encryption extensions that most implementations don't bother with. If you're crossing untrusted networks, you need a VPN or IPsec tunnel. This isn't optional. I've seen organizations run NFS over public Wi-Fi in conference centers and wonder why their data was intercepted. NFS also struggles with non-POSIX compliance on mixed operating systems. Windows NFS implementations exist but have notable bugs with file locking semantics. Apple's NFS client has historically been unreliable for write-heavy workloads. If your environment includes heterogeneous clients, test thoroughly before deploying at scale. The scalability ceiling is another concern. NFS doesn't handle thousands of concurrent clients gracefully. The kernel nfsd thread model hits contention around 200-300 simultaneous connections on typical hardware. Beyond that, you're looking at either switching to NFSv4 with multiple NFS server threads, migrating to GlusterFS or CephFS, or accepting degraded performance. I once watched an NFS server degrade to single-digit IOPS under a load that a similarly specced Samba server handled without breaking a sweat.
When to Choose Something Else
If you need encryption in transit, consider SSHFS for smaller deployments or Samba with AES encryption. For large-scale distributed storage, look at CephFS or GlusterFS. NFS is appropriate when you have a controlled environment, similar Linux clients, and need simple POSIX-compatible file sharing without the overhead of a clustered filesystem. It's not the best tool for every job, but it's the right tool for a specific subset of problems and that subset is still quite large in practice. The bottom line is that NFS works reliably when you understand what each configuration option does and where the failure modes live. Most guides skip those details. The difference between a smooth deployment and a troubleshooting nightmare usually comes down to a handful of configuration choices made in the first hour of setup.