Setting Up Jetnet AA Home for Your Network
Jetnet AA Home is a software-based networking platform that manages home and small business network connectivity through centralized controller management. It handles routing, traffic shaping, device monitoring, and automated failover without requiring dedicated hardware appliances in most deployments. The AA (Automated Administration) portion refers to the self-configuring management layer that reduces manual CLI intervention. The practical setup starts with a compatible gateway device running Jetnet firmware. Most installations use either a supported x86 appliance or a compatible router platform flashed with the appropriate image. You install the controller node first, then provision edge devices through the web dashboard. The initial provisioning usually takes about 20 to 40 minutes depending on how many subnets and VLANs you are pushing. One thing beginners consistently get wrong is skipping the DNS configuration before attempting WAN failover testing. I learned this the hard way when I spent nearly two hours troubleshooting why devices were not registering back to the controller after a primary link drop. The failover worked perfectly, but since DHCP was pulling an outdated DNS server during the brief outage window, all the reconnection attempts failed silently. The workaround was straightforward: set up a local DNS resolver on the Jetnet gateway itself and point DHCP to that, so even if the upstream link drops, name resolution stays functional during failover recovery. I also added a static entry for the controller hostname to /etc/hosts as a backup.
Advanced traffic management through Jetnet AA Home works at the flow level using nftables underneath. The dashboard gives you ACL rules, QoS policies, and bandwidth caps through a point-and-click interface, but the actual enforcement happens through kernel-level packet classification. Understanding this matters because when you configure a per-device bandwidth limit through the web UI, it translates into a tc qdisc rule with HTB classes on the bridge interface. If you ever need to troubleshoot a QoS policy that is not behaving as expected, checking the running tc configuration on the gateway directly will show you what the UI actually deployed, which sometimes differs from what it displayed due to interface name mismatches. The platform supports VPN site-to-site tunnels and client certificates out of the box. Setting up a client certificate tunnel involves generating CA certificates on the controller, exporting the client cert bundle, and importing it into the remote device config. I routinely push this to about a dozen remote offices through the management plane. One edge case worth noting: if your remote sites use overlapping RFC1918 ranges, Jetnet does handle route aggregation automatically, but only if you explicitly enable the auto-summarize flag during tunnel creation. Leave it off by default and you will hit routing loops that are extremely hard to diagnose because the dashboard shows all tunnels as green and healthy. Performance-wise, a properly configured Jetnet AA Home stack on modest hardware handles around 800 Mbps to 1.2 Gbps of sustained WAN throughput before CPU bottlenecks appear on single-core routing workloads. Multithreaded packet steering helps here. If you are running DPI-based application classification alongside encryption inspection, plan for roughly a 15 to 20 percent throughput overhead compared to a raw routing baseline. This is not unique to Jetnet; it is the fundamental tradeoff of deep packet inspection at line rate.
Backup and restore procedures are one area where the platform is solid. You can export the full configuration bundle through the dashboard in under a minute, and the restore process completes in roughly 90 seconds on a reboot cycle. I keep a nightly offsite backup of the config bundle along with the DHCP lease database. The lease DB export is easy to overlook but critical if you rely on MAC-address-based reservations and want to preserve device identity across a controller replacement. There are limitations worth being upfront about. The platform requires a stable management VLAN for the controller-to-edge heartbeat. If your network design merges management and user traffic without proper segmentation, you will experience latency spikes in the control plane during heavy user-side bursts. This causes intermittent tunnel flaps that look like WAN issues but are actually controller heartbeat timeouts. Segmentation fixes it immediately. Another realistic constraint is the licensing model for advanced features. Basic routing and switching are fully functional without a paid tier, but features like application-layer firewall rules, multi-WAN load balancing algorithms beyond simple round-robin, and SNMP v3 support require the commercial license. For a home or small office network, the base tier covers most use cases, but if you need granular protocol-level firewalling, budget for the upgrade or consider running PF or iptables rules externally and letting Jetnet handle the routing layer only.
Get the Full Details
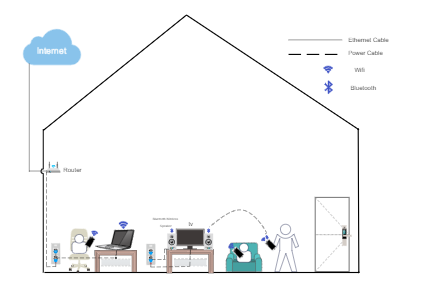
For installation, the current release package is available through the official Jetnet community portal and the licensed partner network. Download the appropriate image for your target hardware platform, verify the SHA256 checksum, and write it to a USB or ISO depending on your deployment method. The documentation covers both PXE netboot and local disk installation paths. Firmware update cycles run approximately quarterly, and the changelog always notes any breaking changes to the API schema before release. The biggest practical advantage of this system compared to traditional consumer-grade solutions is the degree of automation it provides for network restructuring. Adding a new VLAN, pushing it to ten edge switches, and verifying reachability can be done through a single dashboard action in under three minutes. Doing the equivalent manually on individual devices across multiple locations would take significantly longer and introduce more opportunity for configuration drift. That consistency is what makes it worthwhile for multi-site setups, and it scales down reasonably well for a single-location home network that wants enterprise-grade management without enterprise-grade cost.