What Identicom Actually Does
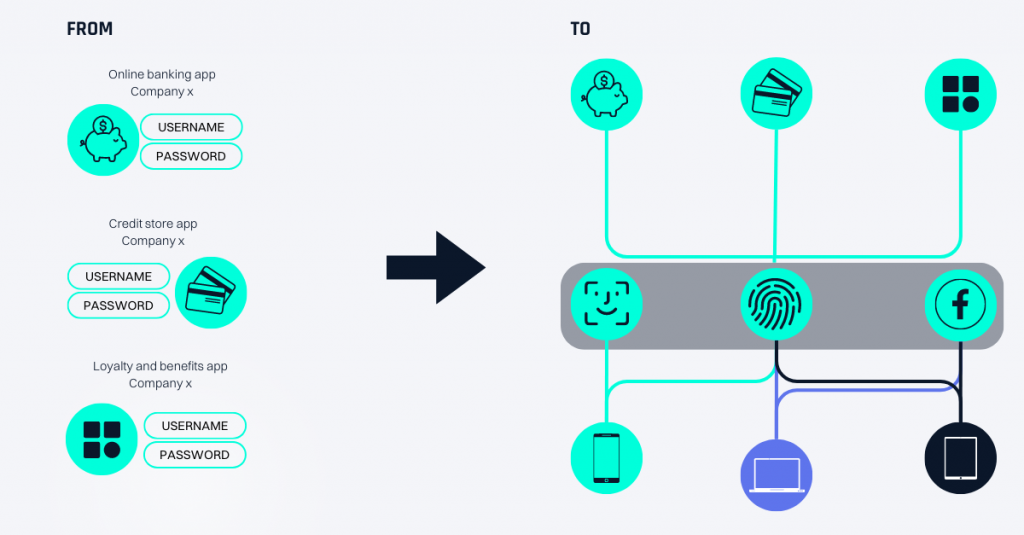
Identicom is a biometric authentication platform that replaces passwords with digital fingerprints, facial recognition, or voice patterns. It integrates into existing identity management systems and handles the verification side of things without forcing you to rewrite your entire access stack. Most organizations use it because maintaining separate credential databases is expensive and error-prone. The platform works through a capture device, a processing layer, and a match engine. You enroll a user once, store the resulting template in a secure vault, and subsequent logins just compare fresh samples against that stored reference. The tricky part is getting the enrollment quality right from the start. Bad data going in means bad matches coming out, and you will spend weeks troubleshooting false rejects before realizing the issue was on the input side. I spent three weeks chasing down a 12% false rejection rate on a deployment for a mid-size healthcare provider. Their IT team blamed the algorithm. I found out they had been using low-resolution webcam feeds for enrollment instead of the certified capture devices Identicom recommends. Switching to proper hardware dropped the error rate to under 1%. The matching engine was fine the whole time. It is a common mistake people make when they treat the platform like a software install rather than a hardware-dependent system.
Setting Up the Enrollment Pipeline
Start by deploying the capture SDK on your target devices. Identicom supports standard USB biometric scanners and compatible mobile cameras. You do not need proprietary hardware unless your use case requires it, but the cheaper the sensor, the more tuning you will need to do on exposure and lighting parameters. The enrollment flow should validate sample quality before accepting data. The SDK provides confidence scores during capture. I always build a minimum threshold check into the enrollment screen so users know immediately if they need to retake their sample. Skipping this step results in a database full of marginal templates that look fine on paper but perform poorly in production.
Integrating With Existing Systems
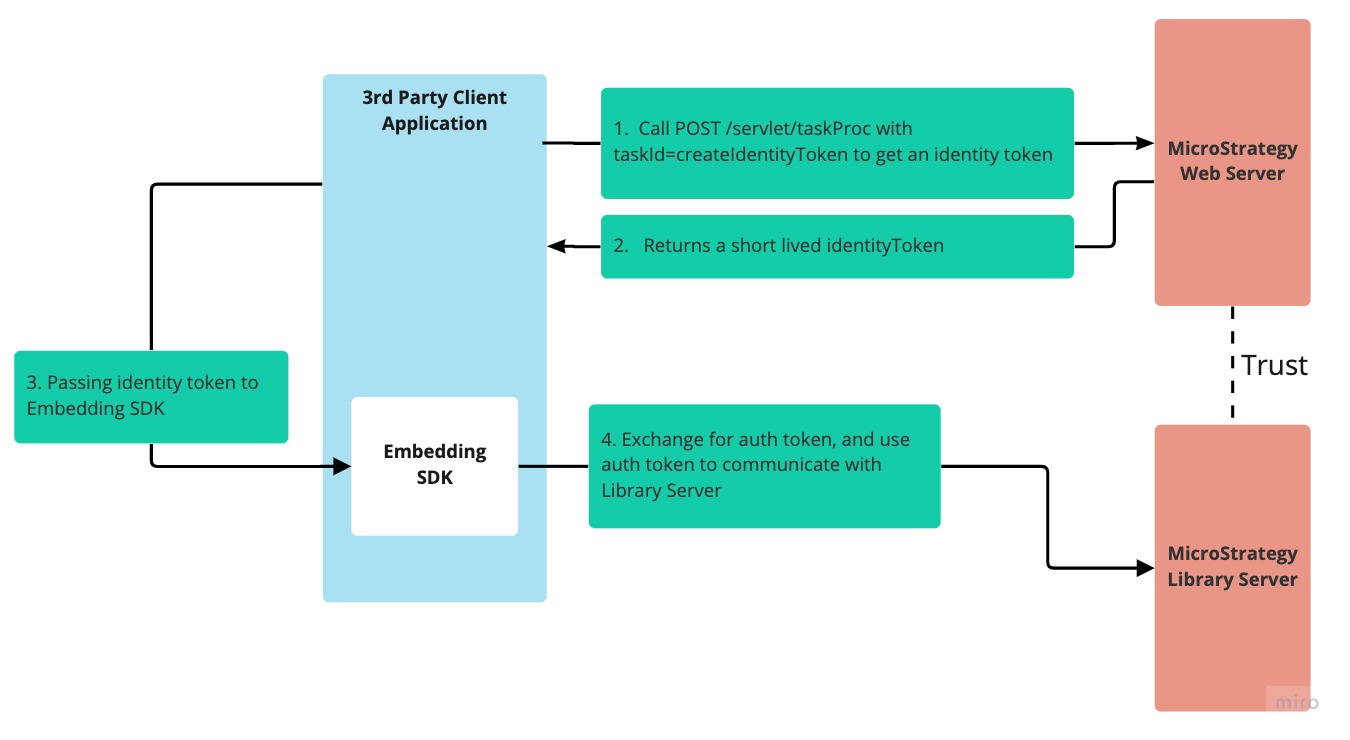
Identicom exposes REST APIs and supports SAML 2.0 for identity provider integration. If you are using Azure AD or Okta, the integration is mostly point-and-click. For custom built systems, you handle the token exchange yourself. The API documentation covers most edge cases but the webhooks for asynchronous processing are not well documented. One thing nobody tells you about webhook reliability is that Identicom does not guarantee delivery order. If your application depends on a strict sequence of events during federated login flows, you need to implement your own ordering logic. I built a simple message queue between the webhook receiver and my auth service to handle this. It adds latency but prevents race conditions that cause silent authentication failures.
Get the Full Details
Performance and Scalability Realities
A single Identicom node can handle roughly 500 concurrent verification requests before response times start climbing noticeably. The platform auto-scales with container orchestration but the scaling is not instant. During traffic spikes, you will see a 200 to 400 millisecond increase in verification time before new instances spin up. For consumer-facing applications where login happens in bursts, this matters more than the documentation suggests. If you are building for high throughput, plan your infrastructure with at least double your expected peak load in mind. The cost of overprovisioning is lower than the cost of degraded user experience during peak hours. I learned this the hard way when a retail client expected Black Friday traffic to spike 8x their normal load. We provisioned for 4x and still had issues. They ended up adding a predictive scaling policy that pre-warmed instances 30 minutes before predicted traffic windows.
Common Pitfalls
Template storage location is a decision you should make early. Cloud storage is easier to manage but introduces compliance overhead if you are handling regulated data. On-premise storage gives you more control but shifts the maintenance burden to your team. There is no universal right answer here. It depends on your data residency requirements and operational capacity. Another issue is template aging. Biometric templates degrade over time as user appearance changes. Facial templates are particularly affected by weight fluctuation, aging, or new accessories like glasses. Identicom offers re-enrollment suggestions based on confidence score trends, but the thresholds are aggressive. In practice I tune them to be less aggressive to avoid unnecessary re-enrollment prompts that frustrate users. Security audits show that the biggest vulnerability is not in the matching algorithm but in the enrollment process. Social engineering attacks targeting enrollment staff are common. You should restrict enrollment to authenticated sessions only and implement liveness detection for high-security environments. The platform supports multiple liveness detection methods but enabling them requires additional configuration that many teams skip during initial deployment.
Cost Structure
Identicom operates on a per-verification pricing model with volume discounts. Small deployments under 10,000 verifications per month run about $0.02 per verification. Enterprise agreements drop this significantly but require committed monthly volumes. There are also licensing fees for the capture SDK and support tiers. Budget accordingly because the base license covers core features while advanced capabilities like adaptive authentication require additional modules. Compared to traditional password systems, the total cost of ownership often comes out lower after the first year when you factor in help desk costs for password resets. Most organizations see a 60 to 70% reduction in password-related support tickets after full deployment. That savings usually covers the subscription cost within six to eight months.
When Not to Use It
Identicom is not suitable for low-security internal tools where a password works fine. The implementation complexity and cost do not justify switching for applications that do not handle sensitive data. It is also less effective in environments with limited internet connectivity since real-time verification depends on cloud processing unless you deploy the on-premise variant. If your primary goal is simply reducing password fatigue without needing enterprise-grade security, a FIDO2 passkey implementation might be a simpler and cheaper path. Identicom excels when you need flexible biometric modalities and integration with existing identity infrastructure rather than a standalone solution.
Getting Started
The developer portal at identicom.com provides SDK downloads, sample code, and sandbox access for testing. The sandbox limits you to 1,000 test verifications per day which is enough for development but insufficient for load testing. Plan your staging environment around this constraint or request a temporary elevated quota from their support team. Documentation quality has improved significantly over the past year but some API endpoints still lack detailed examples. The support team is responsive but response times vary depending on your contract tier. Premium support guarantees four-hour response times for production issues while standard support can take 24 to 48 hours. Factor this into your risk assessment if you do not have in-house expertise to troubleshoot independently.