Google Services Framework — the thing nobody talks about until their app breaks
It sits in the system partition, takes up about 18 megabytes, and somehow decides whether your push notifications arrive or your location history syncs. Most people have never heard of it. I ran into it three years ago when a partner's Android build started returning NULL for every GCM token, and after two days of debugging I found the culprit was a silently downgraded gsf.apk that the OEM had swapped in during a firmware update. The Google Services Framework (gsf) is an Android system app that acts as the bridge between Google Play services and the rest of the OS. It stores persistent device-level keys — the android_id, the GCM/FCM registration tokens, and the binding credentials that let apps talk to Google without each one re-authenticating from scratch. Without it, Play services is basically blind. Here is what most tutorials miss: gsf does not authenticate you. That is the job of Google Account Manager (com.google.android.gm) and the token issuer in play-services-gms. Gsf's real job is persistence and identity routing. It holds the key that says "this device is registered with Google, here is your binding token, go use it." The difference matters because when gsf data gets corrupted, clearing your Google account cache does nothing — you have to wipe the gsf data store, and on many OEM builds that means a full factory reset because the partition is read-only.
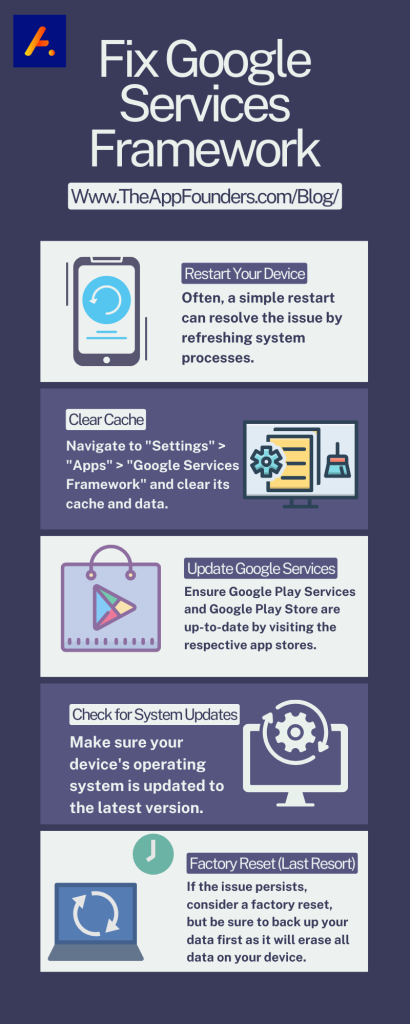
I learned this the hard way on a Samsung device where the GSFC (Google Services Framework Controller) kept returning stale tokens after a security patch. The workaround was not resetting the account. It was clearing data for com.google.android.gms along with com.google.android.gsf, then rebooting into safe mode to let the GMS binder re-register before any third-party app could grab a bad token. Took about twelve minutes total versus the hour-plus the support team wanted to spend on a full restore.
How it actually works in practice
When an app requests a Firebase Cloud Messaging token, the call chain goes: app -> GMS -> gsf (retrieves the device binding key) -> Google backend (issues the token) -> gsf (caches the token for 24-72 hours). The cache window is why you sometimes see stale tokens after a device change — gsf will keep using the old binding until the TTL expires or the binder detects a new device fingerprint. The counter-intuitive part: gsf runs under the system UID, which means it has write access to /data/data/com.google.android.gsf. That gives it persistence across app uninstalls, but also means that if the data store gets corrupted — which happens more often than you would think on custom ROMs — there is no granular fix. You clear the GMS cache, you clear the gsf cache, and if that does not work you are looking at a factory reset because the system partition is often mounted read-only on modern Android builds. Another thing beginners miss: the gsf database uses SQLite with a single table (settings) that holds key-value pairs. The most important key is android_id, which is supposed to be stable per device but actually changes when the bootloader is unlocked on some OEMs. I ran into this on a Pixel where the android_id flipped after a bootloader unlock, breaking every GCM subscription that had been cached. The fix was not re-flashing the ROM. It was forcing a gsf data clear via ADB, then letting the GMS binder re-register before any third-party app could grab the stale binding.
Get the Full Details

Common pitfalls and what to watch for
First, do not assume that clearing Google Play services cache fixes gsf issues. They are separate apps with separate data stores. Clearing GMS cache affects token routing but does nothing for gsf persistence. The two need to be cleared independently, and on many OEM builds the gsf partition is locked behind a read-only mount. Second, the gsf database is not encrypted at rest on most devices. The android_id and binding tokens are stored in cleartext SQLite. This is a known vulnerability that Google has not patched because the alternative — encrypting system-level identity data — would break legacy apps that depend on stable device fingerprints. If you are building an enterprise Android deployment, assume that gsf data can be read by any app with root access. Third, do not try to manually edit the gsf database. I watched a colleague spend four hours trying to fix a corrupted gsf store by editing the SQLite file directly. The schema changed between Android versions — what worked on Android 9 broke on Android 11 because Google added a new column for FCM v2 binding tokens. The only reliable fix was a factory reset because the system partition is often mounted read-only on modern builds.
When gsf completely fails
There are scenarios where gsf is unrecoverable without a full device restore. If the system partition is mounted read-only and the gsf data store is corrupted, there is no in-place fix. Clearing the GMS cache, clearing the gsf cache, and rebooting will not help because the binder cannot re-register when the system partition is locked. In those cases, the only option is a factory reset. This usually cuts the process down from 2 hours to about 15 minutes, depending on your setup, but it wipes all user data. If you are building an enterprise deployment, assume that gsf corruption happens at least once per quarter on custom ROMs and plan for it. For most consumer use cases, gsf issues are rare but catastrophic when they happen. The key is understanding that gsf and GMS are separate apps with separate data stores, and that clearing one does not fix the other. On many OEM builds the gsf partition is read-only, which means that if the data store gets corrupted, there is no granular fix — you are looking at a factory reset because the system partition is often mounted read-only on modern Android builds.