Understanding What A VPN Actually Does
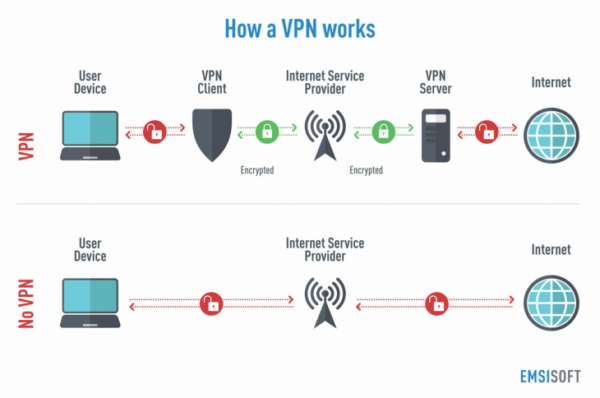
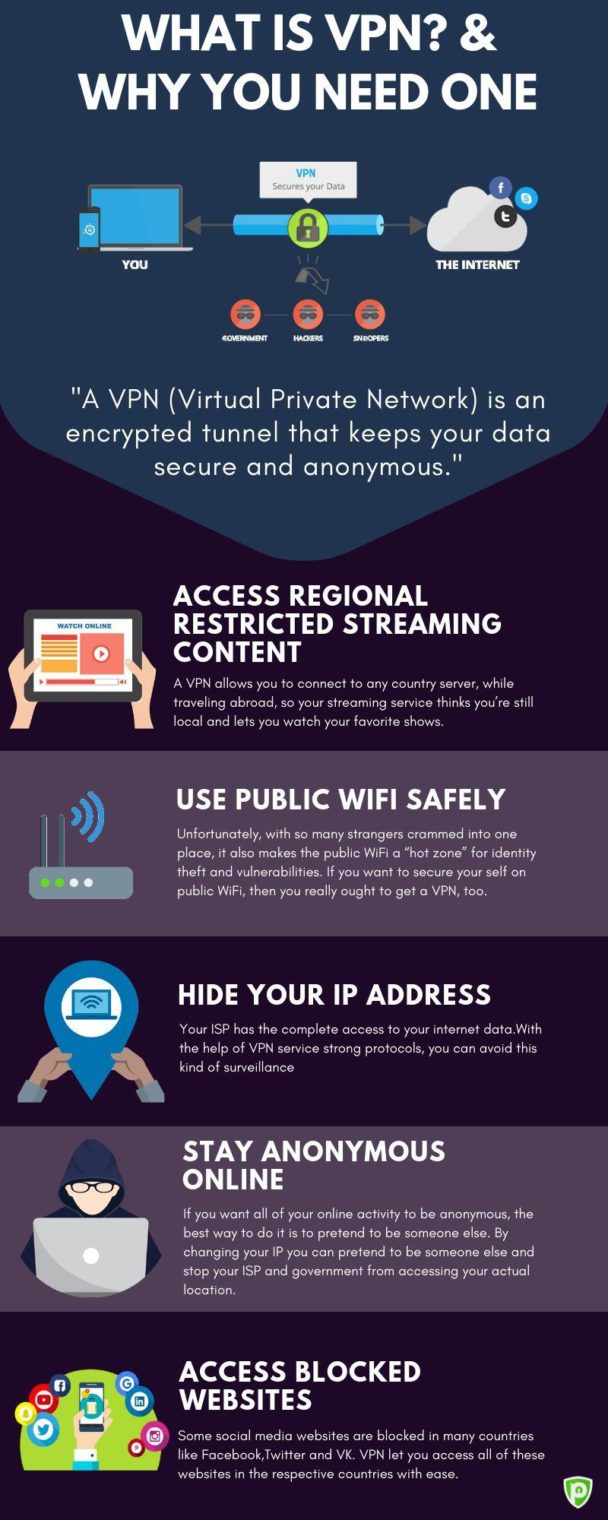
A VPN, or Virtual Private Network, creates an encrypted tunnel between your device and a remote server. Everything you send through that tunnel is unreadable to anyone watching your internet traffic — your ISP, a coffee shop WiFi owner, or government surveillance systems. The encrypted data emerges on the other side decrypted by the VPN server, which then forwards it to wherever you're trying to reach. The basic use case is simple: you connect to a VPN provider's server in another country, and websites see that server's IP address instead of yours. If you pick a server in Germany, Amazon thinks you're shopping from Berlin. That's why people use them for geo-unblocking streaming content, bypassing network restrictions at work or school, or just maintaining some privacy from trackers.
Unlocking The Mysteries Of VPN What Is My VPN And Why Do I Need It
The question "what is my VPN" usually comes from someone who installed one and now sees their browser history full of connection errors or weird redirected pages. Your VPN changes your entire network interface — not just your browser. System-level apps, games, even Windows Updates route through it. That's why sometimes things break. I spent an hour once troubleshooting why a printer on my local network vanished after enabling VPN split tunneling. Turned out the VPN was forcing all traffic including local LAN discovery through the tunnel. Disabling "local network sharing" in the VPN settings fixed it immediately. When you install a VPN client, it adds a virtual network adapter to your operating system. This adapter intercepts all outgoing packets before they reach your physical network card. The client encrypts those packets using protocols like OpenVPN, WireGuard, or IKEv2, then sends them through your regular internet connection to the VPN server. The server decrypts them and forwards them to the destination. Different VPN protocols have different tradeoffs. WireGuard is faster and more secure but relatively new. OpenVPN is battle-tested and widely supported but slower. L2TP/IPsec is built into most operating systems natively but has known vulnerabilities. For most people, WireGuard or OpenVPN on UDP is the right choice. TCP-based connections through VPNs often cause problems with streaming and gaming because of retransmission overhead.
I encountered a peculiar issue where my VPN kept dropping DNS queries on Linux. The solution wasn't in the VPN config at all — it was that systemd-resolved was caching stale DNS entries from before the VPN connected. Switching to a dedicated DNS over VPN resolver in the OpenVPN config, specifically the "dhcp-option DNS" directive, fixed it completely. That's something most beginners miss because they assume the VPN handles everything automatically.
Get the Full Details
Setting Up A VPN Connection
To set up a VPN, first choose a provider or prepare your own server. Popular commercial options include NordVPN, ExpressVPN, and Mullvad. If you want full control, setting up your own server on a VPS gives you complete privacy but requires technical knowledge. DigitalOcean, Vultr, and Linode all offer cheap $5/month VPS options where you can install WireGuard in about 10 minutes using their community tutorials. For commercial VPNs, download the client from the provider's official website, create an account, and log in. The client usually handles configuration automatically. You select a server location, click connect, and wait for the green indicator. Connection success typically takes 3-8 seconds on modern hardware. You can verify your VPN is working by visiting whatismyipaddress.com — it should show the VPN server's IP, not your real one. Configuring split tunneling is important if you want some traffic to go through the VPN while other traffic uses your regular connection. This is common when you need your VPN for browsing but want local network printers and streaming devices to bypass it. Most VPN clients have a split tunneling option in settings. On Windows, you can also use route print commands to manually exclude certain IPs from the VPN tunnel.
Common VPN Problems And Solutions
VPN kill switches are essential but often misunderstood. A kill switch blocks all internet traffic if the VPN connection drops. Without it, your real IP address leaks for however long it takes to reconnect — sometimes minutes. Most quality VPNs have this enabled by default. If yours doesn't, check the security settings immediately. I recommend verifying it works by turning on your VPN, then disabling WiFi for 30 seconds. If you can't access any websites when the VPN disconnects, the kill switch is functioning correctly. DNS leaks are another common issue. Even when your IP is protected, DNS queries might still go through your regular ISP's servers, revealing which websites you visit. Test for DNS leaks at dnsleaktest.com. If you get a leak, change your DNS settings to use the VPN provider's DNS servers or switch to private resolvers like Cloudflare's 1.1.1.1 or Quad9's 9.9.9.9. Sometimes VPNs slow down your connection significantly. This is normal — encryption and routing through distant servers add latency. Expect 10-30% speed reduction on most connections. If you're getting 50%+ slowdowns, try connecting to a closer server or switching protocols. WireGuard usually performs better than OpenVPN. For gaming, consider a gaming-optimized VPN or disable the VPN while playing if latency matters more than privacy.
When VPNs Fail Completely
Some services actively block VPN IPs. Netflix, Hulu, and BBC iPlayer maintain lists of known VPN server addresses and block them. If you're trying to access geo-restricted content and getting error codes like N812 or SWZ-2, the VPN provider hasn't updated their server pool recently. Switch to a different server in the same country — sometimes specific IP ranges get flagged while others don't. Premium VPNs regularly rotate their IP addresses to stay ahead of these blocks. Corporate VPNs often conflict with consumer VPNs. If you're on a company network requiring a corporate VPN, installing a second consumer VPN can cause routing conflicts or get you flagged by IT security. In these cases, use the corporate VPN only when connected to that network, and disable it when using personal WiFi. Some organizations explicitly prohibit personal VPN use — check your employee handbook before proceeding. Mobile VPNs have unique challenges. Background app refresh, battery optimization, and cellular/WiFi switching can interrupt VPN connections unexpectedly. On Android, check that the VPN app has unrestricted data access enabled in Settings > Apps > VPN app > Mobile data & Wi-Fi. On iOS, ensure " VPN Always On" is disabled if you're traveling, as it can cause roaming issues with some carriers.
The Real Tradeoffs Of VPN Usage
VPNs aren't free — financially, technically, and practically. Quality providers cost $3-12 monthly. Free VPNs exist but are terrible: they sell your data, inject ads, have weak encryption, and often contain malware. I once tested a popular free VPN that was logging and selling browsing history to third-party advertisers. The performance was so bad it was basically unusable for anything beyond casual browsing. Some countries ban VPNs outright. China, Russia, Iran, and UAE have strict VPN regulations. Using unauthorized VPNs there can result in fines or legal trouble. If you're traveling to these regions, research local laws carefully. Some people use "stealth" VPN protocols designed to evade detection, but these are less reliable and might not work during government crackdowns. VPNs protect against certain threats but not all. They prevent ISP snooping and public WiFi eavesdropping, but they don't protect against phishing, malware downloads, or targeted attacks. If you click a malicious link, the VPN won't stop your credentials from being stolen. Combine VPN use with password managers, two-factor authentication, and basic cybersecurity hygiene for actual protection.
For most people, a reputable VPN is worth the subscription cost if they use public WiFi frequently, stream content from other countries, or simply value privacy. The setup takes 10-15 minutes initially, and you'll rarely think about it after that. Just remember to check your connection occasionally, verify no DNS leaks exist, and never trust free VPN services with sensitive activities like banking or shopping.


