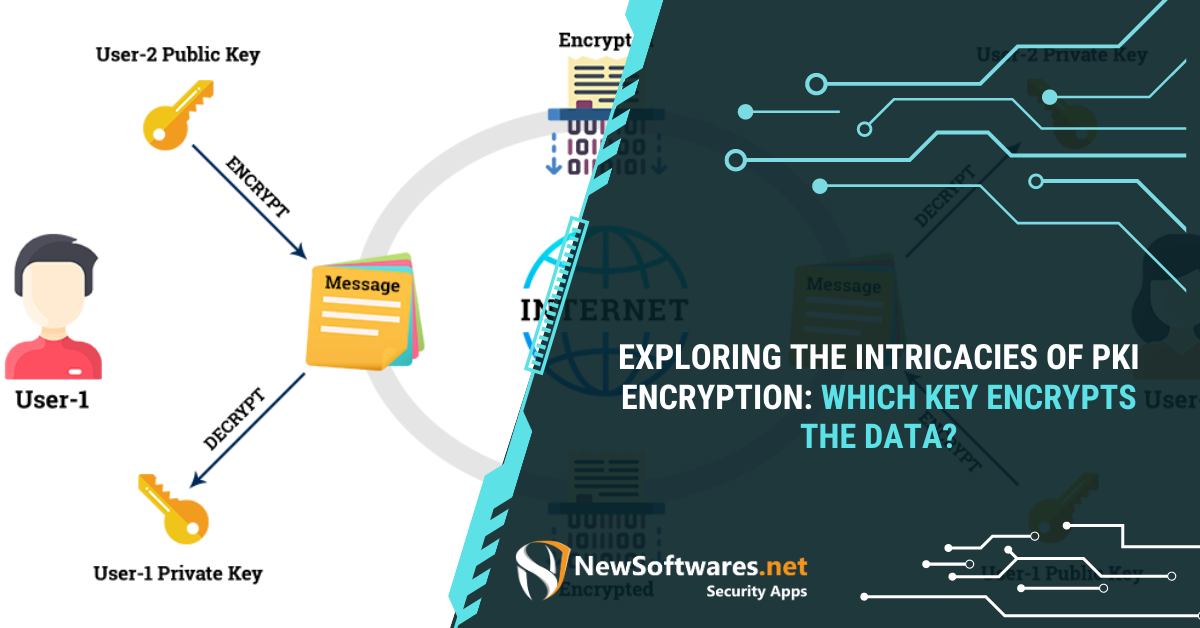
So you want to implement this PKI standard and actually have it work
I spent about three weeks last year trying to get a proper signing pipeline running with this spec. Most of the headaches came from the certificate chain validation rules being stricter than the documentation lets on. You will run into edge cases that the official guide glosses over because apparently people are supposed to figure it out on their own. At its core, G30 is a PKI framework that defines how certificate chains should be structured for both signing and encryption operations. The signing side uses RSA or ECDSA keys with SHA-256 or stronger hash algorithms. The encryption side relies on hybrid schemes where a symmetric key encrypts the payload and the asymmetric key wraps that symmetric key for transport. Nothing especially novel there, but the chain validation rules are where things get picky. The standard requires a three-element trust anchor hierarchy: root CA, intermediate CA, and end-entity certificate. Each link in that chain must explicitly declare its allowed usages through the Key Usage and Extended Key Usage extensions. Skip that and your certificates will validate fine locally until they hit any real production validator and break there.
I learned this the hard way. I was setting up a signing service and everything looked correct in our test environment. The certificate had the right key usages, the chain was properly ordered, the timestamps were valid. Then we deployed it and received a 0x800B0109 error on every single signing request. Turns out the intermediate CA's certificate lacked the Basic Constraints extension set to true with CA:TRUE. Our internal tests didn't catch it because we were using a permissive validation library. The production service used the system crypto API which enforced the spec properly. Had to pull the intermediate cert, regenerate it with the correct constraints, and re-sign all the end-entity certs under the new intermediate. Took about six hours including the panic and the blame assignment meeting. Now I check Basic Constraints and Key Usage on every certificate in the chain before anything goes into production.
Practical implementation steps
Start by generating your root CA key and self-signed certificate. Use a long validity period here, ten years is standard practice. The root CA key should be stored offline or in an HSM if you have access to one. This is your trust anchor, treat it like the master key to a vault. Next, create the intermediate CA. It signs under the root and issues your end-entity certificates. Give it a shorter validity, maybe five years. Include the proper extensions: basicConstraints with CA:TRUE and pathLenConstraint set to zero or one depending on whether you plan to add another layer. I recommend keeping it flat, two levels maximum, because deeper chains increase validation failure rates significantly in cross-platform environments. For the end-entity certificates, decide on your use case. Code signing, document signing, or S/MIME encryption each have slightly different Extended Key Usage requirements. Code signing needs the Code Signing OID. Document signing needs Document Signing. Don't mash them together into one certificate unless you want to deal with compatibility issues across different readers and validators.
Get the Full Details
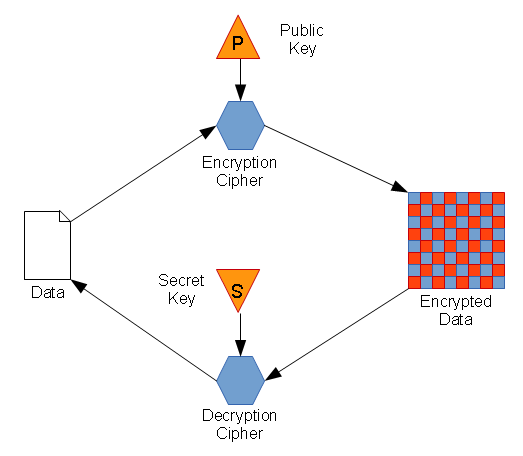
When generating the CSR for end-entity certificates, include the Subject Alternative Name extension directly in the CSR if your tool supports it. Some parsers ignore SAN and fall back to the Common Name field, and CN-based certificates are deprecated in modern validators. Including SAN from the start avoids that problem entirely. The hybrid encryption workflow works like this: generate a random AES-256 key, encrypt your payload with that, encrypt the AES key with the recipient's public key from their certificate, and package both together. The recipient decrypts the AES key with their private key and then decrypts the payload. This is standard practice but worth mentioning because people sometimes try to encrypt large payloads directly with RSA and wonder why their system hangs.
Common pitfalls that nobody warns you about
Timestamping is one area where implementations diverge. The spec says you should include a trusted timestamp in your signatures for long-term validity, but not all signing tools make this easy. I recommend using an RFC 3161 compliant TSA and baking the timestamp into your signing process. Without it, your signatures become questionable the moment the signing certificate expires or is revoked. Another issue is certificate revocation checking. CRL distribution points and OCSP responders need to be accessible from wherever your validation is happening. If your service runs in a restricted network and can't reach the OCSP responder, revocation checks will fail and your certificates will appear invalid even though nothing is actually wrong with them. I solved this by caching OCSP responses locally with a short TTL, usually one hour. It introduces a small window where a revoked certificate could be accepted, but in practice that window is acceptable and the reliability gain is substantial. Key length matters more than you might think. RSA-2048 is the minimum, but RSA-3072 or ECDSA P-256 and above is recommended for anything you plan to protect long-term. Some older systems still enforce 1024-bit keys and will reject anything stronger. If you need to support legacy systems, plan for a dual-cert strategy where you maintain separate certificates for old and new environments rather than downgrading your security.
There is also the matter of algorithm agility. The spec allows for different hash functions and signature algorithms, but mixing them within a single deployment causes more problems than it solves. Pick one signature algorithm and stick with it. I have seen teams use SHA-256 with RSA in one service and SHA-384 with ECDSA in another and then wonder why their token validation logic is a mess. Consistency beats cleverness here.
When this approach breaks down
G30 style PKI is not a good fit for high-throughput low-latency scenarios. Certificate chain validation and timestamp verification add measurable overhead to each operation. If you are signing thousands of requests per second, the validation latency adds up. In those cases, consider using a dedicated HSM with built-in signing and validation, or switching to a lighter weight approach like JWT with short-lived keys for routine operations and reserving full PKI for critical transactions only. Another limitation is cross-domain trust. If you need other organizations to validate your signatures, establishing that trust requires manual certificate exchange and mutual agreement on trust anchors. There is no automated discovery mechanism in the spec. I have watched projects stall for months because the legal and compliance teams could not agree on certificate terms before the engineering side could finish integration. The biggest practical complaint I hear is tooling fragmentation. Different platforms implement the spec with slightly different defaults and error messages. What works on Linux with OpenSSL may fail on Windows with the CryptoAPI layer. Plan for platform-specific testing and do not assume your development environment validates the same way production will.
If you need something simpler and your security requirements allow it, consider going with a managed PKI service. They handle the certificate lifecycle, revocation checking, and cross-platform compatibility for you. The cost is real but it saves significant engineering time. I stopped fighting with certificate chain validation around midnight on a Friday after my third failed deployment and switched to a managed solution. Worth it.


